🚨🚨🚨 ATTENTION 🚨🚨🚨
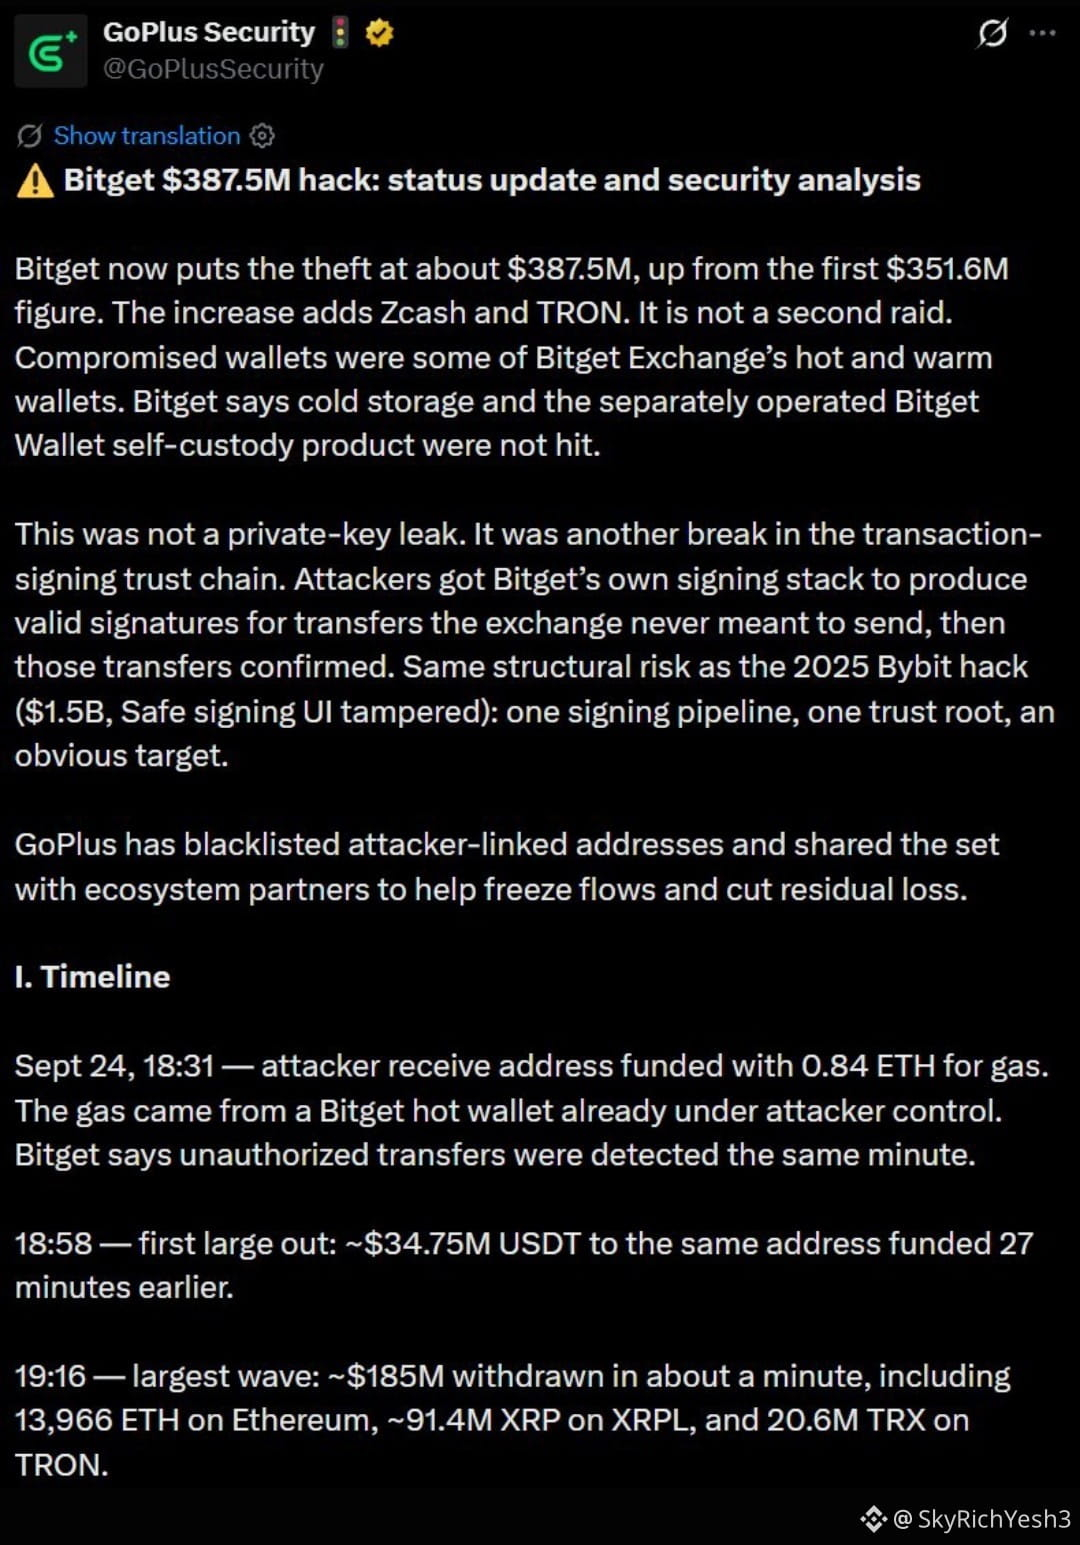
🛟🛟🛟GoPlus: The hacking of $387.5 million on Bitget exploited the trust chain in transaction signing, not the private keys🛟🛟
💥💥💥GoPlus Security said its review of the $387.5 million security incident involving Bitget found that the attack did not involve a private key leak, but rather a compromise of the trust chain in transaction signing.💥💥💥
🌐🌐🌐 The attackers breached a critical wallet backend system, falsified transaction data, and caused Bitget’s authorized signing flow to generate valid signatures for transfers the exchange did not intend to make.🌐🌐🌐
☯️☯️☯️GoPlus said the fund-draining window lasted about 2 hours and 25 minutes, with the biggest wave moving around $185 million in about one minute.☯️☯️☯️
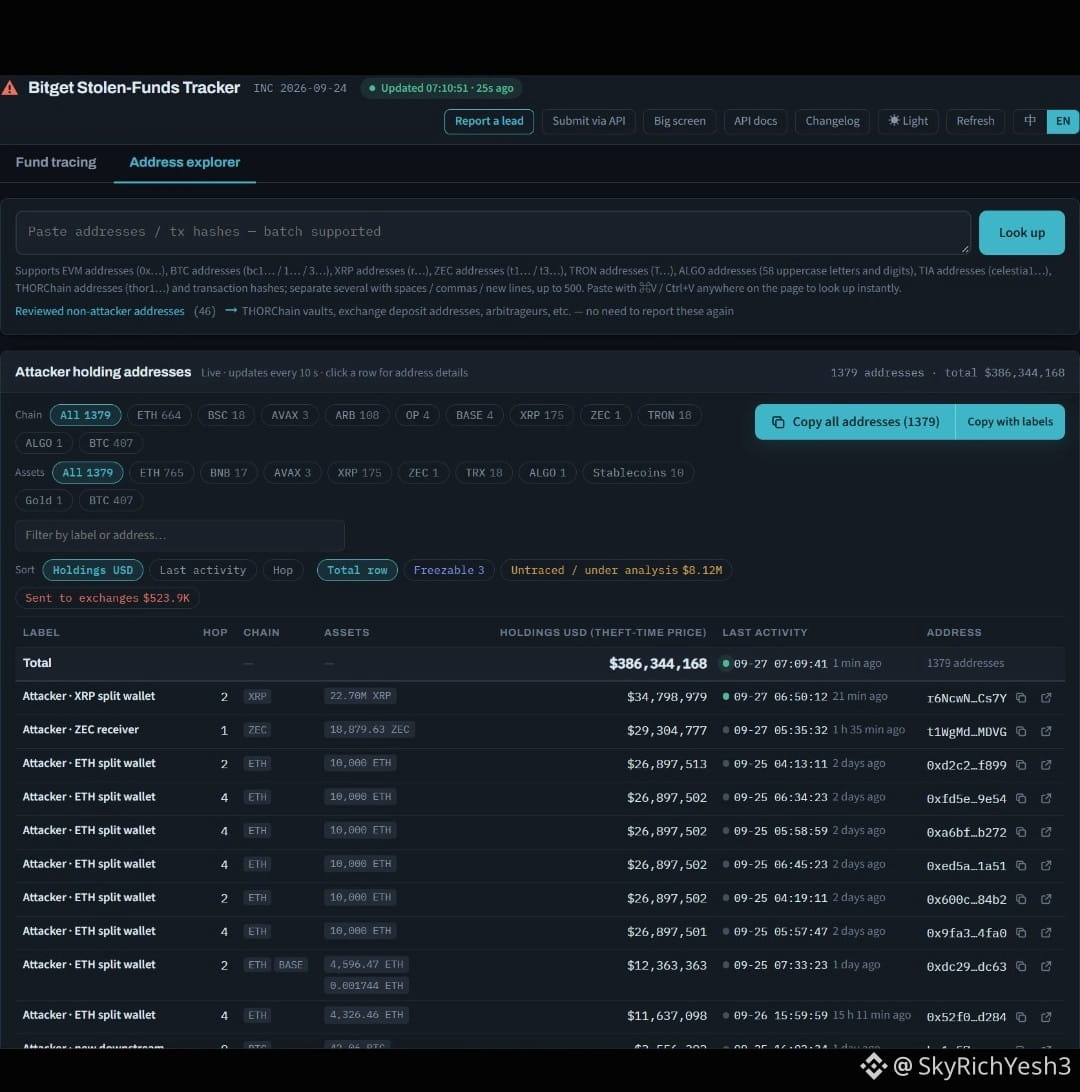
🕋🕋It has blacklisted addresses linked to the attackers and shared them with ecosystem partners. GoPlus said the incident shows structural similarities to the 2025 Bybit hack, although Bitget has not yet published a complete technical report and the initial intrusion method remains unconfirmed.🕋
#CircleMints500MUSDCOnSolana
#SECSaysTokenBuybacksNotAutoSecurities
$BERA
$OP
$WLD
🛟🛟🛟GoPlus: The hacking of $387.5 million on Bitget exploited the trust chain in transaction signing, not the private keys🛟🛟
💥💥💥GoPlus Security said its review of the $387.5 million security incident involving Bitget found that the attack did not involve a private key leak, but rather a compromise of the trust chain in transaction signing.💥💥💥
🌐🌐🌐 The attackers breached a critical wallet backend system, falsified transaction data, and caused Bitget’s authorized signing flow to generate valid signatures for transfers the exchange did not intend to make.🌐🌐🌐
☯️☯️☯️GoPlus said the fund-draining window lasted about 2 hours and 25 minutes, with the biggest wave moving around $185 million in about one minute.☯️☯️☯️
🕋🕋It has blacklisted addresses linked to the attackers and shared them with ecosystem partners. GoPlus said the incident shows structural similarities to the 2025 Bybit hack, although Bitget has not yet published a complete technical report and the initial intrusion method remains unconfirmed.🕋
#CircleMints500MUSDCOnSolana
#SECSaysTokenBuybacksNotAutoSecurities
$BERA
$OP
$WLD