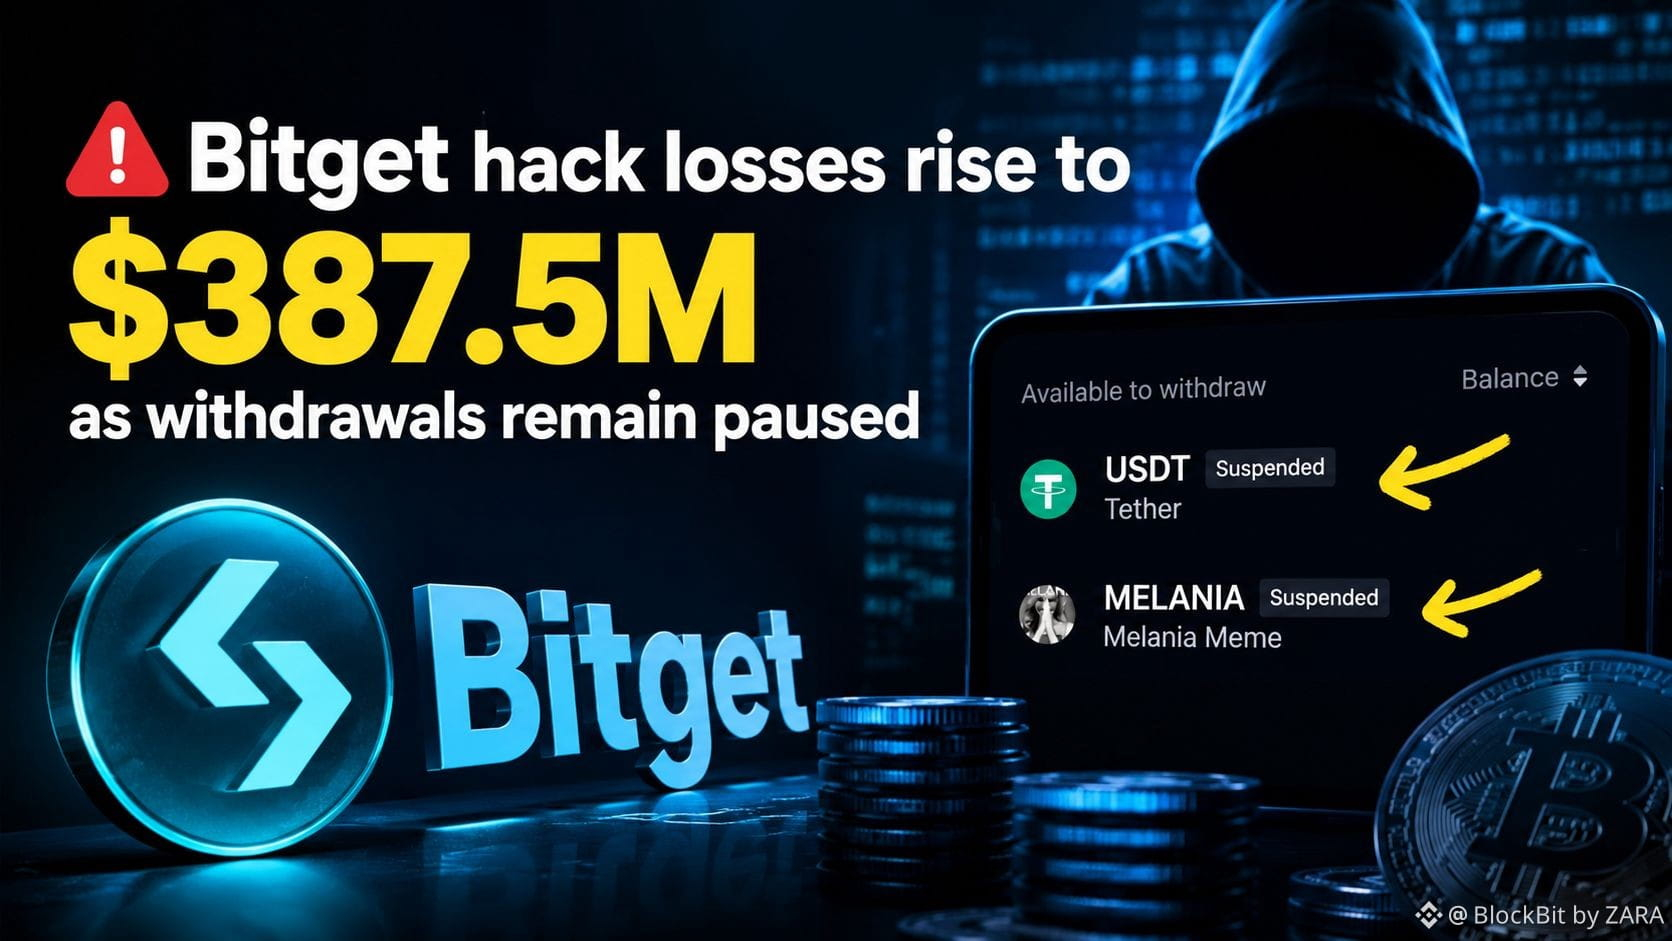
⚠️ Bitget hack losses rise to $387.5M as withdrawals remain paused
Bitget has raised its estimated losses from the September 24 security breach to approximately $387.5 million, up from the initial $351.6 million.
The exchange says the increase came after further on-chain tracing identified additional Zcash and TRON assets involved in the original incident. It does not represent another attack or additional unauthorized transfers.
The breach affected portions of Bitget’s hot and warm wallet infrastructure, while its cold wallets remained secure. According to CEO Gracy Chen, attackers did not steal private keys. Instead, they allegedly compromised a backend system and spoofed transaction data to make unauthorized transfers appear legitimate to the exchange’s authorization process. The investigation with Mandiant and SlowMist is still ongoing.
Bitget has temporarily suspended withdrawals, while deposits and trading remain operational. The exchange says its $464M+ User Protection Fund covers the reported loss.
North Korean-linked hackers are currently a leading suspect, but the attribution has not been independently confirmed, so it should not be presented as established fact.
Bitget is also pursuing recovery efforts, with industry security firms and other platforms involved in tracing the stolen assets.
The bigger question now is how quickly Bitget can restore withdrawals and recover the affected funds...
#PolymarketBankFailureBetsDrawFDICConcern #BlackRockBuildsTokenizedPortfoliosForOndo #BitwiseFilesToListNEARETFOnNYSEArca
Bitget has raised its estimated losses from the September 24 security breach to approximately $387.5 million, up from the initial $351.6 million.
The exchange says the increase came after further on-chain tracing identified additional Zcash and TRON assets involved in the original incident. It does not represent another attack or additional unauthorized transfers.
The breach affected portions of Bitget’s hot and warm wallet infrastructure, while its cold wallets remained secure. According to CEO Gracy Chen, attackers did not steal private keys. Instead, they allegedly compromised a backend system and spoofed transaction data to make unauthorized transfers appear legitimate to the exchange’s authorization process. The investigation with Mandiant and SlowMist is still ongoing.
Bitget has temporarily suspended withdrawals, while deposits and trading remain operational. The exchange says its $464M+ User Protection Fund covers the reported loss.
North Korean-linked hackers are currently a leading suspect, but the attribution has not been independently confirmed, so it should not be presented as established fact.
Bitget is also pursuing recovery efforts, with industry security firms and other platforms involved in tracing the stolen assets.
The bigger question now is how quickly Bitget can restore withdrawals and recover the affected funds...
#PolymarketBankFailureBetsDrawFDICConcern #BlackRockBuildsTokenizedPortfoliosForOndo #BitwiseFilesToListNEARETFOnNYSEArca