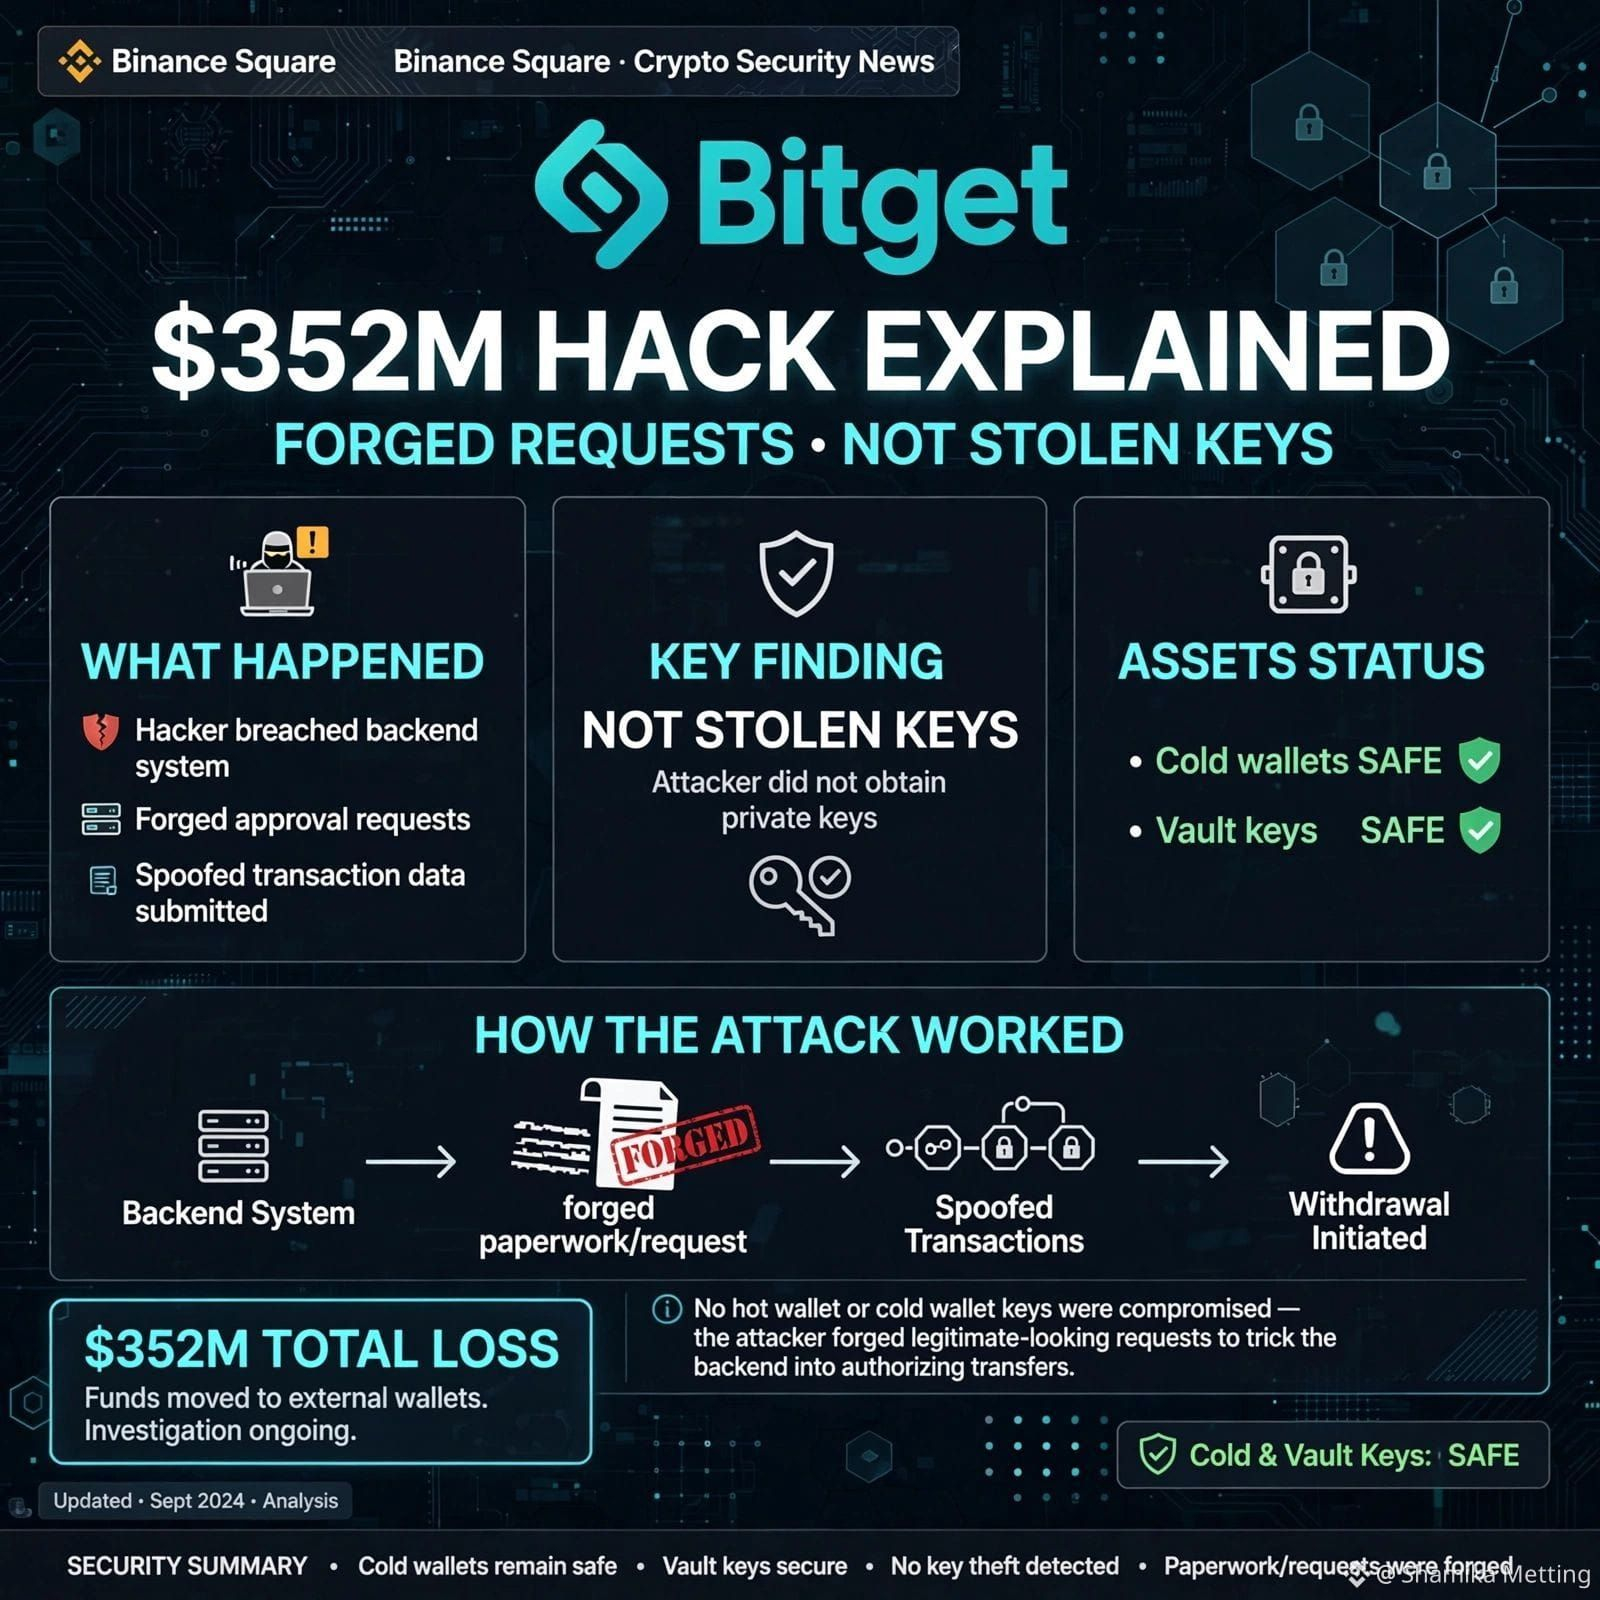
🚨 The Bitget intrusion was explained for $352 million: ¡forged requests, not stolen keys!
Everyone panics about private keys. But Bitget’s CEO, Gracy Chen, confirmed something even more concerning.
What really happened?
❌ Private keys weren’t stolen (cold, hot, and warm keys protected in secure vaults)
❌ Users’ withdrawal requests weren’t falsified
✅ The attackers compromised a critical and backup system (Backend)
✅ They falsified transaction data
✅ They triggered Bitget’s authorization process to move $351.6 million
Think of it like this: "They didn’t break into the safe; they forged the documents." The safe keys never left the building; someone simply created official forged receipts.
Current status:
Detected at 18:31 UTC on September 24
Cold wallets are safe
The users’ protection fund will cover a loss of $464 million
The chairwoman links the attack to connections with North Korea through evidence from IP address directions
What do you think: should CEX platforms make their backend public (open source)?
Please continue
$AVAX $TRX $XRP
#Bitget #BitgetHack #CryptoSecurity #BreakingNews #BinanceSquare #bitgetbreachforgedrequestsnotstolenkeys
Everyone panics about private keys. But Bitget’s CEO, Gracy Chen, confirmed something even more concerning.
What really happened?
❌ Private keys weren’t stolen (cold, hot, and warm keys protected in secure vaults)
❌ Users’ withdrawal requests weren’t falsified
✅ The attackers compromised a critical and backup system (Backend)
✅ They falsified transaction data
✅ They triggered Bitget’s authorization process to move $351.6 million
Think of it like this: "They didn’t break into the safe; they forged the documents." The safe keys never left the building; someone simply created official forged receipts.
Current status:
Detected at 18:31 UTC on September 24
Cold wallets are safe
The users’ protection fund will cover a loss of $464 million
The chairwoman links the attack to connections with North Korea through evidence from IP address directions
What do you think: should CEX platforms make their backend public (open source)?
Please continue
$AVAX $TRX $XRP
#Bitget #BitgetHack #CryptoSecurity #BreakingNews #BinanceSquare #bitgetbreachforgedrequestsnotstolenkeys