Payment Processor Vulnerability Impacts 23,000 NFTs
Once again, an approval is what gets confiscated—leaving the market to learn a lesson the hard way.
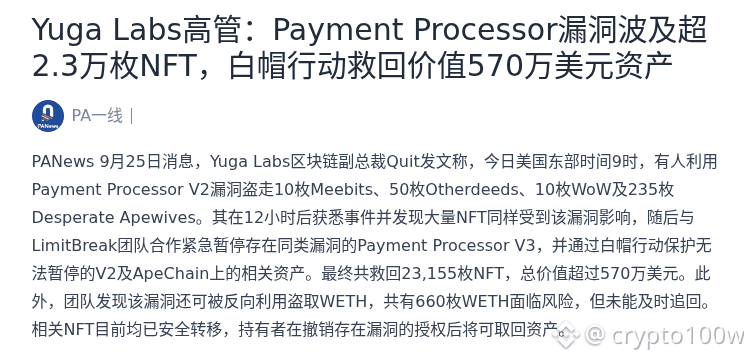
According to a report by PANews, Yuga Labs’ blockchain vice president Quit said that at 9:00 AM Eastern Time in the United States today, the Payment Processor V2 vulnerability was exploited. The attackers first stole 10 Meebits, 50 Otherdeeds, 10 WoW, and 235 Desperate Apewives. After 12 hours, the team confirmed that more NFTs were affected and, together with LimitBreak, urgently paused Payment Processor V3 to prevent similar vulnerabilities. For the V2 and ApeChain-related assets that white-hat teams were unable to pause, they ultimately recovered 23,155 NFTs with a total value exceeding $5.7 million.
More notably, this attack path also enables reverse theft of WETH—about 660 WETH are at risk, though they were not recovered in time. The affected NFTs have already been safely transferred. Holders can retrieve their assets after revoking the vulnerable approvals.
In incidents like this, one point to watch is how many of the old approvals are still active, and another is whether platforms can close off similar vulnerabilities faster. Which do you care more about: the “23,155 NFTs that were recovered,” or the “approximately 660 WETH that remain exposed to risk”?
Figure 1: Payment Processor vulnerability impacts 23,000 NFTs · Partial screenshot from the source page
Image source: https://www.panewslab.com/zh/articles/01a0d7e5-a691-715a-ae1c-5303203c7c4e
Once again, an approval is what gets confiscated—leaving the market to learn a lesson the hard way.
According to a report by PANews, Yuga Labs’ blockchain vice president Quit said that at 9:00 AM Eastern Time in the United States today, the Payment Processor V2 vulnerability was exploited. The attackers first stole 10 Meebits, 50 Otherdeeds, 10 WoW, and 235 Desperate Apewives. After 12 hours, the team confirmed that more NFTs were affected and, together with LimitBreak, urgently paused Payment Processor V3 to prevent similar vulnerabilities. For the V2 and ApeChain-related assets that white-hat teams were unable to pause, they ultimately recovered 23,155 NFTs with a total value exceeding $5.7 million.
More notably, this attack path also enables reverse theft of WETH—about 660 WETH are at risk, though they were not recovered in time. The affected NFTs have already been safely transferred. Holders can retrieve their assets after revoking the vulnerable approvals.
In incidents like this, one point to watch is how many of the old approvals are still active, and another is whether platforms can close off similar vulnerabilities faster. Which do you care more about: the “23,155 NFTs that were recovered,” or the “approximately 660 WETH that remain exposed to risk”?
Figure 1: Payment Processor vulnerability impacts 23,000 NFTs · Partial screenshot from the source page
Image source: https://www.panewslab.com/zh/articles/01a0d7e5-a691-715a-ae1c-5303203c7c4e