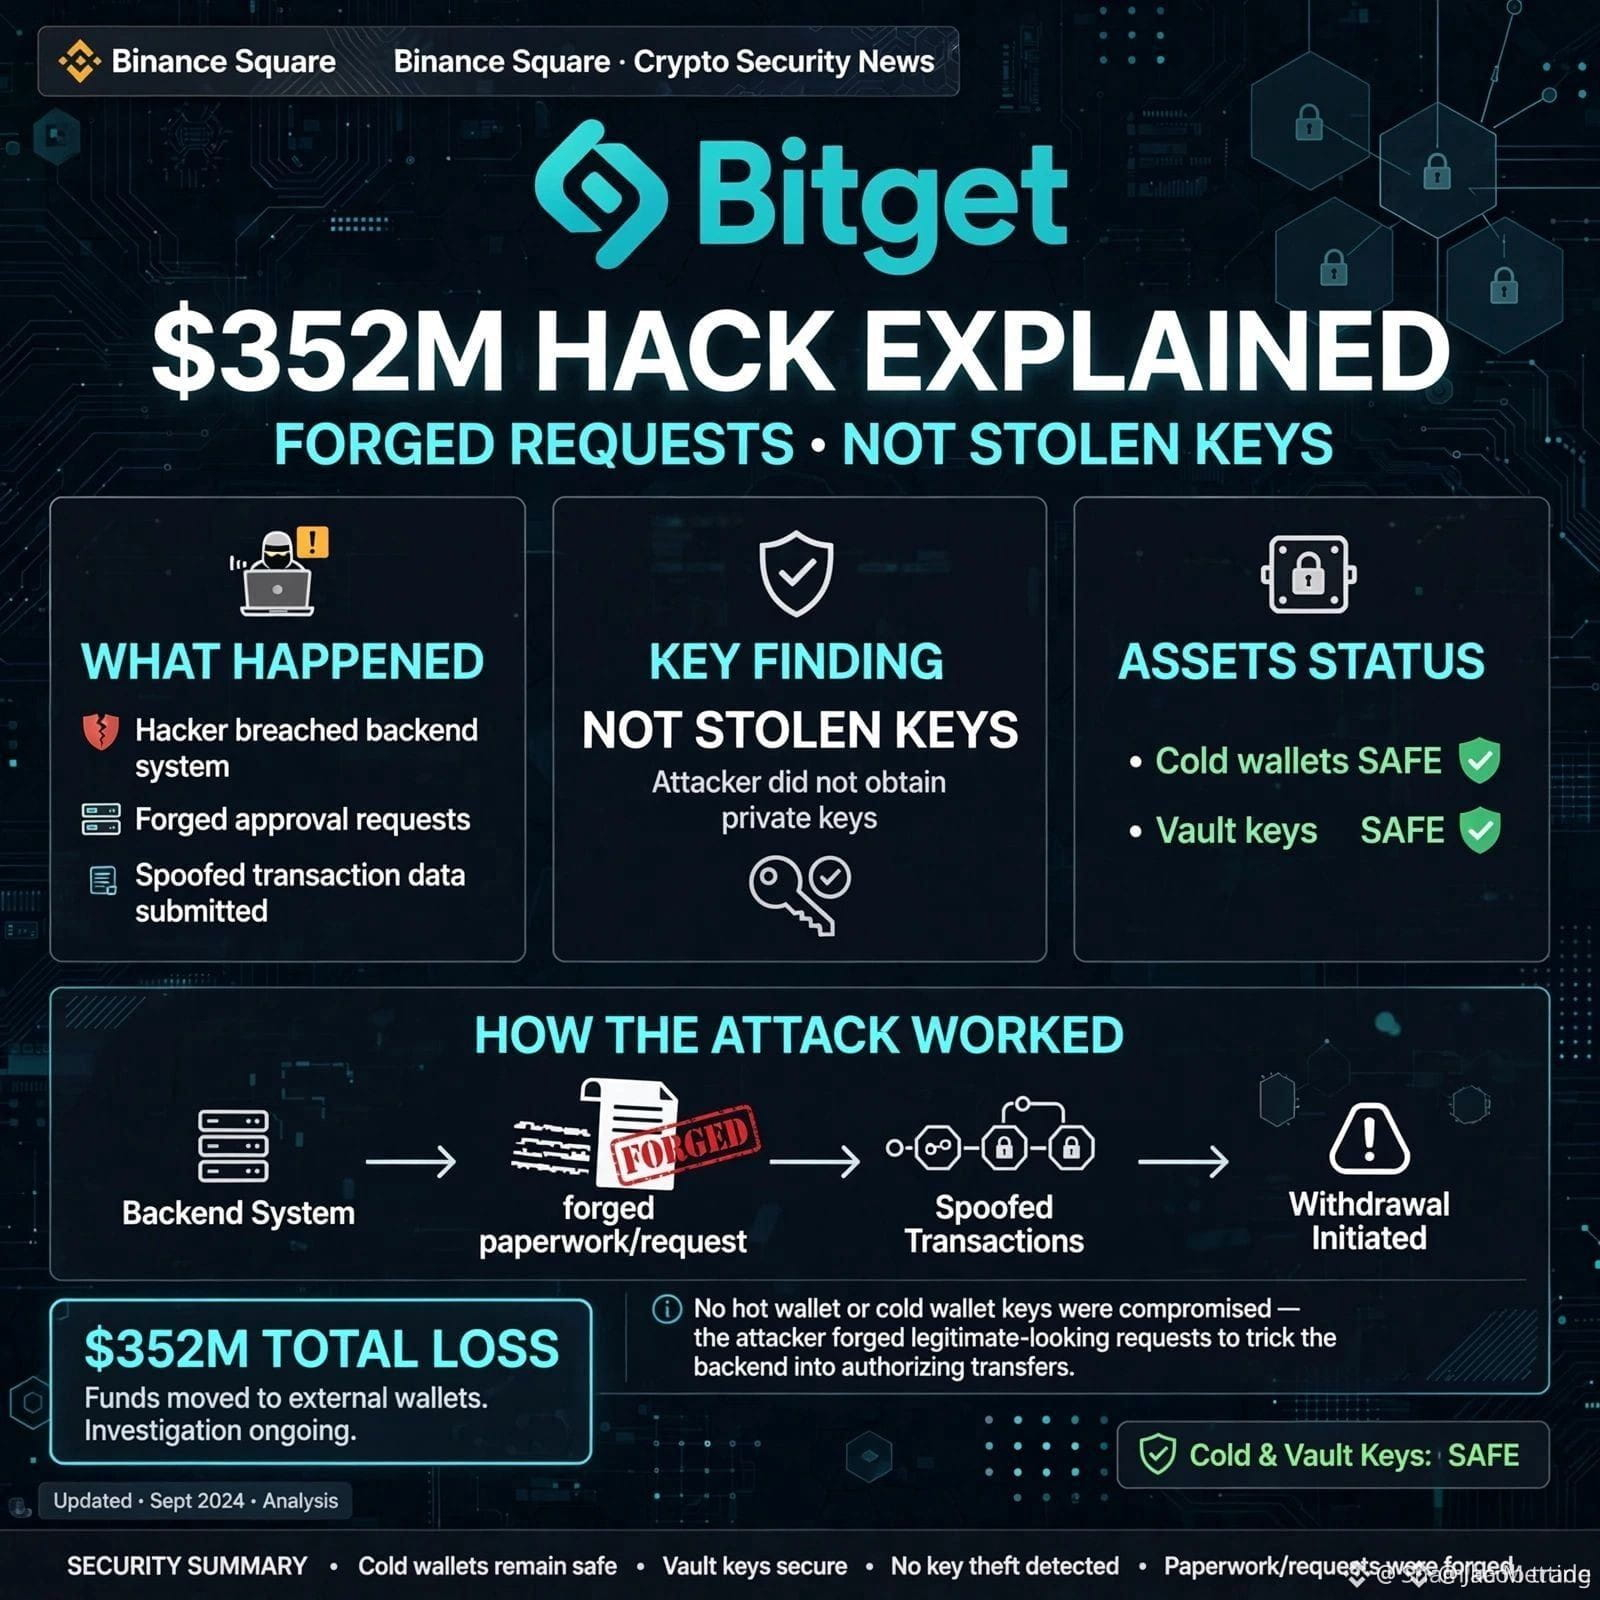
🚨 Details on the $352 million Bitget compromise: falsified requests, not stolen keys!
Everyone is panicking about private keys. But Bitget’s CEO, Gracy Chen, confirmed something even more worrying.
What actually happened:
❌ Private keys (cold, hot, and warm—stored in secure vaults) were not stolen
❌ Users’ withdrawal requests were not forged
✅ The attackers compromised a crucial vital system in the background (backend)
✅ They falsified transaction data
✅ They triggered Bitget’s authorization process to transfer $351.6 million
Imagine the situation like this: “They didn’t break into the vault—they forged the paperwork.” The vault keys never left the building; someone simply created official forged receipts.
Current situation:
Detected at 18:31 UTC on September 24
Cold wallets are secured
The $464 million User Protection Fund will cover the value of the loss
The CEO links the attack to connections coming from North Korea, based on clues drawn from IP addresses
And you—do you think CEX platforms should make their backend open source?
#BitgetBreachForgedRequestsNotStolenKeys #BinanceSquare #CryptoNews #Cybersecurity
$PHA
$BTW
$ARK
Everyone is panicking about private keys. But Bitget’s CEO, Gracy Chen, confirmed something even more worrying.
What actually happened:
❌ Private keys (cold, hot, and warm—stored in secure vaults) were not stolen
❌ Users’ withdrawal requests were not forged
✅ The attackers compromised a crucial vital system in the background (backend)
✅ They falsified transaction data
✅ They triggered Bitget’s authorization process to transfer $351.6 million
Imagine the situation like this: “They didn’t break into the vault—they forged the paperwork.” The vault keys never left the building; someone simply created official forged receipts.
Current situation:
Detected at 18:31 UTC on September 24
Cold wallets are secured
The $464 million User Protection Fund will cover the value of the loss
The CEO links the attack to connections coming from North Korea, based on clues drawn from IP addresses
And you—do you think CEX platforms should make their backend open source?
#BitgetBreachForgedRequestsNotStolenKeys #BinanceSquare #CryptoNews #Cybersecurity
$PHA
$BTW
$ARK