🚨 NEW INFORMATION ABOUT THE BITGET HACK — THEY DIDN’T STEAL KEYS, THEY FALSIFIED DATA 🔥
📌 Source: Binance News
📅 September 25, 2026
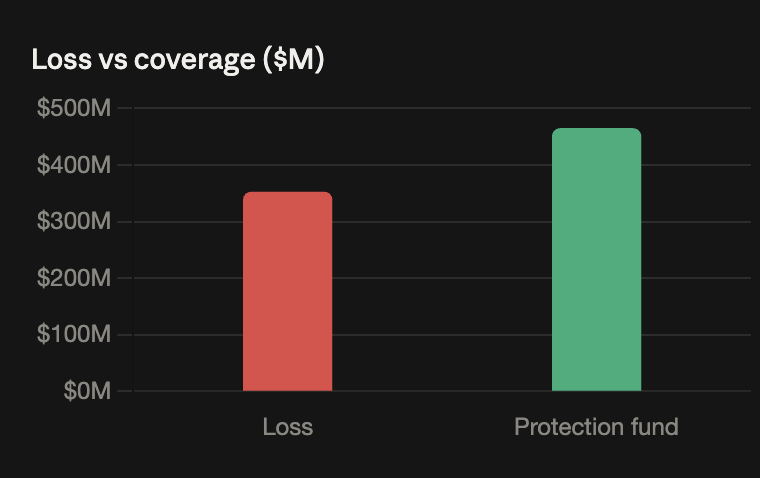
🔹 THE EVENT: Bitget confirms the loss of $351.6 MILLION in the attack. CEO Gracy Chen clarifies one key point: THEY NEVER stole private keys or from vaults. The hackers compromised the wallet backend system, falsified documentation and transaction data, and the fraudulent transfers went through the platform’s own authorization system 🔒
🔹 KEY FACTS:
- 💥 $351.6 MILLION lost — one of the biggest incidents of the year
- 📄 They didn’t steal private keys — the attack was through manipulation of the internal system
- ✅ The protection fund covers everything — $464 million available for full refunds
- 🔍 Binance is collaborating in the tracking — security teams are working to recover funds
🔹 WHAT THIS MEANS FOR YOU:
- ✅ It wasn’t a user security failure — it was an internal exchange failure
- ✅ The protection fund covers 100% of what was lost — users don’t lose their funds
- ⚠️ But trust is broken — if they can falsify transactions, what else is at risk?
- ✅ Reminder: internal and external audits are vital. If the system can be manipulated like this, the risk is real
💡 The hardest lesson: it’s not enough to protect the keys. If the internal infrastructure can be compromised, even funds in "cold storage" are exposed. The risk isn’t only outside—it’s also inside.
📢 What do you think? Does it give you confidence that the fund covers everything, or are you more concerned that they falsified the data? Comment 👇
🐦🔥 HadesCripto
#Bitget #Cybersecurity #CryptoHacking #DigitalSecurity #HadesCripto
📌 Source: Binance News
📅 September 25, 2026
🔹 THE EVENT: Bitget confirms the loss of $351.6 MILLION in the attack. CEO Gracy Chen clarifies one key point: THEY NEVER stole private keys or from vaults. The hackers compromised the wallet backend system, falsified documentation and transaction data, and the fraudulent transfers went through the platform’s own authorization system 🔒
🔹 KEY FACTS:
- 💥 $351.6 MILLION lost — one of the biggest incidents of the year
- 📄 They didn’t steal private keys — the attack was through manipulation of the internal system
- ✅ The protection fund covers everything — $464 million available for full refunds
- 🔍 Binance is collaborating in the tracking — security teams are working to recover funds
🔹 WHAT THIS MEANS FOR YOU:
- ✅ It wasn’t a user security failure — it was an internal exchange failure
- ✅ The protection fund covers 100% of what was lost — users don’t lose their funds
- ⚠️ But trust is broken — if they can falsify transactions, what else is at risk?
- ✅ Reminder: internal and external audits are vital. If the system can be manipulated like this, the risk is real
💡 The hardest lesson: it’s not enough to protect the keys. If the internal infrastructure can be compromised, even funds in "cold storage" are exposed. The risk isn’t only outside—it’s also inside.
📢 What do you think? Does it give you confidence that the fund covers everything, or are you more concerned that they falsified the data? Comment 👇
🐦🔥 HadesCripto
#Bitget #Cybersecurity #CryptoHacking #DigitalSecurity #HadesCripto