

The crypto community remains on maximum alert after Bitget’s security incident. New statements from CEO Gracy Chen and on-chain analyses have brought to light crucial information about the suspects and the dynamics of the breach:
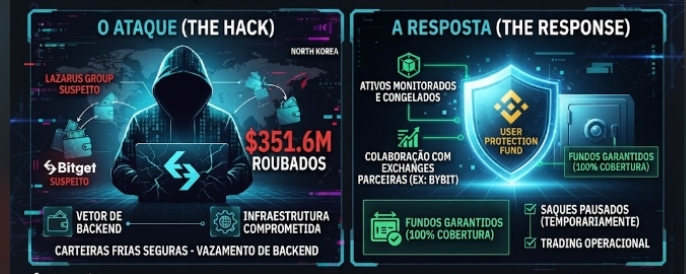
Main Suspect (North Korea / Lazarus Group): Bitget’s CEO publicly pointed to indications of a strong link with North Korean hackers (DPRK). The suspicion was raised after tracking IP addresses and identical VPN patterns to those used in previous attacks attributed to the regime. Independent on-chain researchers also traced part of the funds to addresses associated with hacker networks such as TraderTraitor.
How did the attack happen? (Technical Details):
The management has dismissed the leakage of private keys. The cold wallets remain completely secure and isolated.
The attack vector consisted of compromising a backend system of the wallet management infrastructure. The attackers were able to tamper with transaction-signing processes without needing to forge withdrawal requests from ordinary customers.
The hypothesis of internal involvement (inside job) was initially ruled out by the board, although forensic investigations are still ongoing.
to.
Recovery and Current Status:
A portion of the stolen assets is already being monitored, and joint efforts with other major exchanges (such as Bybit, which offered support) are underway to freeze destination addresses.
The User Protection Fund (a fund of more than US$ 464 million) continues to be guaranteed to cover 100% of the losses of affected users.
Withdrawals are temporarily paused as a precaution while the team strengthens its security barriers, but trading and deposits operate normally.
.
A complete technical report (post-mortem) detailing the exact root cause and the progress of the funds recovery should be released soon.
#Bitget #LazarusGroup #CriptoNoticias #SegurancaCripto #BinanceSquare $BTC $AVAX
