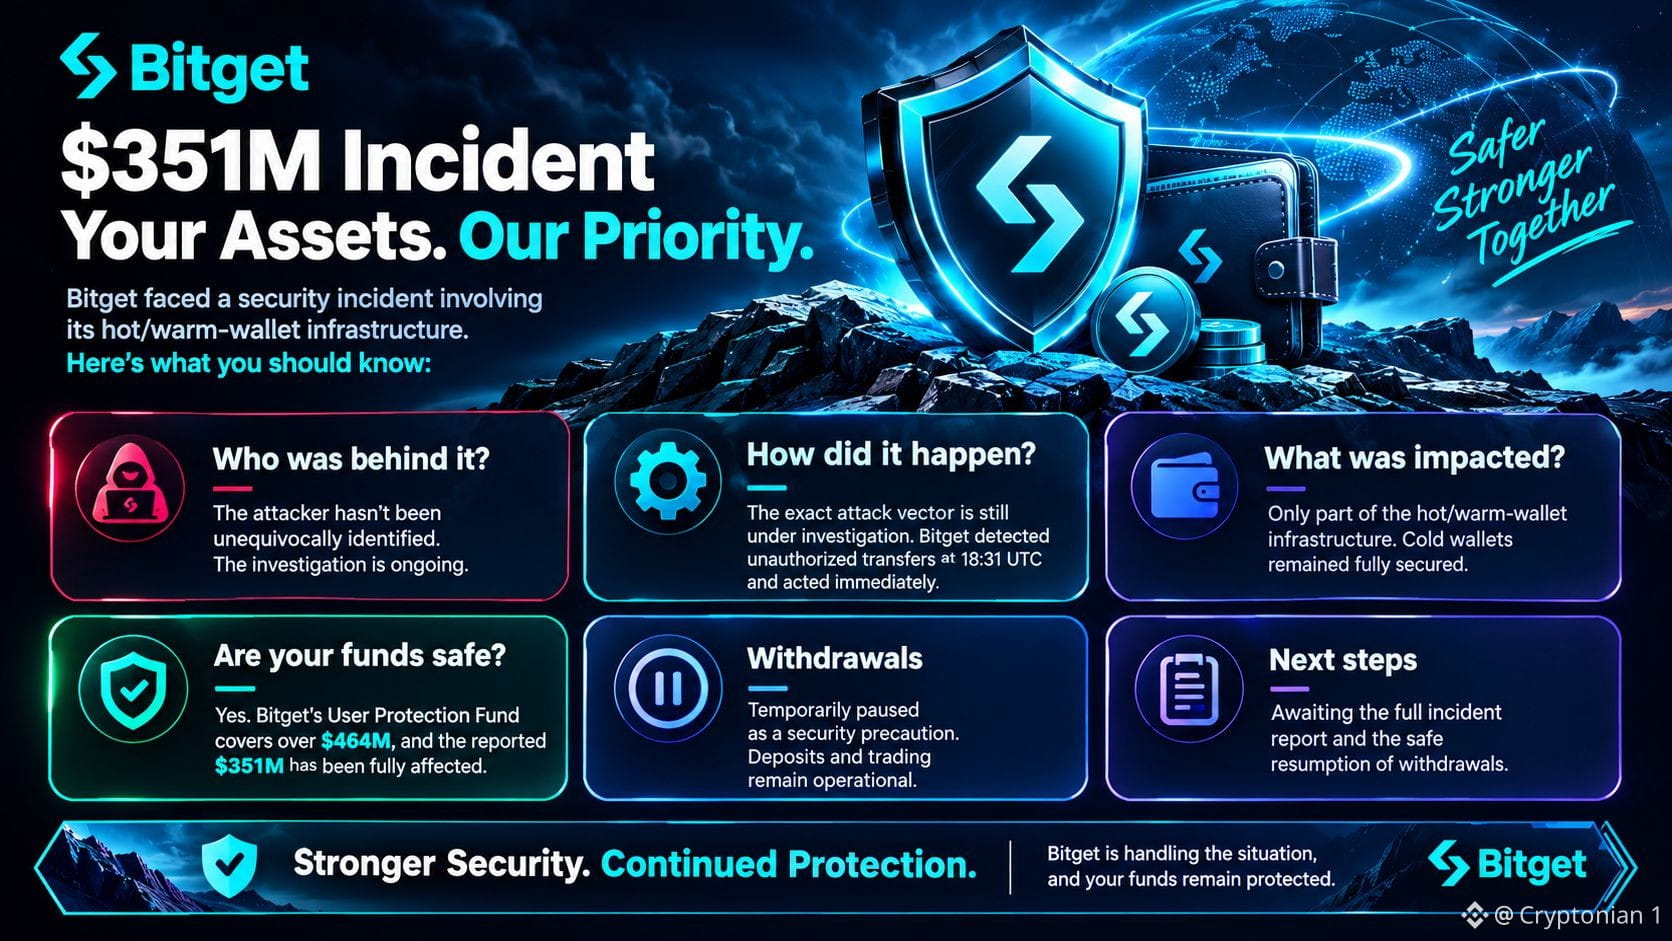
Looks like North Korean hackers are the prime suspects behind Bitget’s $351M hit, based on IP trails and attack patterns the CEO flagged. They didn’t steal private keys, instead they broke into a backend wallet system, spoofed transfer data, and tricked the authorization process into dumping funds from hot and warm wallets. User funds should be fine since Bitget’s $464M protection fund covers the whole loss and cold wallets including $BTC stayed locked down, though withdrawals are paused while they clean up.
$ETH #BTC Price Analysis# #ETH
$ETH #BTC Price Analysis# #ETH