One more reminder: the risk may not be on the chain—it may first be hidden in your phone.
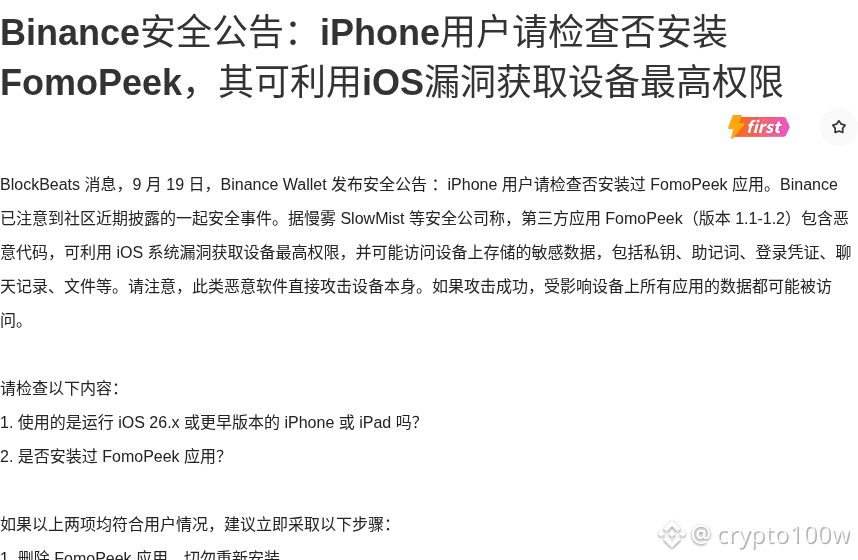
BlockBeats cites a Binance security notice stating that a third-party app, FomoPeek version 1.1–1.2, was exposed by security organizations such as SlowMist for containing embedded malicious code. It can exploit an iOS vulnerability to obtain the highest permissions on the device, thereby accessing sensitive data including private keys, seed phrases, login credentials, chat records, and files. The main impact is on iPhone/iPad users—especially devices running iOS 26.x or below and that have installed FomoPeek.
What’s frightening about this kind of device-level attack is that it does not target an individual app. If the attack succeeds, data from all apps on the affected device may be accessed. On the surface, one scenario is that self-custody wallet security is amplified; another is that multiple wallets and accounts across multiple exchanges are simultaneously exposed to risk on the same device.
If you’re using an iPhone/iPad, would you first check whether FomoPeek is installed, or would you first update your system and clean your device?
Figure 1: FomoPeek was exposed for embedding malicious code · Partial screenshot of the source page
Image source: https://www.theblockbeats.info/flash/368030