Radix discloses authorization vulnerability in asset vault
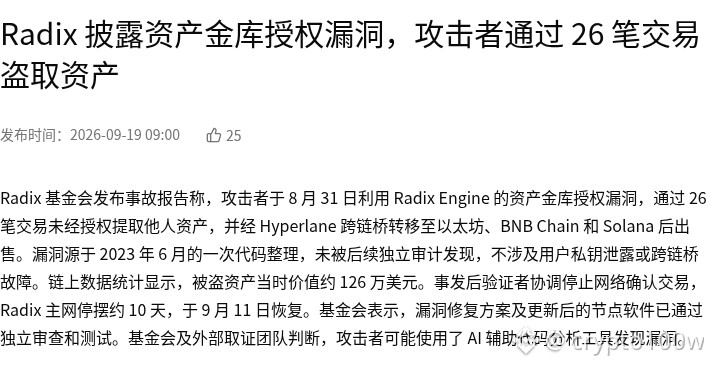
The Radix Foundation disclosed details of an asset vault authorization vulnerability on August 31: the attacker exploited a flaw in Radix Engine permission checks to withdraw user and dApp assets through 26 unauthorized transactions, and then routed them out via Hyperlane cross-chain transfers. The team says the vulnerability has been fixed and the incident is now in the recovery and forensic investigation stage. The market interpretation is bearish for XRD.
The issue lies in the execution layer rather than a single application or leaked private key—it targets the most core asset security trust of the public chain. Even after the fix is completed, traders may reprice the security discount for the Radix ecosystem. In the short term, the focus is whether funds will flow back after the mainnet resumes, whether exchange functions are restored, and whether ecosystem TVL can stop falling.
Source: Wu Shuo
#XRD
Figure 1: Radix discloses authorization vulnerability in asset vault · Partial screenshot of the source page
Image source: https://www.wublock123.com/news/radix-vault-authorization-bug-attacker-stole-assets-26-transactions-68645
The Radix Foundation disclosed details of an asset vault authorization vulnerability on August 31: the attacker exploited a flaw in Radix Engine permission checks to withdraw user and dApp assets through 26 unauthorized transactions, and then routed them out via Hyperlane cross-chain transfers. The team says the vulnerability has been fixed and the incident is now in the recovery and forensic investigation stage. The market interpretation is bearish for XRD.
The issue lies in the execution layer rather than a single application or leaked private key—it targets the most core asset security trust of the public chain. Even after the fix is completed, traders may reprice the security discount for the Radix ecosystem. In the short term, the focus is whether funds will flow back after the mainnet resumes, whether exchange functions are restored, and whether ecosystem TVL can stop falling.
Source: Wu Shuo
#XRD
Figure 1: Radix discloses authorization vulnerability in asset vault · Partial screenshot of the source page
Image source: https://www.wublock123.com/news/radix-vault-authorization-bug-attacker-stole-assets-26-transactions-68645