🔸 S&P Global buys the auditor
The company that audits the code S&P wants to rate. Signed today, price not disclosed, which usually means the number was big enough to be awkward)
What OpenZeppelin is, for anyone who knows the name only as an import line:
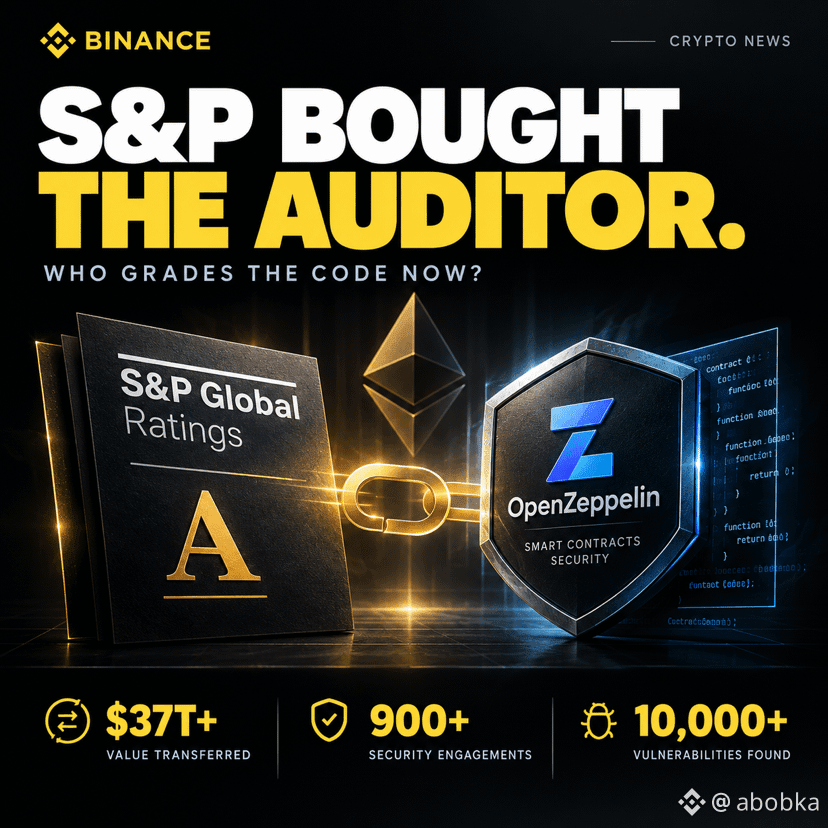
🔸 more than 37 trillion dollars has moved through their Contracts library
🔸 900+ security engagements
🔸 10,000+ vulnerabilities found before anything hit production
The library itself is fine:
open source, permanently
every released version stays up and nobody can withdraw it
Brener stays CEO, audits keep running
the whole thing just reports into S&P Global Ratings now
The conflict:
the group that wants to grade your contract risk now owns the shop that finds it. Le Pallec at S&P Ratings says the plan out loud, that OpenZeppelin complements their onchain risk assessment. No mystery about it.
Audits don't get worse overnight. The customer changed, though. An audit is something a protocol buys for itself and publishes. A grade gets sold to the institution on the other side, and that buyer wants one letter, not a list.
That's the direction for everything settling on $ETH rails: tokenized funds, stablecoins, treasury desks. Someone was always going to price smart contract risk. Turns out it's the credit guys, and they bought the toolmaker instead of building one.
Smart buy on their side, honestly. Just read the audit and the grade as two documents, because from today they share a parent.
Would you take an S&P grade over the audit itself?
#snp500 #S&P500
The company that audits the code S&P wants to rate. Signed today, price not disclosed, which usually means the number was big enough to be awkward)
What OpenZeppelin is, for anyone who knows the name only as an import line:
🔸 more than 37 trillion dollars has moved through their Contracts library
🔸 900+ security engagements
🔸 10,000+ vulnerabilities found before anything hit production
The library itself is fine:
open source, permanently
every released version stays up and nobody can withdraw it
Brener stays CEO, audits keep running
the whole thing just reports into S&P Global Ratings now
The conflict:
the group that wants to grade your contract risk now owns the shop that finds it. Le Pallec at S&P Ratings says the plan out loud, that OpenZeppelin complements their onchain risk assessment. No mystery about it.
Audits don't get worse overnight. The customer changed, though. An audit is something a protocol buys for itself and publishes. A grade gets sold to the institution on the other side, and that buyer wants one letter, not a list.
That's the direction for everything settling on $ETH rails: tokenized funds, stablecoins, treasury desks. Someone was always going to price smart contract risk. Turns out it's the credit guys, and they bought the toolmaker instead of building one.
Smart buy on their side, honestly. Just read the audit and the grade as two documents, because from today they share a parent.
Would you take an S&P grade over the audit itself?
#snp500 #S&P500