#dusk $DUSK @Dusk
At first I thought Citadel 2’s adoption test was whether users wanted private credentials. Looking closer at @DuskFoundation, I found a practical question: its complete JavaScript SDK remains “available soon.”
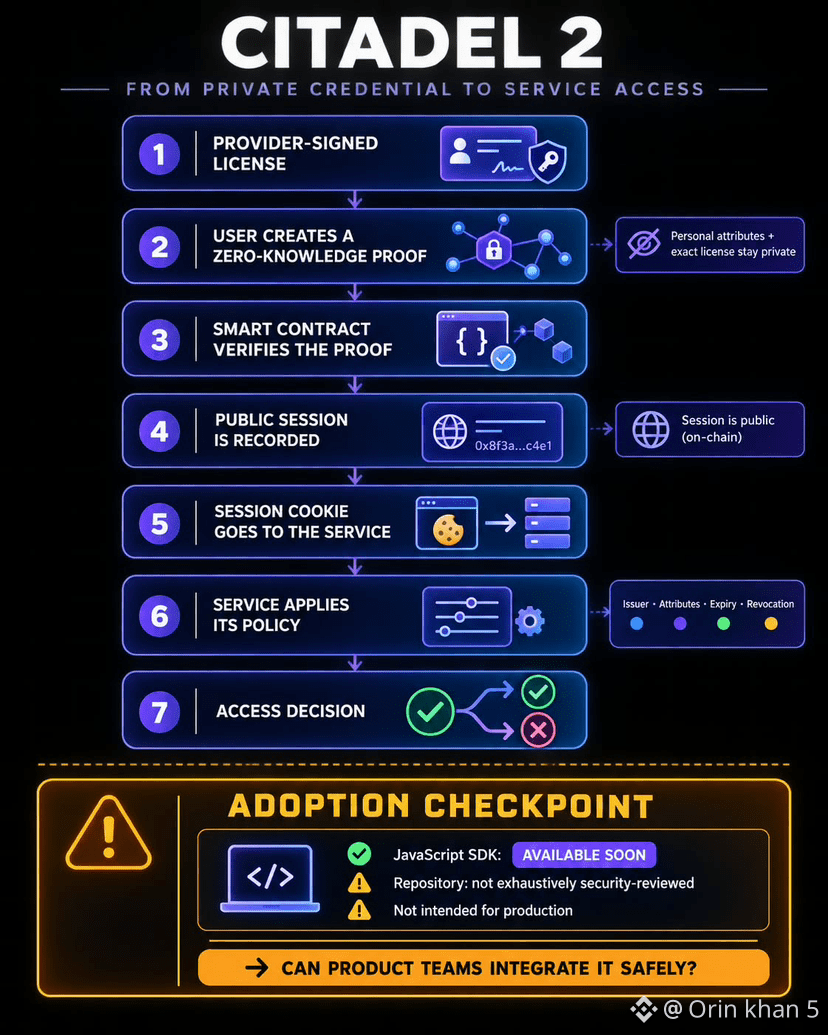
Citadel 2 lets someone prove they hold a registered, provider-signed license without placing personal attributes—or the exact license used—on-chain. A contract verifies the zero-knowledge proof and records a public session. The user then gives a session cookie to a service, which decides which issuers and attributes it accepts, plus expiry and revocation rules.
That is what I like about this approach. Privacy does not remove the service’s control. But careful cryptography matters little if ordinary product teams cannot integrate it safely. Dusk’s repository currently says the code has not undergone an exhaustive security review and is not intended for production.
The SDK will test more than convenience: it will test whether this design can reach real workflows.
Would you choose flexible policy controls or the simplest possible integration?
At first I thought Citadel 2’s adoption test was whether users wanted private credentials. Looking closer at @DuskFoundation, I found a practical question: its complete JavaScript SDK remains “available soon.”
Citadel 2 lets someone prove they hold a registered, provider-signed license without placing personal attributes—or the exact license used—on-chain. A contract verifies the zero-knowledge proof and records a public session. The user then gives a session cookie to a service, which decides which issuers and attributes it accepts, plus expiry and revocation rules.
That is what I like about this approach. Privacy does not remove the service’s control. But careful cryptography matters little if ordinary product teams cannot integrate it safely. Dusk’s repository currently says the code has not undergone an exhaustive security review and is not intended for production.
The SDK will test more than convenience: it will test whether this design can reach real workflows.
Would you choose flexible policy controls or the simplest possible integration?