I was looking into how identity checks could work onchain, and something about Dusk’s approach made me stop and think. 👀
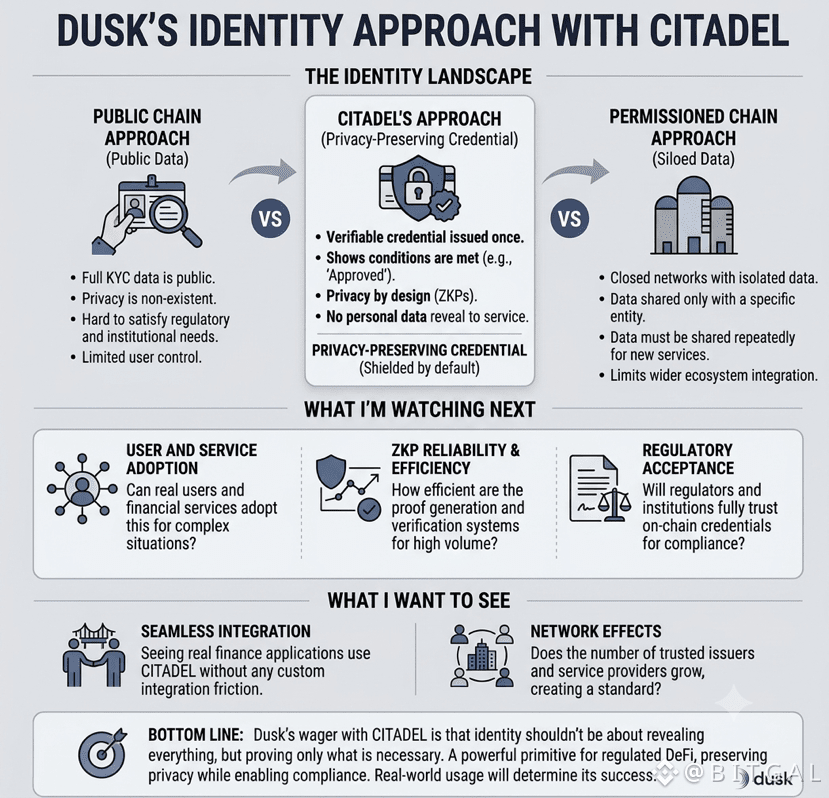
Usually, when a service asks for KYC, you give them your personal information and trust them to handle it properly. Then another service comes along and may ask for much of the same information again. That can become uncomfortable pretty quickly.
CITADEL takes an interesting approach to this. Instead of treating your personal information as something that needs to be passed around again and again, a verified user can have a credential that shows they meet the required conditions.
What I like about that idea is the separation between proving something and revealing everything. A financial service may need to know that you are approved to use it without needing access to every detail from your original identity check. 🔐
That could be a useful piece of infrastructure for regulated applications, especially as more financial activity moves onchain.
I’m still interested in seeing how this works outside the concept itself, because real users and real financial services will bring a lot more situations to deal with.
But the basic idea makes sense to me.
Why reveal more personal information than a service actually needs? 🤔
@Dusk $DUSK #dusk
Usually, when a service asks for KYC, you give them your personal information and trust them to handle it properly. Then another service comes along and may ask for much of the same information again. That can become uncomfortable pretty quickly.
CITADEL takes an interesting approach to this. Instead of treating your personal information as something that needs to be passed around again and again, a verified user can have a credential that shows they meet the required conditions.
What I like about that idea is the separation between proving something and revealing everything. A financial service may need to know that you are approved to use it without needing access to every detail from your original identity check. 🔐
That could be a useful piece of infrastructure for regulated applications, especially as more financial activity moves onchain.
I’m still interested in seeing how this works outside the concept itself, because real users and real financial services will bring a lot more situations to deal with.
But the basic idea makes sense to me.
Why reveal more personal information than a service actually needs? 🤔
@Dusk $DUSK #dusk