Author: Vitalik
Organization & Translation | RuoYan
Original link: https://vitalik.eth.limo/general/2025/09/24/openness_and_verifiability.html
Statement: This article is a reprinted content. Readers can obtain more information through the original link. If the author has any objections to the form of reprinting, please contact us, and we will modify it according to the author's requirements. Reprinting is for information sharing only and does not constitute any investment advice, nor does it represent Wu's views and positions.
The biggest trend of this century can be summarized as "the internet has become a reality in our lives." From email to instant messaging, from digital finance to health tracking, and the upcoming brain-computer interfaces, our daily lives are becoming fully digitalized. However, this digitization brings immense opportunities and risks. Vitalik Buterin explores in this article why we need true openness and verifiability across the entire technology stack (software, hardware, and biotechnology) and how to build a safer, freer, and more equal digital future.
The internet is reality.
The biggest trend of this century so far can be summarized as "the internet has become reality." It started with email and instant messaging. Private conversations that took place through mouths, ears, pens, and paper for thousands of years are now running on digital infrastructure. Then we welcomed digital finance—both including crypto finance and the digitization of traditional finance itself. Next is our health: thanks to smartphones, personal health tracking watches, and data inferred from purchasing behavior, various information about our bodies is being processed through computers and computer networks. In the next twenty years, I expect this trend to permeate various other fields, including various government processes (eventually even voting), monitoring of physical and biological indicators and threats in public environments, and ultimately, through brain-computer interfaces, even our own thoughts.
I believe these trends are inevitable; their benefits are too great, and in a highly competitive global environment, civilizations that reject these technologies will first lose competitiveness, then lose sovereignty. However, in addition to providing significant benefits, these technologies profoundly influence the power dynamics within and between nations.
The civilizations that benefit the most from the wave of new technologies are not those that consume technology but those that produce technology. Central planning access programs aimed at equal access to locked platforms and APIs can only provide a small part of it and will fail in situations outside the predetermined "normal" range. Furthermore, this future involves a significant amount of trust in technology. If this trust is broken (e.g., backdoors, security failures), we will face real problems. Even the mere possibility that this trust could be broken would force people back into fundamentally exclusive social trust models ("Is this thing built by someone I trust?"). This creates an incentive to rise: the sovereign is the one who decides the state of exception.
Avoiding these issues requires technologies with two interwoven attributes throughout the tech stack—software, hardware, and biology: true openness (i.e., open source, including free licensing) and verifiability (including, ideally, direct verification by end users).
The internet is reality. We want it to be a utopia, not a dystopia.
The importance of openness and verifiability in the health sector.
We saw the consequences of unequal access to the means of technological production during the COVID-19 pandemic. Vaccines were produced in only a handful of countries, leading to significant disparities in when different countries received vaccines [1]. Wealthier countries received the top vaccines in 2021, while others received lower-quality vaccines in 2022 or 2023. Initiatives have attempted to ensure equal access [2], but because vaccines were designed to rely on capital-intensive proprietary manufacturing processes that can only be conducted in a few places, these initiatives can only do so much.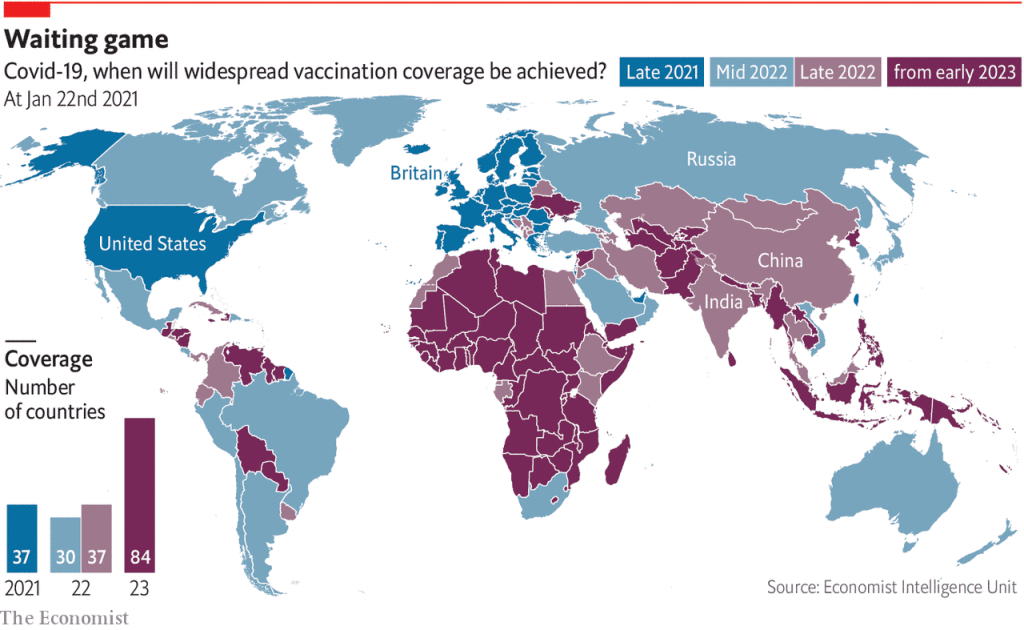
COVID-19 vaccine coverage from 2021-2023.
The second major issue with vaccines is the lack of transparency [3] in science and communication strategies [4], trying to pretend to the public that they carry literally zero risks or downsides, which is untrue and ultimately greatly fueled [5] distrust [6]. Today, this distrust has spiraled upward and feels like a rejection of half a century of science.
In fact, both of these issues are solvable. Vaccines developed with lower costs and more open manufacturing processes, like those funded by Balvi [7] and PopVax [8], reduce access inequality while making it easier to analyze and verify their safety and efficacy. We can go further in designing vaccines for verifiability.
Similar issues apply to the digital aspects of biotechnology. When you talk to longevity researchers, the first thing you typically hear is that the future of anti-aging medicine is personalized and data-driven. To know what medications and nutritional changes should be recommended for someone today, you need to understand their current bodily condition. If massive amounts of digital data can be collected and processed in real time, this would be even more effective.
The internet is reality. We want it to be a utopia, not a dystopia.
The same idea also applies to defensive biotechnology aimed at preventing risks, such as combating pandemics. The sooner a pandemic is detected, the more likely it is to be stopped at its source—even if it cannot be, each week gives more time to prepare and start developing countermeasures. During a pandemic, being able to know where people are getting sick so countermeasures can be deployed in real-time is of great value. If ordinary people infected with a pandemic know this and self-isolate within an hour, it means the spread is 72 times less than if they spread it to others for three days. If we know which 20% of locations are responsible for 80% of the spread, improving air quality there can yield further benefits. All of this requires (i) a large number of sensors, and (ii) the ability for sensors to communicate in real-time to provide information to other systems.
If we move further towards a 'sci-fi' direction, we encounter brain-computer interfaces that can enable massive productivity, help people understand each other better through telepathy, and unlock a safer path to highly intelligent AI.
If the infrastructure for biological and health tracking (personal and spatial) is proprietary, then the data defaults to large companies. These companies have the ability to build various applications on top of it, while others cannot. They may provide access through APIs, but API access will be limited and used for monopoly rent extraction and can be revoked at any time. This means that a few people and companies can access the most important components of the 21st century's major technological fields, which in turn limits who can gain economic benefits from it.
On the other hand, if this personal health data is insecure, hackers could exploit any health issues to blackmail you, optimizing insurance and healthcare product pricing to extract value from you, and if the data includes location tracking, they know where to wait to kidnap you. In another direction, your location data (which is very [9] often hacked [10]) can be used to infer information about your health. If your BCI is hacked, that means hostile actors are literally reading (or worse, writing) your thoughts. This is no longer science fiction: see here [11] to understand how BCI hacks can lead to someone losing motor control.
Overall, huge benefits but also significant risks: emphasizing openness and verifiability is very well-suited to mitigate those risks.
The importance of openness and verifiability in personal and commercial digital technologies.
Earlier this month, I had to fill out and sign a form required for a legal function. At that time, I was not in the country. There is a national electronic signature system, but I had not set it up at that time. I had to print the form, sign it, walk to a nearby DHL, spend a lot of time filling out a paper form, and then pay the fee to have it expedited to the other side of the world. Time required: half an hour, cost: $119. On the same day, I had to sign a (digital) transaction to execute an action on the Ethereum blockchain. Time required: 5 seconds, cost: $0.10 (fairly speaking, without the blockchain, the signature could be completely free).
These stories are easily found in areas such as corporate or nonprofit governance, intellectual property management, etc. Over the past decade, you can find them in a significant portion of the pitch materials from all blockchain startups. Beyond that, there is the mother of all use cases for 'digitally exercising personal authority': payments and finance.
Of course, all of this carries substantial risks: what happens if software or hardware is hacked? This is a risk that the crypto space recognized early on: blockchain is permissionless and decentralized, so if you lose access to funds [12], there are no resources, no uncle in the sky to turn to. Not your keys, not your coins. For this reason, the crypto space early on considered multi-signature [13] and social recovery wallets [14], as well as hardware wallets [15]. However, in reality, there are many situations where the lack of a trustworthy uncle in the sky is not an ideological choice but an inherent part of the scenario. In fact, even in traditional finance, the 'uncle in the sky' cannot protect most people: for example, only 4% of scam victims recover their losses [16]. In use cases involving the custody of personal data, recovery from leaks is impossible even in principle. Therefore, we need real verifiability and security—verifiability and security of software and ultimately hardware.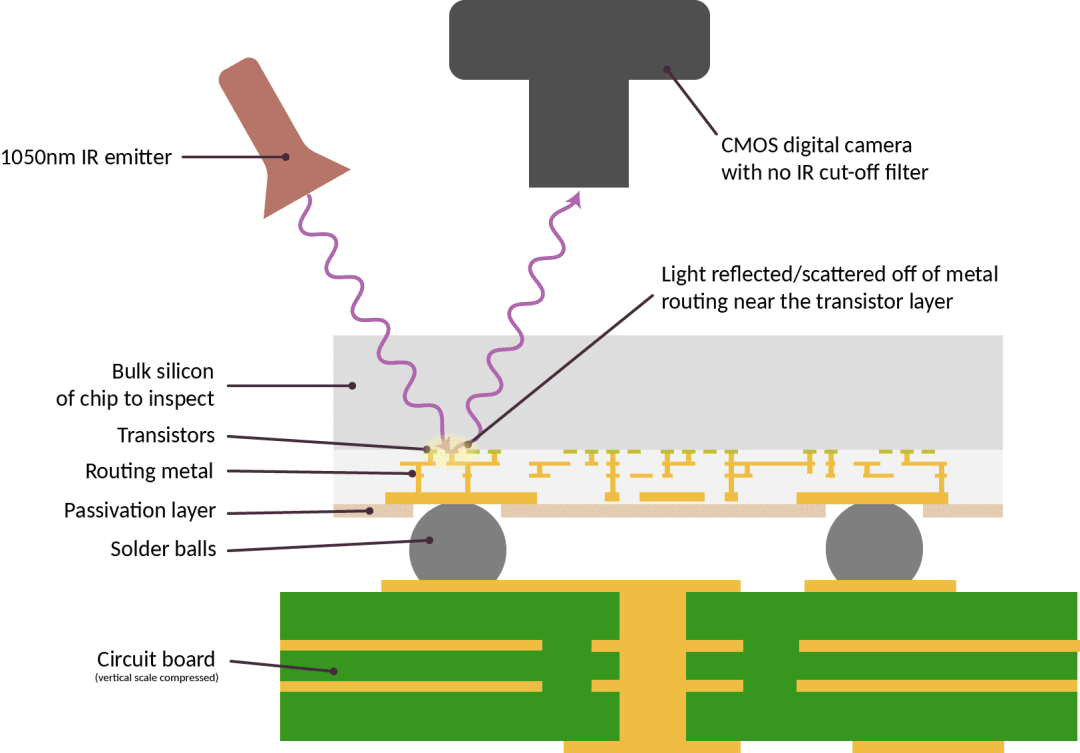
A proposed technology for checking whether computer chips are manufactured correctly.
Importantly, in the case of hardware, the risks we are trying to prevent far exceed 'Is the manufacturer evil?'. Rather, the issue is that there are many dependencies, most of which are closed source, any one of which could lead to unacceptable security outcomes. This paper shows recent examples [18] illustrating how microarchitecture choices can compromise side-channel resistance in designs that are provably secure in models that only look at software. Attacks like EUCLEAK [19] rely on vulnerabilities that are harder to discover due to how many components are proprietary. AI models, if trained on compromised hardware [20], can have backdoors inserted during training.
Another issue in all of these cases is the drawbacks of closed and centralized systems, even if they are completely secure. Centralization creates ongoing leverage between individuals, companies, or nations: if your core infrastructure is built and maintained by potentially untrustworthy companies from potentially untrustworthy nations, you are vulnerable to pressure (e.g., see Henry Farrell on weaponizing interdependence [21]). This is the problem that cryptography aims to solve—but it exists in more areas than finance.
The importance of openness and verifiability in digital citizenship technologies.
I often talk with various individuals trying to find better forms of governance for various situations of the 21st century. Some, like Audrey Tang [22], are trying to elevate already functional political systems to the next level by empowering local open-source communities and using mechanisms like citizens' assemblies, lotteries, and secondary voting. Others start from scratch: here is a [23] recent constitution proposed for Russia by some political scientists born in Russia, featuring strong guarantees of personal freedom and local autonomy, a strong institutional bias for peace against aggression, and unprecedented direct democratic strong roles. Others, such as economists working on land value tax [24] or congestion pricing, try to improve the economics of their countries.
Different individuals may have varying degrees of enthusiasm for each idea. But they all have one thing in common: they all involve high-bandwidth participation, so any realistic implementation must be digital. Pen and paper are fine for basic records of who owns what and elections held every four years, but not for anything that requires us to input at a higher bandwidth or frequency.
However, historically, security researchers' acceptance of ideas like electronic voting has ranged from skepticism to hostility. Here is a good summary [25] of the case against electronic voting. Quoting the document:
First, the technology is 'black box software,' meaning the public is not allowed access to the software controlling the voting machines. While companies protect their software to prevent fraud (and outcompete rivals), it also means the public does not know how the voting software works. It would be easy for a company to manipulate the software to produce fraudulent results. Furthermore, the vendors selling the machines compete with each other, with no guarantee that they are producing machines in the best interests of voters and the accuracy of ballots.
There are many real-world cases [26] that demonstrate that this skepticism is reasonable.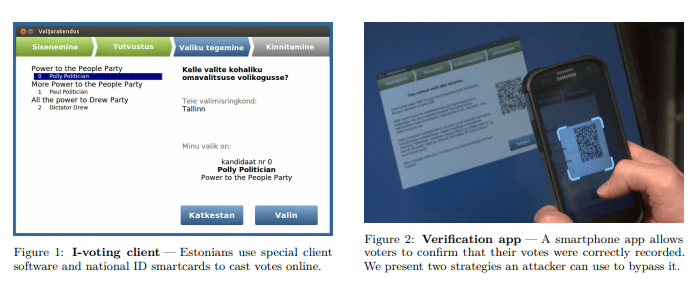
A critical analysis of Estonia's online voting in 2014 [27].
These arguments apply word-for-word in all other cases. But I predict that as technology advances, the response of 'let's just not do it' will become increasingly unrealistic across a wide range of fields. The world is rapidly becoming more efficient due to technology (for better or worse), and I predict that any system that does not follow this trend will become increasingly irrelevant to individual and collective affairs as people bypass it. Therefore, we need an alternative: truly doing the hard work of figuring out how to make complex technological solutions secure and verifiable.
In theory, 'secure and verifiable' and 'open source' are two different things. Certain things can be proprietary and secure, which is absolutely possible: airplanes are highly proprietary technology, but overall commercial aviation is a very safe way to travel [28]. What proprietary models cannot achieve is shared knowledge of security—the ability to be trusted by actors who do not trust each other.
Citizen systems like elections are a case where shared knowledge security is crucial. Another instance is evidence collection in court. Recently, in Massachusetts, a large amount of breathalyzer evidence was ruled inadmissible [29] because it was discovered that information about testing failures was concealed. Quoting the article:
And so, do all results have failures? No. In fact, in most cases, breathalyzer tests do not have calibration issues. However, because investigators later found that the state crime lab concealed evidence, showing that the problem was more widespread than they stated, Judge Frank Gaziano wrote that the due process rights of all these defendants were violated.
Due process in court is essentially a field that not only requires fairness and accuracy but also requires shared knowledge of fairness and accuracy—because without shared knowledge, the court can easily fall into a spiral of people taking matters into their own hands.
In addition to verifiability, openness itself has intrinsic benefits. Openness allows local communities to design governance, identity, and other needs in ways that align with local goals. If the voting system is proprietary, then countries (or provinces or towns) wanting to try new systems will face greater difficulties: they must either persuade the company to implement their preferred rules as functionality or start from scratch and do all the work to make it secure. This adds high costs to innovation in political systems.
In any of these areas, a more open-source hacker ethic approach would give more agency to local implementers, whether they are acting as individuals or as part of a government or company. To make this possible, the built open tools need to be widely available, and the infrastructure and codebases need to allow free licenses so that others can build on top of them. To the extent the goal is to minimize power differentials, copyleft is particularly valuable [30].
The last critical area of civic technology that will be important in the coming years is physical security. Surveillance cameras have been ubiquitous over the past two decades, raising many civil liberties concerns. Unfortunately, I predict that the recent rise of drone warfare will make 'not doing high-tech security' no longer a viable option. Even if a country's laws do not infringe on individual liberties, if that country cannot protect you from laws imposed on you by other countries (or rogue companies or individuals), it is meaningless. Drones make such attacks much easier. Therefore, we need countermeasures, potentially involving extensive anti-drone systems [31] and sensors and cameras.
If these tools are proprietary, data collection will be opaque and centralized. If these tools are open and verifiable, then we have a chance to adopt a better approach: secure devices that can prove to output limited data only in limited circumstances and delete the rest. We can have a digitized physical security future, much like a digital watchdog rather than a digital panopticon. One can imagine a world where public surveillance devices are required to be open source and verifiable, and anyone has the legal right to randomly select public surveillance devices and take them apart for verification. University computer science clubs could often conduct this as an educational exercise.
Open source and verifiable methods.
We cannot avoid deeply embedding digital computing things in all aspects of life (both personal and collective). By default, we may end up with digital computing things built and operated by centralized companies, optimized for the profit motives of a few, backdoored by their host country's government, which the majority of the world's population cannot participate in creating or know whether they are secure. But we can strive towards better alternatives. Imagine a world:
· You have a secure personal electronic device—something with phone functionality, the security of an encrypted hardware wallet, and the checkability of a mechanical watch.
· Your messaging applications are all encrypted, message patterns obscured through mixnets, and all code is formally verified. You can be confident that your private communication is indeed private.
· Your finances are standardized ERC20 assets on-chain (or hashes and proofs published to some servers to guarantee correctness) managed by a wallet controlled by your personal electronic device. If you lose the device, they can be recovered through some combination of other devices you choose, family members, friends, or institutional devices (not necessarily the government: if anyone can easily do this, for example, a church could also provide it).
· There is an open-source version of Starlink-like infrastructure, so we have strong global connectivity without relying on a few individual actors.
· You have devices with open-source weight LLM scanning your activities, providing suggestions and auto-completing tasks, and warning you when you might receive misinformation or are about to make a mistake. The operating system is also open-source and formally verified.
· You wear a 24x7 personal health tracking device that is also open-source and checkable, allowing you to obtain data and ensure that no one else is accessing it without your consent.
· We have more advanced forms of governance using lotteries, citizens' assemblies, secondary voting, and generally clever combinations of democratic voting to set goals, along with some method of selecting ideas from experts to determine how to achieve those goals. As a participant, you can actually be confident that the system is implementing the rules in the way you understand.
· Public spaces are equipped with monitoring devices to track biological variables (such as CO2 and AQI levels, the presence of airborne diseases, wastewater). However, these devices (as well as any surveillance cameras and defense drones) are open-source and verifiable, with a legal framework allowing the public to randomly check them.
· This is a world where we have more security, freedom, and global economic equality of access than we do today. But achieving this world requires more investment in various technologies: more advanced forms of cryptography. I refer to ZK-SNARKs, fully homomorphic encryption, and obfuscation as cryptographic Egyptian god cards, as they are so powerful that they allow you to compute arbitrary programs on data in multi-party environments and give guarantees about outputs while keeping data and computations private. This enables more powerful privacy-preserving applications. Adjacent tools of cryptography (such as blockchains to enable applications with strong guarantees that data cannot be tampered with and users cannot be excluded, as well as differential privacy to add noise to data to further protect privacy) also apply here.
· Application and user-level security. Applications are only secure when the security guarantees they make are actually understandable and verifiable to the user. This will involve making software frameworks easy to build applications with strong security properties. Importantly, it will also involve browsers, operating systems, and other intermediaries (like locally running observer LLMs) doing everything they can to verify applications, determine their risk levels, and present this information to users.
· Formal verification. We can use automated proof techniques to algorithmically verify that programs satisfy the properties we care about, such as not leaking data or not being easily subject to unauthorized modification. Lean has recently become a popular language for this. These techniques have already begun to be used to verify ZK-SNARK proof algorithms for Ethereum Virtual Machine (EVM) and other high-value, high-risk use cases in cryptography, and similar usage is seen in the broader world. Beyond that, we need to make further progress in other more mundane security practices.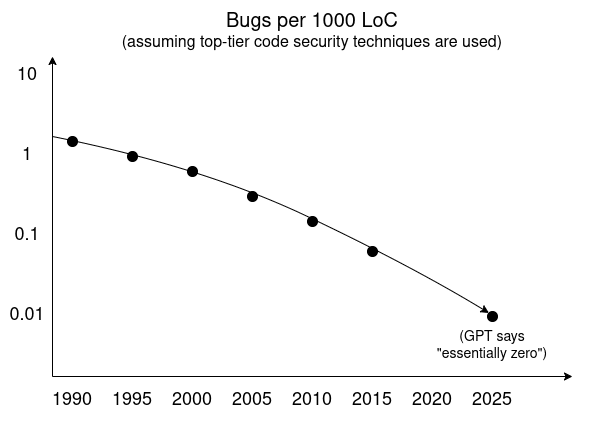
The pessimism about cybersecurity in the 2000s was wrong: vulnerabilities (and backdoors) can be overcome. We 'just need' to learn to prioritize security over other competitive goals.
· Open-source and security-focused operating systems. More and more of these are starting to appear: GrapheneOS as a security-focused version of Android, minimal security-focused kernels like Asterinas, Huawei's HarmonyOS (with an open-source version) is using formal verification (I expect many readers to think 'If it's Huawei, there must be a backdoor,' but this misses the point: as long as it is open, anyone can verify it, who produces it should not matter. This is a great example of how openness and verifiability fight global balkanization) secure open-source hardware. If you cannot be sure that your hardware is indeed running that software and not leaking data separately on the side, then no software is secure. In this regard, I am most interested in two short-term goals:
· Personal secure electronic devices—what blockchain people call 'hardware wallets' and open-source enthusiasts call 'secure smartphones,' which will ultimately converge into the same thing once you understand the need for security and universality.
· Physical infrastructure in public spaces—smart locks, the biological monitoring devices I described above, and general 'IoT' technologies. We need to be able to trust them. This requires openness and verifiability.
· Building secure open-source toolchains for open-source hardware. Today, designing hardware relies on a series of closed-source dependencies. This significantly raises the cost of manufacturing hardware and makes the process more permissive. It also makes hardware verification unrealistic: if the tools that generate the chip designs are closed-source, you do not know what you are verifying. Even tools like scan chains that exist today often cannot be used in practice because too many necessary tools are closed-source. All of this can change.
· Hardware verification (e.g., IRIS and X-ray scanning). We need methods to scan chips to verify that they actually have the logic they are supposed to have and that they do not have extra components that allow for accidental forms of tampering and data extraction. This can be done destructively: auditors randomly order products containing computer chips (using identities that look like ordinary end users) and then take apart the chips and verify that the logic matches. With IRIS or X-ray scanning, it can be done non-destructively, allowing every chip to potentially be scanned.
· Open-source, low-cost, local environmental and biological monitoring devices. Communities and individuals should be able to measure their environments and themselves and identify biological risks. This includes various forms of technology: personal-scale medical devices like OpenWater, air quality sensors, general airborne disease sensors (like Varro), and larger-scale environmental monitoring.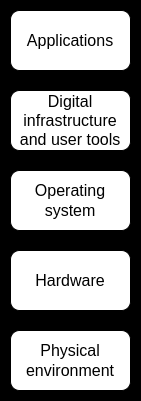
The openness and verifiability across layers of the technology stack is crucial.
From here to there.
The key difference between this vision and more 'traditional' technological visions is that it is more friendly to local sovereignty and individual empowerment and freedom. Security is not achieved by scanning the entire world to ensure there are no bad actors anywhere; it is achieved by making the world more robust at every level. Openness means openness to building and improving every layer of technology, not just open access APIs from central planning. Verification is not reserved for proprietary rubber stamp auditors who may collude with the companies and governments rolling out the technology—it is a right of the people and a social encouragement hobby.
I believe this vision is more robust and aligns better with our fractured global 21st century. But we do not have unlimited time to execute this vision. Centralized approaches involving more centralized data collection and backdoors, reducing verification entirely to 'Is this made by a trusted developer or manufacturer?' are advancing rapidly. Attempts to centralize what should be truly open access have been trying for decades. It may have started with Facebook's internet.org and will continue, each attempt being more complex than the last. We need to act quickly to compete with these methods and demonstrate to people and institutions that better solutions are possible.
If we are able to successfully realize this vision, another way to understand the world we get is that it is a retro-futurism. On one hand, we gain the benefits of more powerful technologies that allow us to improve health, organize ourselves more efficiently and flexibly, and protect ourselves from new and old threats. On the other hand, we get a world that brings back to 1900 each person's second nature attribute: infrastructure that is free to people, can be taken apart, verified, and modified to meet one's needs, where anyone can participate not just as a consumer or 'application builder,' but at any level of the technology stack, anyone can be confident that devices do what they say they do.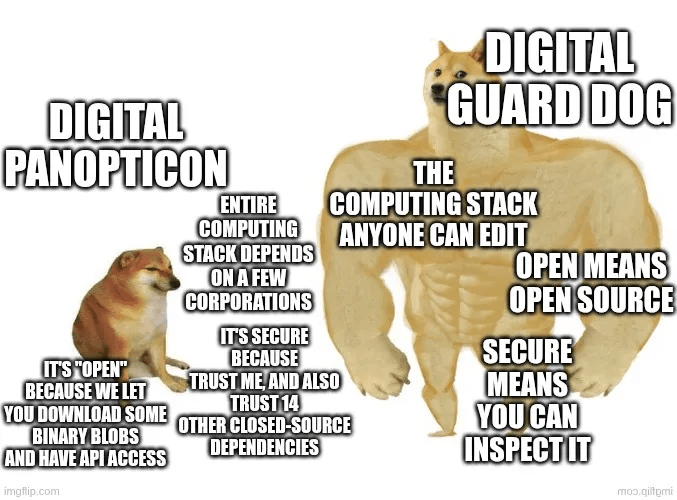
Designing for verifiability comes with costs: many optimizations in hardware and software provide speed gains that are in high demand, but at the expense of making designs harder to understand or more brittle. Open source makes it more challenging to make money under many standard business models. I believe both of these issues are exaggerated—but this is not something the world will be persuaded of overnight. This raises the question: what are the realistic short-term goals?
I will propose an answer: to strive for a fully open-source and verification-friendly technology stack, aimed at high security, non-performance-critical applications—both consumer and institutional, both long-distance and face-to-face. This will include hardware, software, and biology. Most computing that truly needs security does not actually need to be high-speed, even in cases where it does, there are often ways to combine high-performance but untrusted and trusted but low-performance components [32] to achieve high levels of performance and trust for many applications. It is unrealistic to achieve maximum security and openness for everything. But we can first ensure that these properties are available in the truly important areas.
Hyperlinks in the original text.
[1] https://www.ucl.ac.uk/bartlett/news/2025/apr/new-research-finds-substantial-global-disparities-covid-19-vaccine-accessibility
[2] https://www.who.int/initiatives/act-accelerator/covax
[3] https://www.nytimes.com/2021/01/28/world/europe/vaccine-secret-contracts-prices.html
[4] https://jphe.amegroups.org/article/view/9331/html
[5] https://www.transparency.org/en/press/covid-19-vaccines-lack-of-transparency-trials-secretive-contracts-science-by-press-release-risk-success-of-global-response
[6] https://www.sciencedirect.com/science/article/pii/S0264410X24007217
[7] https://x.com/VitalikButerin/status/1567908552714616832
[8] https://popvax.com/
[9] https://www.nbcnews.com/tech/security/location-data-broker-gravy-analytics-was-seemingly-hacked-experts-say-rcna187038
[10] https://www.nytimes.com/interactive/2019/12/19/opinion/location-tracking-cell-phone.html
[11] https://www.sciencedirect.com/science/article/abs/pii/S0165027022002357
[12] https://bitcoinmagazine.com/culture/bitcoin-self-defense-part-i-wallet-protection-1368758841
[13] https://bitcoinmagazine.com/technical/multisig-future-bitcoin-1394686504
[14] https://vitalik.eth.limo/general/2021/01/11/recovery.html
[15] https://www.coinbase.com/en-sg/learn/crypto-basics/what-is-a-hardware-wallet
[16] https://www.gasa.org/post/global-state-of-scams-report-2024-1-trillion-stolen-in-12-months-gasa-feedzai#:~:text=Only%204%25%20of%20Victims%20Recover,more%20effective%20financial%20recovery%20processes.
[17] https://www.bunniestudios.com/blog/2023/infra-red-in-situ-iris-inspection-of-silicon/
[18] https://eprint.iacr.org/2024/574.pdf
[19] https://ninjalab.io/eucleak/
[20] https://arxiv.org/pdf/2304.08411
[21] https://www.brookings.edu/wp-content/uploads/2020/05/9780815738374_ch1.pdf
[22] https://6pack.care/manifesto
[23] https://www.igrec.io/constitution-project
[24] https://www.landisabigdeal.com/
[25] https://cs.stanford.edu/people/eroberts/cs181/projects/2006-07/electronic-voting/index_files/page0002.html
[26] https://apnews.com/article/f6876669cb6b4e4c9850844f8e015b4c
[27] https://jhalderm.com/pub/papers/ivoting-ccs14.pdf
[28] https://www.linkedin.com/pulse/beyond-intuition-why-flying-really-safer-than-driving-philip-mann-15tee
[29] https://www.wbur.org/news/2023/04/27/massachusetts-breathalyzer-court-ruling-newsletter
[30] https://vitalik.eth.limo/general/2025/07/07/copyleft.html
[31] https://www.robinradar.com/resources/10-counter-drone-technologies-to-detect-and-stop-drones-today
[32] https://vitalik.eth.limo/general/2024/09/02/gluecp.html

Article
Vitalik's Blog: Why Do We Need an Open and Verifiable World?


--