



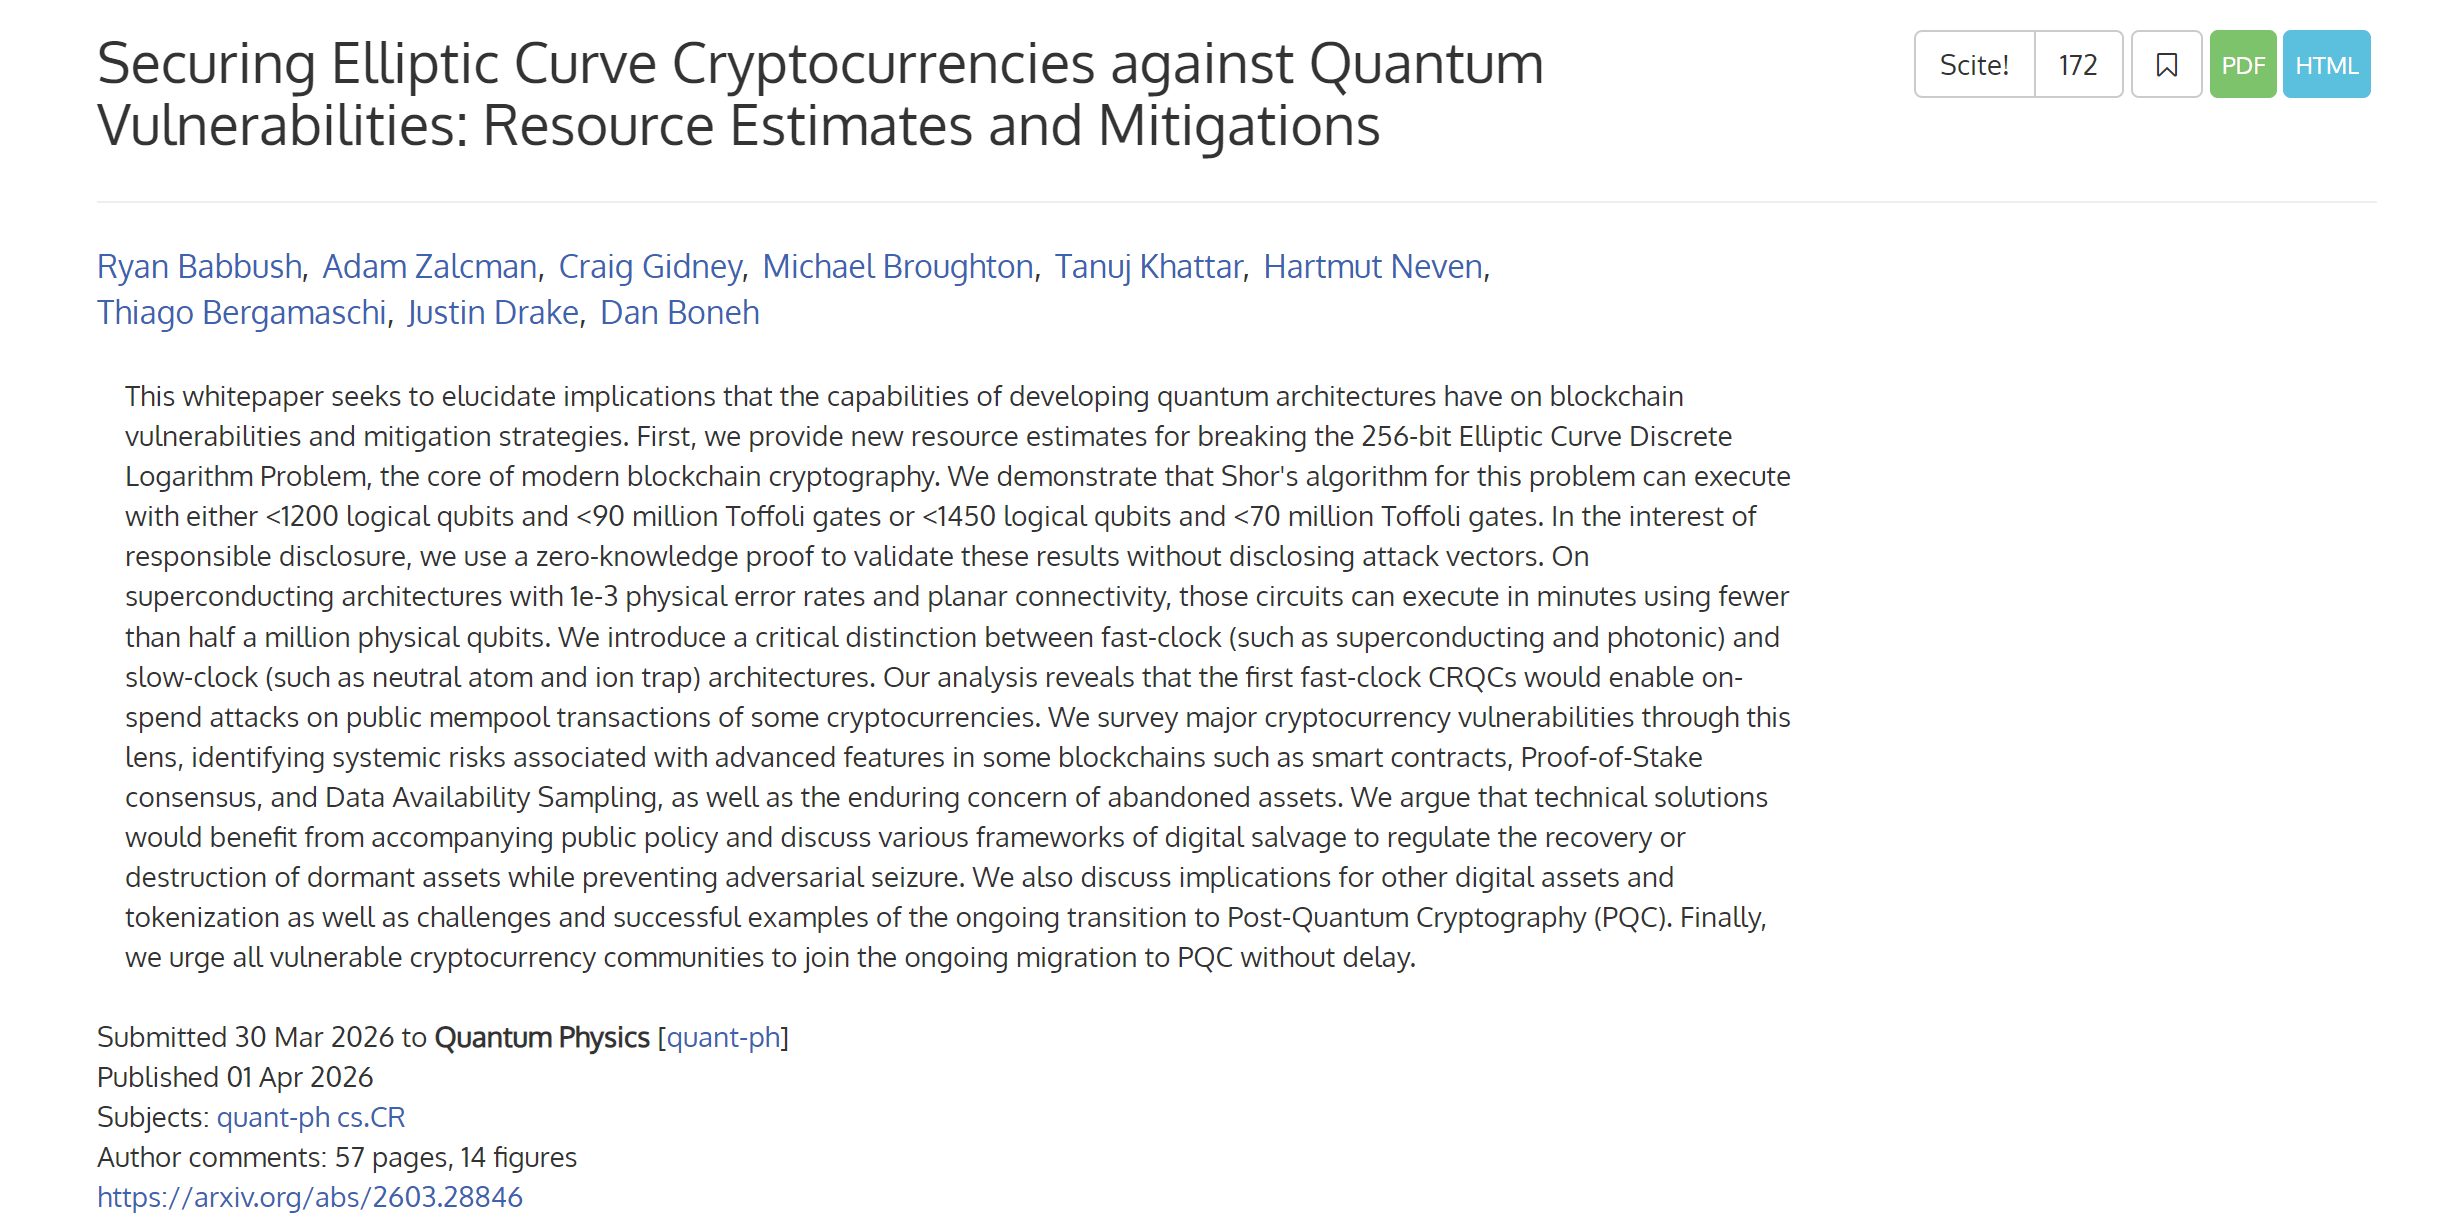
Just last week, the Google Quantum AI team published a groundbreaking paper, stating that under superconducting architecture, specific error correction, and hardware assumptions, future quantum computers could utilize fewer than 500,000 physical qubits to crack the widely used 256-bit elliptic curve cryptography (ECDLP-256) in current cryptocurrencies and blockchains within minutes, reducing the estimated number of required qubits by about 20 times.
This directly points to the core ECDSA signature scheme of almost all mainstream public chains like Bitcoin and Ethereum. Once the news broke, the claim that 'quantum computers could crack Bitcoin private keys' began to spread rapidly online.
In fact, it is necessary for us to calm down first and clarify this matter—while the threat is real, it is still far from 'your wallet will be unsafe tomorrow.'
More importantly, the entire industry has actually begun to take action long ago.
1. What exactly is quantum computing threatening?
To understand this issue, we must start from the most basic place: how is your crypto asset actually being protected?
As we all know, on Bitcoin or Ethereum, each account is backed by a pair of keys: a private key and a public key. The private key is a string of randomly generated large numbers and is extremely confidential, equivalent to the password of your safe; the public key is derived from the private key through elliptic curve multiplication, and your wallet address is a string obtained by compressing the public key through a hash function.
The security basis of this system lies precisely in the fact that this process is one-way.
In the end, deriving a public key from a private key is easy, but deriving a private key from a public key takes far longer on traditional computers than the age of the universe. This is the essence of the 'elliptic curve discrete logarithm problem' (ECDLP)—forward computation is simple, while reverse cracking is impossible.
However, quantum computers break this assumption. They can solve integer factorization and discrete logarithm problems in polynomial time. In other words, a sufficiently powerful quantum computer could theoretically derive your private key from your public key.
So, when will the public key be exposed?
Every time you initiate a transaction on the blockchain, you need to sign the transaction data with your private key while broadcasting your public key for verification, which means that as long as you have made a transaction, your public key has already been exposed on-chain.
The significance of Google's paper is precisely that it has moved the notion of 'cracking private keys from public keys' from a theoretically feasible but absurd idea to a target that can be planned on a quantum hardware roadmap. For example, the paper estimates that cracking a 256-bit ECDLP would require about 500,000 physical qubits of fault-tolerant quantum computer, which is a significant reduction from previous estimates.
Ultimately, quantum computing is not about cracking blockchain; it primarily targets the signature system in blockchain that is still based on the elliptic curve discrete logarithm problem.
Thus, while the threat is real, strictly speaking, the term 'imminent' is not accurate. The mainstream estimate in the industry gives a window period, with the earliest still around 2030 (Extended reading (native account abstraction + quantum threat: Why hasn't EIP-8141 become Ethereum's flagship in Bogotá?)).
2. What preparations are various public chains making?
Of course, from an objective perspective, there is a key distinction that many reports fail to clarify: many Bitcoin addresses do not directly expose the public key on-chain at the beginning.
Taking common forms like P2PKH and P2WPKH as examples, the address itself is usually just a hash of the public key, which often only gets exposed when 'first spent,' meaning that if your address has never made a transaction, there is only your wallet address on-chain, and no public key.
Therefore, the most direct attack surface of quantum computing is more likely to be the public keys of addresses that have already made transactions. Of course, this detail directly leads to the first thing users can do now, which we will discuss later.
The industry is not unaware of this issue; in fact, preparations for post-quantum cryptography migration have already been synchronously advanced on multiple fronts.
Ethereum's response is to decouple the account layer from the signing scheme, such as the advancement of EIP-7702 and account abstraction (AA), allowing Ethereum accounts to define what constitutes a valid signature through smart contract logic. This means that when a post-quantum signing scheme is introduced in the future, there will be no need to rewrite the underlying protocol; only the signature verification module of the account needs to be replaced.
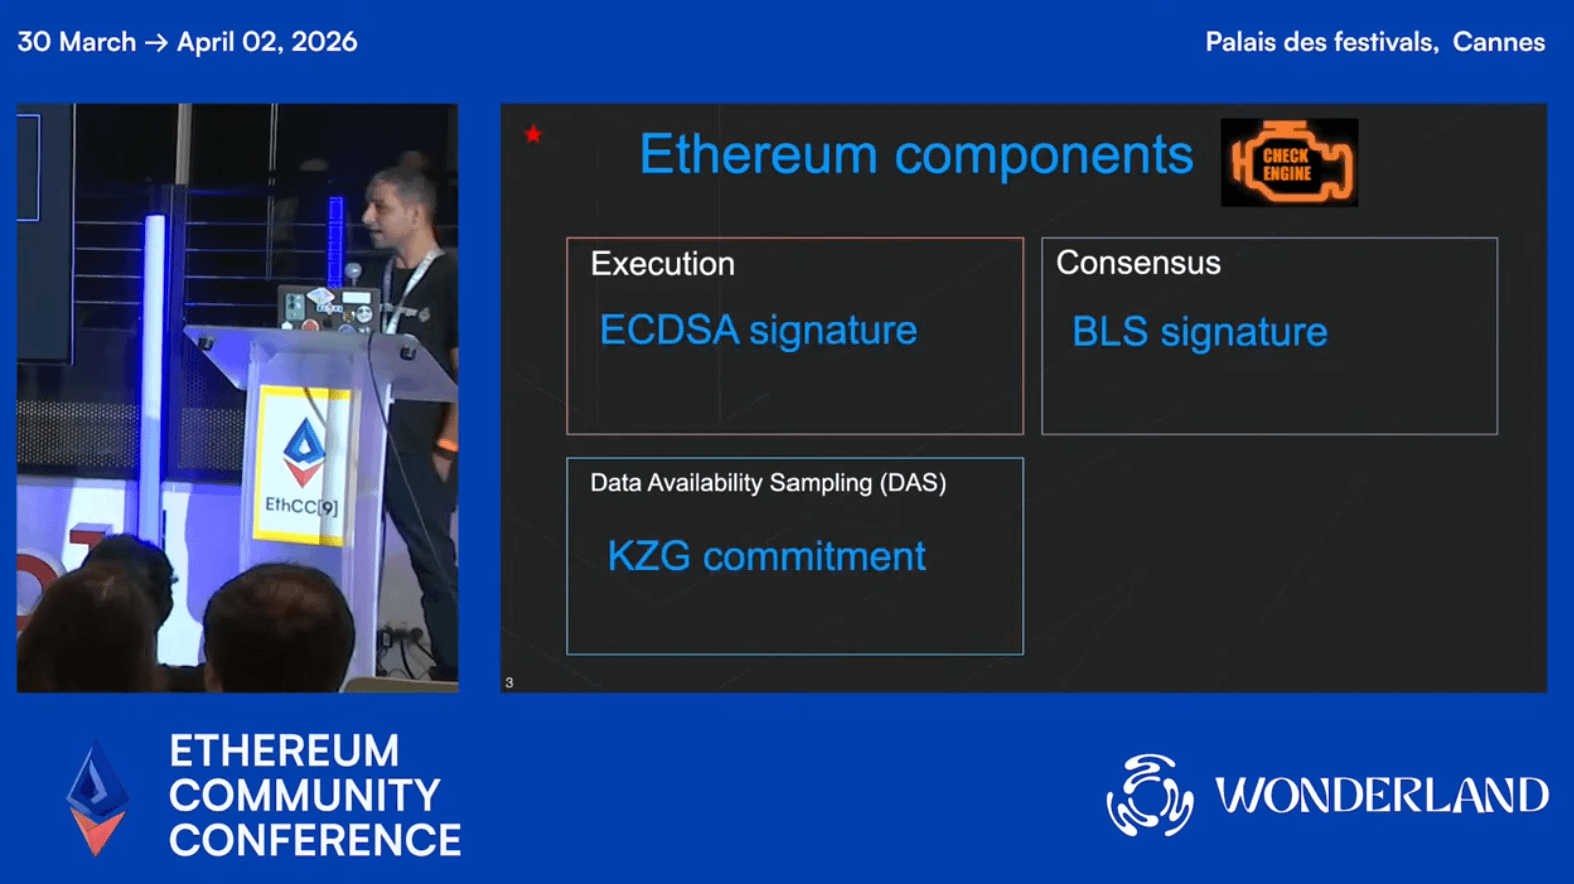
Furthermore, Ethereum Foundation cryptography researcher Antonio Sanso updated the latest progress on Ethereum's quantum security at the EthCC9 conference, noting that quantum computers may pose an actual threat to the ECDSA signature algorithm in the mid-2030s. Ethereum has currently completed about 20% of its post-quantum preparation work and plans to achieve full quantum resistance through the Lean Ethereum upgrade between 2028 and 2032.
However, the main technical challenge currently faced is the size of the signature. For instance, the signature size of the most lightweight post-quantum signature algorithm Falcon is still more than 10 times that of ECDSA, and directly verifying lattice-based signatures in Solidity is extremely costly in gas. Therefore, the research team has established two core technical paths:
First, allow users to upgrade wallet signing algorithms to quantum-resistant solutions through account abstraction, without modifying the underlying protocol;
Second, introduce LeanVM to handle complex hash operations, and combine zero-knowledge proofs to verify the ownership of address mnemonic phrases, ensuring asset security during the migration process;
Antonio stated that he will host bi-weekly ACD post-quantum special meetings starting from February 2026. Currently, consensus clients such as Lighthouse and Grandine have already launched experimental post-quantum testnets.
In addition, the style of the Bitcoin community is clearly more conservative. The newly entered BIP360 proposal in the BIPs repository introduces a new output type P2MR (Pay-to-Merkle-Root), one of its design goals being to eliminate the quantum-vulnerable key-path spend in Taproot, leaving a more friendly structure for possible future post-quantum signature migration.
Of course, just because a proposal enters the BIPs repository does not mean it has formed community consensus, nor does it mean it will be adopted soon. Thus, we can only say that the Bitcoin community has already begun more specific proposal discussions around quantum exposure and potential output type changes, which aligns with Bitcoin's consistent style of first clearly defining the problem and then very slowly forming consensus.
It is worth noting that as early as 2024, the National Institute of Standards and Technology (NIST) officially released three post-quantum cryptography standards, meaning that the blockchain ecosystem has a clear migration goal and no longer needs to wait for discussions to converge on which algorithm is better. Engineering implementation has essentially already begun.
3. What should ordinary users do?
Although the threat of quantum computers is a matter for years to come, the future does not mean we shouldn't care now. Some good habits can be cultivated today at virtually no cost.
The first thing is to avoid address reuse, which is the most direct and effective self-protection measure.
The reason is as mentioned above—if you are a user of UTXO chains like Bitcoin, each time you initiate a transaction, your public key will be exposed on-chain. If you use the same address every time, your public key will be publicly available for a long time and, once quantum computing matures, an attacker could easily derive your private key from your public key.
Currently, mainstream wallets like imToken already provide HD wallet functions by default. A good habit is to use a new address for each transfer and not to treat a single address as a permanent identity identifier. For those addresses that have never made a transaction, the public key has never been exposed, and the current quantum threat is almost not applicable.
Next, pay attention to the post-quantum upgrade path of the wallet.
If you primarily use account model chains like Ethereum, the focus is not on mechanically changing addresses constantly but on the wallet you use and the public chain you are on, and whether it will provide a clear migration path in the future.
For account model chains, the bigger issue in the quantum era is often not a single exposure, but the long-term binding of active accounts, public key history, on-chain identity, and application permissions. Once we truly enter a migration window in the future, the one whose account is more upgradable and whose wallet can more smoothly replace the signing logic will be safer.
Lastly, from a human perspective, it can be anticipated that as the topic heats up, there will be more and more wallets or protocols claiming to be 'quantum safe' appearing on the market. We should be cautious of these wallets, protocols, and infrastructure products that brandish the 'quantum safe' banner.
In the face of such claims, the most pressing questions are not about promotional copy, but about three harder questions:
Is the algorithm it relies on a finalized standard from NIST?
Has its security been independently audited and sufficiently validated?
Is the claimed quantum security about chain-level migration, account-level upgrades, or just application layer packaging?
After all, true post-quantum security ultimately needs to cover not just a single app's label but the entire path from signing, verification to on-chain compatibility.
Overall, the threat of quantum computing to blockchain is real, and the importance of Google's latest white paper lies in its advancement of the threat from a distant theory to a manageable risk.
However, this still does not signal that 'wallets will be compromised tomorrow.' A more accurate understanding should be that post-quantum migration is no longer just an academic topic but will gradually enter realistic issues in protocol upgrades, wallet design, and user asset management in the coming years.
In conclusion
For the industry, what is truly important next is not who first shouts that quantum is here, but who can clearly design the migration path first.
For users, it is not necessary to panic now, but to first establish the most basic risk awareness: which assets are exposed first, which operations will amplify exposure, and which wallets and public chains are more likely to provide smooth upgrades in the future.
What we need is to take action early, rather than being overly anxious.
Let's encourage each other.