
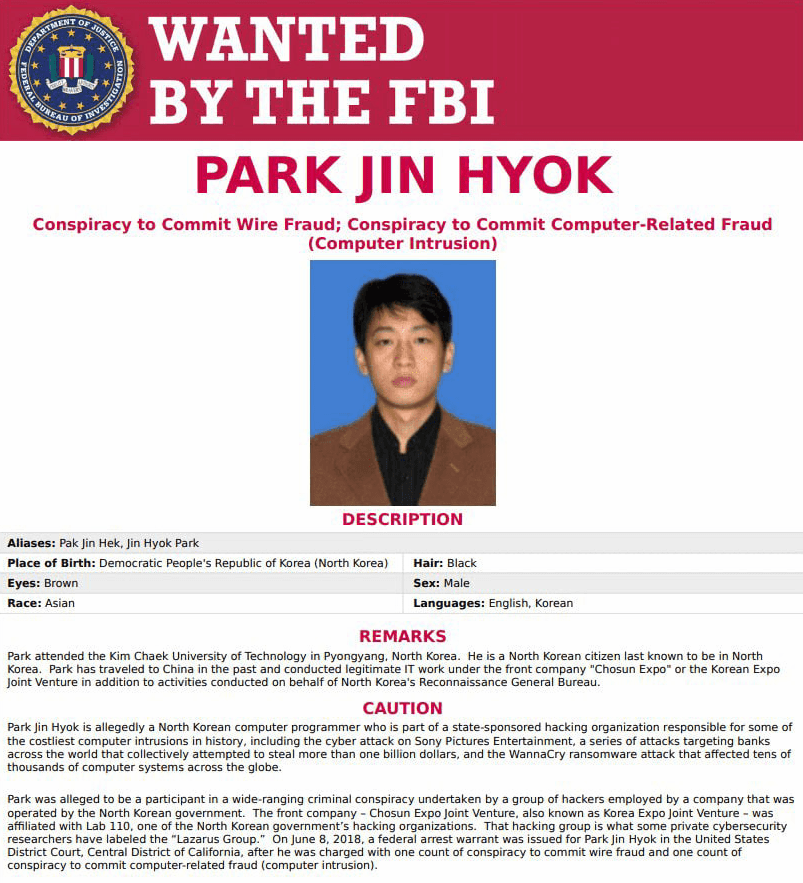
The North Korean hacker group Lazarus Group has long been active in the field of cybercrime, notorious for its activities in cryptocurrency and cyber attacks. Prior to the Bybit incident, they had already carried out a series of shocking cyber thefts, causing huge financial losses to many institutions and individuals around the world.
As early as 2014, Lazarus Group targeted Sony Pictures. They launched a massive attack that successfully leaked a large amount of sensitive data from Sony Pictures, including unreleased films, personal information of employees, etc. The losses from this incident amounted to hundreds of millions of dollars.
In 2016, Lazarus Group's attack methods became bolder and more sophisticated. They exploited vulnerabilities in the SWIFT banking payment system to infiltrate the systems of the Bangladesh Central Bank. Although some funds were recovered, they still successfully stole about 81 million dollars.
2017 was a year when the evil deeds of Lazarus Group 'erupted'. That year, the WannaCry ransomware virus spread rapidly worldwide, affecting tens of thousands of computers across multiple industries and institutions, including healthcare, transportation, and finance. It is estimated that the damages from this attack exceeded 4 billion dollars. In the same year, they also stole approximately 150 million dollars worth of Ethereum assets by exploiting vulnerabilities in the Ethereum Parity wallet.
By 2018, several cryptocurrency exchanges in South Korea became targets of Lazarus Group, with a significant amount of cryptocurrency assets stolen, resulting in losses exceeding 200 million dollars. Almost around the same time, Japan's Coincheck exchange also fell victim, suffering losses of about 530 million dollars in cryptocurrency after the attack.
In 2020, Lazarus Group attacked the KuCoin exchange, stealing approximately 280 million dollars worth of cryptocurrency.
In 2022, Lazarus Group continued their criminal activities. They launched an attack on the Ronin Network (related to the Axie Infinity project), stealing about 620 million dollars; in the same year, Harmony's Horizon Bridge was also attacked by them, resulting in a loss of about 100 million dollars in cryptocurrency.
In 2023, Atomic Wallet became a victim, and Lazarus Group may be related to this cryptocurrency wallet theft incident, causing losses of about 50 million dollars.
In 2024, Lazarus Group was accused of using a disguised PDF poisoning method to deceive the Radiant Capital team into granting multi-signature permissions, stealing a large amount of cryptocurrency, amounting to about 50 million dollars.
Over the years, Lazarus Group has stolen a large amount of funds and digital assets through various complex cyber attack methods, posing a severe threat to global cybersecurity. These criminal acts have not only caused significant economic losses but have also raised global awareness of cybersecurity. With the continuous development of the cryptocurrency market, the threat posed by Lazarus Group is also evolving, making it an important issue in the global cybersecurity field to prevent their attacks.#bybit被盗 #钱包安全