

#darksword
darksword
1,758 views
26 Discussing
Hot
Latest

·
--
The same gang has set up over 1,500 fake websites, including fake exchanges and wallets
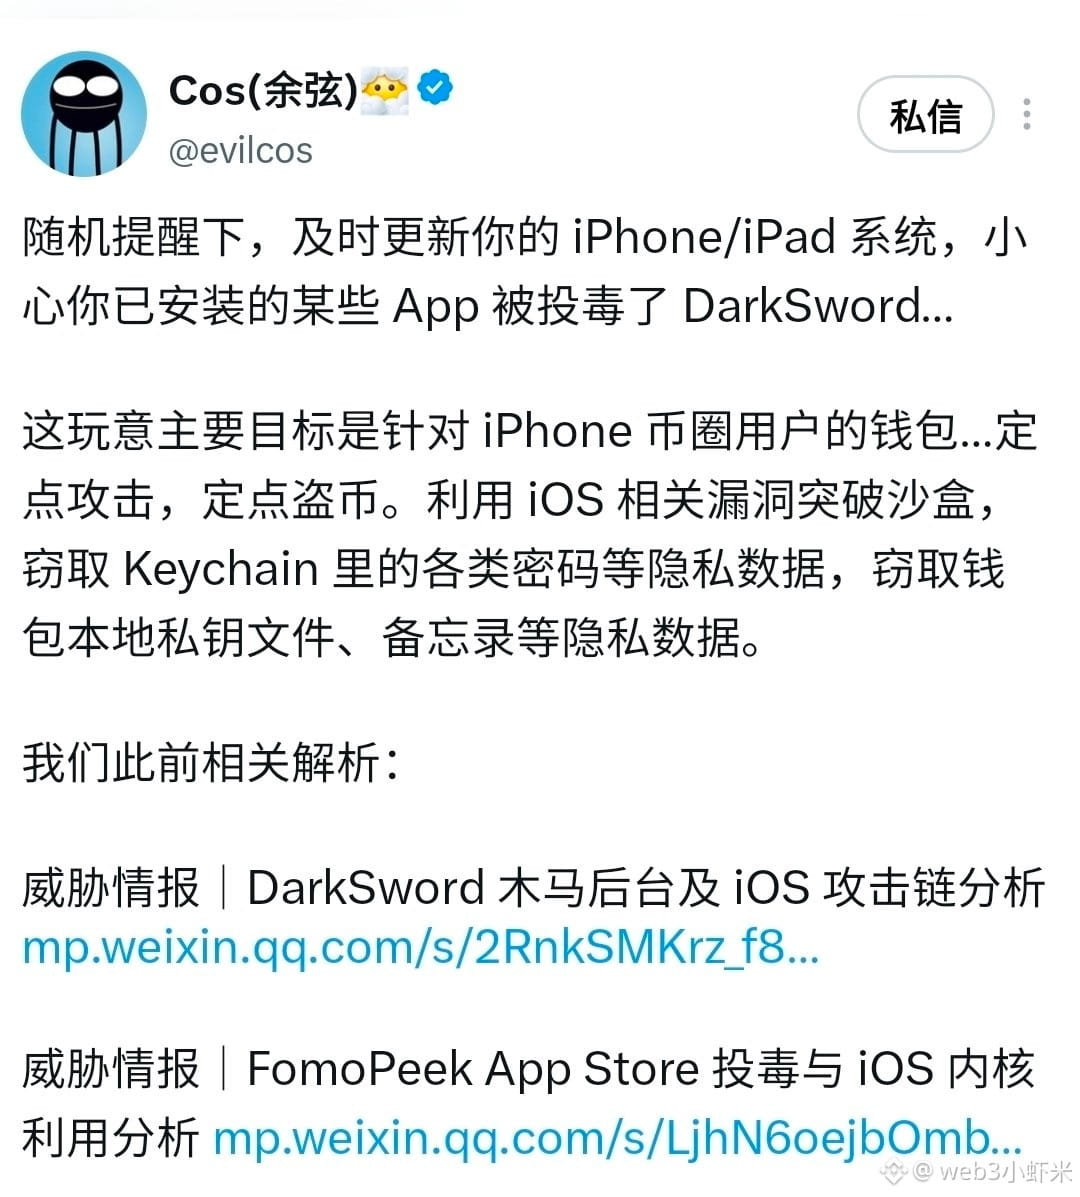
Last week, we talked about the DarkSword gang, which uses an iOS trojan to steal wallet private keys and Keychain data. Today, SlowMist shared a new development: the same group has set up more than 1,500 fake websites online, and they’re still accessible. This isn’t old news being recycled—it’s the scale they confirmed today.
These fake websites come in all kinds of disguises: fake e-commerce platforms, exchanges, wallets, games, and virtual currency services. SlowMist Chief Information Security Officer 23pds called them out in a post today, saying that fake Binance and OKX sites are among them. MistEye’s count is also over 1,500—not an estimate, but the number of sites already identified.
There are three common ways retail investors get caught out. First, they search for an exchange’s name and find fake sites mixed in with the top results. The pages look almost identical to the real ones, including the login form. Second, they click links sent through communities, text messages, or DMs. The site asks them to log in, then complete a security check—and once they do, their wallet is empty. Third, they download a fake wallet app. The first thing it asks them to do is import their seed phrase. The moment they enter it, they’ve handed over the keys themselves.
Here are three things you can do right now. First, access exchanges and wallets only through bookmarks you’ve saved yourself or official apps. Don’t click search results or links sent by other people. If you need to log in, open your bookmarks manually. Second, if any website or app asks you to enter your seed phrase or private key, close it immediately. Legitimate official services will never ask you for these on a webpage. Third, update your iPhone to the latest version as soon as possible, and don’t store your seed phrase in Notes or Photos. The trojan is after things like your Keychain data and Notes.
Have you ever opened a fake website that looked almost identical to the real one? How did you realize something was wrong?
#钱包安全 #防骗 #DarkSword #SlowMist
—— Web3 Leek Xiaokai
Disclaimer: This article is for sharing security information and educational purposes only and does not constitute investment advice. Cryptocurrency trading is extremely risky. Please make decisions carefully.
38

·
--
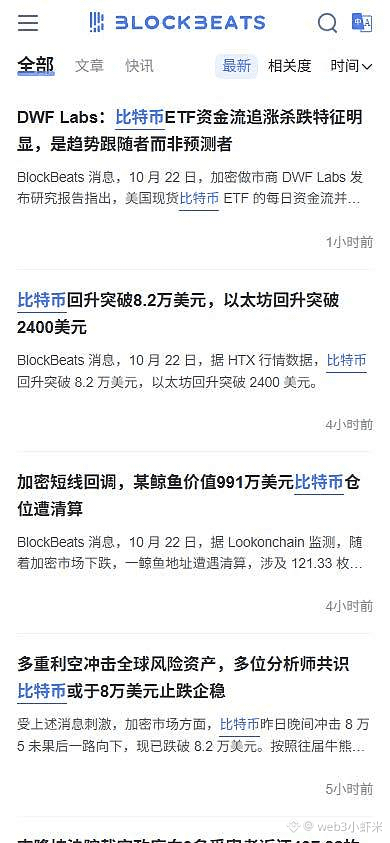
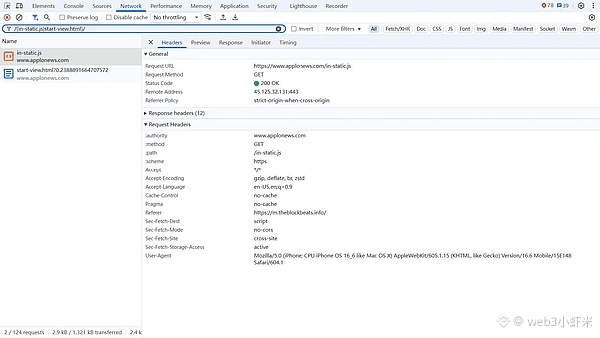
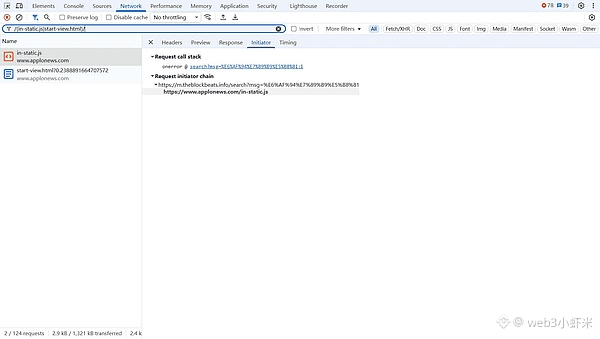
Saw official announcements from SlowMist / BlockBeats: On October 22, a third-party script related to DarkSword was found injected into the mobile H5 search page of BlockBeats. The page looked normal while you searched for news, but it could have been fetching malicious JS in the background. BlockBeats reproduced the issue and removed the script. SlowMist MistEye reported that over 1,500 DarkSword phishing sites had been deployed across the web that same day, including fake Binance and OKX sites, fake wallets, and e-commerce exchange sites.
Key point: The main window for successful exploitation is iOS 18.6–18.7.2 and 26.0–26.1. BlockBeats advises upgrading to the latest iOS 27 as soon as possible. The attack starts in the browser—you don't necessarily have to tap “Connect Wallet.” Even browsing breaking news on an official media domain could trigger the malicious script to load.
Crypto media homepages can all be turned into attack vectors. If your iPhone is still running an older OS, update it tonight.
#DarkSword #慢雾 #BlockBeats
·
--
Lost coins on your iPhone—and you still have to click a link yourself to get hacked?
SlowMist published a report today exposing the backend of a Trojan called DarkSword. Its attack code first surfaced in March, a repository appeared on GitHub in July, and by the end of September, the whole operation was officially up and running. It’s an end-to-end setup: serve malicious webpages, install a Trojan, steal data from phones, then sweep up the funds in crypto wallets.
It claims to support iOS 13 and later, but a look at the code shows it can only target two version ranges: 18.6 to 18.7.2, and 26.0 to 26.1.
SlowMist’s advice is straightforward: update your operating system as soon as you can, and stay away from suspicious links. If you think you’ve been affected, stop using that phone for your wallet. Set up a new wallet on a clean device, move your funds, and revoke any approvals while you’re at it.
What version of iOS is your phone running? After reading the report, I went to check mine. Even a crypto sucker’s life matters.
#慢雾 #DarkSword #iOS安全 #WalletSecurity
—— Web3 crypto sucker Xiaokai
These are only my personal opinions and do not constitute investment advice.
26

·
--
🎯 iPhones are being targeted—thieves are after wallet seed phrases
📰 The DarkSword exploit kit uses Coruna malware to attack iOS and steal crypto wallet seed phrases. Its C2 servers have been exposed.
💬 Hardware wallets keep getting more sophisticated, but phones are still the weakest link. If you’ve stored your seed phrase in your photo library, screenshots, or Notes, it’s time to check. I was stunned for a couple of seconds after reading this.
🏷️ #iOS安全 #钱包安全 #DarkSword #seedphrase
27
·
--
🎯 iPhone users, beware: your seed phrase is being targeted
📰 The P7 DarkSword toolkit uses Coruna malware to steal wallet seed phrases, remotely control devices, and send data back. It specifically targets iOS crypto wallets.
💬 We’ve barely gotten over the hardware wallet scare, and now phones are under attack. If you store your seed phrase in your photos or notes, it’s like sticking your keys to your forehead. Your phone isn’t a safe; offline storage is the way to go.
🏷️ #DarkSword #iOS安全 #助记词 #MobileSecurity
19
·
--
Article
BREAKING: Darksword Targets iOS 26.5 Wallets – Crypto World on EdgeThe flood has started. SlowMist’s latest alert shows attackers have hijacked the Darksword exploit chain to slash into iOS 26.5 devices, siphoning private keys from self‑custody wallets. In a chilling statement, Chief Information Security Officer 23pds warned that the attack vector bypasses Apple’s latest security patch, leaving millions of users exposed.
This isn’t a rumor; it’s a hard‑fact that the Darksword chain, once dormant, has been re‑engineered to exploit the newest iOS update. The implications? Every iOS user with a crypto wallet is now a potential target, and the market could see a sudden dip as confidence erodes. #iOS #Darksword #CryptoSecurity
If you’re holding crypto on an iOS device, the stakes are sky‑high. A single exploit could drain your entire portfolio in seconds, and the ripple effect could trigger a broader sell‑off across the ecosystem. The market’s reaction could be swift, and liquidity might dry up faster than you can say “panic.”
Don’t wait for the next headline. Secure your wallet, update your device, and stay ahead of the curve. Are you ready to protect your assets before the next wave hits?
BREAKING: Darksword Targets iOS 26.5 Wallets – Crypto World on Edge
The flood has started. SlowMist’s latest alert shows attackers have hijacked the Darksword exploit chain to slash into iOS 26.5 devices, siphoning private keys from self‑custody wallets. In a chilling statement, Chief Information Security Officer 23pds warned that the attack vector bypasses Apple’s latest security patch, leaving millions of users exposed.
This isn’t a rumor; it’s a hard‑fact that the Darksword chain, once dormant, has been re‑engineered to exploit the newest iOS update. The implications? Every iOS user with a crypto wallet is now a potential target, and the market could see a sudden dip as confidence erodes. #iOS #Darksword #CryptoSecurity
If you’re holding crypto on an iOS device, the stakes are sky‑high. A single exploit could drain your entire portfolio in seconds, and the ripple effect could trigger a broader sell‑off across the ecosystem. The market’s reaction could be swift, and liquidity might dry up faster than you can say “panic.”
Don’t wait for the next headline. Secure your wallet, update your device, and stay ahead of the curve. Are you ready to protect your assets before the next wave hits?
34

·
--
Bearish
your chats say DarkSword hits iOS 13 through 26.5 lol. documented: 18.4 to 18.7, fully patched by February #DarkSword
🔸 one Safari link, then it reads wallet data
🔸 six chained bugs, all closed in iOS 26.3, 11 Feb
🔸 26.5 is SlowMist's claim, nobody official confirmed it
the claim itself stops at 26.5, a May build. iOS 27 and 26.7 shipped 14 Sep
keys on a phone? update tonight, or Lockdown Mode)
Apple or Google confirm or kill the 26.5 part, I'll post it. follow if you care #Apple
1
4
357
·
--
Bearish
26.7.1
that's the iOS you want if keys live on an iPhone
Apple shipped it September 28 for CVE-2026-86950, a CoreGraphics bug
a crafted file can run code, and Apple says it may have been exploited against specific targeted individuals on versions before iOS 27
26.7, the one I told you to install last week, was still exposed. my bad
now the part the chats add on their own:
- "this is DarkSword": Apple's page never says that, and no source has confirmed it
- "iOS 13 through 26.5": that's the alert's claim, not Apple's
on iOS 27 this bug doesn't apply. 27.0.1 came out the same day with no published CVEs
last week I also said I'd post once Apple or Google settle SlowMist's 26.5 claim either way. still nothing from either
#Apple #DarkSword
7
97

Warning: A Safari vulnerability attack threatens DarkSword cryptocurrency
- Ledger CTO Charles Guillemet has issued a warning about a new attack called DarkSword.
- He advises iPhone users to update their devices immediately.
- This attack could cause users to lose cryptocurrency if they visit malicious websites.
- Detailed information about the vulnerability has not yet been fully disclosed.
#CryptoNews #Ledger #Safari #DarkSword #BinanceSquare
$btc $eth
vlikevn Titanbot
Source: U.Today
428

·
--
DARKSWORD HACK LEAKED OLD iPHONE USERS AT RISK 🚨
🚨 DARKSWORD ATTACK LEAKED IN THE WILD OLD iPHONES AND SAFARI USERS ARE TARGETED
This is a serious SECURITY WARNING for every crypto holder.
SlowMist's Yu Xian confirmed that the DarkSword attack program has been leaked in the wild and is actively targeting crypto wallets .
Who is at risk:
iPhones running older versions of iOS
Safari browser users
Anyone holding cryptocurrency wallets on affected devices
How the attack works:
Malicious JavaScript exploit code is being embedded in fake websites impersonating:
Adult live-streaming platforms
TRON energy stations
Refund procedures
Vulnerability alerts
The danger: If users of older iPhone models open such websites using Safari and leave them open, while simultaneously unlocking their wallet apps, their plaintext private keys could be stolen .
What you should do NOW:
Update your iPhone to the latest iOS version
Avoid using Safari for crypto-related browsing
Never leave wallet apps unlocked while browsing
Be extremely cautious of suspicious links
👇 Have you updated your iPhone recently? Stay safe out there.
#DarkSword #cryptohacks #SecurityAlert #SlowMist $BTC
1
68
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#BinancePick
3.2M views
159,643 Discussing
2
#EarningsSeason
5.4M views
26,395 Discussing
3
#BitmineAdds10452ETH
2,049 views
49 Discussing
4
#SouthKoreaConsidersEducationTaxOnCryptoExchanges
1,944 views
62 Discussing
5
#OCCUrgesCommunityBanksToEnterStablecoinPayments
1,297 views
41 Discussing
6
#RippleWinsFullApprovalAsNationalTrustBank
1,236 views
41 Discussing
7
#AkashSelectsSolanaAsMigrationTarget
620 views
12 Discussing
8
#OndoToOpenSubscriptionsForOpenAIPreIPOTokenizedNotes
54 views
4 Discussing
9
#AnthropicTTMRevenueGrewAbout1200%
47,587 views
524 Discussing
10
#AnthropicS1ExpectedToday
38,575 views
411 Discussing