

#cst
cst
6,154 views
48 Discussing
Hot
Latest
·
--
Detailed Rules of the Joint Bug Bounty Program for CST and CSCT Token Contracts
1. Project Overview
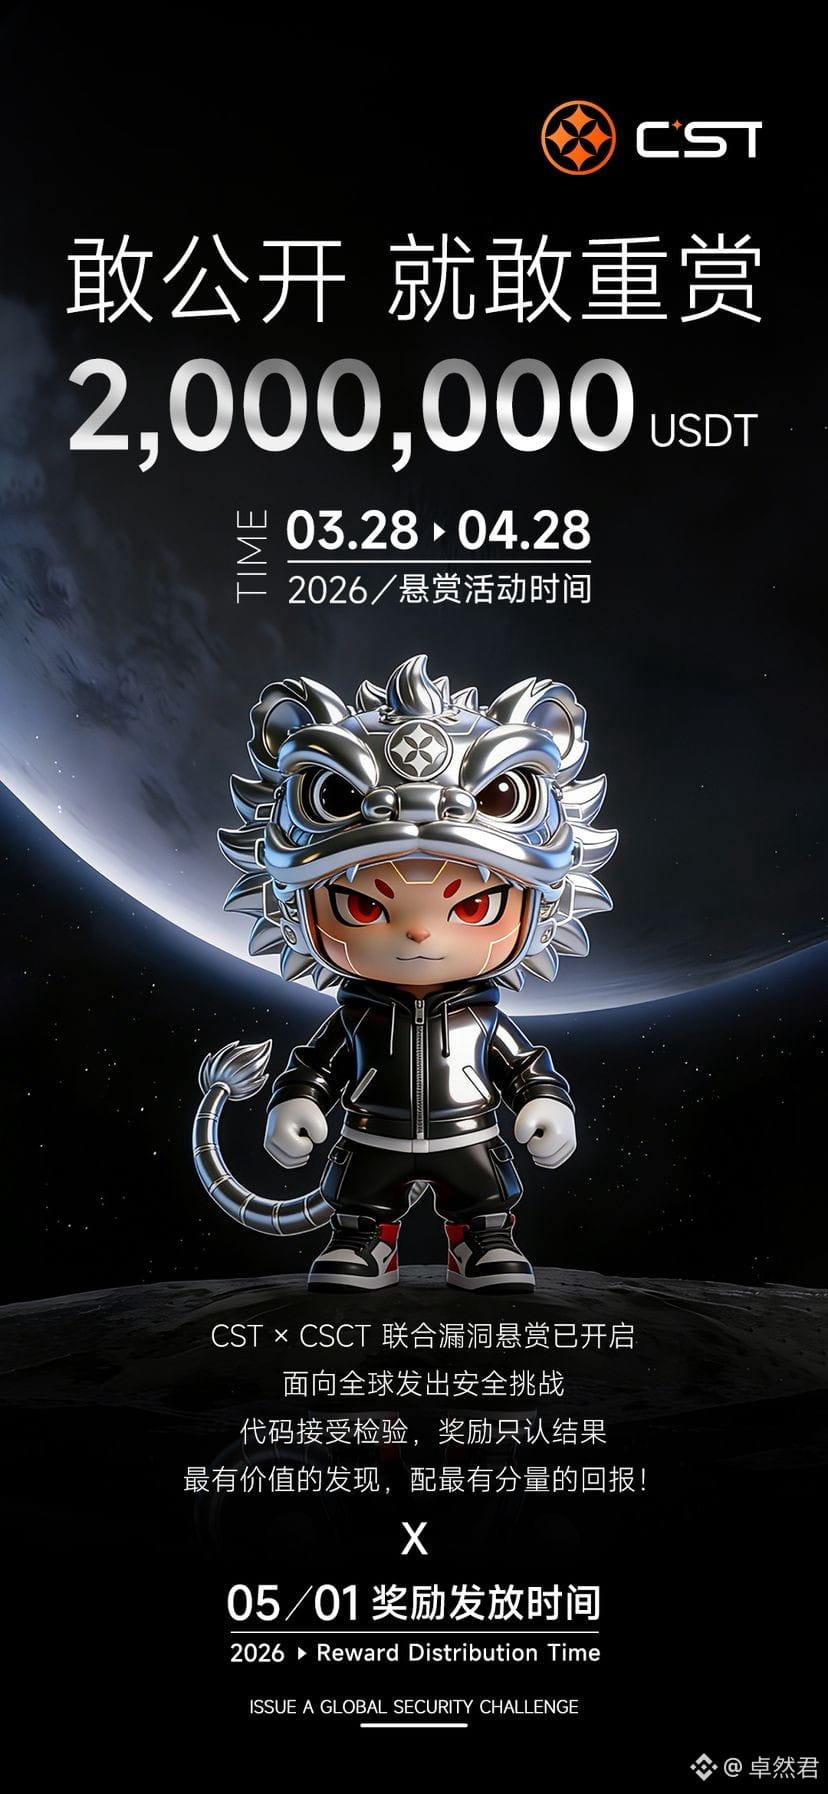
In order to further enhance the security of CST and CSCT token contracts and protect user assets, we officially launch the joint bug bounty program. We sincerely invite security researchers, white hat hackers, and developers from around the world to conduct in-depth audits and tests on our token contracts. The first person to submit an effective vulnerability report that helps us fix potential security risks will be rewarded based on the severity of the vulnerability.
Total Reward Pool: 2,000,000 USDT
Reward Period: March 28, 2026 to April 28, 2026
Reward Distribution Date: May 1, 2026
Covered Contracts:
CST Token Contract Address: 0x677476c15F339d341F4B82cC06A7672403deF5f0
CSCT Token Contract Address: 0xF2Daf3F85E4b79BA6224DbFCAc2562079663f501
Reward Pool Wallet Address: TKq96WcKC3i5wTKyzZyNggeJuqX2ZnvqRx
#CST #DDA基金会 #200万U漏洞悬赏 #BNB
4
3
356
·
--
Article
Let's All Find Vulnerabilities in the Token ContractsCST and CSCT Token Contract Joint Vulnerability Reward Details
I. Overview of the Plan
To further enhance the security of CST and CSCT token contracts and protect user assets, we are officially launching a joint vulnerability reward program. We invite security researchers, white-hat hackers, and developers from around the globe to conduct in-depth audits and tests on our token contracts. For the first reporter of valid vulnerabilities that help us address potential security risks, we will issue corresponding rewards based on the severity level of the vulnerabilities.
Total Reward Pool: 2,000,000 USDT
Reward Period: March 28, 2026, to April 28, 2026
Let's All Find Vulnerabilities in the Token Contracts
CST and CSCT Token Contract Joint Vulnerability Reward Details
I. Overview of the Plan
To further enhance the security of CST and CSCT token contracts and protect user assets, we are officially launching a joint vulnerability reward program. We invite security researchers, white-hat hackers, and developers from around the globe to conduct in-depth audits and tests on our token contracts. For the first reporter of valid vulnerabilities that help us address potential security risks, we will issue corresponding rewards based on the severity level of the vulnerabilities.
Total Reward Pool: 2,000,000 USDT
Reward Period: March 28, 2026, to April 28, 2026
2
162
·
--
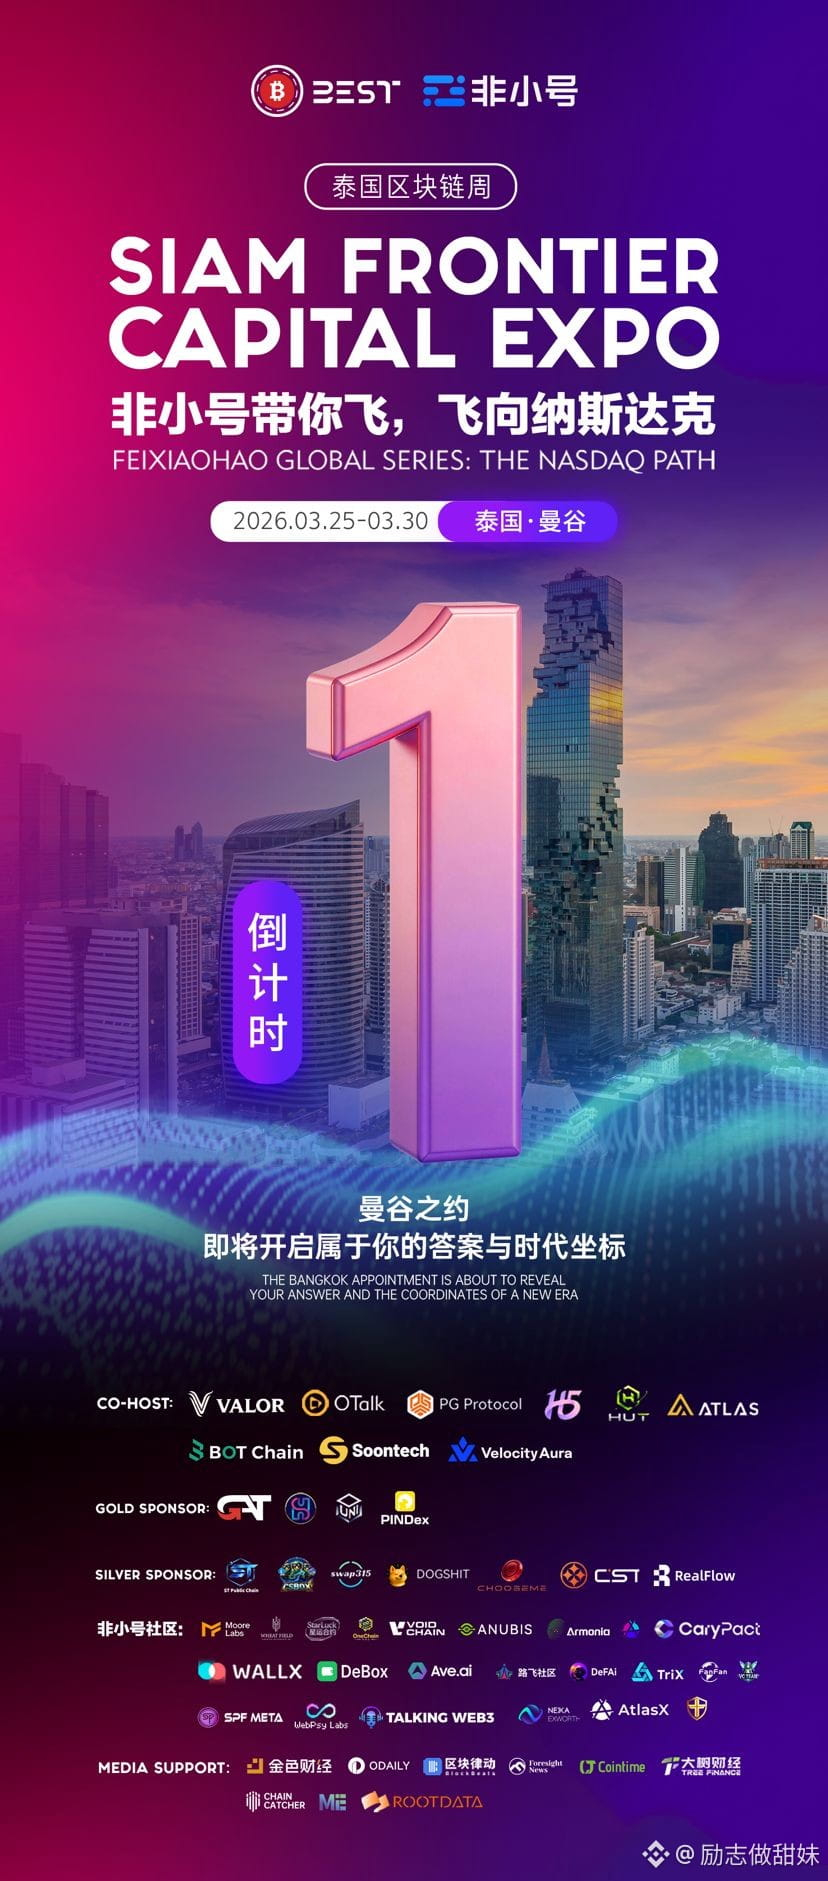
Countdown to the Thailand Summit: 1 day left. The DDA Foundation, as a silver sponsor, is ready and will officially appear with CST tomorrow. Today's bounty event has also started, with a prize of 2 million U. Tech experts are welcome to challenge. The DDA Foundation has been following a technical route since its establishment in 2019 by several core technology companies. This time, we are making efforts both online and offline, with a strong sense of rhythm. #CST #DDA基金会 #200万U漏洞悬赏
Countdown to the Thailand Summit: 1 day left. The DDA Foundation, as a silver sponsor, is ready and will officially appear with CST tomorrow. Today's bounty event has also started, with a prize of 2 million U. Tech experts are welcome to challenge. The DDA Foundation has been following a technical route since its establishment in 2019 by several core technology companies. This time, we are making efforts both online and offline, with a strong sense of rhythm. #CST #DDA基金会 #200万U漏洞悬赏
170
1
23
522
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#GoldFallsTo$4144
0 views
0 Discussing
2
#QNTFallsOver40%FromMorningHigh
0 views
4 Discussing
3
#BitgetCEOConfirms$388MStolenInHack
0 views
0 Discussing
4
#BTCFallsBelow$83000
5,150 views
76 Discussing
5
#BitgetDetailsSecurityIncidentTimeline
948 views
83 Discussing
6
#BitcoinSpotETFs$2.39BWeeklyNetInflow
704 views
14 Discussing
7
#FedProposesPaymentStablecoinRules
21,303 views
446 Discussing
8
#ChinaMayLetAlibabaByteDanceBuyNvidiaChips
23,311 views
477 Discussing
9
#USChinaRelease$30BTariffCutProductLists
2,965 views
49 Discussing
10
#SKoreaFSCConsidersVirtualAssetMarketMaker
15,233 views
366 Discussing