
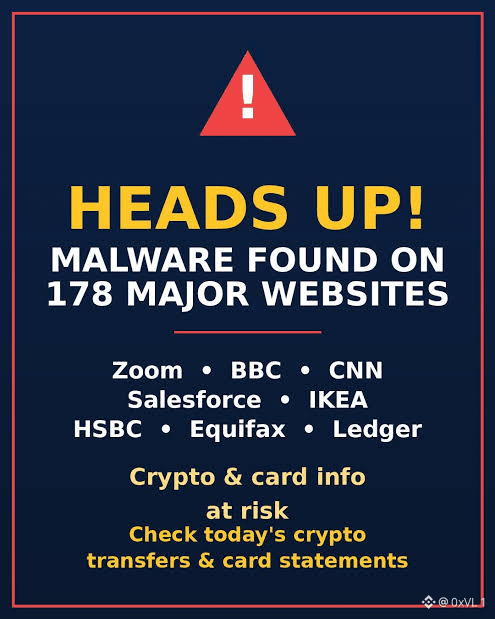
That is a really sharp question to bring up, especially since supply-chain and third-party script vulnerabilities are easily one of the most overlooked attack vectors in both traditional finance and Web3. It is fascinating how a single compromised vendor dependency or an unverified snippet can quietly cascade across 178 high-profile domains like HSBC, the BBC, and Ledger all at once, proving that even enterprise-grade perimeter security is only as strong as its weakest external integration. At the same time, shifting the blame solely onto the upstream provider feels like a convenient excuse for the organizations running those frontends. Any company handling sensitive user sessions or hardware wallet interfaces should be enforcing strict Subresource Integrity hashes, tight Content Security Policies, and rigorous dependency pinning rather than blindly trusting third-party scripts in production. When firms prioritize rapid deployment over basic client-side hygiene, they leave the door wide open for these exact single-point-of-failure compromises, and end users end up paying the price for corporate negligence. $BTC $ETH
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number