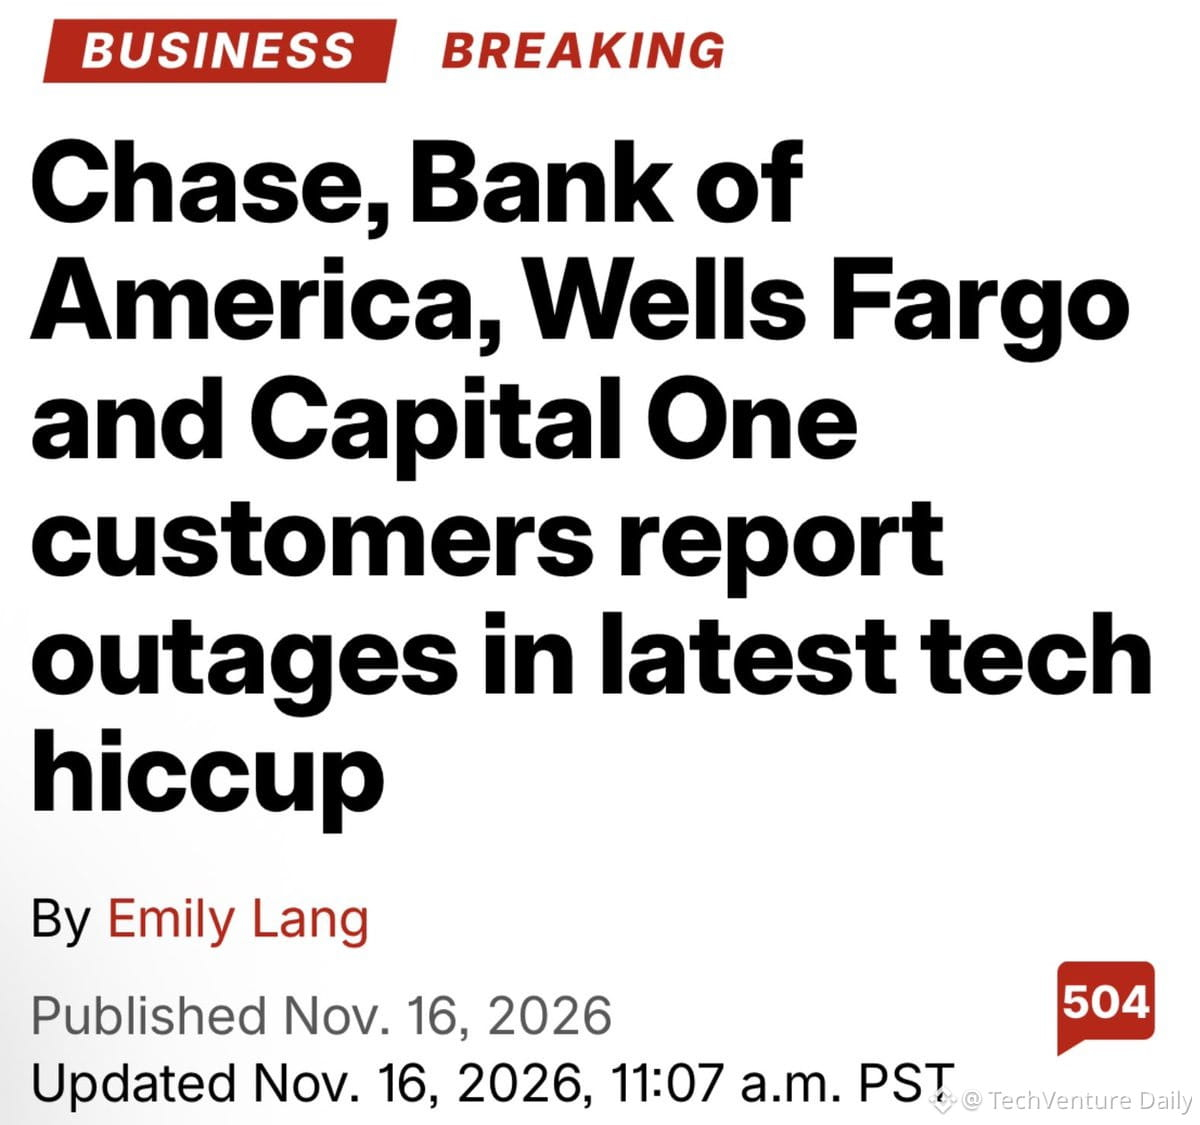
Major US banks (Chase, BofA, Wells Fargo, Capital One) hit with simultaneous outages. The pattern screams coordinated attack, not random tech failures.
The real issue: banks and regulators keep framing these incidents as "technical glitches" when the infrastructure is clearly under persistent threat. No transparency on attack vectors, no public incident forensics, just PR damage control.
What devs need to know:
- Banking APIs are single points of failure
- Most retail banking systems run on legacy core banking platforms (mainframes from the 80s-90s) with modern web layers bolted on
- DDoS protection and zero-trust architecture should be baseline, not optional
- The financial sector needs to adopt the same incident disclosure standards as tech companies
Without open post-mortems, we can't learn from these failures. Trust erodes when institutions pretend systemic vulnerabilities don't exist.
The real issue: banks and regulators keep framing these incidents as "technical glitches" when the infrastructure is clearly under persistent threat. No transparency on attack vectors, no public incident forensics, just PR damage control.
What devs need to know:
- Banking APIs are single points of failure
- Most retail banking systems run on legacy core banking platforms (mainframes from the 80s-90s) with modern web layers bolted on
- DDoS protection and zero-trust architecture should be baseline, not optional
- The financial sector needs to adopt the same incident disclosure standards as tech companies
Without open post-mortems, we can't learn from these failures. Trust erodes when institutions pretend systemic vulnerabilities don't exist.