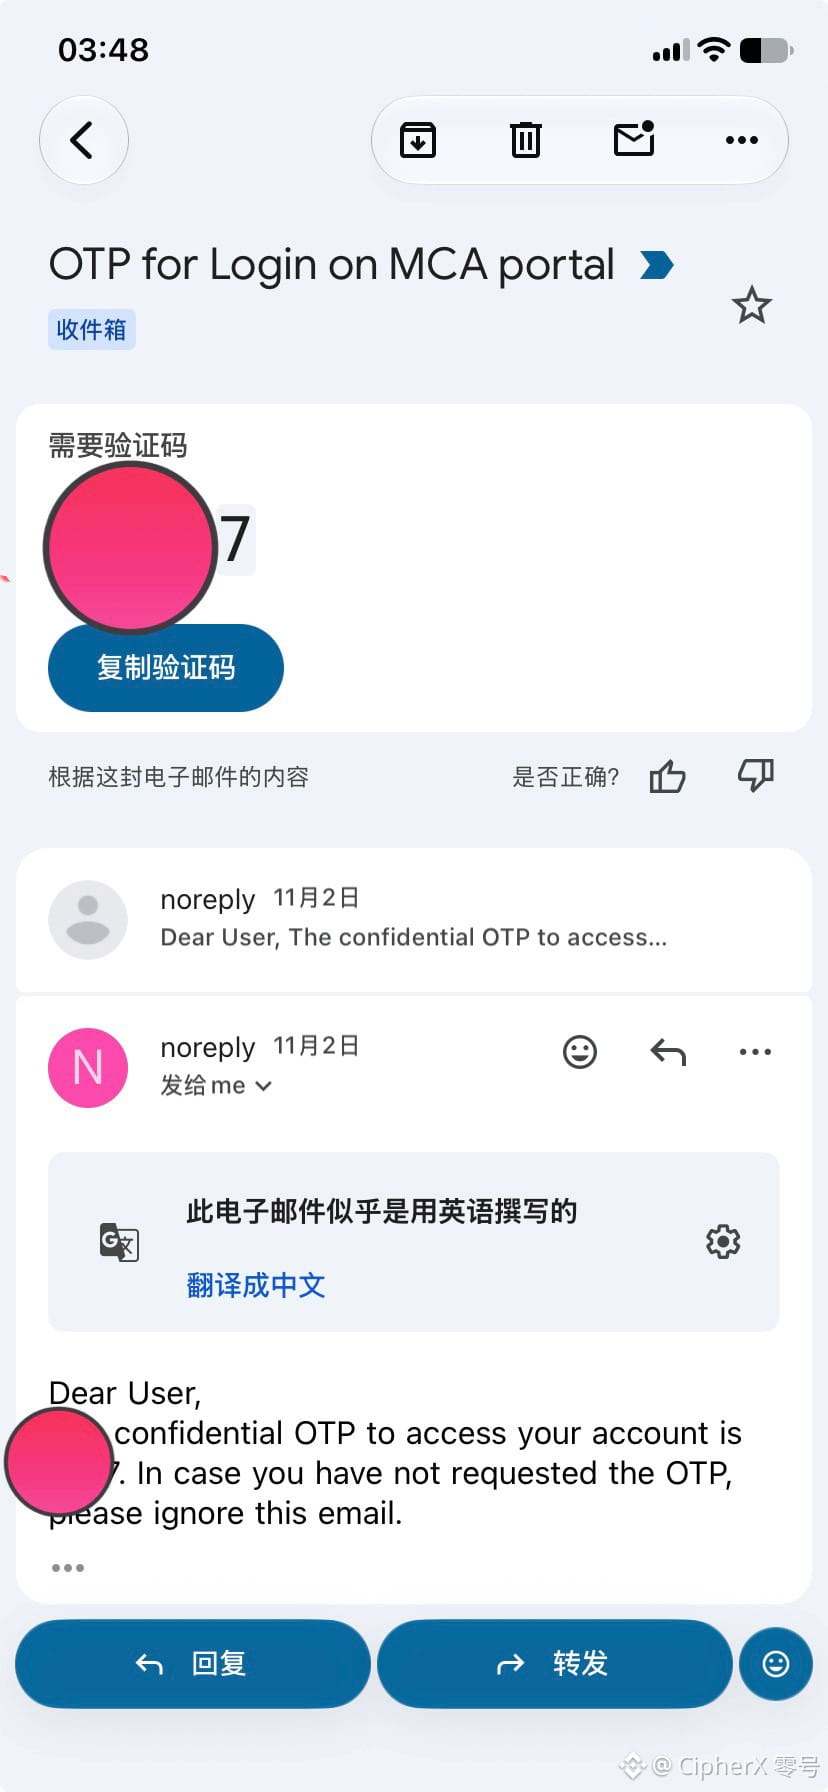
My systems recently endured two targeted attacks back-to-back on November 2 and November 4.
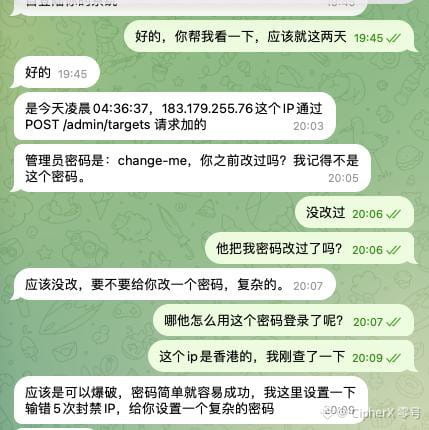
While I was upgrading my password security framework from November 3 to 4, an attacker took advantage of the maintenance window to breach my AI system at 4:36 AM on the 4th. It wasn't until 7:40 PM that evening during live runtime that I caught an injected rogue username running background test scripts in my system.
This has been a serious wake-up call for access security. I have immediately completed a full rebuild and hardening of my password architecture, reset all credentials, and deployed a dedicated premium protection layer to secure the entire environment.
Meanwhile, I am still in the process of upgrading passwords across my accounts on all major platforms, which will take a bit more time to finish.
While I was upgrading my password security framework from November 3 to 4, an attacker took advantage of the maintenance window to breach my AI system at 4:36 AM on the 4th. It wasn't until 7:40 PM that evening during live runtime that I caught an injected rogue username running background test scripts in my system.
This has been a serious wake-up call for access security. I have immediately completed a full rebuild and hardening of my password architecture, reset all credentials, and deployed a dedicated premium protection layer to secure the entire environment.
Meanwhile, I am still in the process of upgrading passwords across my accounts on all major platforms, which will take a bit more time to finish.