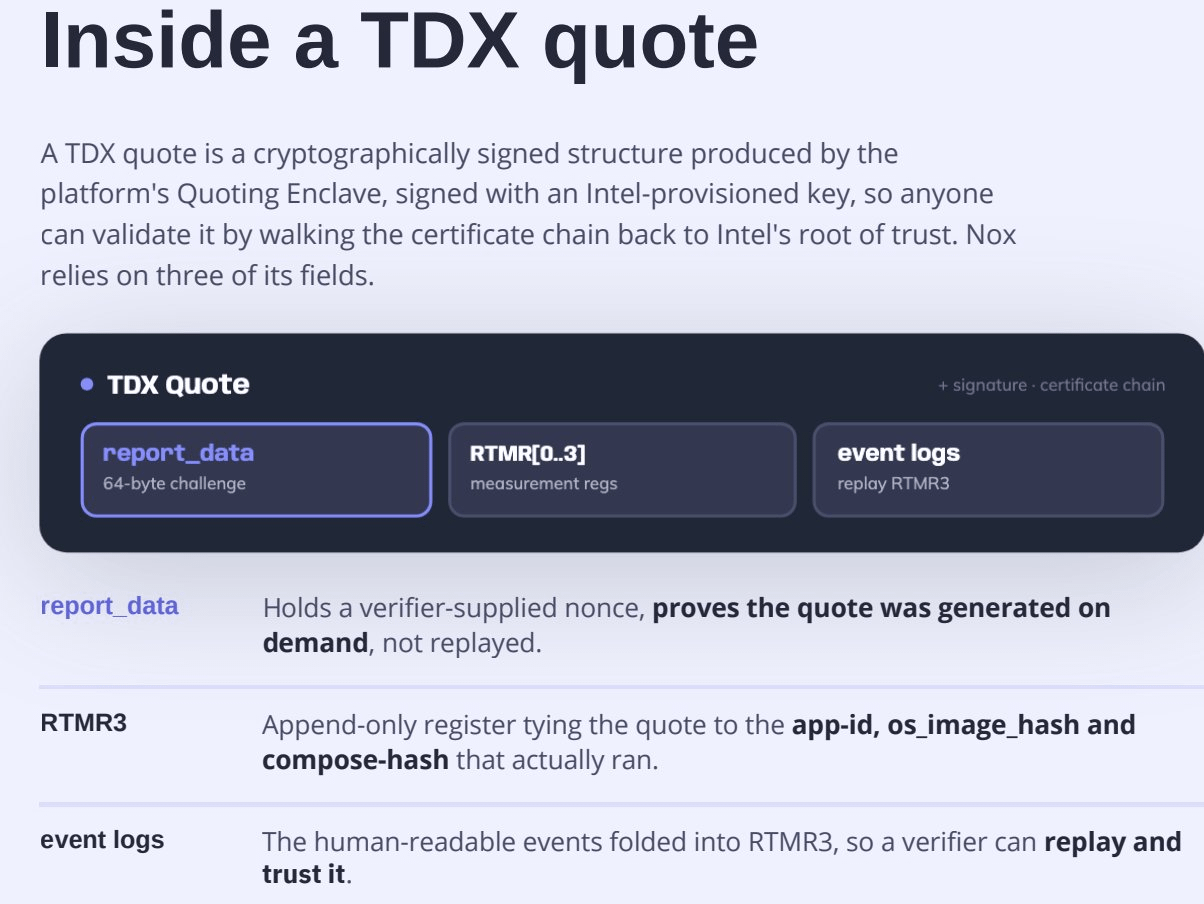

Event logs make RTMR3 interpretable.
A verifier replays the event log and matches it against the signed RTMR3. If they match, the OS image and docker-compose hashes can be trusted as representative of what actually ran.
Three fields. One chain of evidence👇
https://trust.noxprotocol.io/
A verifier replays the event log and matches it against the signed RTMR3. If they match, the OS image and docker-compose hashes can be trusted as representative of what actually ran.
Three fields. One chain of evidence👇
https://trust.noxprotocol.io/