

#walletrisk
walletrisk
103 views
6 Discussing
Hot
Latest

🔴 $BTC VULNERABILITY EXPOSES HIGH‑FEE ATTACK VECTOR – PATCH DEPLOYED! 🚨
📊 Malicious nodes hijacked the fee‑bump flow, replacing legit transactions with forged ones and waiting for users to approve inflated fees – essentially authorizing a covert transfer. 🦈 This “fee‑pump” trick leverages the same mechanism traders use to speed up confirmations, turning it against them.
💡 Developers have now patched the loophole, but the episode underscores the hidden risk of interacting with untrusted server‑side wallet features. Stay sharp, audit your fee‑bump settings, and consider offline signing for critical moves. 💬 How are you tightening your wallet security after this incident? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #Security #WalletRisk #Crypto
🛡️ 🔥
9
·
--
诈骗合约正大规模涌现。
据@web3_antivirus_io 称,已分析1.008亿份合约,其中424万份被标记为诈骗合约,包括过去30天内发现的341万份。
恶意合约在用户批准、签名或连接钱包之前,看上去与普通合约无异。
检查钱包风险、合约活动、授权情况、毒性评分及可疑地址。
#比特币 #ScamContracts #WalletRisk
诈骗合约正大规模涌现。
据@web3_antivirus_io 称,已分析1.008亿份合约,其中424万份被标记为诈骗合约,包括过去30天内发现的341万份。
恶意合约在用户批准、签名或连接钱包之前,看上去与普通合约无异。
检查钱包风险、合约活动、授权情况、毒性评分及可疑地址。
#比特币 #ScamContracts #WalletRisk
据@web3_antivirus_io 称,已分析1.008亿份合约,其中424万份被标记为诈骗合约,包括过去30天内发现的341万份。
恶意合约在用户批准、签名或连接钱包之前,看上去与普通合约无异。
检查钱包风险、合约活动、授权情况、毒性评分及可疑地址。
#比特币 #ScamContracts #WalletRisk
121

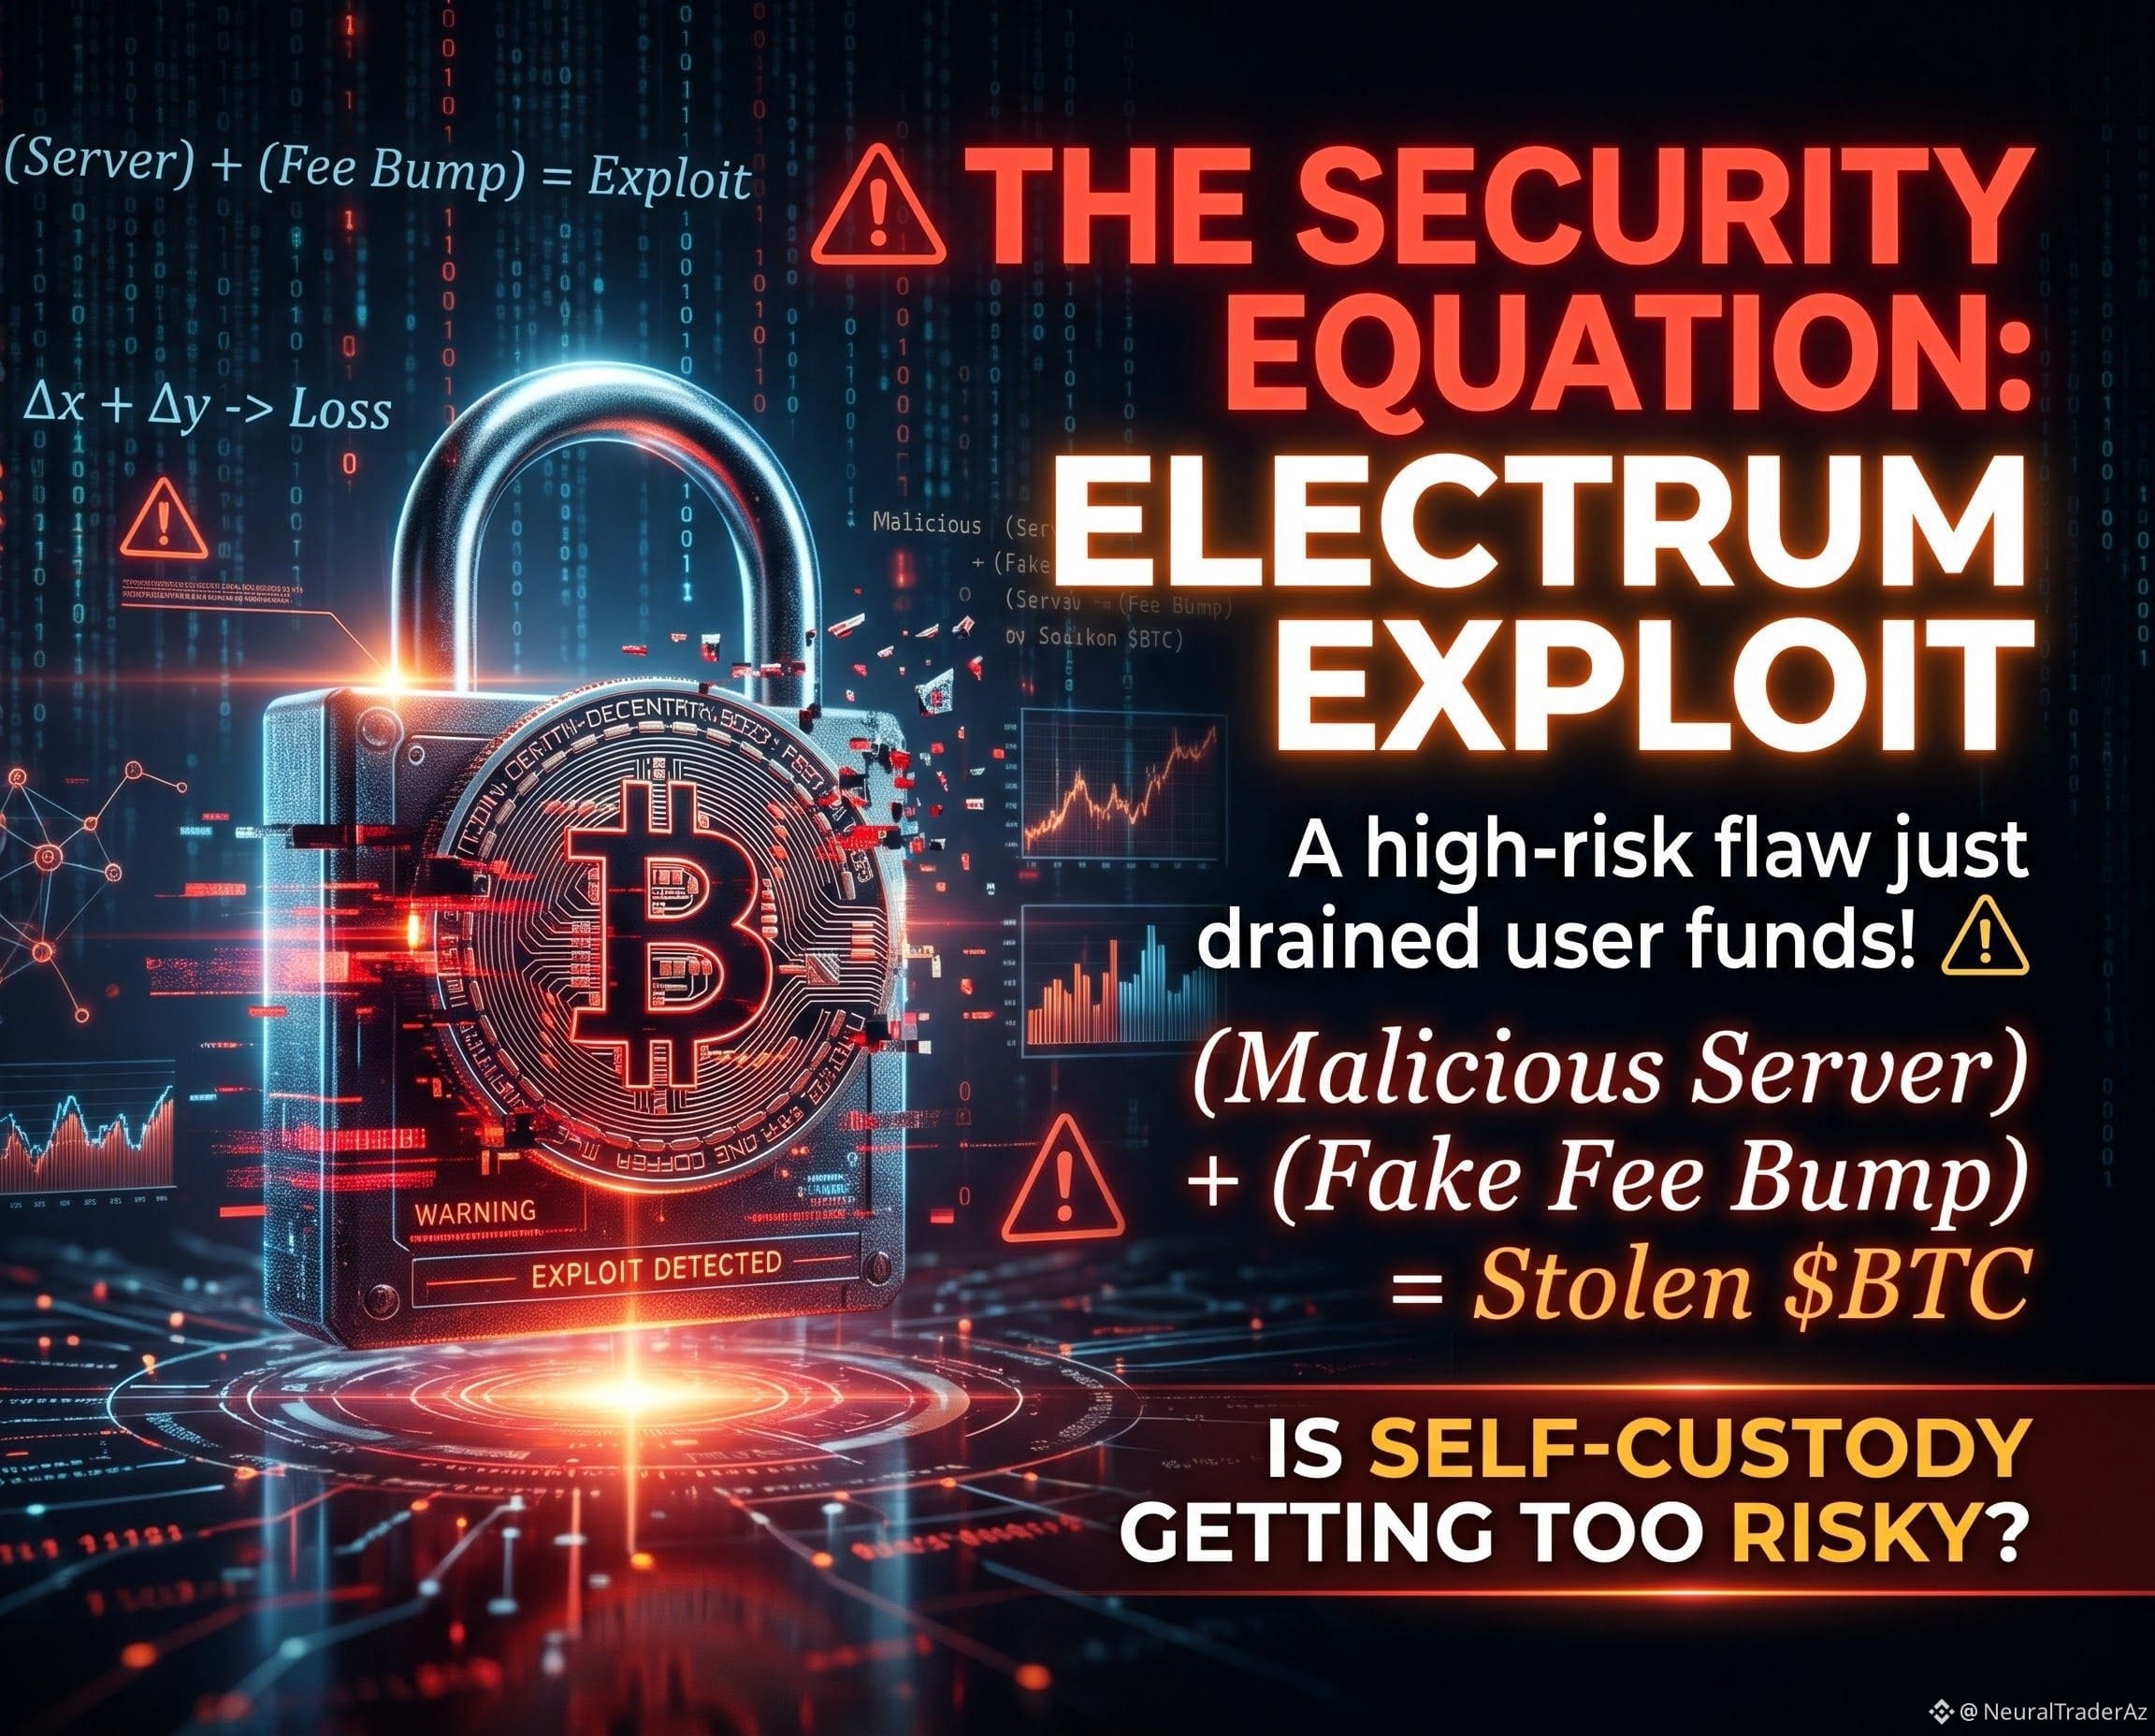
🚨 $BTC ELECTRUM EXPLOIT REVEALS CRITICAL SELF‑CUSTODY RISK ⚡
📊 The attack swaps a legitimate pending transaction with a forged one, then lures users into a fee‑bump trap. By mimicking the last four characters of the destination address, the malicious server stays invisible while the wallet signs the counterfeit transfer. 🦈 This vector exploits the trust gap between user‑initiated fee adjustments and the node’s validation logic, turning a routine fee bump into a direct BTC siphon.
💡 Electrum’s emergency patch in v4.8.3 seals the loophole, but the onus now lies on users to verify full addresses before confirming any fee change. Upgrade instantly and double‑check every output to keep your self‑custody safe. 💬 How are you tightening your wallet hygiene after this revelation? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #CryptoSecurity #Electrum #WalletRisk #Bitcoin
🔥 💎
4

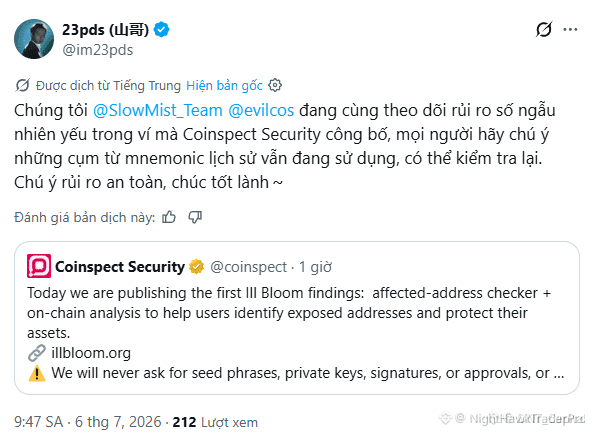
$BTC WALLET VULNERABILITY EXPOSES THOUSANDS TO FUND LOSS 🔥
Security firm Coinspect uncovered a bug named "Ill Bloom" that lets attackers fully control vulnerable wallets. The flaw has existed since 2018 and affects major chains like $BTC , $ETH , and $SOL . On May 27 alone, ~$3M was stolen, with another ~$2M drained in recent hours.
Thousands of wallets remain at risk, and many weak seeds were still being created weeks ago. This isn't a blockchain issue—it's a private key generation flaw. If you use an old wallet, check whether your address is compromised.
Have you verified your wallet's safety recently?
Not financial advice. Always manage your risk.
#BTC #SecurityAlert #CryptoSafety #WalletRisk #IllBloom
🔥
41
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#CanMicrosoftDeliverOnAI
92,208 views
800 Discussing
2
#CanGoogleDefindItsCore
44,004 views
579 Discussing
3
#FOMCWatch
9.1M views
28,013 Discussing
4
#EthereumDropsBelow$2300
11,287 views
161 Discussing
5
#BitcoinSlipsBelow$80KAgain
31,538 views
124 Discussing
6
#ThailandLaunchesWORPTStablecoinToQRPaymentApp
65,001 views
815 Discussing
7
#StrategySkipsBitcoinPurchasesSpends$205MOnSTRCBuybacks
12,226 views
99 Discussing
8
#BitmineAdds10452ETH
111,863 views
1,226 Discussing
9
#SouthKoreaConsidersEducationTaxOnCryptoExchanges
67,776 views
859 Discussing
10
#OCCUrgesCommunityBanksToEnterStablecoinPayments
45,266 views
610 Discussing