

#lazarusgroup
lazarusgroup
1.4M views
391 Discussing
Hot
Latest


·
--
NOW HACKERS ARE START SELLING ETH 🤯.
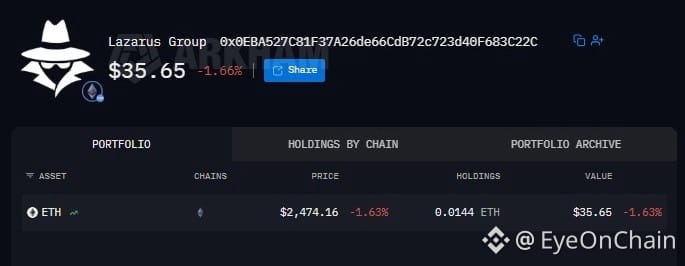
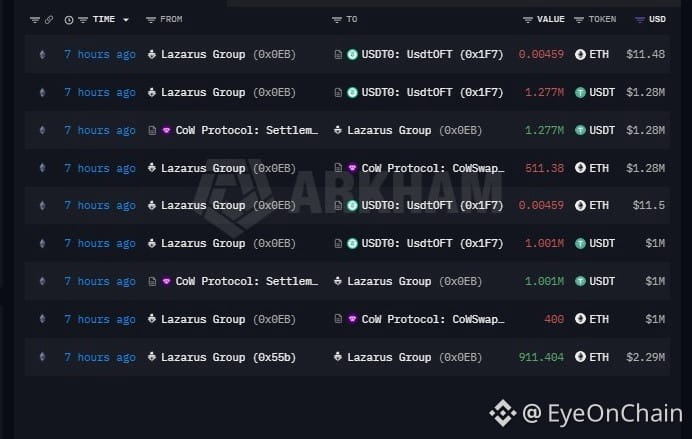
Lazarus Group Just Moved Another $2.28M in $ETH . The wallets linked to the #LazarusGroup have sold 911 ETH, worth around $2.28M, over the past 7 hours at an average price of roughly $2,499.
Worth keeping an eye on this address to see if more ETH gets moved or sold next.
Address: 0x0EBA527C81F37A26de66CdB72c723d40F683C22C
{future}(ETHUSDT)
{spot}(ETHUSDT)
NOW HACKERS ARE START SELLING ETH 🤯.
Lazarus Group Just Moved Another $2.28M in $ETH . The wallets linked to the #LazarusGroup have sold 911 ETH, worth around $2.28M, over the past 7 hours at an average price of roughly $2,499.
Worth keeping an eye on this address to see if more ETH gets moved or sold next.
Address: 0x0EBA527C81F37A26de66CdB72c723d40F683C22C
1
8
3.3k

Lazarus Group Hits Hyperliquid with $30M Move
Sanctioned Lazarus Group wallets moved $30M through Hyperliquid, posing significant regulatory risks for the decentralized exchange.
#LazarusGroup #Hyperliquid
Lazarus Group Hits Hyperliquid with $30M Move
Sanctioned Lazarus Group wallets moved $30M through Hyperliquid, posing significant regulatory risks for the decentralized exchange.
#LazarusGroup #Hyperliquid
Sanctioned Lazarus Group wallets moved $30M through Hyperliquid, posing significant regulatory risks for the decentralized exchange.
#LazarusGroup #Hyperliquid
1
11
Blockchain data reviewed by CoinDesk shows that wallets linked to North Korea's Lazarus Group sold more than $30 million in Bitcoin ($BTC) on the Hyperliquid platform within a three-week span.
These large-scale sales coincided with efforts by political figures to bring the trading platform under onshore regulation. Does this level of transaction activity suggest decentralized venues are becoming primary outlets for illicit asset movement?
#Crypto #Bitcoin #LazarusGroup #Hyperliquid #Cybersecurity
Blockchain data reviewed by CoinDesk shows that wallets linked to North Korea's Lazarus Group sold more than $30 million in Bitcoin ($BTC ) on the Hyperliquid platform within a three-week span.
These large-scale sales coincided with efforts by political figures to bring the trading platform under onshore regulation. Does this level of transaction activity suggest decentralized venues are becoming primary outlets for illicit asset movement?
#Crypto #Bitcoin #LazarusGroup #Hyperliquid #Cybersecurity
70

Lazarus Group bán hơn 30 triệu USD Bitcoin trên Hyperliquid
- Dữ liệu blockchain từ CoinDesk cho thấy nhóm Lazarus thuộc Triều Tiên đã bán hơn 30 triệu USD bitcoin trên Hyperliquid trong 3 tuần qua.
- Vụ việc diễn ra trong bối cảnh Trump đẩy mạnh nỗ lực đưa nền tảng crypto về Mỹ.
- Nguồn: CoinDesk.
#BinanceSquare #CryptoNews #Bitcoin #Hyperliquid #LazarusGroup
$btc btc
vlikevn Titanbot
Nguồn: CoinDesk
37
·
--
ETH: 🚀 Arbitrum just froze $70M worth of ETH in response to the KelpDAO hack ✅
The attacker moved over $176M across multiple chains, with Bitcoin becoming their new playground. 💾
By intervening early, Arbitrum prevented roughly 29% of the stolen funds from entering the laundering pipeline 🔄
A race against time ensued as investigators tracked the thief's rapid moves through THORChain and other decentralized protocols 🔮
Lazarus Group is suspected to be behind this brazen move, using complex tactics to obscure their tracks. 🔍
Is the remaining $176M still in play? Let's watch closely! 💬
Will these funds find a safe haven or will they slip through our fingers? 🛑
Are we overthinking this situation or is there real risk here? 👇
#ETH #KelpDAO #LazarusGroup
47
·
--
Arbitrum Seals a Win, but the Hunt Continues 🛡️
Arbitrum has frozen 30,766 ETH worth over $70 million linked to the KelpDAO exploit, preventing roughly 29% of stolen funds from entering the laundering pipeline. However, the attacker is still moving assets across multiple chains and protocols, including Bitcoin. This high-level operational discipline hints at a sophisticated threat actor behind the scenes.
The Lazarus Group has been linked to previous crypto thefts using similar tactics. With over $176 million already laundered through various decentralized bridges, the race against time continues for blockchain investigators and law enforcement agencies.
Is the Lazarus Group involved in this operation? Share your thoughts below! 💬
#Arbitrum #KelpDAO #LazarusGroup
47
·
--
😱 #MetaMask Parent Company Accidentally Hired a North Korean Hacker!
Consensys, the company behind MetaMask, reportedly hired a developer under the alias "Tyler Knapp" through a third-party recruiting firm.
🇰🇵 About a month later, the company discovered the developer was allegedly linked to North Korea's #LazarusGroup . During that time, he contributed code to a feature related to #crypto -to-fiat conversion.
Even more concerning, the same individual had previously worked at Ankr, Blueberry Protocol, DEPO, Pickle Finance, and Harmony—projects that were all later exploited, although that alone does not prove a connection to those hacks.
🛡 The incident highlights how sophisticated state-sponsored infiltration has become. If a major player like Consensys can be targeted, smaller crypto companies with fewer security resources may face an even greater challenge.
#BurnhamToBecomeUKPrimeMinister @wisegbevecryptonews9
😱 #MetaMask Parent Company Accidentally Hired a North Korean Hacker!
Consensys, the company behind MetaMask, reportedly hired a developer under the alias "Tyler Knapp" through a third-party recruiting firm.
🇰🇵 About a month later, the company discovered the developer was allegedly linked to North Korea's #LazarusGroup . During that time, he contributed code to a feature related to #crypto -to-fiat conversion.
Even more concerning, the same individual had previously worked at Ankr, Blueberry Protocol, DEPO, Pickle Finance, and Harmony—projects that were all later exploited, although that alone does not prove a connection to those hacks.
🛡 The incident highlights how sophisticated state-sponsored infiltration has become. If a major player like Consensys can be targeted, smaller crypto companies with fewer security resources may face an even greater challenge.
#BurnhamToBecomeUKPrimeMinister @WISE PUMPS
2
1.5k
·
--
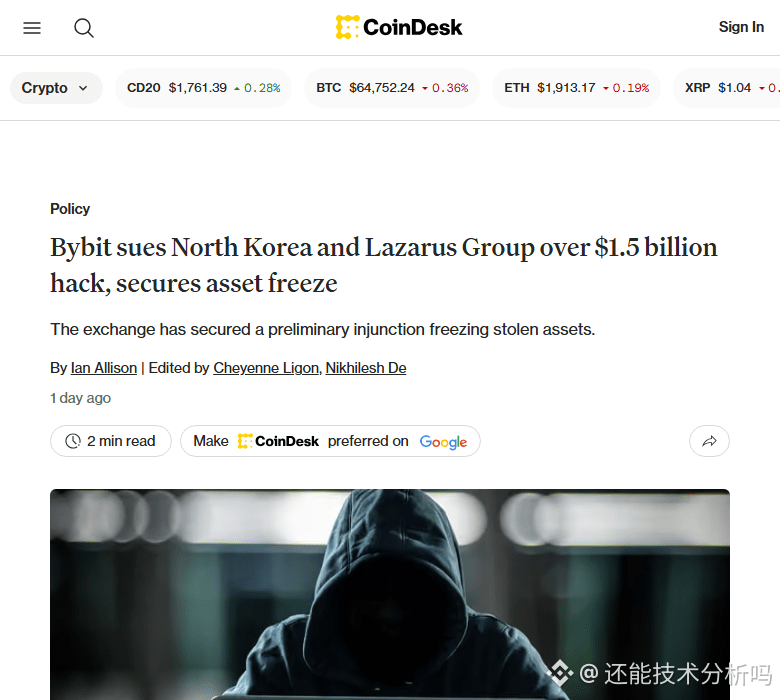
Bybit正式起诉朝鲜及Lazarus Group,追讨15亿美元被盗资产,并获法院初步禁令冻结相关资金。这是加密交易所首次对主权国家发起法律行动,为行业维权树立新标杆。链上追踪与法律手段结合,或成应对国家级黑客的常态路径。
#Bybit #LazarusGroup #加密货币安全 #法律维权
Bybit正式起诉朝鲜及Lazarus Group,追讨15亿美元被盗资产,并获法院初步禁令冻结相关资金。这是加密交易所首次对主权国家发起法律行动,为行业维权树立新标杆。链上追踪与法律手段结合,或成应对国家级黑客的常态路径。
#Bybit #LazarusGroup #加密货币安全 #法律维权
#Bybit #LazarusGroup #加密货币安全 #法律维权
50

Un tribunal de EEUU otorgó al intercambio Bybit una orden preliminar para congelar activos vinculados al hackeo del Grupo Lazarus de US$1.5 mil millones en 2025, determinando que el intercambio demostró una probabilidad de éxito en el fondo del asunto. La orden prohíbe de forma inmediata a los demandados transferir, vender o dilapidar los activos robados identificados que aún se encuentren en plataformas u organismos bajo jurisdicción de la corte.
A pesar de que gran parte de los fondos fue rápidamente desviada e intercambiada en los días posteriores al ataque, este fallo judicial sienta un precedente importante al permitir que las víctimas de ciberataques estatales utilicen herramientas legales civiles en EEUU para rastrear y bloquear activos vinculados a grupos como Lazarus a medida que intentan introducirlos al sistema financiero.
#LazarusGroup #bybit #HackerAlert #EEUU #CoreaDelNorte $BTC $ETH
{web3_wallet_create}(CT_5014SoQ8UkWfeDH47T56PA53CZCeW4KytYCiU65CwBWoJUt)
{web3_wallet_create}(10880xeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeeee)
Un tribunal de EEUU otorgó al intercambio Bybit una orden preliminar para congelar activos vinculados al hackeo del Grupo Lazarus de US$1.5 mil millones en 2025, determinando que el intercambio demostró una probabilidad de éxito en el fondo del asunto. La orden prohíbe de forma inmediata a los demandados transferir, vender o dilapidar los activos robados identificados que aún se encuentren en plataformas u organismos bajo jurisdicción de la corte.
A pesar de que gran parte de los fondos fue rápidamente desviada e intercambiada en los días posteriores al ataque, este fallo judicial sienta un precedente importante al permitir que las víctimas de ciberataques estatales utilicen herramientas legales civiles en EEUU para rastrear y bloquear activos vinculados a grupos como Lazarus a medida que intentan introducirlos al sistema financiero.
#LazarusGroup #bybit #HackerAlert #EEUU #CoreaDelNorte $BTC $ETH
258
·
--
Bearish
🇰🇵 LATEST: Byblt has sued North Korea and the Lazarus Group over the $1.5 billion hack and has secured a preliminary court order freezing stolen assets. $BTC $ETH
{future}(ETHUSDT)
{future}(BTCUSDT)
#LazarusGroup #HackerAlert
🇰🇵 LATEST: Byblt has sued North Korea and the Lazarus Group over the $1.5 billion hack and has secured a preliminary court order freezing stolen assets. $BTC $ETH
#LazarusGroup #HackerAlert
#LazarusGroup #HackerAlert
1
782

🚨 $BTC WATCHES TOP EXCHANGE FREEZE $1.5B LAZARUS LOOT — NORTH KOREA SUED! ⚡
This is the kind of announcement that doesn't hit price instantly but quietly rewires the entire risk map. A top-tier exchange just took North Korea, its spy agency, and Lazarus Group straight to federal court over that $1.5B theft — and secured a preliminary injunction that nails the stolen goods in place. 🔍
Key detail: a list of unnamed "John Doe" defendants can no longer transfer or sell the frozen assets while the case moves. That removes one giant overhang of potential sell pressure from the market. 🌊
The exchange stresses this civil action is separate from U.S. criminal probes — meaning more dominoes are still falling. ⚡ 💬 Will this legal pressure force the hackers to move through darker corridors, or is $1.5B already washed clean? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #CryptoNews #LazarusGroup #ExchangeSecurity
🦈 ⚡
18

·
--
Have you noticed how the market treats billion-dollar hacks like temporary noise instead of structural risk?
Traders obsess over entries on $BTC, $ETH, and $BNB, but one exploit can freeze liquidity, trigger panic selling, and wreck confidence across the board. The painful part is most people only price in security risk after the damage is already done.
This case is a real reminder. A major crypto exchange is reportedly suing North Korea over an alleged $1.5 billion Lazarus Group crypto heist, while a U.S. federal court has granted a preliminary injunction to freeze identified assets tied to the hack.
The mainstream take is usually “hackers stole funds, move on.” I think that misses the bigger point. If courts can track and freeze assets linked to state-backed crypto theft, then enforcement is becoming part of the market structure, not just an after-the-fact headline.
That changes how investors should think about exchange risk, custody, and even liquidity during black swan events. Security is not a side topic anymore. It is part of the trade.
Where do you think this goes from here?
#CryptoSecurity #LazarusGroup #CryptoMarket
Have you noticed how the market treats billion-dollar hacks like temporary noise instead of structural risk?
Traders obsess over entries on $BTC , $ETH , and $BNB , but one exploit can freeze liquidity, trigger panic selling, and wreck confidence across the board. The painful part is most people only price in security risk after the damage is already done.
This case is a real reminder. A major crypto exchange is reportedly suing North Korea over an alleged $1.5 billion Lazarus Group crypto heist, while a U.S. federal court has granted a preliminary injunction to freeze identified assets tied to the hack.
The mainstream take is usually “hackers stole funds, move on.” I think that misses the bigger point. If courts can track and freeze assets linked to state-backed crypto theft, then enforcement is becoming part of the market structure, not just an after-the-fact headline.
That changes how investors should think about exchange risk, custody, and even liquidity during black swan events. Security is not a side topic anymore. It is part of the trade.
Where do you think this goes from here?
#CryptoSecurity #LazarusGroup #CryptoMarket
25
🇰🇵 ÚLTIMA HORA: Byblt ha demandado a Corea del Norte y al Grupo Lazarus por el hackeo de 1.500 millones de dólares y ha obtenido una orden judicial preliminar para congelar los activos robados. $BTC $ETH
#LazarusGroup #HackerAlert
🇰🇵 ÚLTIMA HORA: Byblt ha demandado a Corea del Norte y al Grupo Lazarus por el hackeo de 1.500 millones de dólares y ha obtenido una orden judicial preliminar para congelar los activos robados. $BTC $ETH
#LazarusGroup #HackerAlert
#LazarusGroup #HackerAlert
3
395
🚨 Bybit Just Sued North Korea — And a Judge Already Froze the Stolen Crypto
A crypto exchange just took on an entire nation-state in federal court — and won round one.
Bybit isn't just chasing hackers anymore — it's taking on a sovereign state in federal court. The world's second-largest crypto exchange filed a civil RICO lawsuit in the U.S. District Court for D.C. against North Korea, its Reconnaissance General Bureau, and the state-linked Lazarus Group over the record $1.5B Ethereum hack from February 2025 — still the largest crypto heist ever recorded.
The suit, filed under seal in June and made public this week, already has teeth: a federal judge issued a restraining order, then a preliminary injunction on July 30 freezing stolen assets tied to unidentified holders. Bybit says it has recovered $48.4M and frozen another $30.5M across 28+ exchanges, though over 90% of the funds remain untraced.
Lazarus Group has hit crypto before — the $620M Ronin and $100M Harmony hacks — and this suit argues it's all one racketeering pattern. Stolen crypto can now be legally chased, even to a nation-state's doorstep.
Think Bybit recovers the rest? Like, comment, and follow for more crypto justice updates. ⚖️
#Bybit #LazarusGroup #CryptoSecurity
$ETH
{spot}(ETHUSDT)
🚨 Bybit Just Sued North Korea — And a Judge Already Froze the Stolen Crypto
A crypto exchange just took on an entire nation-state in federal court — and won round one.
Bybit isn't just chasing hackers anymore — it's taking on a sovereign state in federal court. The world's second-largest crypto exchange filed a civil RICO lawsuit in the U.S. District Court for D.C. against North Korea, its Reconnaissance General Bureau, and the state-linked Lazarus Group over the record $1.5B Ethereum hack from February 2025 — still the largest crypto heist ever recorded.
The suit, filed under seal in June and made public this week, already has teeth: a federal judge issued a restraining order, then a preliminary injunction on July 30 freezing stolen assets tied to unidentified holders. Bybit says it has recovered $48.4M and frozen another $30.5M across 28+ exchanges, though over 90% of the funds remain untraced.
Lazarus Group has hit crypto before — the $620M Ronin and $100M Harmony hacks — and this suit argues it's all one racketeering pattern. Stolen crypto can now be legally chased, even to a nation-state's doorstep.
Think Bybit recovers the rest? Like, comment, and follow for more crypto justice updates. ⚖️
#Bybit #LazarusGroup #CryptoSecurity
$ETH
97
#BitgetBreachForgedRequestsNotStolenKeys
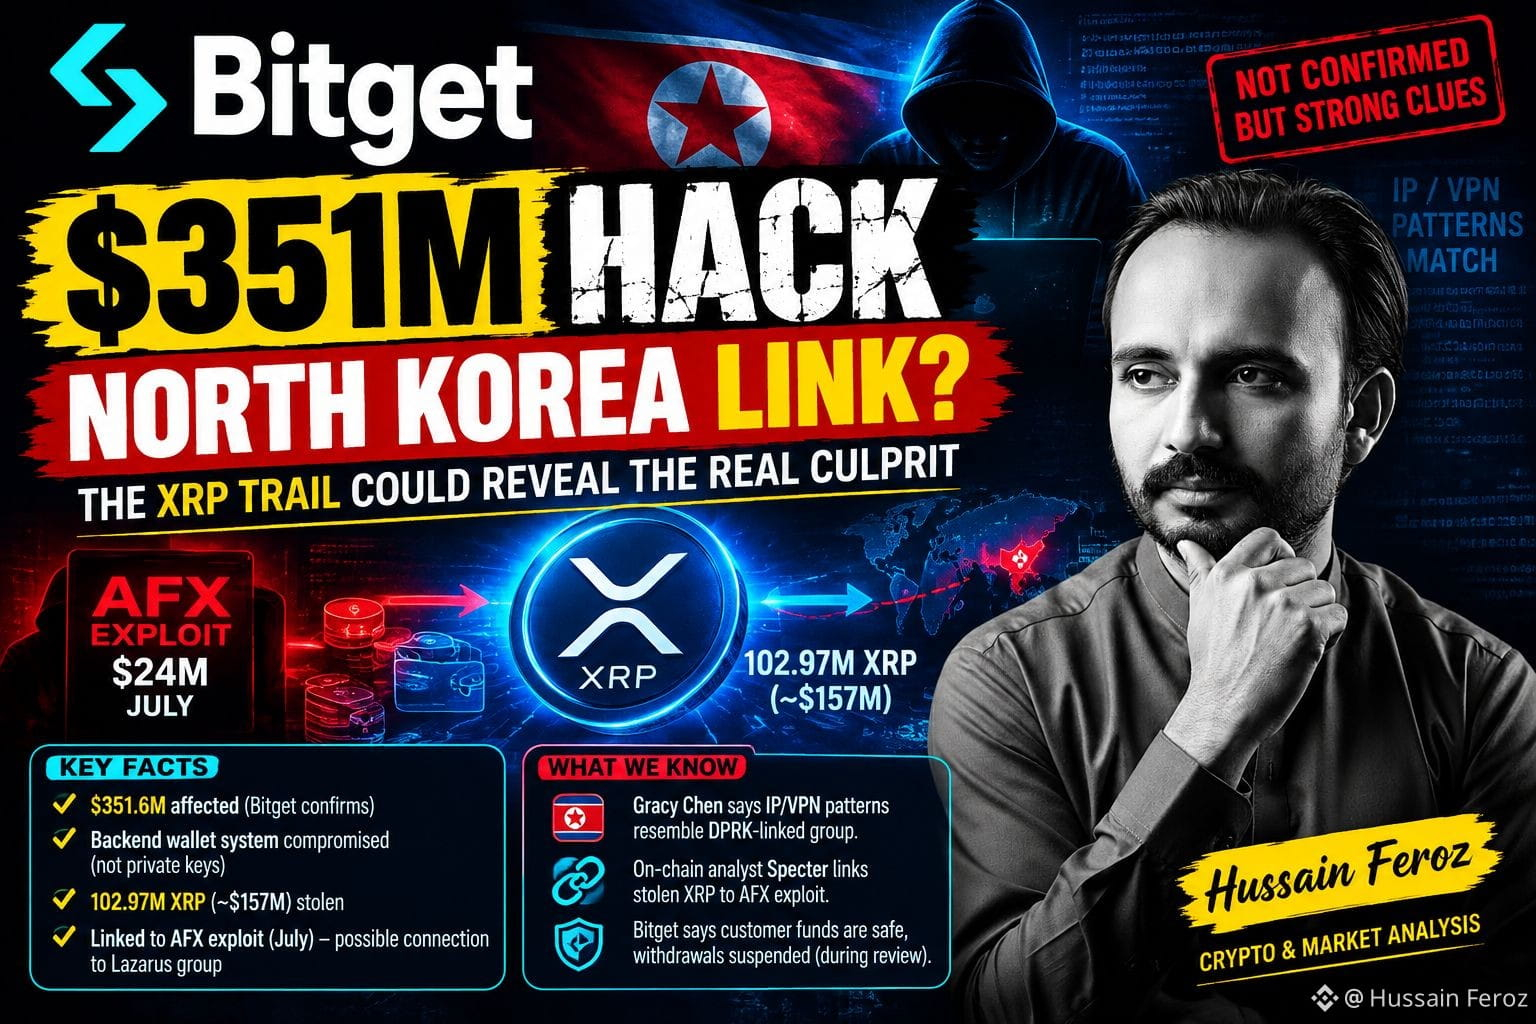
EXCLUSIVE: THE BITGET $351.6M HACK MAY HAVE LEFT A BIGGER CLUE
Everyone is talking about the possible North Korea connection.
But the more interesting clue may be hiding on-chain. 👀
🔎 What investigators are seeing:
• Bitget says ~$351.6M was affected across its wallet infrastructure
• The attacker reportedly compromised a backend wallet system, spoofed transaction data and triggered the normal authorization process
• Private keys were NOT compromised, according to Bitget
• Around 102.97M XRP — roughly $157M — was among the largest stolen portions
• On-chain analyst Specter says the stolen XRP can be traced to funds connected to the $24M AFX exploit from July
• That AFX incident has been associated with the TraderTraitor/Lazarus ecosystem
And there’s another clue:
Bitget CEO Gracy Chen says some attacker IP/VPN patterns resemble infrastructure previously associated with a North Korea-linked group.
⚠️ But this is NOT final attribution yet.
The real question now is:
Did the same North Korea-linked operation move from the AFX exploit to Bitget?
If the XRP trail + infrastructure evidence is independently confirmed, this could turn the Bitget incident from a massive exchange hack into another major Lazarus-linked operation.
💰 Bitget says its $464M+ User Protection Fund can cover the affected amount, while withdrawals remain suspended during the security review.
👀 Watch the XRP wallets.
The blockchain may reveal who is behind the attack before the official investigation does.
#Bitget #XRP #CryptoHack #LazarusGroup #NorthKorea #CryptoSecurity #CryptoNews
1
97
·
--
Bearish
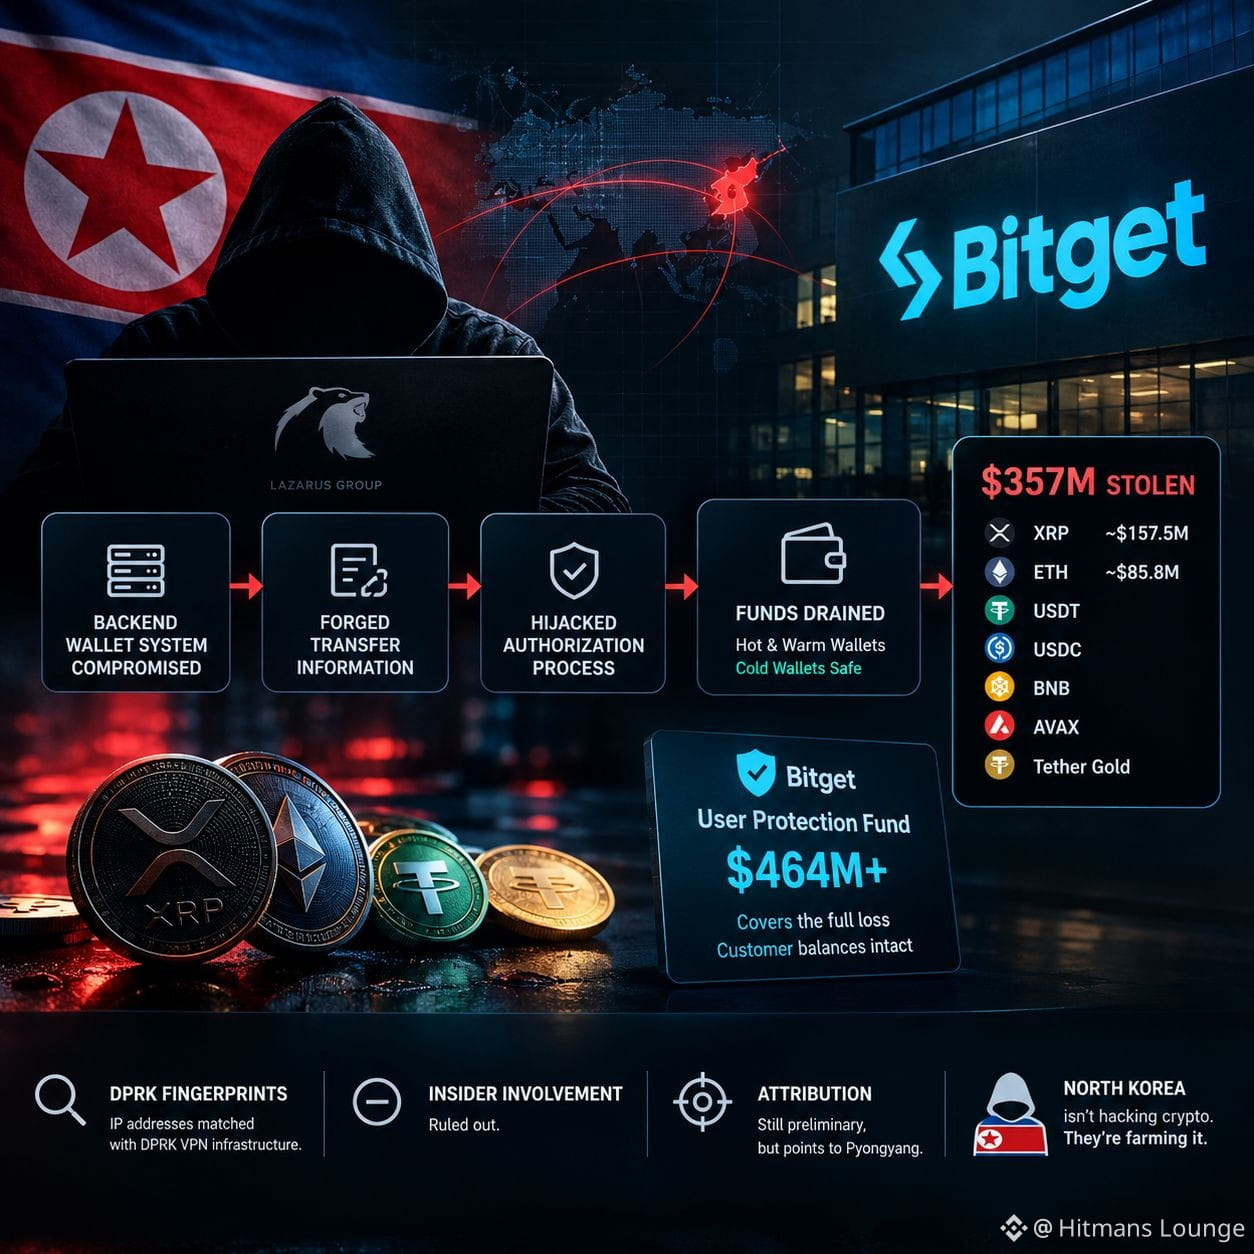
🚨🔥 BITGET HACKED FOR $351.6M ? — AND SEEMS LIKE NORTH KOREA'S FINGERPRINTS ARE ALL OVER IT.
CEO Gracy Chen went live on X hours after the breach and dropped a bombshell: "We've identified some IP addresses that match the VPN choices by a certain DPRK group."
She added: "The pattern looks very much like what the North Korean team did before."
And here's where it gets wilder — the hackers didn't steal private keys. They breached Bitget's backend wallet system and forged transfer information, hijacking the legitimate authorization signing process to silently bleed the exchange dry. 19 transfers. Hot wallets and warm wallets drained. Cold wallets untouched.
Assets taken?
👻 $157.5M in XRP
👻 $85.8M in ETH
👻 USDT, USDC, BNB, AVAX & Tether Gold — $357M in total.
The silver lining: Bitget's User Protection Fund holds over $464M — enough to cover the full loss. Customer balances remain intact.
Insider involvement? Ruled out. Attribution? Still preliminary — but the evidence is pointing hard at Pyongyang.
North Korea isn't hacking crypto. They're farming it.
💀 #Bitget #NorthKorea #LazarusGroup #CryptoSecurity #DPRK
$QI $BREW $SUI
{future}(SUIUSDT)
{alpha}(560xfa6d9b504848606eb9aec04ccc161d169b3f2159)
{spot}(QIUSDT)
🚨🔥 BITGET HACKED FOR $351.6M ? — AND SEEMS LIKE NORTH KOREA'S FINGERPRINTS ARE ALL OVER IT.
CEO Gracy Chen went live on X hours after the breach and dropped a bombshell: "We've identified some IP addresses that match the VPN choices by a certain DPRK group."
She added: "The pattern looks very much like what the North Korean team did before."
And here's where it gets wilder — the hackers didn't steal private keys. They breached Bitget's backend wallet system and forged transfer information, hijacking the legitimate authorization signing process to silently bleed the exchange dry. 19 transfers. Hot wallets and warm wallets drained. Cold wallets untouched.
Assets taken?
👻 $157.5M in XRP
👻 $85.8M in ETH
👻 USDT, USDC, BNB, AVAX & Tether Gold — $357M in total.
The silver lining: Bitget's User Protection Fund holds over $464M — enough to cover the full loss. Customer balances remain intact.
Insider involvement? Ruled out. Attribution? Still preliminary — but the evidence is pointing hard at Pyongyang.
North Korea isn't hacking crypto. They're farming it.
💀 #Bitget #NorthKorea #LazarusGroup #CryptoSecurity #DPRK
$QI $BREW $SUI
1
1.1k
·
--
Article
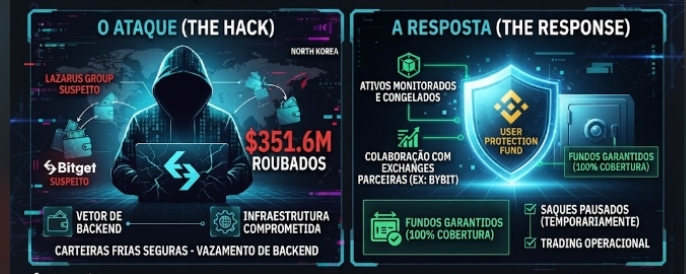
🕵️♂️ Atualização Bitget ($351.6M): Quem está por trás do ataque e novos detalhes técnicosA comunidade cripto continua em alerta máximo após o incidente de segurança da Bitget. Novas declarações da CEO Gracy Chen e análises on-chain trouxeram à tona informações cruciais sobre os suspeitos e a dinâmica da invasão:
Principal Suspeito (Coreia do Norte / Grupo Lazarus): A CEO da Bitget apontou publicamente indícios de forte ligação com hackers norte-coreanos (DPRK). A suspeita foi levantada após o rastreamento de endereços IP e padrões de VPN idênticos aos utilizados em ataques anteriores atribuídos ao regime. Pesquisadores on-chain independentes também rastrearam parte dos fundos para endereços associados a redes de hackers como o TraderTraitor.
Como o ataque aconteceu? (Detalhes Técnicos):
A administração descartou o vazamento de chaves privadas. As carteiras frias (cold wallets) continuam completamente seguras e isoladas.
O vetor de ataque consistiu na invasão de um sistema de backend da infraestrutura de gerenciamento de carteiras. Os invasores conseguiram manipular processos de assinatura de transações sem precisar falsificar solicitações de saque de clientes comuns.
A hipótese de envolvimento interno (inside job) foi inicialmente descartada pela diretoria, embora as investigações forenses continuem em aberto.
to.
Recuperação e Status Atual:
Parte dos ativos desviados já está sendo monitorada e há esforços conjuntos com outras grandes exchanges (como a Bybit, que ofereceu suporte) para congelar endereços de destino.
O User Protection Fund (fundo de mais de US$ 464 milhões) segue garantido para cobrir 100% das perdas dos usuários afetados.
Os saques continuam temporariamente pausados por precaução enquanto a equipe endurece as barreiras de segurança, mas o trading e os depósitos operam normalmente.
.
Um relatório técnico completo (post-mortem) detalhando a causa raiz exata e o avanço da recuperação dos fundos deve ser divulgado em breve.
#Bitget #LazarusGroup #CriptoNoticias #SegurancaCripto #BinanceSquare $BTC $AVAX
{spot}(AVAXUSDT)
🕵️♂️ Atualização Bitget ($351.6M): Quem está por trás do ataque e novos detalhes técnicos
A comunidade cripto continua em alerta máximo após o incidente de segurança da Bitget. Novas declarações da CEO Gracy Chen e análises on-chain trouxeram à tona informações cruciais sobre os suspeitos e a dinâmica da invasão:
Principal Suspeito (Coreia do Norte / Grupo Lazarus): A CEO da Bitget apontou publicamente indícios de forte ligação com hackers norte-coreanos (DPRK). A suspeita foi levantada após o rastreamento de endereços IP e padrões de VPN idênticos aos utilizados em ataques anteriores atribuídos ao regime. Pesquisadores on-chain independentes também rastrearam parte dos fundos para endereços associados a redes de hackers como o TraderTraitor.
Como o ataque aconteceu? (Detalhes Técnicos):
A administração descartou o vazamento de chaves privadas. As carteiras frias (cold wallets) continuam completamente seguras e isoladas.
O vetor de ataque consistiu na invasão de um sistema de backend da infraestrutura de gerenciamento de carteiras. Os invasores conseguiram manipular processos de assinatura de transações sem precisar falsificar solicitações de saque de clientes comuns.
A hipótese de envolvimento interno (inside job) foi inicialmente descartada pela diretoria, embora as investigações forenses continuem em aberto.
to.
Recuperação e Status Atual:
Parte dos ativos desviados já está sendo monitorada e há esforços conjuntos com outras grandes exchanges (como a Bybit, que ofereceu suporte) para congelar endereços de destino.
O User Protection Fund (fundo de mais de US$ 464 milhões) segue garantido para cobrir 100% das perdas dos usuários afetados.
Os saques continuam temporariamente pausados por precaução enquanto a equipe endurece as barreiras de segurança, mas o trading e os depósitos operam normalmente.
.
Um relatório técnico completo (post-mortem) detalhando a causa raiz exata e o avanço da recuperação dos fundos deve ser divulgado em breve.
#Bitget #LazarusGroup #CriptoNoticias #SegurancaCripto #BinanceSquare $BTC $AVAX
3
2.5k
·
--
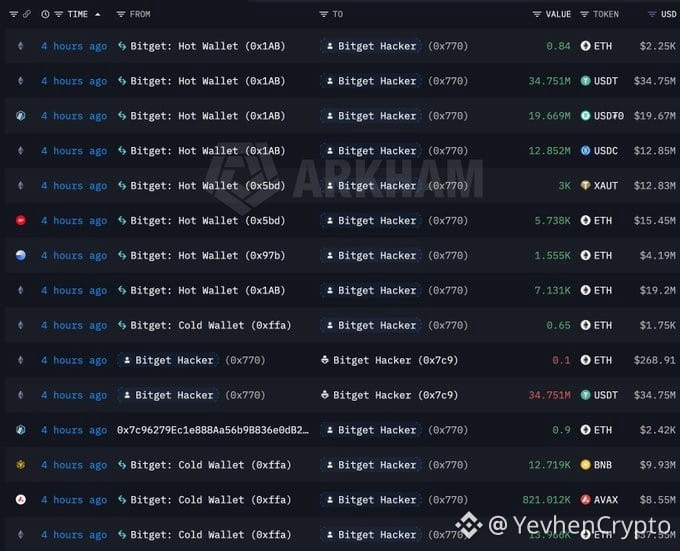
🚨 Bitget зазнав зламу на $351.6M: що відомо зараз
Централізована криптобіржа Bitget виявила підозрілі та незапитувані трансфери коштів. Основні деталі інциденту:
🔹 Масштаб: Постраждало близько $351.6 млн у цифрових активах.
🔹 Зона ураження: Злам зачепив лише частину інфраструктури гарячих і теплих гаманців.
🔹 Холодні гаманці: За заявою біржі, вони перебувають у повній безпеці.
🔹 Статус коштів та виведення: Виведення коштів тимчасово призупинено на час безпекової перевірки. Депозити продовжують працювати. Баланси користувачів ідентифіковані та залишаються в безпеці.
🔹 Підозрювані: CEO Bitget вказує на ймовірну причетність хакерського угруповання Lazarus Group (яке раніше пов'язували із масштабованим зламом Bybit на $1.46B у 2025 році).
🔹 Механіка атаки: Зловмисники підробили дані транзакцій та запустили процес авторизації для переміщення коштів. Компрометацію приватних ключів виключено.
💡 Порада для користувачів: Без паніки - чекайте офіційних оновлень від Bitget щодо відновлення виведення коштів. І як завжди: тримайте свої довгострокові активи на холодних гаманцях!
#Bitget #CryptoHack #LazarusGroup #CryptoNews #Web3Safety
2
455
Bitget hack: hơn 157 triệu USD XRP bị đánh cắp, Lazarus bị tình nghi
- Bitget xác nhận chuyển khoản trái phép từ một số ví nóng và ví ấm, làm mất gần $351 triệu crypto.
- XRP là tài sản bị đánh cắp lớn nhất, trị giá gần $157,5 triệu.
- CEO Gracy Chen và một số nhà phân tích on-chain nghi ngờ Lazarus Group của Triều Tiên.
#XRP #CryptoNews #Bitget #LazarusGroup #BinanceSquare
$xrp
vlikevn Titanbot
Nguồn: CoinGape
102
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#GoldFallsTo$4144
1,256 views
36 Discussing
2
#QNTFallsOver40%FromMorningHigh
8,526 views
293 Discussing
3
#KospiFalls2.7%SamsungSKHynixDropOver5%
478 views
71 Discussing
4
#BitgetCEOConfirms$388MStolenInHack
426 views
18 Discussing
5
#BTCFallsBelow$83000
10,206 views
97 Discussing
6
#BitgetDetailsSecurityIncidentTimeline
7,698 views
245 Discussing
7
#BitcoinSpotETFs$2.39BWeeklyNetInflow
3,432 views
21 Discussing
8
#FedProposesPaymentStablecoinRules
33,389 views
609 Discussing
9
#ChinaMayLetAlibabaByteDanceBuyNvidiaChips
35,158 views
646 Discussing
10
#USChinaRelease$30BTariffCutProductLists
3,397 views
50 Discussing