If it passed an audit, why can a project still get hacked?
This is how I understand it: contracts that have been running for a long time and have stood the test of handling large amounts of funds are generally considered more reliable, but that still doesn’t mean they’re vulnerability-free.
In 2016, The DAO was attacked due to a reentrancy vulnerability. Ethereum then responded with a hard fork, while the unforked original chain continued as Ethereum Classic (ETC).
My habit now: remember to revoke token approvals for protocols you no longer use.
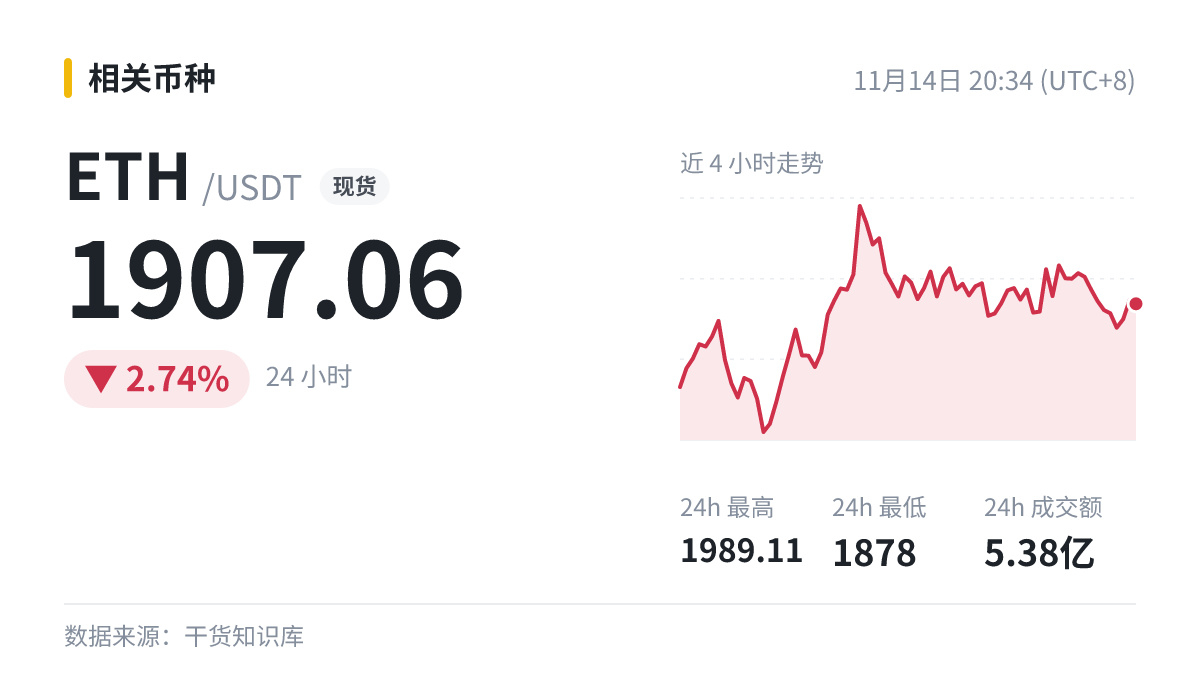
Ethereum, where $ETH is located, was one of the earliest public blockchains to support general-purpose smart contracts.
Don’t treat this as a buy or sell signal.
This is how I understand it: contracts that have been running for a long time and have stood the test of handling large amounts of funds are generally considered more reliable, but that still doesn’t mean they’re vulnerability-free.
In 2016, The DAO was attacked due to a reentrancy vulnerability. Ethereum then responded with a hard fork, while the unforked original chain continued as Ethereum Classic (ETC).
My habit now: remember to revoke token approvals for protocols you no longer use.
Ethereum, where $ETH is located, was one of the earliest public blockchains to support general-purpose smart contracts.
Don’t treat this as a buy or sell signal.