
MartIn-赚钱版
20 Posts

MartIn-赚钱版
Report
Block User
2 Following
44 Followers
36 Liked
Posts
·
--
Article
See translation
一场假面试,币安丢了 63 亿美元北京时间 10 月 30 日凌晨 4 点 05 分,币安五个热钱包开始往同一个陌生地址打 XRP。四分钟后停下,2.33 亿枚出去了。
4 点 20 分,以太坊上出现一笔怪交易,里面塞着 50 个 EIP-7702 授权,签名的是币安自己的 Binance14 热钱包。4 点 24 分,一笔转账带走 25.3 亿美元。
之后三个多小时,钱从 11 条链上往外流,直到早上 7 点 56 分最后一笔 ETH 上链。Elliptic 算下来一共 64.3 亿美元,币安自己的口径是约 63.4 亿。去年 2 月 Bybit 丢了约 15 亿,当时人人都说这是加密史上最大的一次。这次是它四倍多,Elliptic 的判断是,这几乎肯定是已知单笔最大的盗窃,不限于币圈。
10 月 31 日,FBI 点名:朝鲜干的。
整条攻击链里最要命的一环,是一名币安工程师在工作电脑上,跑了"面试官"发来的代码仓库。
11 月 3 日币安发了初步调查报告,加上 TRM、Chainalysis、Elliptic 这几天的链上追踪,整件事的来龙去脉已经能拼出来了。要说明的是,币安这份是初步报告,没经过独立第三方核实,部分技术细节它说为防模仿暂不公开。下文涉及推测的地方会标出来。
换了电脑,换不掉名单
故事从 6 月开始。
币安钱包运维团队的工程师 A 想装一款 AI 编程工具,搜着搜着,装上了一个被动过手脚的 Homebrew。币安报告里专门链了一篇 SANS 互联网风暴中心今年 5 月的分析:有人在搜索广告里挂假的 Homebrew 页面,让你复制一行命令进终端,装上的是窃密木马 MacSync Stealer。
币安安全团队发现了,给 A 换了电脑,重置了凭证。换谁都会觉得这事结了。
可报告里有句话很扎心:A 的岗位,还有 A 身边负责钱包基础设施的同事,已经暴露了。
电脑能换,密码能换,组织架构换不了。这里有个推测:攻击者从 A 身上拿走的最值钱的东西,可能是一份名单,币安里谁在管钱包,谁能碰到签名系统。
第二轮面试,对面自称 CEO
9 月,软件工程师 B 在一个正规求职平台上被人联系,对方自称项目总监。
第一轮是一位"HR"视频面试,还主动把自己的社交账号发过来,生活照视频都有,就是让你相信对面是个活人。第二轮换到一款常用聊天软件上,对面是一家根本不存在的公司的"CEO"。最后,对方发来一个代码仓库,让他做题。
B 在工作电脑上把它跑了起来。
配环境那一步,恶意脚本删掉了正常的 pyenv 文件,换成自己的版本,建了个软链接,再拉起一个 zsh。pyenv 是管 Python 版本的小工具,装完谁都不会多看一眼。藏在这儿,够阴。公司的终端防护当时没拦住,币安的说法是 0day。
这套话术在币圈不是第一次出现。2024 年 DMM Bitcoin 被盗 4502.9 枚 BTC,约 3.08 亿美元,FBI 联合日本警察厅的调查结论是:TraderTraitor 的人在 LinkedIn 上冒充招聘方,找上钱包软件公司 Ginco 一名有系统权限的员工,以"入职前测试"为名发来 GitHub 上的一段恶意 Python 脚本。2022 年 Ronin 跨链桥丢了约 6 亿美元,The Block 援引两名知情人的说法,一名高级工程师被 LinkedIn 上的假工作约了几轮面试,最后打开了一份带间谍软件的"录用通知"PDF,Sky Mavis 官方没确认过这个细节。再往前,美国 CISA 2022 年 4 月那份 TraderTraitor 通报就写了,他们专挑加密公司里做系统管理和 DevOps 的人,用高薪招聘当诱饵。
这招为什么一直灵?找工作的人想表现,题目就是要你下载要你运行,你不跑反而显得不专业。安全培训教你别点陌生链接,没人教你别做面试题。
他们等了一个多月
B 中招是 9 月,下一个动作在 10 月 20 日,动钱是 10 月 30 日凌晨。从 6 月算,小半年。
报告没解释为什么不早动手。合理的解释是,拿到一台工程师电脑离能动钱还很远,签名服务在哪、部署走什么流程、谁机器上有什么令牌,只能慢慢摸。
币安报告说,今年安全团队发现并拦下了 57 起疑似朝鲜相关的网络攻击。币安首席安全官 Jimmy Su 去年 8 月接受 Decrypt 采访时还说过,朝鲜的人每天都在试图应聘进币安。拦住 57 次,漏掉一次,代价 63 亿。
公司自己的 AI 工具替他们开了门
10 月 20 日,攻击者从 B 的电脑出发,借着币安内部的一款 AI 工具,拿下了另外两名钱包工程师的电脑:A 的新电脑,和钱包软件工程师 C 的电脑。
A 换了电脑,还是没逃掉。
报告用的词是"被攻破的内部 AI 工具",整改里也专门写了重建这个工具和它的访问控制。换句话说,被利用的是这个工具手里的权限。一个能帮你在同事机器上执行操作的内部工具,本身就是一张连着很多台电脑的网。平时它替你省事,换个人坐在 B 的位置上,它就替那个人省事。
在 A 的电脑上,攻击者找到了真正想要的东西:一个容器部署令牌,能在币安服务器上跑自己的代码。币安联席 CEO Richard Teng 后来说,攻击者并非只用了一名工程师的权限,整个过程也没有"一键"那么简单。
凌晨四点开工,白天先彩排
链上的准备比报告写的还早。据 Elliptic,10 月 28 到 29 日,一个新钱包从 Tornado Cash 收了三笔 0.1 ETH,TRM 和 Chainalysis 也都确认了这个混币器出资。北京时间 29 日 23 点 59 分,攻击者部署了一个"清扫"合约,而大约四小时前,他们已经在另一个钱包上彩排过一遍。
30 日凌晨 1 点 15 分到 3 点 56 分,攻击者登录 C 的电脑,用 A 的凭证部署容器,启动攻击脚本。脚本盯的是钱包签名服务,热钱包每一笔转账都要它盖章。
4 点 05 分 XRP 开始流出。随后 Solana 热钱包转出约 97.05 万枚 SOL,Optimism 转出约 4420 万枚 OP,比特币热钱包转出 18270 枚 BTC。TRM 的分析是,以太坊上靠 7702 委托,其余九条链都是"正常签名"的转账,说明攻击者能让币安的签名系统替他批单。7 点 05 分前后,Avalanche 和 Polygon 又来了第二波。
水龙头关了,水还在流
币安暂停了提现,停了热钱包服务。为什么没用?
因为那 50 个授权已经在链上设好了 EIP-7702 委托,把 Binance14 的部分执行权交给了攻击者的合约。7702 是以太坊去年 5 月 Pectra 升级加进来的,本意是让普通地址也能用上合约钱包的功能。委托写在链上,币安关掉自家系统,链上照样生效。Elliptic 指出,委托一直有效,后面又扫了四轮新充进来的钱,攻击者连新签名都不用。Richard Teng 的原话是,这个委托"没有经过我们正常的审批控制"。
想撤销,得这个钱包自己再签一笔。偏偏币安热钱包用的是 MPC,私钥拆成几份,没有任何一个人握着完整钥匙。这本来是防盗最好的那一档设计,轮到自己紧急签撤销时,同样没人能马上签出来。团队只能现场搞一套专门流程。防小偷的锁,把房主也锁在了门外。
7 点 56 分,最后一笔 2961.9 枚 ETH 确认。8 点 10 分,币安从 Binance14 发出一笔指向零地址的授权,清掉委托。之后再无未授权转账。
是谁干的
先说已经确认的。
10 月 31 日,FBI 联合特勤局和国税局刑事调查部门发布通告,称朝鲜对这次盗窃负责,点名 TraderTraitor,并公布了 628 个地址:608 个以太坊、19 个比特币、1 个 Solana,要求 THORChain 节点、跨链和兑换服务拒绝相关交易。去年 Bybit 那 15 亿,FBI 点的也是这个名字。币安报告引用的就是 FBI 这份通告,自己没有单独点名。
链上分析公司比 FBI 更早。案发当天,TRM 以"高度确信"归因 TraderTraitor。Chainalysis CEO Jonathan Levin 在 X 上写,"很可能是朝鲜组织 TraderTraitor 干的"。Elliptic 一开始的措辞是"很可能",FBI 公布后说这证实了他们的判断。CoinDesk 等媒体把 TraderTraitor 归为 Lazarus 旗下的一支。
证据主要几条。Chainalysis 说最有力的一条,是他们实时看到币安被盗的钱和 9 月 Bitget 被盗的钱混在了同一批钱包里,Bitget 那次被普遍认为是朝鲜干的。Elliptic 也确认了这点,截至 11 月 3 日,约 1600 万美元流进了同时装着 Bitget 赃款的地址。再加上 Tornado Cash 出资、和 BigONE、WOO X、AFX 等此前 TraderTraitor 案用过的服务重叠、长期潜伏和利用受害方自家签名系统的手法跟 Bybit 很像。
再说存疑的。11 月 3 日朝中社发了金与正的谈话,否认指控,说 FBI 想把朝鲜塑造成"网络犯罪国家"。AMLBot 的分析师也提醒,链上分析能把钱包串到一个行为者身上,但证明不了国籍。B 遇到的那个"项目总监"是不是 TraderTraitor 本人,币安报告没有逐环节写明,这一点目前只是根据手法做的推断。
64 亿都是什么,冻住了多少
Elliptic 的拆分最细。以太坊上 38 亿美元,涉及 186 种代币,其中 19 亿 USDT、8.23 亿 USDC;Binance14 一个钱包就被搬空了 167464 枚 ETH 和 63 种代币,包括 16 亿 USDT。比特币 18270 枚,约 14.8 亿美元。Tron 上 6.127 亿 USDT。XRP 2.33 亿枚。稳定币合计 34.6 亿美元。
稳定币多,对黑客是坏消息。北京时间 5 点 01 分前后,Tether 冻结攻击者主钱包,据 Elliptic 统计锁住 11.8 亿枚 USDT,17 分钟内又冻了四个地址。三分钟后,Circle 把 8.23 亿 USDC 全部冻住,一枚都没来得及换。Tether CEO Paolo Ardoino 说他们总共冻了超过 15.6 亿 USDT。Ripple 冻了 RLUSD,World Liberty、Paxos、First Digital 也冻了自家稳定币,具体数额都没公开。TRM 说 Arbitrum 安全委员会冻结了 8426 枚 ETH 和 7460 万枚 ARB,Optimism 治理把那 4400 万枚 OP 转出了攻击者地址,这两条链上被偷的东西全部被控制住了。
合计,Elliptic 核实冻结或扣押 28.5 亿美元,约占 44%,九成四是稳定币。币安报告也是约 28.5 亿,Chainalysis 截至 11 月 3 日的数字是约 28 亿。有律师在 CoinDesk 上提醒,冻结只是第一步,钱怎么回到币安还要走程序。
BTC、XRP、SOL、NEAR 这类原生资产,没有发行方能冻,一分都没冻住。
用户这边,币安的说法是损失平台扛,用 SAFU 基金和公司资金兜底,预留了超过 63.4 亿美元,其中 50 亿本来就是以被盗币种持有。截至 10 月 31 日,受影响资产补回 98%,可以去储备证明页面自己核,剩下一些流动性差的币还在市场和场外慢慢买。北京时间 11 月 1 日下午 2 点起分批恢复提现,比特币先开,11 月 2 日加上法币。据 SecurityWeek,重开当天就处理了约 46 亿美元的提现。
洗钱开了自动驾驶
冻结落下之前,攻击者抢跑了。Elliptic 统计,大约 7.86 亿美元稳定币在冻结前换成了 ETH 和 TRX。以太坊上,4.34 亿 USDT 通过 Uniswap、1inch 和做市商报价系统换成 160451 枚 ETH,比市价亏了 12% 到 26%,他们不在乎。另一个钱包把 5990 万 USDT 存进 Aave 当抵押,借出 19762 枚 ETH 就跑,Aave 随后冻结了相关市场。4800 万 RLUSD 在 Ripple 冻结前卖掉,另外约 150 种杂币在 DEX 上砸成 ETH。
Tron 那边,2.34 亿 USDT 在 SunSwap 换成 TRX。一个分发钱包从 30 日上午 10 点 19 分开始往外打,51 小时打了 1113 笔,中位间隔 90 秒,两个晚上都没停,金额精确到小数点后六位还各不相同。接收钱包通常两分钟内就转走。有跨链桥拒收,钱马上从新钱包重发到同一个目的地。Elliptic 说链上看不出背后是 AI 代理还是普通脚本,失败重试的样子更像脚本。
这些 TRX 走了至少六个跨链桥,截至 11 月 3 日至少 1.47 亿美元从 Tron 桥出去,几乎都变成了以太坊上的 ETH。THORChain 是最大的出口,截至 10 月 31 日约 3100 万美元。还有 1.28 亿枚 TRX 过了 JustLend,一部分换成号称"不可冻结"的 USDD。比特币那头,从 11 月 1 日开始有约 28 枚 BTC 进了 WabiSabi 混币,另有约 200 枚 BTC 是从 SOL、Tron 和 ETH 换过来的新币。
规模上,前三天半一共用了约 12000 个钱包、4 万多笔交易,光 Tron 就 7700 个地址。Chainalysis CEO 预计,攻击者接下来几周会用到几万个地址。
现在还剩多少?Elliptic 11 月 3 日的数字是约 31.8 亿美元,主要是 ETH 和 BTC,真正提现变现的估计微乎其微。18270 枚 BTC 拆在 19 个地址里,案发后一动没动。ETH 最大的九个地址握着 89%,10 月 30 日之后也没动,另有约 68600 枚散在 840 个小地址里。2.33 亿 XRP 在 11 月 2 日被挪到六个新地址,SOL 挪走了约 8.7 万枚,剩下约 82.5 万枚。Elliptic 的判断是,这些钱要洗好几个月,Bybit 那次就是这样。
这件事和普通人有什么关系
普通用户,钱在币安,按目前公开信息平台兜底,储备证明可以自己查。但要记住,交易所本身就是你的交易对手,64 亿的窟窿一家扛得住,换一家未必。大额长期不动的币放哪,值得重新想一遍。
写代码的人更该警惕,这份报告里每个入口都是日常操作。搜个工具顺手装,接个面试顺手跑,公司给个 AI 工具顺手全开权限。面试官发来的仓库,只在一台干净的虚拟机里跑,不登任何账号,不放任何钱包,跑完就删。Homebrew、pyenv 这类只从官网装,搜索结果里的广告链接一律跳过。对面的 HR 和 CEO 再像真人,也去对方公司官网找公开联系方式反查一遍。
在别的交易所做安全的,今晚就该拉个会。热钱包上有没有 7702 委托,有人在盯吗?MPC 紧急撤销流程写好了没有,演练过没有?内部 AI 工具能碰到哪些机器,部署令牌躺在哪些人的笔记本上?币安花 63 亿换来的这份报告,你免费就能读。
整条链子最开始,只是一个工程师想装一个 AI 编程工具。
一场假面试,币安丢了 63 亿美元
北京时间 10 月 30 日凌晨 4 点 05 分,币安五个热钱包开始往同一个陌生地址打 XRP。四分钟后停下,2.33 亿枚出去了。
4 点 20 分,以太坊上出现一笔怪交易,里面塞着 50 个 EIP-7702 授权,签名的是币安自己的 Binance14 热钱包。4 点 24 分,一笔转账带走 25.3 亿美元。
之后三个多小时,钱从 11 条链上往外流,直到早上 7 点 56 分最后一笔 ETH 上链。Elliptic 算下来一共 64.3 亿美元,币安自己的口径是约 63.4 亿。去年 2 月 Bybit 丢了约 15 亿,当时人人都说这是加密史上最大的一次。这次是它四倍多,Elliptic 的判断是,这几乎肯定是已知单笔最大的盗窃,不限于币圈。
10 月 31 日,FBI 点名:朝鲜干的。
整条攻击链里最要命的一环,是一名币安工程师在工作电脑上,跑了"面试官"发来的代码仓库。
11 月 3 日币安发了初步调查报告,加上 TRM、Chainalysis、Elliptic 这几天的链上追踪,整件事的来龙去脉已经能拼出来了。要说明的是,币安这份是初步报告,没经过独立第三方核实,部分技术细节它说为防模仿暂不公开。下文涉及推测的地方会标出来。
换了电脑,换不掉名单
故事从 6 月开始。
币安钱包运维团队的工程师 A 想装一款 AI 编程工具,搜着搜着,装上了一个被动过手脚的 Homebrew。币安报告里专门链了一篇 SANS 互联网风暴中心今年 5 月的分析:有人在搜索广告里挂假的 Homebrew 页面,让你复制一行命令进终端,装上的是窃密木马 MacSync Stealer。
币安安全团队发现了,给 A 换了电脑,重置了凭证。换谁都会觉得这事结了。
可报告里有句话很扎心:A 的岗位,还有 A 身边负责钱包基础设施的同事,已经暴露了。
电脑能换,密码能换,组织架构换不了。这里有个推测:攻击者从 A 身上拿走的最值钱的东西,可能是一份名单,币安里谁在管钱包,谁能碰到签名系统。
第二轮面试,对面自称 CEO
9 月,软件工程师 B 在一个正规求职平台上被人联系,对方自称项目总监。
第一轮是一位"HR"视频面试,还主动把自己的社交账号发过来,生活照视频都有,就是让你相信对面是个活人。第二轮换到一款常用聊天软件上,对面是一家根本不存在的公司的"CEO"。最后,对方发来一个代码仓库,让他做题。
B 在工作电脑上把它跑了起来。
配环境那一步,恶意脚本删掉了正常的 pyenv 文件,换成自己的版本,建了个软链接,再拉起一个 zsh。pyenv 是管 Python 版本的小工具,装完谁都不会多看一眼。藏在这儿,够阴。公司的终端防护当时没拦住,币安的说法是 0day。
这套话术在币圈不是第一次出现。2024 年 DMM Bitcoin 被盗 4502.9 枚 BTC,约 3.08 亿美元,FBI 联合日本警察厅的调查结论是:TraderTraitor 的人在 LinkedIn 上冒充招聘方,找上钱包软件公司 Ginco 一名有系统权限的员工,以"入职前测试"为名发来 GitHub 上的一段恶意 Python 脚本。2022 年 Ronin 跨链桥丢了约 6 亿美元,The Block 援引两名知情人的说法,一名高级工程师被 LinkedIn 上的假工作约了几轮面试,最后打开了一份带间谍软件的"录用通知"PDF,Sky Mavis 官方没确认过这个细节。再往前,美国 CISA 2022 年 4 月那份 TraderTraitor 通报就写了,他们专挑加密公司里做系统管理和 DevOps 的人,用高薪招聘当诱饵。
这招为什么一直灵?找工作的人想表现,题目就是要你下载要你运行,你不跑反而显得不专业。安全培训教你别点陌生链接,没人教你别做面试题。
他们等了一个多月
B 中招是 9 月,下一个动作在 10 月 20 日,动钱是 10 月 30 日凌晨。从 6 月算,小半年。
报告没解释为什么不早动手。合理的解释是,拿到一台工程师电脑离能动钱还很远,签名服务在哪、部署走什么流程、谁机器上有什么令牌,只能慢慢摸。
币安报告说,今年安全团队发现并拦下了 57 起疑似朝鲜相关的网络攻击。币安首席安全官 Jimmy Su 去年 8 月接受 Decrypt 采访时还说过,朝鲜的人每天都在试图应聘进币安。拦住 57 次,漏掉一次,代价 63 亿。
公司自己的 AI 工具替他们开了门
10 月 20 日,攻击者从 B 的电脑出发,借着币安内部的一款 AI 工具,拿下了另外两名钱包工程师的电脑:A 的新电脑,和钱包软件工程师 C 的电脑。
A 换了电脑,还是没逃掉。
报告用的词是"被攻破的内部 AI 工具",整改里也专门写了重建这个工具和它的访问控制。换句话说,被利用的是这个工具手里的权限。一个能帮你在同事机器上执行操作的内部工具,本身就是一张连着很多台电脑的网。平时它替你省事,换个人坐在 B 的位置上,它就替那个人省事。
在 A 的电脑上,攻击者找到了真正想要的东西:一个容器部署令牌,能在币安服务器上跑自己的代码。币安联席 CEO Richard Teng 后来说,攻击者并非只用了一名工程师的权限,整个过程也没有"一键"那么简单。
凌晨四点开工,白天先彩排
链上的准备比报告写的还早。据 Elliptic,10 月 28 到 29 日,一个新钱包从 Tornado Cash 收了三笔 0.1 ETH,TRM 和 Chainalysis 也都确认了这个混币器出资。北京时间 29 日 23 点 59 分,攻击者部署了一个"清扫"合约,而大约四小时前,他们已经在另一个钱包上彩排过一遍。
30 日凌晨 1 点 15 分到 3 点 56 分,攻击者登录 C 的电脑,用 A 的凭证部署容器,启动攻击脚本。脚本盯的是钱包签名服务,热钱包每一笔转账都要它盖章。
4 点 05 分 XRP 开始流出。随后 Solana 热钱包转出约 97.05 万枚 SOL,Optimism 转出约 4420 万枚 OP,比特币热钱包转出 18270 枚 BTC。TRM 的分析是,以太坊上靠 7702 委托,其余九条链都是"正常签名"的转账,说明攻击者能让币安的签名系统替他批单。7 点 05 分前后,Avalanche 和 Polygon 又来了第二波。
水龙头关了,水还在流
币安暂停了提现,停了热钱包服务。为什么没用?
因为那 50 个授权已经在链上设好了 EIP-7702 委托,把 Binance14 的部分执行权交给了攻击者的合约。7702 是以太坊去年 5 月 Pectra 升级加进来的,本意是让普通地址也能用上合约钱包的功能。委托写在链上,币安关掉自家系统,链上照样生效。Elliptic 指出,委托一直有效,后面又扫了四轮新充进来的钱,攻击者连新签名都不用。Richard Teng 的原话是,这个委托"没有经过我们正常的审批控制"。
想撤销,得这个钱包自己再签一笔。偏偏币安热钱包用的是 MPC,私钥拆成几份,没有任何一个人握着完整钥匙。这本来是防盗最好的那一档设计,轮到自己紧急签撤销时,同样没人能马上签出来。团队只能现场搞一套专门流程。防小偷的锁,把房主也锁在了门外。
7 点 56 分,最后一笔 2961.9 枚 ETH 确认。8 点 10 分,币安从 Binance14 发出一笔指向零地址的授权,清掉委托。之后再无未授权转账。
是谁干的
先说已经确认的。
10 月 31 日,FBI 联合特勤局和国税局刑事调查部门发布通告,称朝鲜对这次盗窃负责,点名 TraderTraitor,并公布了 628 个地址:608 个以太坊、19 个比特币、1 个 Solana,要求 THORChain 节点、跨链和兑换服务拒绝相关交易。去年 Bybit 那 15 亿,FBI 点的也是这个名字。币安报告引用的就是 FBI 这份通告,自己没有单独点名。
链上分析公司比 FBI 更早。案发当天,TRM 以"高度确信"归因 TraderTraitor。Chainalysis CEO Jonathan Levin 在 X 上写,"很可能是朝鲜组织 TraderTraitor 干的"。Elliptic 一开始的措辞是"很可能",FBI 公布后说这证实了他们的判断。CoinDesk 等媒体把 TraderTraitor 归为 Lazarus 旗下的一支。
证据主要几条。Chainalysis 说最有力的一条,是他们实时看到币安被盗的钱和 9 月 Bitget 被盗的钱混在了同一批钱包里,Bitget 那次被普遍认为是朝鲜干的。Elliptic 也确认了这点,截至 11 月 3 日,约 1600 万美元流进了同时装着 Bitget 赃款的地址。再加上 Tornado Cash 出资、和 BigONE、WOO X、AFX 等此前 TraderTraitor 案用过的服务重叠、长期潜伏和利用受害方自家签名系统的手法跟 Bybit 很像。
再说存疑的。11 月 3 日朝中社发了金与正的谈话,否认指控,说 FBI 想把朝鲜塑造成"网络犯罪国家"。AMLBot 的分析师也提醒,链上分析能把钱包串到一个行为者身上,但证明不了国籍。B 遇到的那个"项目总监"是不是 TraderTraitor 本人,币安报告没有逐环节写明,这一点目前只是根据手法做的推断。
64 亿都是什么,冻住了多少
Elliptic 的拆分最细。以太坊上 38 亿美元,涉及 186 种代币,其中 19 亿 USDT、8.23 亿 USDC;Binance14 一个钱包就被搬空了 167464 枚 ETH 和 63 种代币,包括 16 亿 USDT。比特币 18270 枚,约 14.8 亿美元。Tron 上 6.127 亿 USDT。XRP 2.33 亿枚。稳定币合计 34.6 亿美元。
稳定币多,对黑客是坏消息。北京时间 5 点 01 分前后,Tether 冻结攻击者主钱包,据 Elliptic 统计锁住 11.8 亿枚 USDT,17 分钟内又冻了四个地址。三分钟后,Circle 把 8.23 亿 USDC 全部冻住,一枚都没来得及换。Tether CEO Paolo Ardoino 说他们总共冻了超过 15.6 亿 USDT。Ripple 冻了 RLUSD,World Liberty、Paxos、First Digital 也冻了自家稳定币,具体数额都没公开。TRM 说 Arbitrum 安全委员会冻结了 8426 枚 ETH 和 7460 万枚 ARB,Optimism 治理把那 4400 万枚 OP 转出了攻击者地址,这两条链上被偷的东西全部被控制住了。
合计,Elliptic 核实冻结或扣押 28.5 亿美元,约占 44%,九成四是稳定币。币安报告也是约 28.5 亿,Chainalysis 截至 11 月 3 日的数字是约 28 亿。有律师在 CoinDesk 上提醒,冻结只是第一步,钱怎么回到币安还要走程序。
BTC、XRP、SOL、NEAR 这类原生资产,没有发行方能冻,一分都没冻住。
用户这边,币安的说法是损失平台扛,用 SAFU 基金和公司资金兜底,预留了超过 63.4 亿美元,其中 50 亿本来就是以被盗币种持有。截至 10 月 31 日,受影响资产补回 98%,可以去储备证明页面自己核,剩下一些流动性差的币还在市场和场外慢慢买。北京时间 11 月 1 日下午 2 点起分批恢复提现,比特币先开,11 月 2 日加上法币。据 SecurityWeek,重开当天就处理了约 46 亿美元的提现。
洗钱开了自动驾驶
冻结落下之前,攻击者抢跑了。Elliptic 统计,大约 7.86 亿美元稳定币在冻结前换成了 ETH 和 TRX。以太坊上,4.34 亿 USDT 通过 Uniswap、1inch 和做市商报价系统换成 160451 枚 ETH,比市价亏了 12% 到 26%,他们不在乎。另一个钱包把 5990 万 USDT 存进 Aave 当抵押,借出 19762 枚 ETH 就跑,Aave 随后冻结了相关市场。4800 万 RLUSD 在 Ripple 冻结前卖掉,另外约 150 种杂币在 DEX 上砸成 ETH。
Tron 那边,2.34 亿 USDT 在 SunSwap 换成 TRX。一个分发钱包从 30 日上午 10 点 19 分开始往外打,51 小时打了 1113 笔,中位间隔 90 秒,两个晚上都没停,金额精确到小数点后六位还各不相同。接收钱包通常两分钟内就转走。有跨链桥拒收,钱马上从新钱包重发到同一个目的地。Elliptic 说链上看不出背后是 AI 代理还是普通脚本,失败重试的样子更像脚本。
这些 TRX 走了至少六个跨链桥,截至 11 月 3 日至少 1.47 亿美元从 Tron 桥出去,几乎都变成了以太坊上的 ETH。THORChain 是最大的出口,截至 10 月 31 日约 3100 万美元。还有 1.28 亿枚 TRX 过了 JustLend,一部分换成号称"不可冻结"的 USDD。比特币那头,从 11 月 1 日开始有约 28 枚 BTC 进了 WabiSabi 混币,另有约 200 枚 BTC 是从 SOL、Tron 和 ETH 换过来的新币。
规模上,前三天半一共用了约 12000 个钱包、4 万多笔交易,光 Tron 就 7700 个地址。Chainalysis CEO 预计,攻击者接下来几周会用到几万个地址。
现在还剩多少?Elliptic 11 月 3 日的数字是约 31.8 亿美元,主要是 ETH 和 BTC,真正提现变现的估计微乎其微。18270 枚 BTC 拆在 19 个地址里,案发后一动没动。ETH 最大的九个地址握着 89%,10 月 30 日之后也没动,另有约 68600 枚散在 840 个小地址里。2.33 亿 XRP 在 11 月 2 日被挪到六个新地址,SOL 挪走了约 8.7 万枚,剩下约 82.5 万枚。Elliptic 的判断是,这些钱要洗好几个月,Bybit 那次就是这样。
这件事和普通人有什么关系
普通用户,钱在币安,按目前公开信息平台兜底,储备证明可以自己查。但要记住,交易所本身就是你的交易对手,64 亿的窟窿一家扛得住,换一家未必。大额长期不动的币放哪,值得重新想一遍。
写代码的人更该警惕,这份报告里每个入口都是日常操作。搜个工具顺手装,接个面试顺手跑,公司给个 AI 工具顺手全开权限。面试官发来的仓库,只在一台干净的虚拟机里跑,不登任何账号,不放任何钱包,跑完就删。Homebrew、pyenv 这类只从官网装,搜索结果里的广告链接一律跳过。对面的 HR 和 CEO 再像真人,也去对方公司官网找公开联系方式反查一遍。
在别的交易所做安全的,今晚就该拉个会。热钱包上有没有 7702 委托,有人在盯吗?MPC 紧急撤销流程写好了没有,演练过没有?内部 AI 工具能碰到哪些机器,部署令牌躺在哪些人的笔记本上?币安花 63 亿换来的这份报告,你免费就能读。
整条链子最开始,只是一个工程师想装一个 AI 编程工具。
4 点 20 分,以太坊上出现一笔怪交易,里面塞着 50 个 EIP-7702 授权,签名的是币安自己的 Binance14 热钱包。4 点 24 分,一笔转账带走 25.3 亿美元。
之后三个多小时,钱从 11 条链上往外流,直到早上 7 点 56 分最后一笔 ETH 上链。Elliptic 算下来一共 64.3 亿美元,币安自己的口径是约 63.4 亿。去年 2 月 Bybit 丢了约 15 亿,当时人人都说这是加密史上最大的一次。这次是它四倍多,Elliptic 的判断是,这几乎肯定是已知单笔最大的盗窃,不限于币圈。
10 月 31 日,FBI 点名:朝鲜干的。
整条攻击链里最要命的一环,是一名币安工程师在工作电脑上,跑了"面试官"发来的代码仓库。
11 月 3 日币安发了初步调查报告,加上 TRM、Chainalysis、Elliptic 这几天的链上追踪,整件事的来龙去脉已经能拼出来了。要说明的是,币安这份是初步报告,没经过独立第三方核实,部分技术细节它说为防模仿暂不公开。下文涉及推测的地方会标出来。
换了电脑,换不掉名单
故事从 6 月开始。
币安钱包运维团队的工程师 A 想装一款 AI 编程工具,搜着搜着,装上了一个被动过手脚的 Homebrew。币安报告里专门链了一篇 SANS 互联网风暴中心今年 5 月的分析:有人在搜索广告里挂假的 Homebrew 页面,让你复制一行命令进终端,装上的是窃密木马 MacSync Stealer。
币安安全团队发现了,给 A 换了电脑,重置了凭证。换谁都会觉得这事结了。
可报告里有句话很扎心:A 的岗位,还有 A 身边负责钱包基础设施的同事,已经暴露了。
电脑能换,密码能换,组织架构换不了。这里有个推测:攻击者从 A 身上拿走的最值钱的东西,可能是一份名单,币安里谁在管钱包,谁能碰到签名系统。
第二轮面试,对面自称 CEO
9 月,软件工程师 B 在一个正规求职平台上被人联系,对方自称项目总监。
第一轮是一位"HR"视频面试,还主动把自己的社交账号发过来,生活照视频都有,就是让你相信对面是个活人。第二轮换到一款常用聊天软件上,对面是一家根本不存在的公司的"CEO"。最后,对方发来一个代码仓库,让他做题。
B 在工作电脑上把它跑了起来。
配环境那一步,恶意脚本删掉了正常的 pyenv 文件,换成自己的版本,建了个软链接,再拉起一个 zsh。pyenv 是管 Python 版本的小工具,装完谁都不会多看一眼。藏在这儿,够阴。公司的终端防护当时没拦住,币安的说法是 0day。
这套话术在币圈不是第一次出现。2024 年 DMM Bitcoin 被盗 4502.9 枚 BTC,约 3.08 亿美元,FBI 联合日本警察厅的调查结论是:TraderTraitor 的人在 LinkedIn 上冒充招聘方,找上钱包软件公司 Ginco 一名有系统权限的员工,以"入职前测试"为名发来 GitHub 上的一段恶意 Python 脚本。2022 年 Ronin 跨链桥丢了约 6 亿美元,The Block 援引两名知情人的说法,一名高级工程师被 LinkedIn 上的假工作约了几轮面试,最后打开了一份带间谍软件的"录用通知"PDF,Sky Mavis 官方没确认过这个细节。再往前,美国 CISA 2022 年 4 月那份 TraderTraitor 通报就写了,他们专挑加密公司里做系统管理和 DevOps 的人,用高薪招聘当诱饵。
这招为什么一直灵?找工作的人想表现,题目就是要你下载要你运行,你不跑反而显得不专业。安全培训教你别点陌生链接,没人教你别做面试题。
他们等了一个多月
B 中招是 9 月,下一个动作在 10 月 20 日,动钱是 10 月 30 日凌晨。从 6 月算,小半年。
报告没解释为什么不早动手。合理的解释是,拿到一台工程师电脑离能动钱还很远,签名服务在哪、部署走什么流程、谁机器上有什么令牌,只能慢慢摸。
币安报告说,今年安全团队发现并拦下了 57 起疑似朝鲜相关的网络攻击。币安首席安全官 Jimmy Su 去年 8 月接受 Decrypt 采访时还说过,朝鲜的人每天都在试图应聘进币安。拦住 57 次,漏掉一次,代价 63 亿。
公司自己的 AI 工具替他们开了门
10 月 20 日,攻击者从 B 的电脑出发,借着币安内部的一款 AI 工具,拿下了另外两名钱包工程师的电脑:A 的新电脑,和钱包软件工程师 C 的电脑。
A 换了电脑,还是没逃掉。
报告用的词是"被攻破的内部 AI 工具",整改里也专门写了重建这个工具和它的访问控制。换句话说,被利用的是这个工具手里的权限。一个能帮你在同事机器上执行操作的内部工具,本身就是一张连着很多台电脑的网。平时它替你省事,换个人坐在 B 的位置上,它就替那个人省事。
在 A 的电脑上,攻击者找到了真正想要的东西:一个容器部署令牌,能在币安服务器上跑自己的代码。币安联席 CEO Richard Teng 后来说,攻击者并非只用了一名工程师的权限,整个过程也没有"一键"那么简单。
凌晨四点开工,白天先彩排
链上的准备比报告写的还早。据 Elliptic,10 月 28 到 29 日,一个新钱包从 Tornado Cash 收了三笔 0.1 ETH,TRM 和 Chainalysis 也都确认了这个混币器出资。北京时间 29 日 23 点 59 分,攻击者部署了一个"清扫"合约,而大约四小时前,他们已经在另一个钱包上彩排过一遍。
30 日凌晨 1 点 15 分到 3 点 56 分,攻击者登录 C 的电脑,用 A 的凭证部署容器,启动攻击脚本。脚本盯的是钱包签名服务,热钱包每一笔转账都要它盖章。
4 点 05 分 XRP 开始流出。随后 Solana 热钱包转出约 97.05 万枚 SOL,Optimism 转出约 4420 万枚 OP,比特币热钱包转出 18270 枚 BTC。TRM 的分析是,以太坊上靠 7702 委托,其余九条链都是"正常签名"的转账,说明攻击者能让币安的签名系统替他批单。7 点 05 分前后,Avalanche 和 Polygon 又来了第二波。
水龙头关了,水还在流
币安暂停了提现,停了热钱包服务。为什么没用?
因为那 50 个授权已经在链上设好了 EIP-7702 委托,把 Binance14 的部分执行权交给了攻击者的合约。7702 是以太坊去年 5 月 Pectra 升级加进来的,本意是让普通地址也能用上合约钱包的功能。委托写在链上,币安关掉自家系统,链上照样生效。Elliptic 指出,委托一直有效,后面又扫了四轮新充进来的钱,攻击者连新签名都不用。Richard Teng 的原话是,这个委托"没有经过我们正常的审批控制"。
想撤销,得这个钱包自己再签一笔。偏偏币安热钱包用的是 MPC,私钥拆成几份,没有任何一个人握着完整钥匙。这本来是防盗最好的那一档设计,轮到自己紧急签撤销时,同样没人能马上签出来。团队只能现场搞一套专门流程。防小偷的锁,把房主也锁在了门外。
7 点 56 分,最后一笔 2961.9 枚 ETH 确认。8 点 10 分,币安从 Binance14 发出一笔指向零地址的授权,清掉委托。之后再无未授权转账。
是谁干的
先说已经确认的。
10 月 31 日,FBI 联合特勤局和国税局刑事调查部门发布通告,称朝鲜对这次盗窃负责,点名 TraderTraitor,并公布了 628 个地址:608 个以太坊、19 个比特币、1 个 Solana,要求 THORChain 节点、跨链和兑换服务拒绝相关交易。去年 Bybit 那 15 亿,FBI 点的也是这个名字。币安报告引用的就是 FBI 这份通告,自己没有单独点名。
链上分析公司比 FBI 更早。案发当天,TRM 以"高度确信"归因 TraderTraitor。Chainalysis CEO Jonathan Levin 在 X 上写,"很可能是朝鲜组织 TraderTraitor 干的"。Elliptic 一开始的措辞是"很可能",FBI 公布后说这证实了他们的判断。CoinDesk 等媒体把 TraderTraitor 归为 Lazarus 旗下的一支。
证据主要几条。Chainalysis 说最有力的一条,是他们实时看到币安被盗的钱和 9 月 Bitget 被盗的钱混在了同一批钱包里,Bitget 那次被普遍认为是朝鲜干的。Elliptic 也确认了这点,截至 11 月 3 日,约 1600 万美元流进了同时装着 Bitget 赃款的地址。再加上 Tornado Cash 出资、和 BigONE、WOO X、AFX 等此前 TraderTraitor 案用过的服务重叠、长期潜伏和利用受害方自家签名系统的手法跟 Bybit 很像。
再说存疑的。11 月 3 日朝中社发了金与正的谈话,否认指控,说 FBI 想把朝鲜塑造成"网络犯罪国家"。AMLBot 的分析师也提醒,链上分析能把钱包串到一个行为者身上,但证明不了国籍。B 遇到的那个"项目总监"是不是 TraderTraitor 本人,币安报告没有逐环节写明,这一点目前只是根据手法做的推断。
64 亿都是什么,冻住了多少
Elliptic 的拆分最细。以太坊上 38 亿美元,涉及 186 种代币,其中 19 亿 USDT、8.23 亿 USDC;Binance14 一个钱包就被搬空了 167464 枚 ETH 和 63 种代币,包括 16 亿 USDT。比特币 18270 枚,约 14.8 亿美元。Tron 上 6.127 亿 USDT。XRP 2.33 亿枚。稳定币合计 34.6 亿美元。
稳定币多,对黑客是坏消息。北京时间 5 点 01 分前后,Tether 冻结攻击者主钱包,据 Elliptic 统计锁住 11.8 亿枚 USDT,17 分钟内又冻了四个地址。三分钟后,Circle 把 8.23 亿 USDC 全部冻住,一枚都没来得及换。Tether CEO Paolo Ardoino 说他们总共冻了超过 15.6 亿 USDT。Ripple 冻了 RLUSD,World Liberty、Paxos、First Digital 也冻了自家稳定币,具体数额都没公开。TRM 说 Arbitrum 安全委员会冻结了 8426 枚 ETH 和 7460 万枚 ARB,Optimism 治理把那 4400 万枚 OP 转出了攻击者地址,这两条链上被偷的东西全部被控制住了。
合计,Elliptic 核实冻结或扣押 28.5 亿美元,约占 44%,九成四是稳定币。币安报告也是约 28.5 亿,Chainalysis 截至 11 月 3 日的数字是约 28 亿。有律师在 CoinDesk 上提醒,冻结只是第一步,钱怎么回到币安还要走程序。
BTC、XRP、SOL、NEAR 这类原生资产,没有发行方能冻,一分都没冻住。
用户这边,币安的说法是损失平台扛,用 SAFU 基金和公司资金兜底,预留了超过 63.4 亿美元,其中 50 亿本来就是以被盗币种持有。截至 10 月 31 日,受影响资产补回 98%,可以去储备证明页面自己核,剩下一些流动性差的币还在市场和场外慢慢买。北京时间 11 月 1 日下午 2 点起分批恢复提现,比特币先开,11 月 2 日加上法币。据 SecurityWeek,重开当天就处理了约 46 亿美元的提现。
洗钱开了自动驾驶
冻结落下之前,攻击者抢跑了。Elliptic 统计,大约 7.86 亿美元稳定币在冻结前换成了 ETH 和 TRX。以太坊上,4.34 亿 USDT 通过 Uniswap、1inch 和做市商报价系统换成 160451 枚 ETH,比市价亏了 12% 到 26%,他们不在乎。另一个钱包把 5990 万 USDT 存进 Aave 当抵押,借出 19762 枚 ETH 就跑,Aave 随后冻结了相关市场。4800 万 RLUSD 在 Ripple 冻结前卖掉,另外约 150 种杂币在 DEX 上砸成 ETH。
Tron 那边,2.34 亿 USDT 在 SunSwap 换成 TRX。一个分发钱包从 30 日上午 10 点 19 分开始往外打,51 小时打了 1113 笔,中位间隔 90 秒,两个晚上都没停,金额精确到小数点后六位还各不相同。接收钱包通常两分钟内就转走。有跨链桥拒收,钱马上从新钱包重发到同一个目的地。Elliptic 说链上看不出背后是 AI 代理还是普通脚本,失败重试的样子更像脚本。
这些 TRX 走了至少六个跨链桥,截至 11 月 3 日至少 1.47 亿美元从 Tron 桥出去,几乎都变成了以太坊上的 ETH。THORChain 是最大的出口,截至 10 月 31 日约 3100 万美元。还有 1.28 亿枚 TRX 过了 JustLend,一部分换成号称"不可冻结"的 USDD。比特币那头,从 11 月 1 日开始有约 28 枚 BTC 进了 WabiSabi 混币,另有约 200 枚 BTC 是从 SOL、Tron 和 ETH 换过来的新币。
规模上,前三天半一共用了约 12000 个钱包、4 万多笔交易,光 Tron 就 7700 个地址。Chainalysis CEO 预计,攻击者接下来几周会用到几万个地址。
现在还剩多少?Elliptic 11 月 3 日的数字是约 31.8 亿美元,主要是 ETH 和 BTC,真正提现变现的估计微乎其微。18270 枚 BTC 拆在 19 个地址里,案发后一动没动。ETH 最大的九个地址握着 89%,10 月 30 日之后也没动,另有约 68600 枚散在 840 个小地址里。2.33 亿 XRP 在 11 月 2 日被挪到六个新地址,SOL 挪走了约 8.7 万枚,剩下约 82.5 万枚。Elliptic 的判断是,这些钱要洗好几个月,Bybit 那次就是这样。
这件事和普通人有什么关系
普通用户,钱在币安,按目前公开信息平台兜底,储备证明可以自己查。但要记住,交易所本身就是你的交易对手,64 亿的窟窿一家扛得住,换一家未必。大额长期不动的币放哪,值得重新想一遍。
写代码的人更该警惕,这份报告里每个入口都是日常操作。搜个工具顺手装,接个面试顺手跑,公司给个 AI 工具顺手全开权限。面试官发来的仓库,只在一台干净的虚拟机里跑,不登任何账号,不放任何钱包,跑完就删。Homebrew、pyenv 这类只从官网装,搜索结果里的广告链接一律跳过。对面的 HR 和 CEO 再像真人,也去对方公司官网找公开联系方式反查一遍。
在别的交易所做安全的,今晚就该拉个会。热钱包上有没有 7702 委托,有人在盯吗?MPC 紧急撤销流程写好了没有,演练过没有?内部 AI 工具能碰到哪些机器,部署令牌躺在哪些人的笔记本上?币安花 63 亿换来的这份报告,你免费就能读。
整条链子最开始,只是一个工程师想装一个 AI 编程工具。
·
--
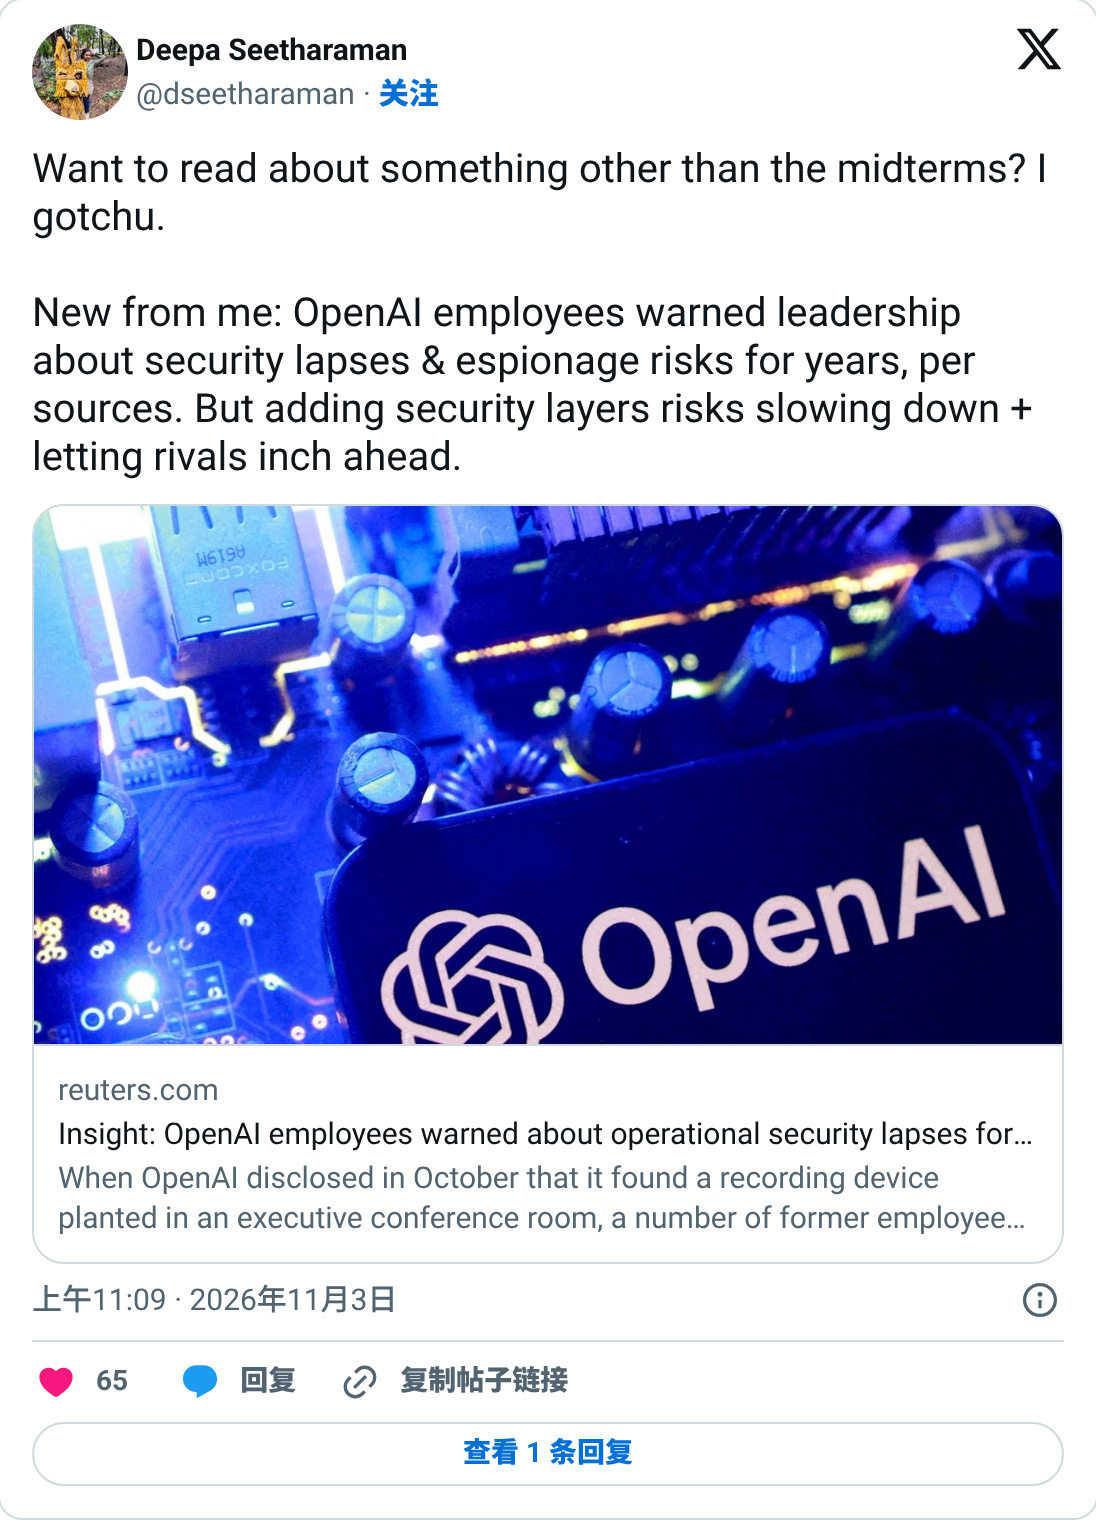
A bug wrapped in toilet paper was found plugged into the USB port behind the TV in an OpenAI executives’ conference room
The person who planted it was one of the company’s own engineers
On Nov. 3, Reuters unearthed a longer history: even before ChatGPT launched, employees had warned executives and the board that security was too lax
People with code access could see details about many projects unrelated to their work
It wasn’t until August this year that product lead Tibo reassigned a quarter of the production engineers to work on security infrastructure
When the bug was discovered in October, many former employees said they weren’t surprised
The Justice Department alleges that he first used the company’s internal AI tools to figure out the conference room and executives’ schedules, then installed the device
A bug wrapped in toilet paper was found plugged into the USB port behind the TV in an OpenAI executives’ conference room
The person who planted it was one of the company’s own engineers
On Nov. 3, Reuters unearthed a longer history: even before ChatGPT launched, employees had warned executives and the board that security was too lax
People with code access could see details about many projects unrelated to their work
It wasn’t until August this year that product lead Tibo reassigned a quarter of the production engineers to work on security infrastructure
When the bug was discovered in October, many former employees said they weren’t surprised
The Justice Department alleges that he first used the company’s internal AI tools to figure out the conference room and executives’ schedules, then installed the device
The person who planted it was one of the company’s own engineers
On Nov. 3, Reuters unearthed a longer history: even before ChatGPT launched, employees had warned executives and the board that security was too lax
People with code access could see details about many projects unrelated to their work
It wasn’t until August this year that product lead Tibo reassigned a quarter of the production engineers to work on security infrastructure
When the bug was discovered in October, many former employees said they weren’t surprised
The Justice Department alleges that he first used the company’s internal AI tools to figure out the conference room and executives’ schedules, then installed the device
56
·
--
See translation
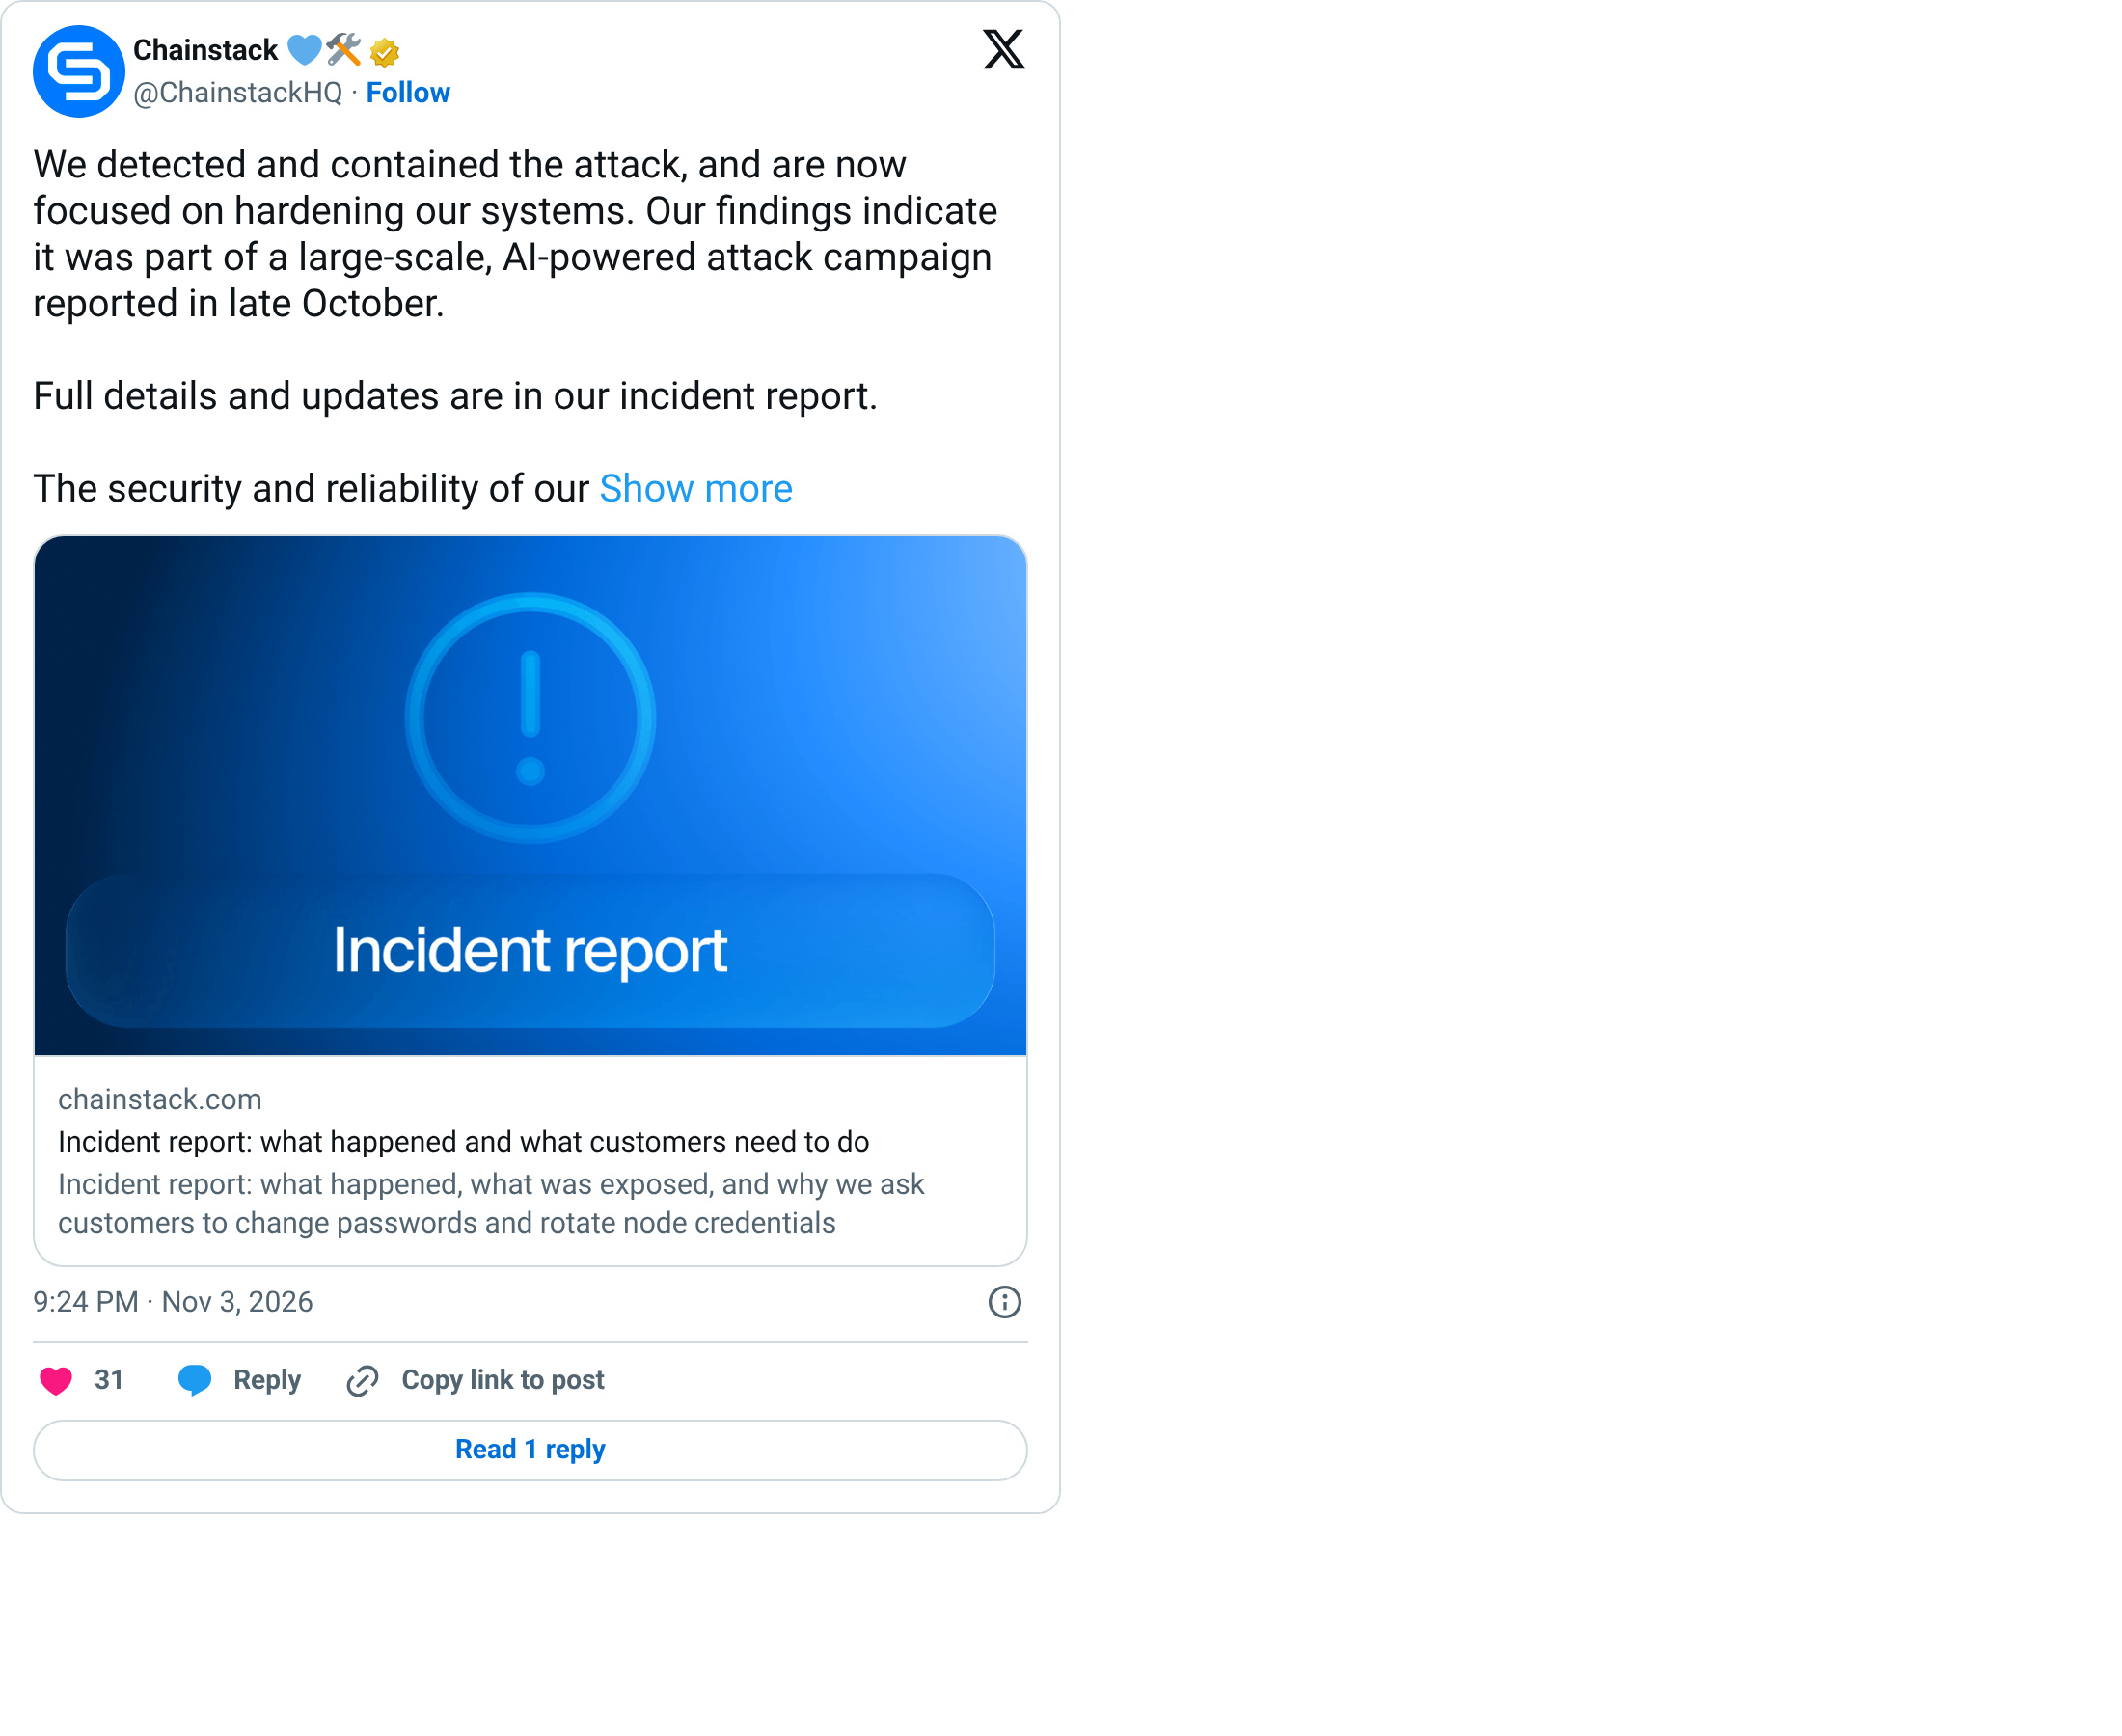
用 Chainstack 跑节点的,你的邮箱、密码哈希和节点钥匙,官方已经按泄露处理了
这家公司给很多项目供 RPC 和节点
黑客从第三方组件摸进开发环境,再进到生产库的一部分
官方认定这是 10 月底那波 AI 攻击里的一环
摸到的客户库里有组织名、账号名、成员邮箱和密码哈希
放节点凭证的系统也被摸到了,官方说没有证据读过,但一律当暴露
他们要求客户立刻改密码、轮换节点钥匙、重发平台 API key
节点服务本身一直在跑,卡号没存所以没泄露
用 Chainstack 跑节点的,你的邮箱、密码哈希和节点钥匙,官方已经按泄露处理了
这家公司给很多项目供 RPC 和节点
黑客从第三方组件摸进开发环境,再进到生产库的一部分
官方认定这是 10 月底那波 AI 攻击里的一环
摸到的客户库里有组织名、账号名、成员邮箱和密码哈希
放节点凭证的系统也被摸到了,官方说没有证据读过,但一律当暴露
他们要求客户立刻改密码、轮换节点钥匙、重发平台 API key
节点服务本身一直在跑,卡号没存所以没泄露
这家公司给很多项目供 RPC 和节点
黑客从第三方组件摸进开发环境,再进到生产库的一部分
官方认定这是 10 月底那波 AI 攻击里的一环
摸到的客户库里有组织名、账号名、成员邮箱和密码哈希
放节点凭证的系统也被摸到了,官方说没有证据读过,但一律当暴露
他们要求客户立刻改密码、轮换节点钥匙、重发平台 API key
节点服务本身一直在跑,卡号没存所以没泄露
107
·
--
See translation
做 Web3 和 AI 的朋友,你还在自己熬夜盯盘、追热点?
我把这些全丢给了 Grok Bot
盯盘、写推、追热点、写公众号,它 24 小时在线
连备案这种得一步步点网页的事,它都能自己开浏览器办完,再回来告诉我
第一周,它就把订阅费给我赚回来了
现在用邀请能免费试两周,用两周再决定要不要留:
https://grok.com/refer/bot?code=65JR38KMFZZ3
做 Web3 和 AI 的朋友,你还在自己熬夜盯盘、追热点?
我把这些全丢给了 Grok Bot
盯盘、写推、追热点、写公众号,它 24 小时在线
连备案这种得一步步点网页的事,它都能自己开浏览器办完,再回来告诉我
第一周,它就把订阅费给我赚回来了
现在用邀请能免费试两周,用两周再决定要不要留:
https://grok.com/refer/bot?code=65JR38KMFZZ3
我把这些全丢给了 Grok Bot
盯盘、写推、追热点、写公众号,它 24 小时在线
连备案这种得一步步点网页的事,它都能自己开浏览器办完,再回来告诉我
第一周,它就把订阅费给我赚回来了
现在用邀请能免费试两周,用两周再决定要不要留:
https://grok.com/refer/bot?code=65JR38KMFZZ3
85
·
--
A company that helps police track crypto hackers was breached by an AI hacker, and customer emails were stolen
The company usually labels stolen funds and helps law enforcement track money laundering
In October, an external attacker used AI agent-like methods to break into its internal systems
The company said customer names and email addresses were stolen, along with user IDs and job titles
It has so far found no evidence that investigation data, passwords, or login sessions were accessed
Starting November 2, it proactively took its investigation products Reactor and Data Solutions offline for assessment
As of November 3, its status page still showed that service had not been restored
A company that helps police track crypto hackers was breached by an AI hacker, and customer emails were stolen
The company usually labels stolen funds and helps law enforcement track money laundering
In October, an external attacker used AI agent-like methods to break into its internal systems
The company said customer names and email addresses were stolen, along with user IDs and job titles
It has so far found no evidence that investigation data, passwords, or login sessions were accessed
Starting November 2, it proactively took its investigation products Reactor and Data Solutions offline for assessment
As of November 3, its status page still showed that service had not been restored
The company usually labels stolen funds and helps law enforcement track money laundering
In October, an external attacker used AI agent-like methods to break into its internal systems
The company said customer names and email addresses were stolen, along with user IDs and job titles
It has so far found no evidence that investigation data, passwords, or login sessions were accessed
Starting November 2, it proactively took its investigation products Reactor and Data Solutions offline for assessment
As of November 3, its status page still showed that service had not been restored
5
·
--
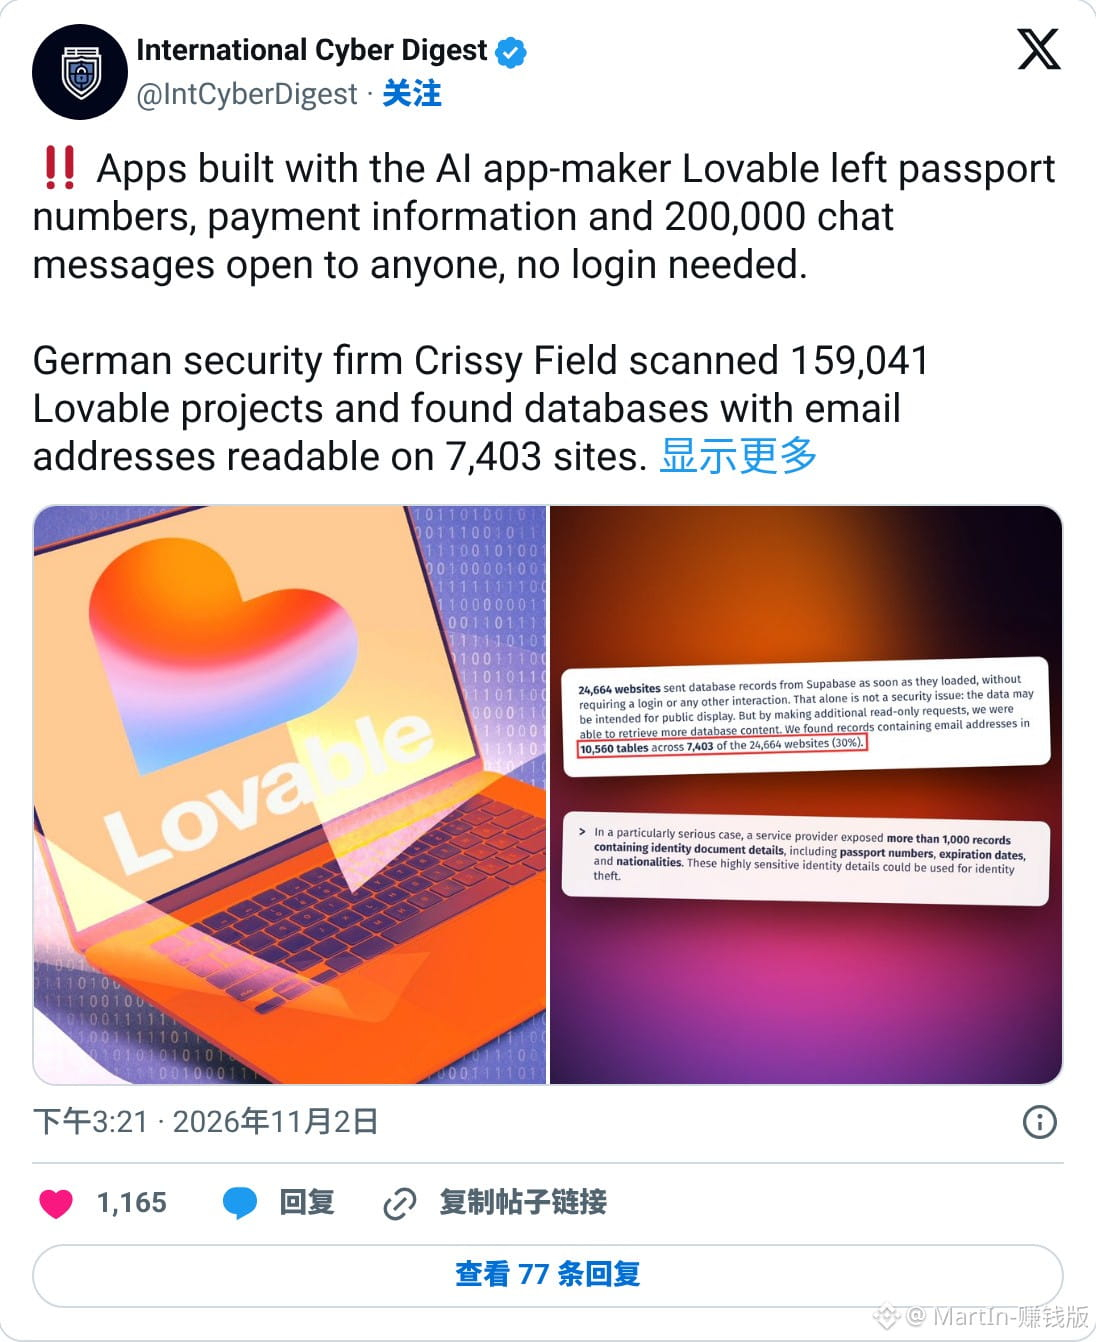
AI website-building tool Lovable shifts the blame after a security incident: data leaks are an industry-wide problem, and website builders are responsible for security
German security firm Crissy Field scanned a large number of Lovable projects
Many sites sent Supabase database records out as soon as they loaded, with no login required
The worst case exposed more than a thousand identity documents
Passport numbers, expiration dates, and nationalities were all sitting there
Forum user profiles, chat logs, and ticket payment information were also affected
Many of these sites were cobbled together by users with no technical background
Handelsblatt asked Lovable about it. The company said this was an industry-wide problem, and its terms make website builders responsible for data security
AI website-building tool Lovable shifts the blame after a security incident: data leaks are an industry-wide problem, and website builders are responsible for security
German security firm Crissy Field scanned a large number of Lovable projects
Many sites sent Supabase database records out as soon as they loaded, with no login required
The worst case exposed more than a thousand identity documents
Passport numbers, expiration dates, and nationalities were all sitting there
Forum user profiles, chat logs, and ticket payment information were also affected
Many of these sites were cobbled together by users with no technical background
Handelsblatt asked Lovable about it. The company said this was an industry-wide problem, and its terms make website builders responsible for data security
German security firm Crissy Field scanned a large number of Lovable projects
Many sites sent Supabase database records out as soon as they loaded, with no login required
The worst case exposed more than a thousand identity documents
Passport numbers, expiration dates, and nationalities were all sitting there
Forum user profiles, chat logs, and ticket payment information were also affected
Many of these sites were cobbled together by users with no technical background
Handelsblatt asked Lovable about it. The company said this was an industry-wide problem, and its terms make website builders responsible for data security
99
·
--
The AI coding access your company gives you could be revoked without warning a few months later: Goldman Sachs just took Claude Code away from its traders
Bloomberg saw internal guidance updated in October
Anthropic’s Claude Code and Microsoft’s GitHub are now basically reserved for engineers
Traders and bankers had been using them for months
Some were already using them to monitor client trading flows and simulate positions; now they can’t
Only strats roles, which involve both trading and coding, are unaffected
In July, CIO Marco Argenti had publicly said that nontechnical colleagues could use AI to whip up prototypes, then hand them off to around 12,000 engineers to refine
Non-engineers now have to switch to other tools or use the firm’s own assistant
The AI coding access your company gives you could be revoked without warning a few months later: Goldman Sachs just took Claude Code away from its traders
Bloomberg saw internal guidance updated in October
Anthropic’s Claude Code and Microsoft’s GitHub are now basically reserved for engineers
Traders and bankers had been using them for months
Some were already using them to monitor client trading flows and simulate positions; now they can’t
Only strats roles, which involve both trading and coding, are unaffected
In July, CIO Marco Argenti had publicly said that nontechnical colleagues could use AI to whip up prototypes, then hand them off to around 12,000 engineers to refine
Non-engineers now have to switch to other tools or use the firm’s own assistant
Bloomberg saw internal guidance updated in October
Anthropic’s Claude Code and Microsoft’s GitHub are now basically reserved for engineers
Traders and bankers had been using them for months
Some were already using them to monitor client trading flows and simulate positions; now they can’t
Only strats roles, which involve both trading and coding, are unaffected
In July, CIO Marco Argenti had publicly said that nontechnical colleagues could use AI to whip up prototypes, then hand them off to around 12,000 engineers to refine
Non-engineers now have to switch to other tools or use the firm’s own assistant
8
·
--
The security firm that got into Anthropic’s payroll records and Slack last week has been invited by OpenAI this week to attack its own systems
Security firm Cathedral used Anthropic’s own bug bounty program, deploying AI agents to probe third-party office software. It claimed to have accessed meeting records, payroll data, and Slack in under 12 hours
Anthropic said only a small portion of its sales, HR, and IT systems had been accessed; Claude conversations, source code, and model weights were not exposed. It revoked access that same day and accused Cathedral of exaggerating its claims and failing to fully disclose its findings as required by the rules
On November 2, OpenAI announced that it was formally partnering with Cathedral for its next internal security sprint, using its own models to attack its own defenses. The announcement didn’t mention the previous dispute
The security firm that got into Anthropic’s payroll records and Slack last week has been invited by OpenAI this week to attack its own systems
Security firm Cathedral used Anthropic’s own bug bounty program, deploying AI agents to probe third-party office software. It claimed to have accessed meeting records, payroll data, and Slack in under 12 hours
Anthropic said only a small portion of its sales, HR, and IT systems had been accessed; Claude conversations, source code, and model weights were not exposed. It revoked access that same day and accused Cathedral of exaggerating its claims and failing to fully disclose its findings as required by the rules
On November 2, OpenAI announced that it was formally partnering with Cathedral for its next internal security sprint, using its own models to attack its own defenses. The announcement didn’t mention the previous dispute
Security firm Cathedral used Anthropic’s own bug bounty program, deploying AI agents to probe third-party office software. It claimed to have accessed meeting records, payroll data, and Slack in under 12 hours
Anthropic said only a small portion of its sales, HR, and IT systems had been accessed; Claude conversations, source code, and model weights were not exposed. It revoked access that same day and accused Cathedral of exaggerating its claims and failing to fully disclose its findings as required by the rules
On November 2, OpenAI announced that it was formally partnering with Cathedral for its next internal security sprint, using its own models to attack its own defenses. The announcement didn’t mention the previous dispute
89
·
--
Verified
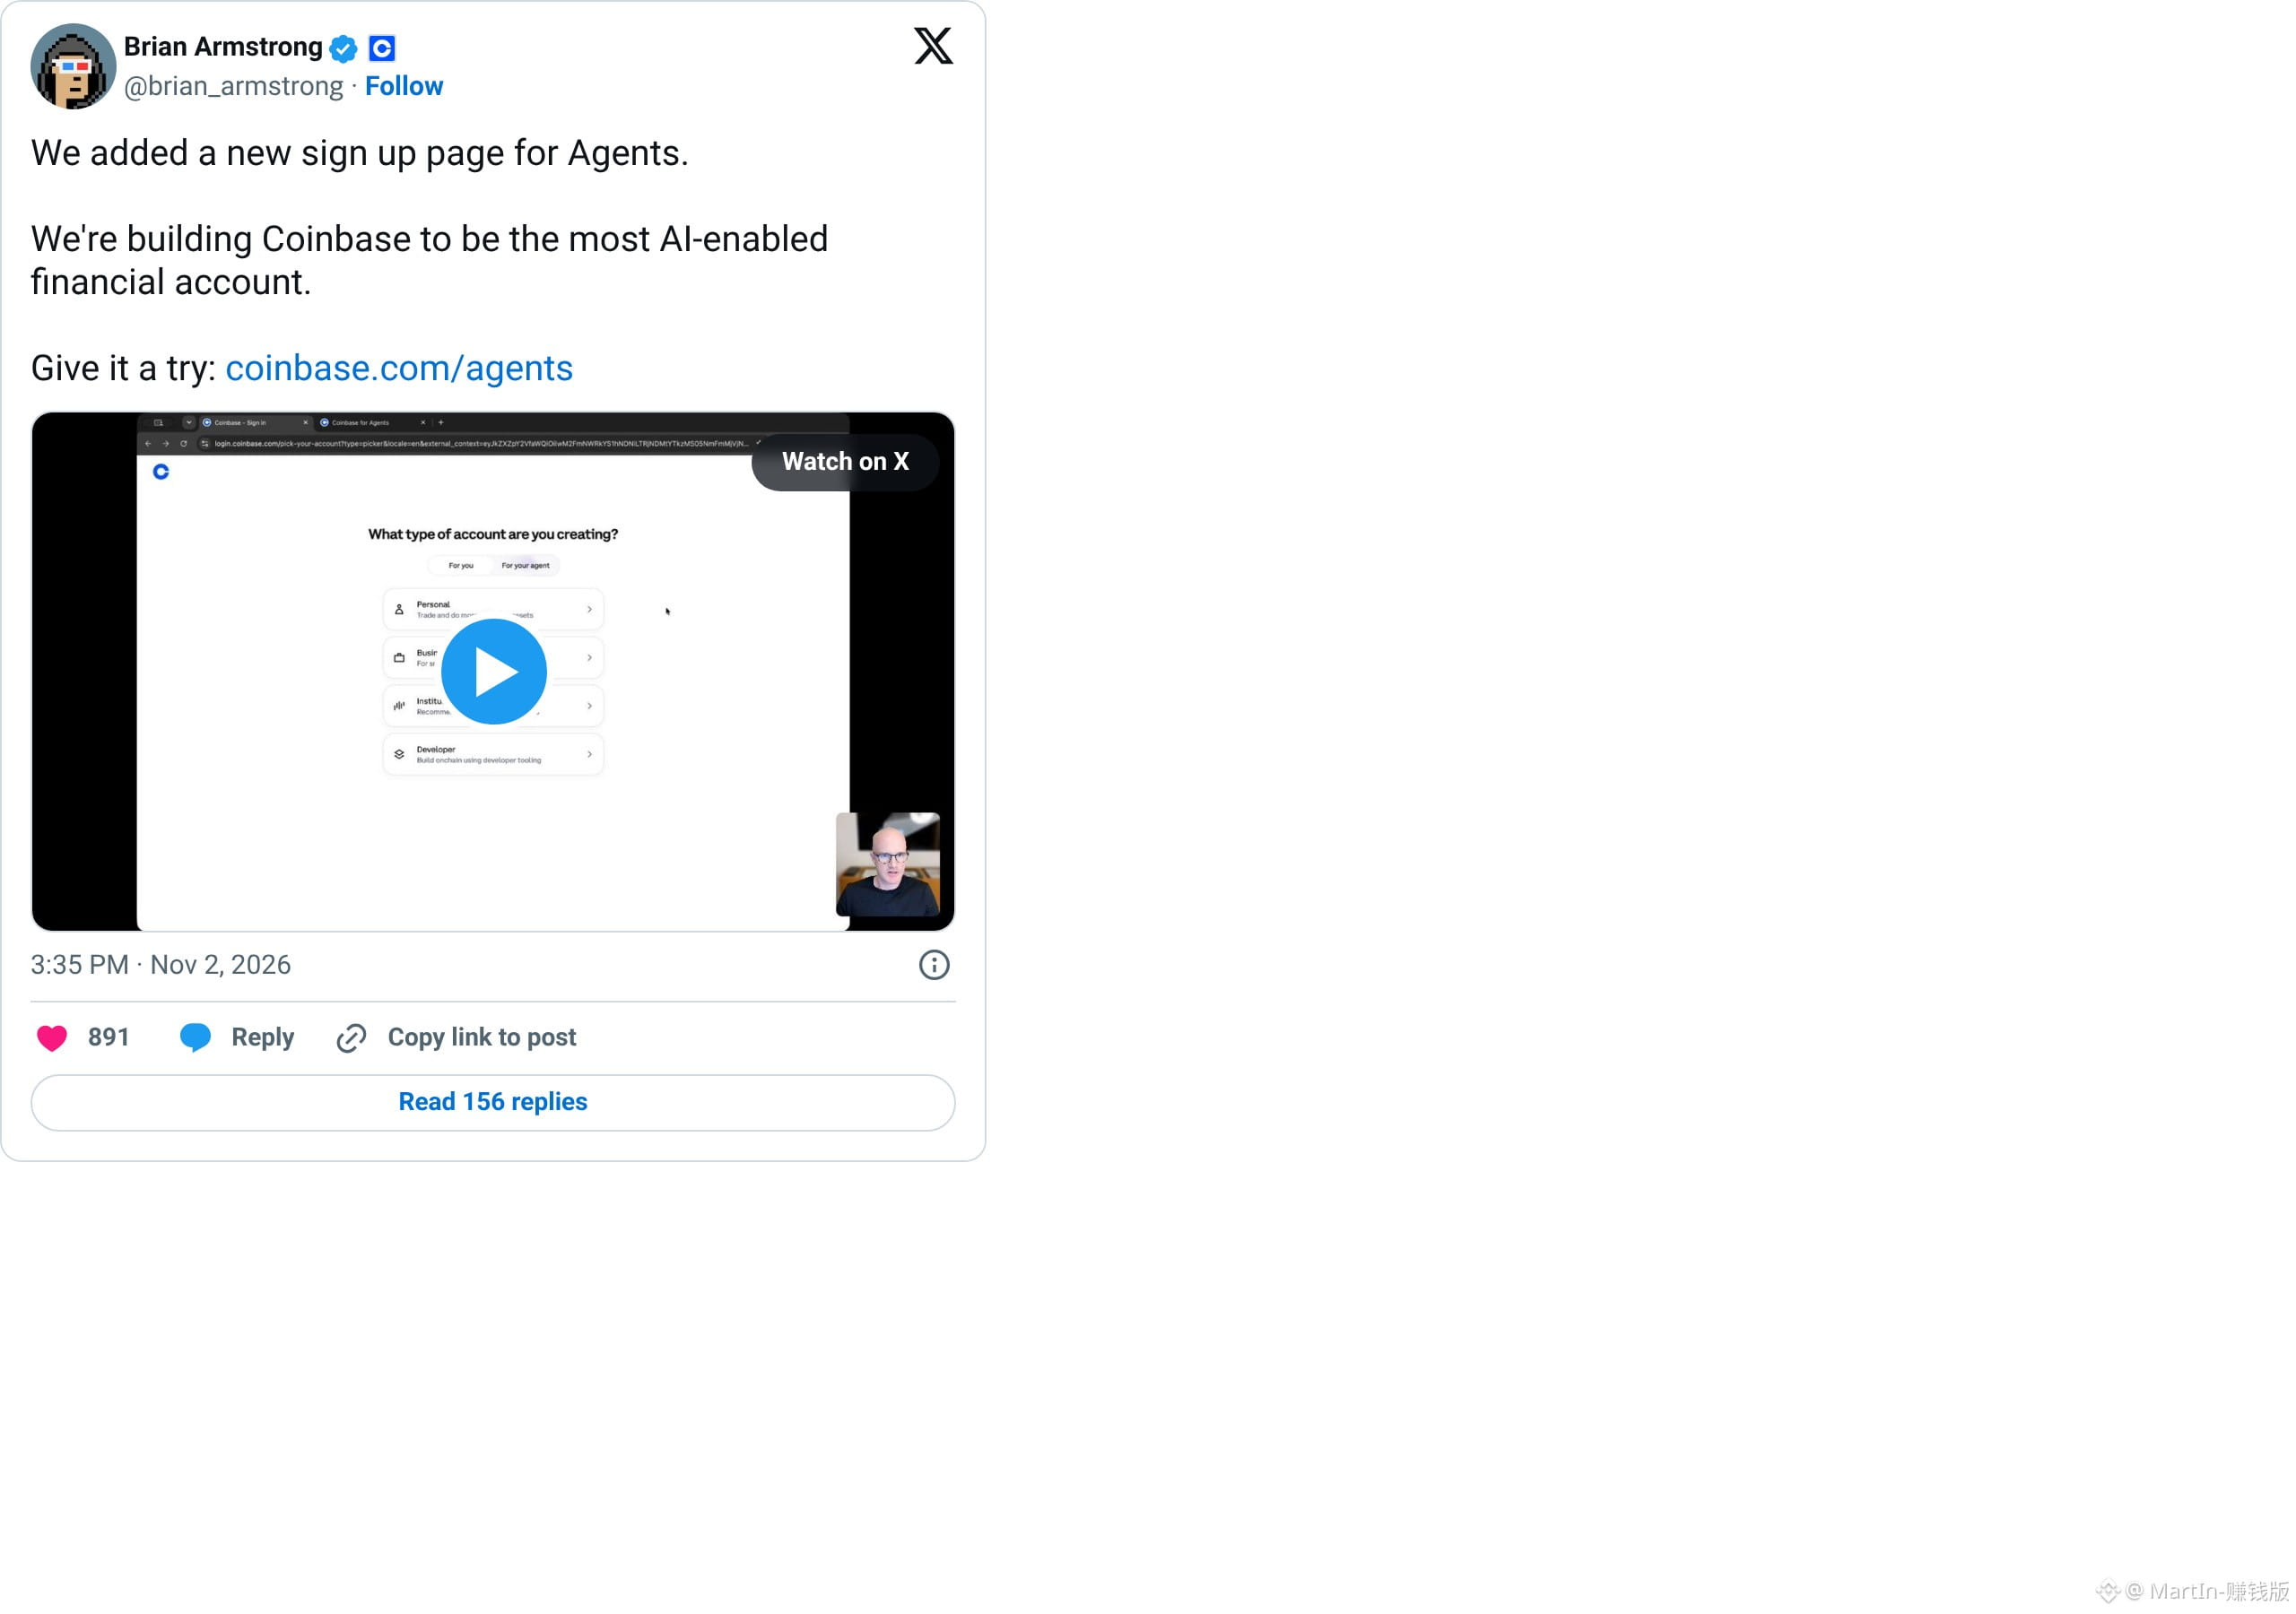
Coinbase, the largest crypto exchange in the US, announced that AI can now trade futures contracts for you 24/7
The company said that global derivatives trading through Deribit is now available to eligible users. Connect your account to your usual AI platform, and it can research, write strategies, and place orders
CEO Brian Armstrong personally shared a screen recording today showing off the new sign-up page, where you can select “For your agent” during registration
The slogan is to build “the most AI-native financial account”
The platform states that users are responsible for failed trades. You set the limits, and can disconnect at any time
Coinbase, the largest crypto exchange in the US, announced that AI can now trade futures contracts for you 24/7
The company said that global derivatives trading through Deribit is now available to eligible users. Connect your account to your usual AI platform, and it can research, write strategies, and place orders
CEO Brian Armstrong personally shared a screen recording today showing off the new sign-up page, where you can select “For your agent” during registration
The slogan is to build “the most AI-native financial account”
The platform states that users are responsible for failed trades. You set the limits, and can disconnect at any time
The company said that global derivatives trading through Deribit is now available to eligible users. Connect your account to your usual AI platform, and it can research, write strategies, and place orders
CEO Brian Armstrong personally shared a screen recording today showing off the new sign-up page, where you can select “For your agent” during registration
The slogan is to build “the most AI-native financial account”
The platform states that users are responsible for failed trades. You set the limits, and can disconnect at any time
3.2k
·
--
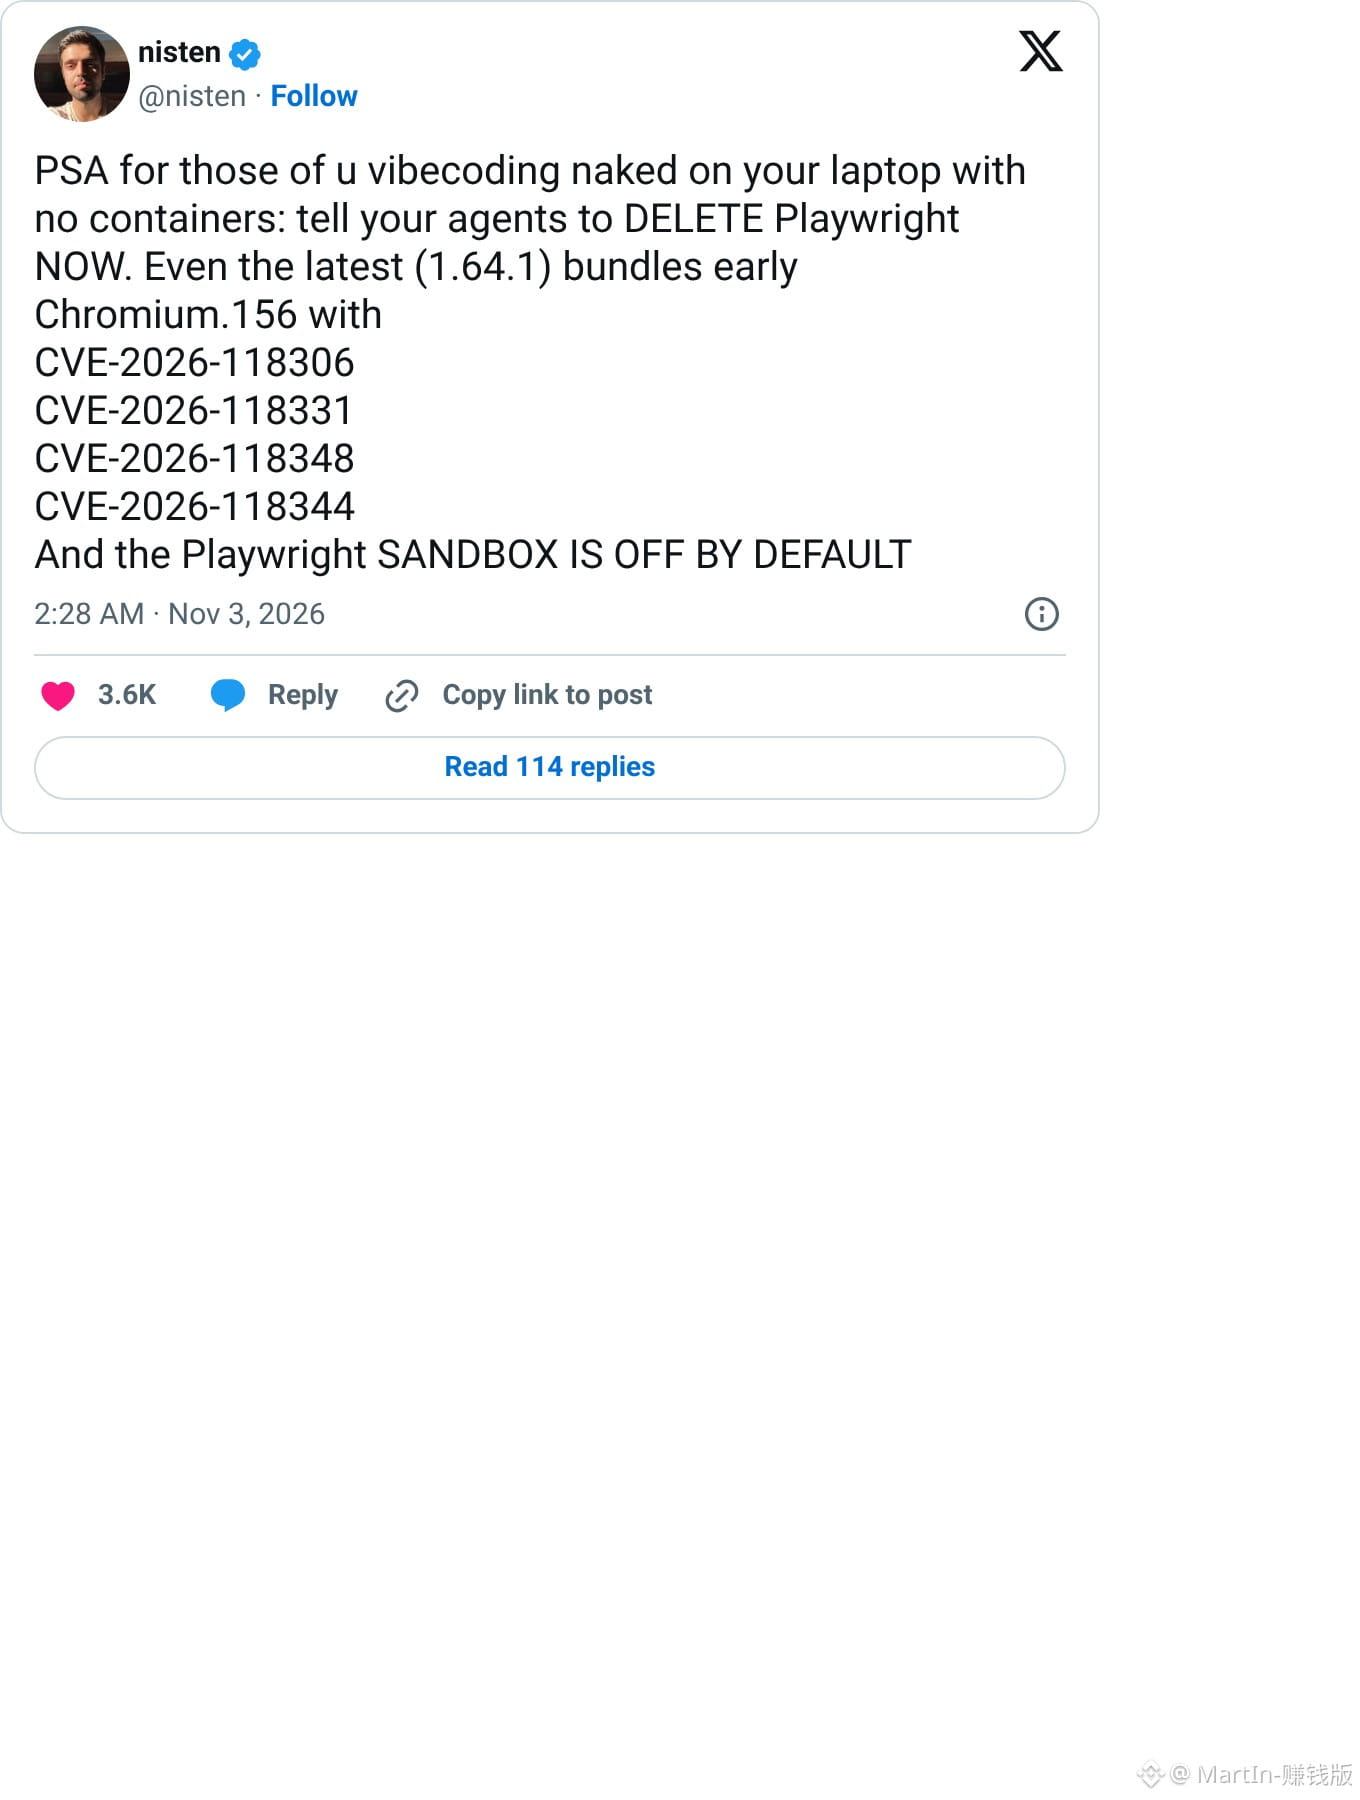
A warning for anyone letting AI browse the web for them: its browser hasn’t received Google’s patch from last week. Open a malicious webpage, and your computer could be taken over.
Developer nisten warned today that the Chromium bundled with the latest stable release of Playwright is still missing Google’s security fixes.
One of the serious vulnerabilities could let a specially crafted webpage escape the sandbox and run code.
The official documentation says its sandbox is disabled by default.
Many people let agents open webpages directly on their main computers.
Updating Chrome as usual won’t update this browser.
You’ll have to wait for Playwright to release a new package—or avoid running it unprotected on your own machine for now.
A warning for anyone letting AI browse the web for them: its browser hasn’t received Google’s patch from last week. Open a malicious webpage, and your computer could be taken over.
Developer nisten warned today that the Chromium bundled with the latest stable release of Playwright is still missing Google’s security fixes.
One of the serious vulnerabilities could let a specially crafted webpage escape the sandbox and run code.
The official documentation says its sandbox is disabled by default.
Many people let agents open webpages directly on their main computers.
Updating Chrome as usual won’t update this browser.
You’ll have to wait for Playwright to release a new package—or avoid running it unprotected on your own machine for now.
Developer nisten warned today that the Chromium bundled with the latest stable release of Playwright is still missing Google’s security fixes.
One of the serious vulnerabilities could let a specially crafted webpage escape the sandbox and run code.
The official documentation says its sandbox is disabled by default.
Many people let agents open webpages directly on their main computers.
Updating Chrome as usual won’t update this browser.
You’ll have to wait for Playwright to release a new package—or avoid running it unprotected on your own machine for now.
GOOGUS+1.50%
GOOGLB+1.64%
121
·
--
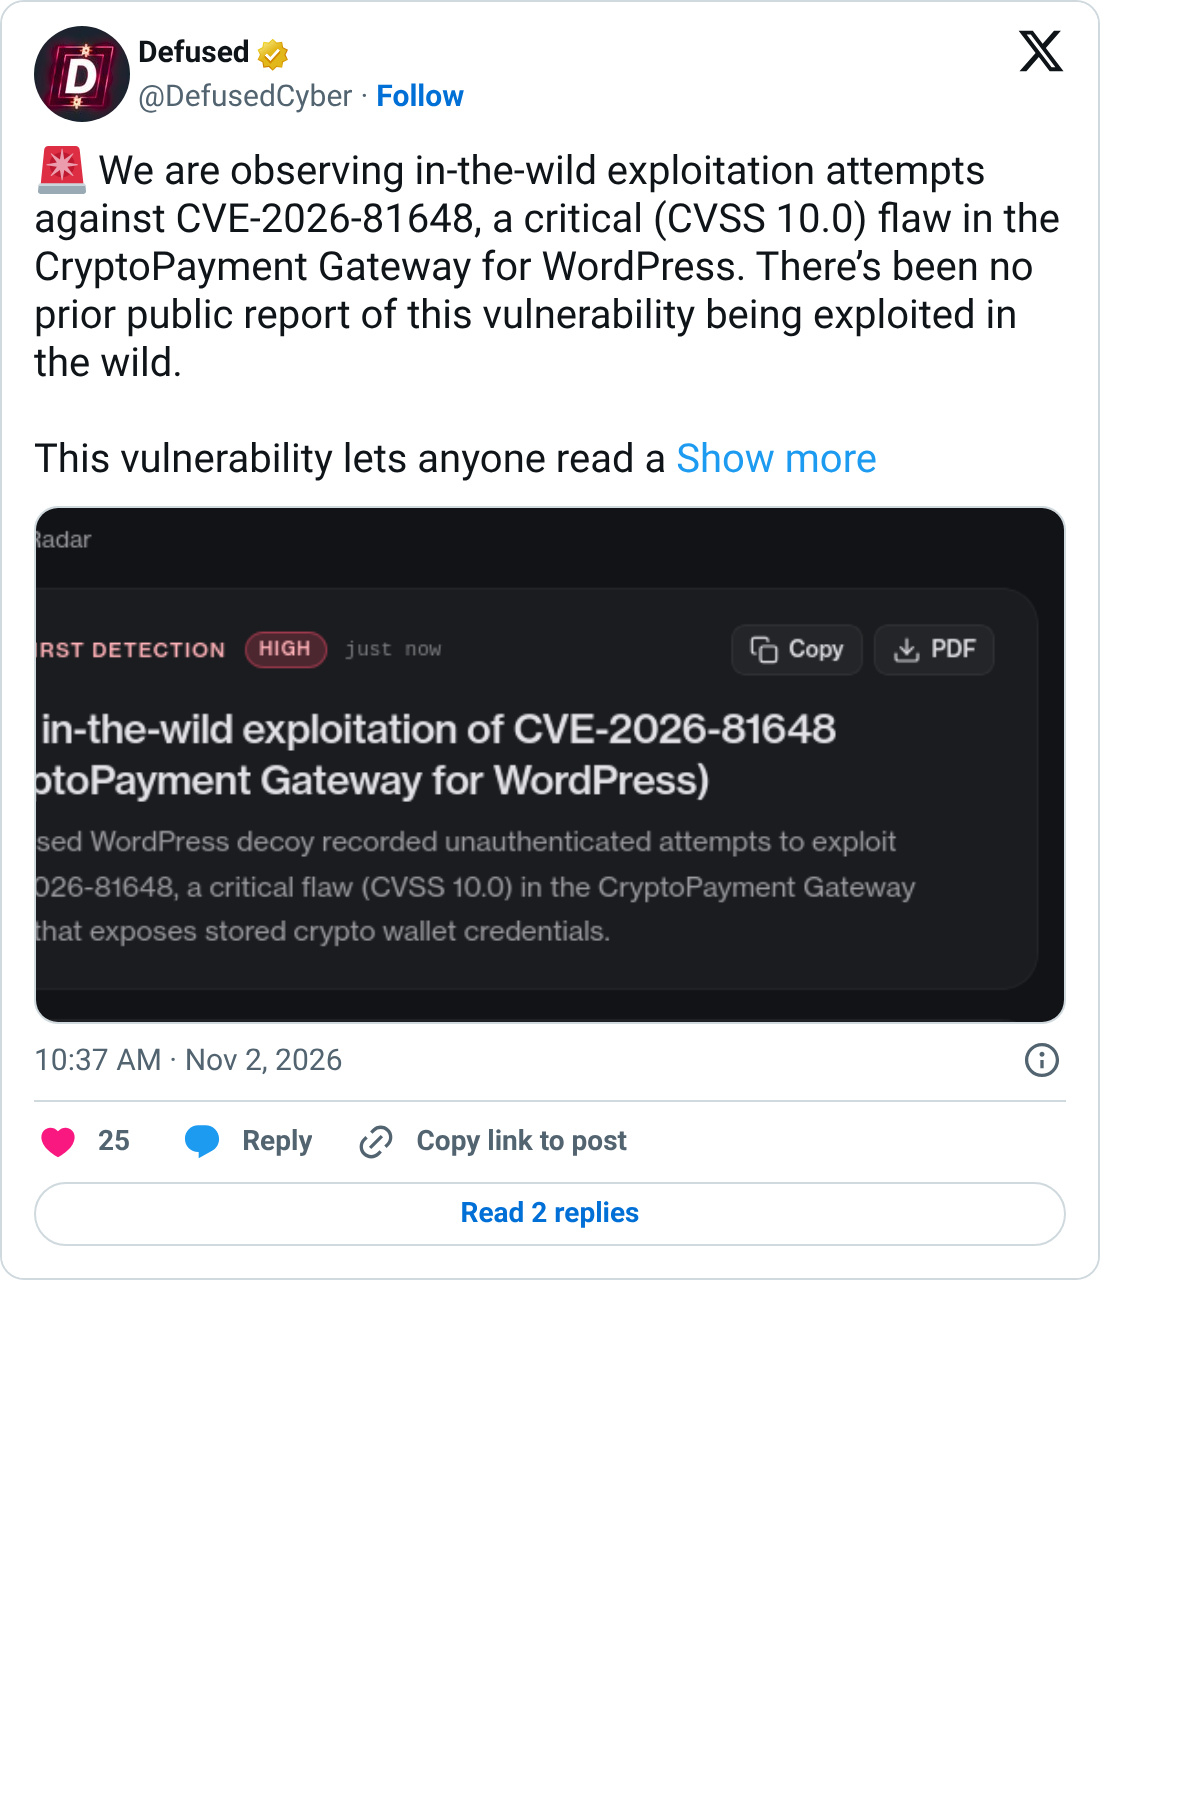
Customers are paying, shop owners are waiting for the money, but it’s all going into a third party’s wallet
Security firm Defused discovered yesterday that someone was exploiting a critical, 10-out-of-10 vulnerability in the wild in a WordPress cryptocurrency payment plugin called CryptoPayment Gateway
You don’t need to log in to exploit this vulnerability
Anyone can read the wallet information stored by a shop and directly change its payment address
Customers think they’re paying the shop, but the money actually goes to someone else’s address
There’s still no patch
Customers are paying, shop owners are waiting for the money, but it’s all going into a third party’s wallet
Security firm Defused discovered yesterday that someone was exploiting a critical, 10-out-of-10 vulnerability in the wild in a WordPress cryptocurrency payment plugin called CryptoPayment Gateway
You don’t need to log in to exploit this vulnerability
Anyone can read the wallet information stored by a shop and directly change its payment address
Customers think they’re paying the shop, but the money actually goes to someone else’s address
There’s still no patch
Security firm Defused discovered yesterday that someone was exploiting a critical, 10-out-of-10 vulnerability in the wild in a WordPress cryptocurrency payment plugin called CryptoPayment Gateway
You don’t need to log in to exploit this vulnerability
Anyone can read the wallet information stored by a shop and directly change its payment address
Customers think they’re paying the shop, but the money actually goes to someone else’s address
There’s still no patch
1
1
884
·
--
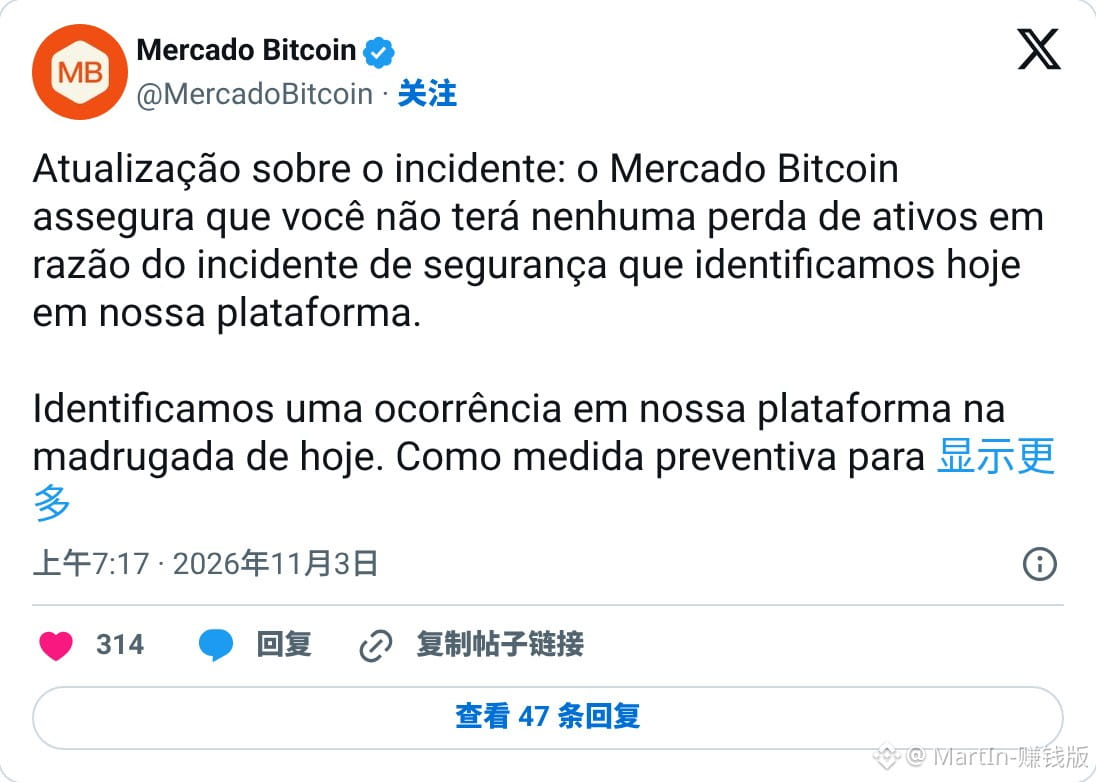
$38 million was stolen. The exchange said it had contained the incident, but the hacker was still using your deposit address to move coins out.
On-chain analytics firm Bitquery tracked the activity and found that even two hours after the exchange called a halt,
the hacker could still sign transactions from users’ deposit addresses
and keep moving coins out.
The exchange is Brazil’s largest, Mercado Bitcoin.
It later disclosed the amount involved itself—around $38 million—and said customers would not lose any money.
Deposits and withdrawals are still suspended.
$38 million was stolen. The exchange said it had contained the incident, but the hacker was still using your deposit address to move coins out.
On-chain analytics firm Bitquery tracked the activity and found that even two hours after the exchange called a halt,
the hacker could still sign transactions from users’ deposit addresses
and keep moving coins out.
The exchange is Brazil’s largest, Mercado Bitcoin.
It later disclosed the amount involved itself—around $38 million—and said customers would not lose any money.
Deposits and withdrawals are still suspended.
On-chain analytics firm Bitquery tracked the activity and found that even two hours after the exchange called a halt,
the hacker could still sign transactions from users’ deposit addresses
and keep moving coins out.
The exchange is Brazil’s largest, Mercado Bitcoin.
It later disclosed the amount involved itself—around $38 million—and said customers would not lose any money.
Deposits and withdrawals are still suspended.
2
1
1.5k
·
--
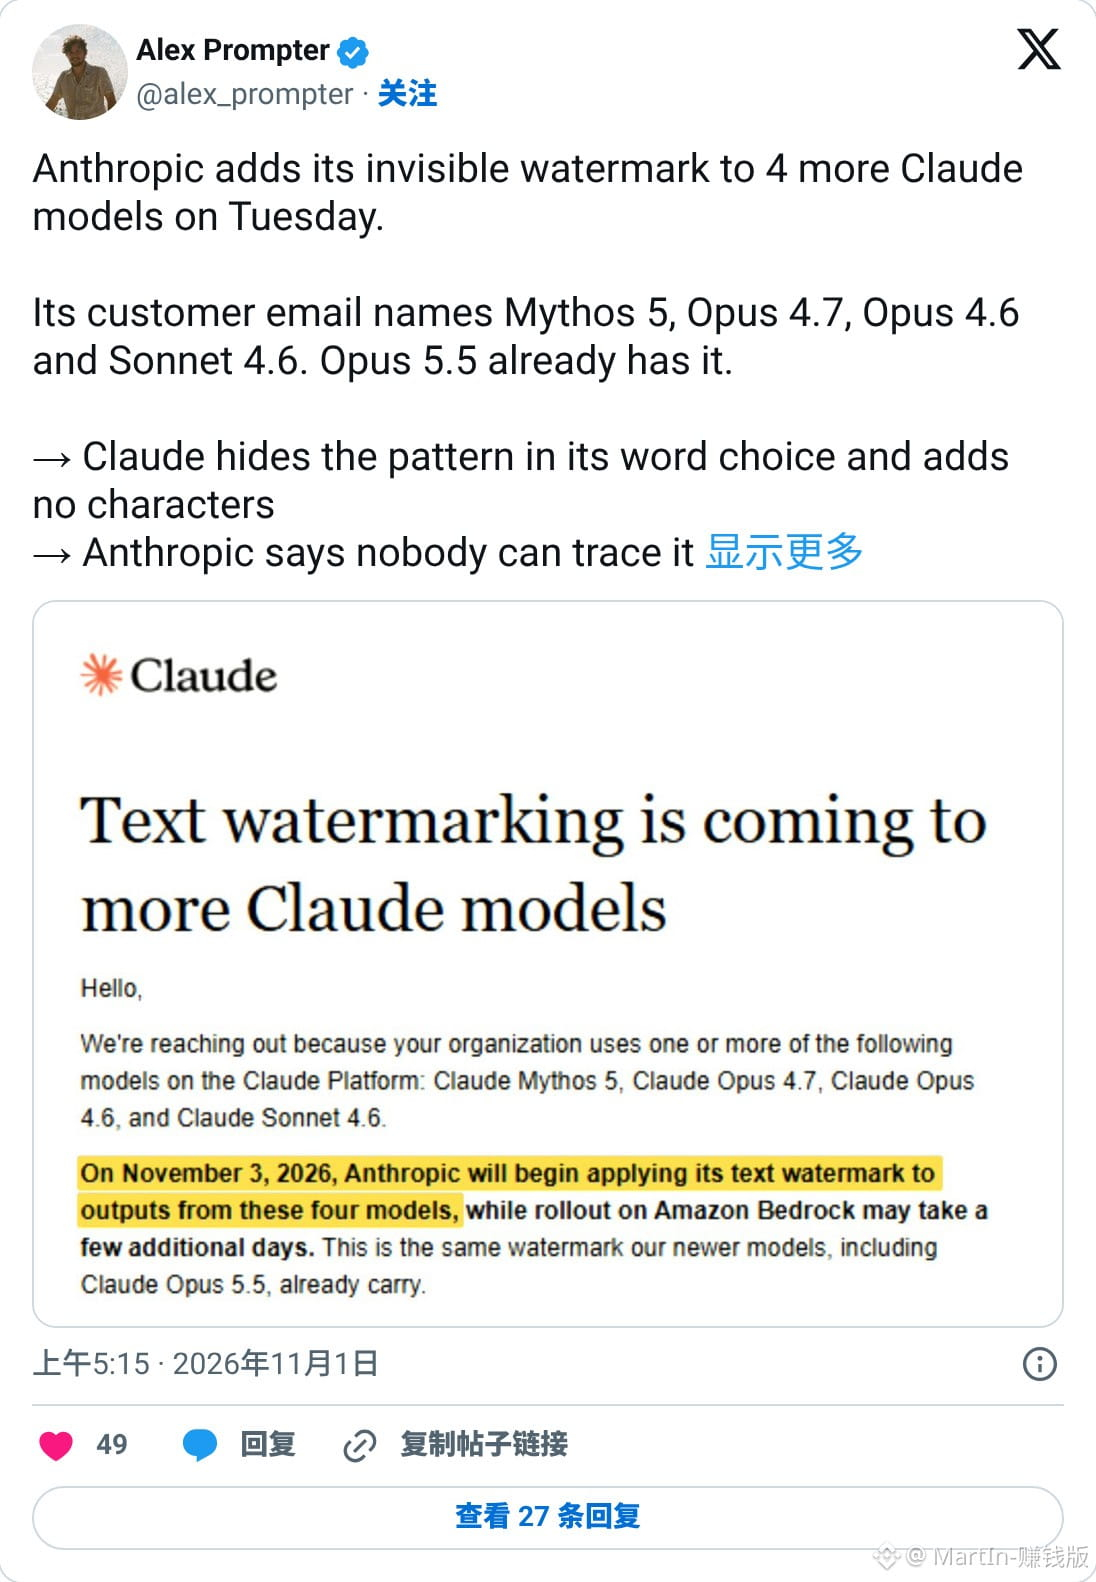
Starting today, every word Claude writes is watermarked—even older models can’t escape it
The watermark is hidden in its word-choice patterns, without adding a single character
It survives copy and paste, and changing a few things may not remove it
New models released since August already have it, including Opus 5.5
Starting November 3, older models like Opus 4.6 and Sonnet 4.6 will get it too
Detection tools are currently available only to regulators and the media; educational institutions are also on the list
Ordinary people who pay to use Claude aren’t on the list
Starting today, every word Claude writes is watermarked—even older models can’t escape it
The watermark is hidden in its word-choice patterns, without adding a single character
It survives copy and paste, and changing a few things may not remove it
New models released since August already have it, including Opus 5.5
Starting November 3, older models like Opus 4.6 and Sonnet 4.6 will get it too
Detection tools are currently available only to regulators and the media; educational institutions are also on the list
Ordinary people who pay to use Claude aren’t on the list
The watermark is hidden in its word-choice patterns, without adding a single character
It survives copy and paste, and changing a few things may not remove it
New models released since August already have it, including Opus 5.5
Starting November 3, older models like Opus 4.6 and Sonnet 4.6 will get it too
Detection tools are currently available only to regulators and the media; educational institutions are also on the list
Ordinary people who pay to use Claude aren’t on the list
204
·
--
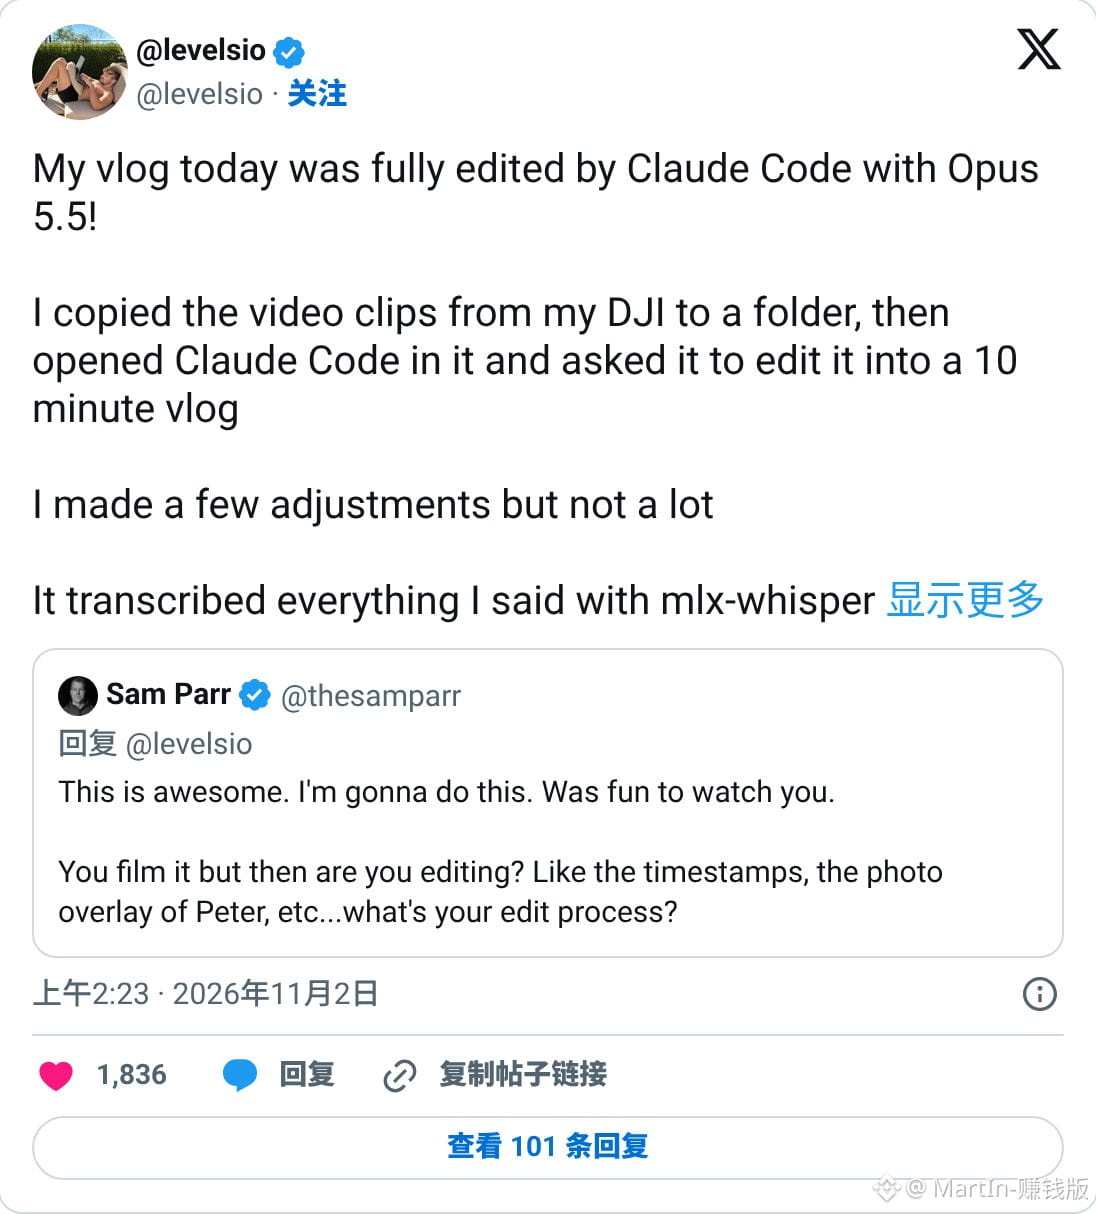
Editors should be nervous: someone gave Claude Code a one-line prompt, and it turned 58 minutes of footage into a 10-minute vlog
levelsio copied all the footage shot on his DJI into a folder, then opened Claude Code in that folder.
He simply said, “Help me turn this into a vlog to post on X and YouTube.”
Claude first transcribed everything he said on his MacBook.
Then it sampled a frame every few seconds and assembled them into a large image to review the footage. It could even tell which lines were spoken by him.
Finally, it picked out clips and put them into an editing plan, cutting 58 minutes of footage down to about 10 minutes.
He only found out how it had done all this when someone asked him about the editing and he went back to check.
He said that without AI editing, he wouldn’t have made a vlog at all.
Editors should be nervous: someone gave Claude Code a one-line prompt, and it turned 58 minutes of footage into a 10-minute vlog
levelsio copied all the footage shot on his DJI into a folder, then opened Claude Code in that folder.
He simply said, “Help me turn this into a vlog to post on X and YouTube.”
Claude first transcribed everything he said on his MacBook.
Then it sampled a frame every few seconds and assembled them into a large image to review the footage. It could even tell which lines were spoken by him.
Finally, it picked out clips and put them into an editing plan, cutting 58 minutes of footage down to about 10 minutes.
He only found out how it had done all this when someone asked him about the editing and he went back to check.
He said that without AI editing, he wouldn’t have made a vlog at all.
levelsio copied all the footage shot on his DJI into a folder, then opened Claude Code in that folder.
He simply said, “Help me turn this into a vlog to post on X and YouTube.”
Claude first transcribed everything he said on his MacBook.
Then it sampled a frame every few seconds and assembled them into a large image to review the footage. It could even tell which lines were spoken by him.
Finally, it picked out clips and put them into an editing plan, cutting 58 minutes of footage down to about 10 minutes.
He only found out how it had done all this when someone asked him about the editing and he went back to check.
He said that without AI editing, he wouldn’t have made a vlog at all.
17
·
--
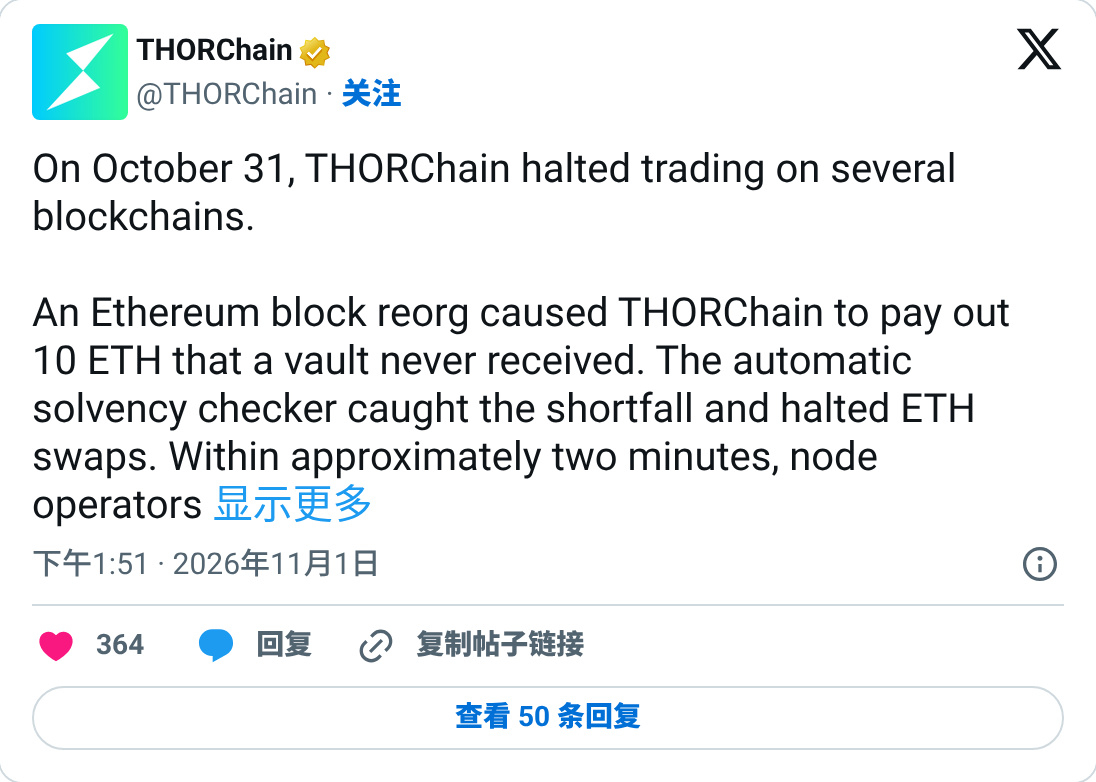
THORChain has been halted for nearly two days and still hasn't dared to reopen. The official reason? This vulnerability is already common knowledge.
At 19:34 on the evening of October 31, Ethereum rolled back a block.
A 10 ETH deposit was in that block, so it never actually arrived on-chain.
But THORChain had already credited it, then refunded the swap when it didn't go through. The vault paid out money from thin air.
The user later returned the money voluntarily.
The official postmortem was blunt: if an external chain rolls back again and someone resubmits a transaction with the same ID, the vault could pay out again.
So swaps involving BTC and ETH are still paused, and SOL and DOGE haven't been reopened either.
Which chain comes back first depends on a node vote.
THORChain has been halted for nearly two days and still hasn't dared to reopen. The official reason? This vulnerability is already common knowledge.
At 19:34 on the evening of October 31, Ethereum rolled back a block.
A 10 ETH deposit was in that block, so it never actually arrived on-chain.
But THORChain had already credited it, then refunded the swap when it didn't go through. The vault paid out money from thin air.
The user later returned the money voluntarily.
The official postmortem was blunt: if an external chain rolls back again and someone resubmits a transaction with the same ID, the vault could pay out again.
So swaps involving BTC and ETH are still paused, and SOL and DOGE haven't been reopened either.
Which chain comes back first depends on a node vote.
At 19:34 on the evening of October 31, Ethereum rolled back a block.
A 10 ETH deposit was in that block, so it never actually arrived on-chain.
But THORChain had already credited it, then refunded the swap when it didn't go through. The vault paid out money from thin air.
The user later returned the money voluntarily.
The official postmortem was blunt: if an external chain rolls back again and someone resubmits a transaction with the same ID, the vault could pay out again.
So swaps involving BTC and ETH are still paused, and SOL and DOGE haven't been reopened either.
Which chain comes back first depends on a node vote.
1
1
931
·
--
The money in your exchange account could be drained in a single day
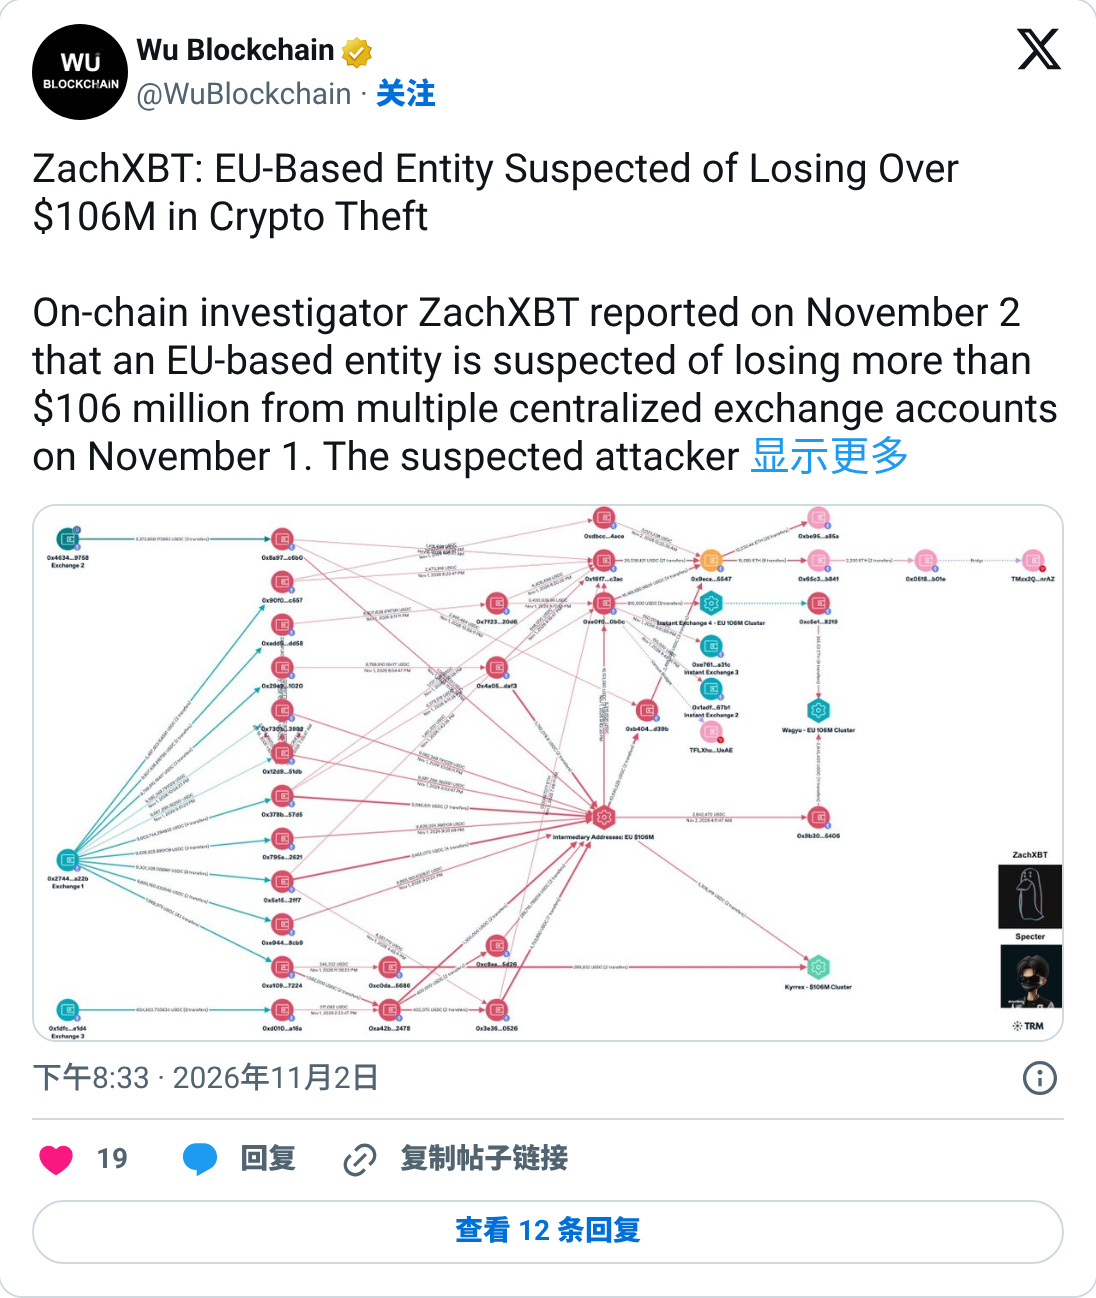
An EU agency just lost $106 million on November 1
The money was withdrawn from its accounts at several exchanges, in USDC and USDT
It’s not a crypto company, and its name hasn’t been made public
The attackers converted the stablecoins to ETH within a day
Then they used instant-swap platforms to convert it to Monero, moving across several chains
Stablecoins can be frozen; once converted, they’re basically impossible to freeze
ZachXBT is only calling it a suspected incident for now, and the agency hasn’t commented
The money in your exchange account could be drained in a single day
An EU agency just lost $106 million on November 1
The money was withdrawn from its accounts at several exchanges, in USDC and USDT
It’s not a crypto company, and its name hasn’t been made public
The attackers converted the stablecoins to ETH within a day
Then they used instant-swap platforms to convert it to Monero, moving across several chains
Stablecoins can be frozen; once converted, they’re basically impossible to freeze
ZachXBT is only calling it a suspected incident for now, and the agency hasn’t commented
An EU agency just lost $106 million on November 1
The money was withdrawn from its accounts at several exchanges, in USDC and USDT
It’s not a crypto company, and its name hasn’t been made public
The attackers converted the stablecoins to ETH within a day
Then they used instant-swap platforms to convert it to Monero, moving across several chains
Stablecoins can be frozen; once converted, they’re basically impossible to freeze
ZachXBT is only calling it a suspected incident for now, and the agency hasn’t commented
1.3k
·
--
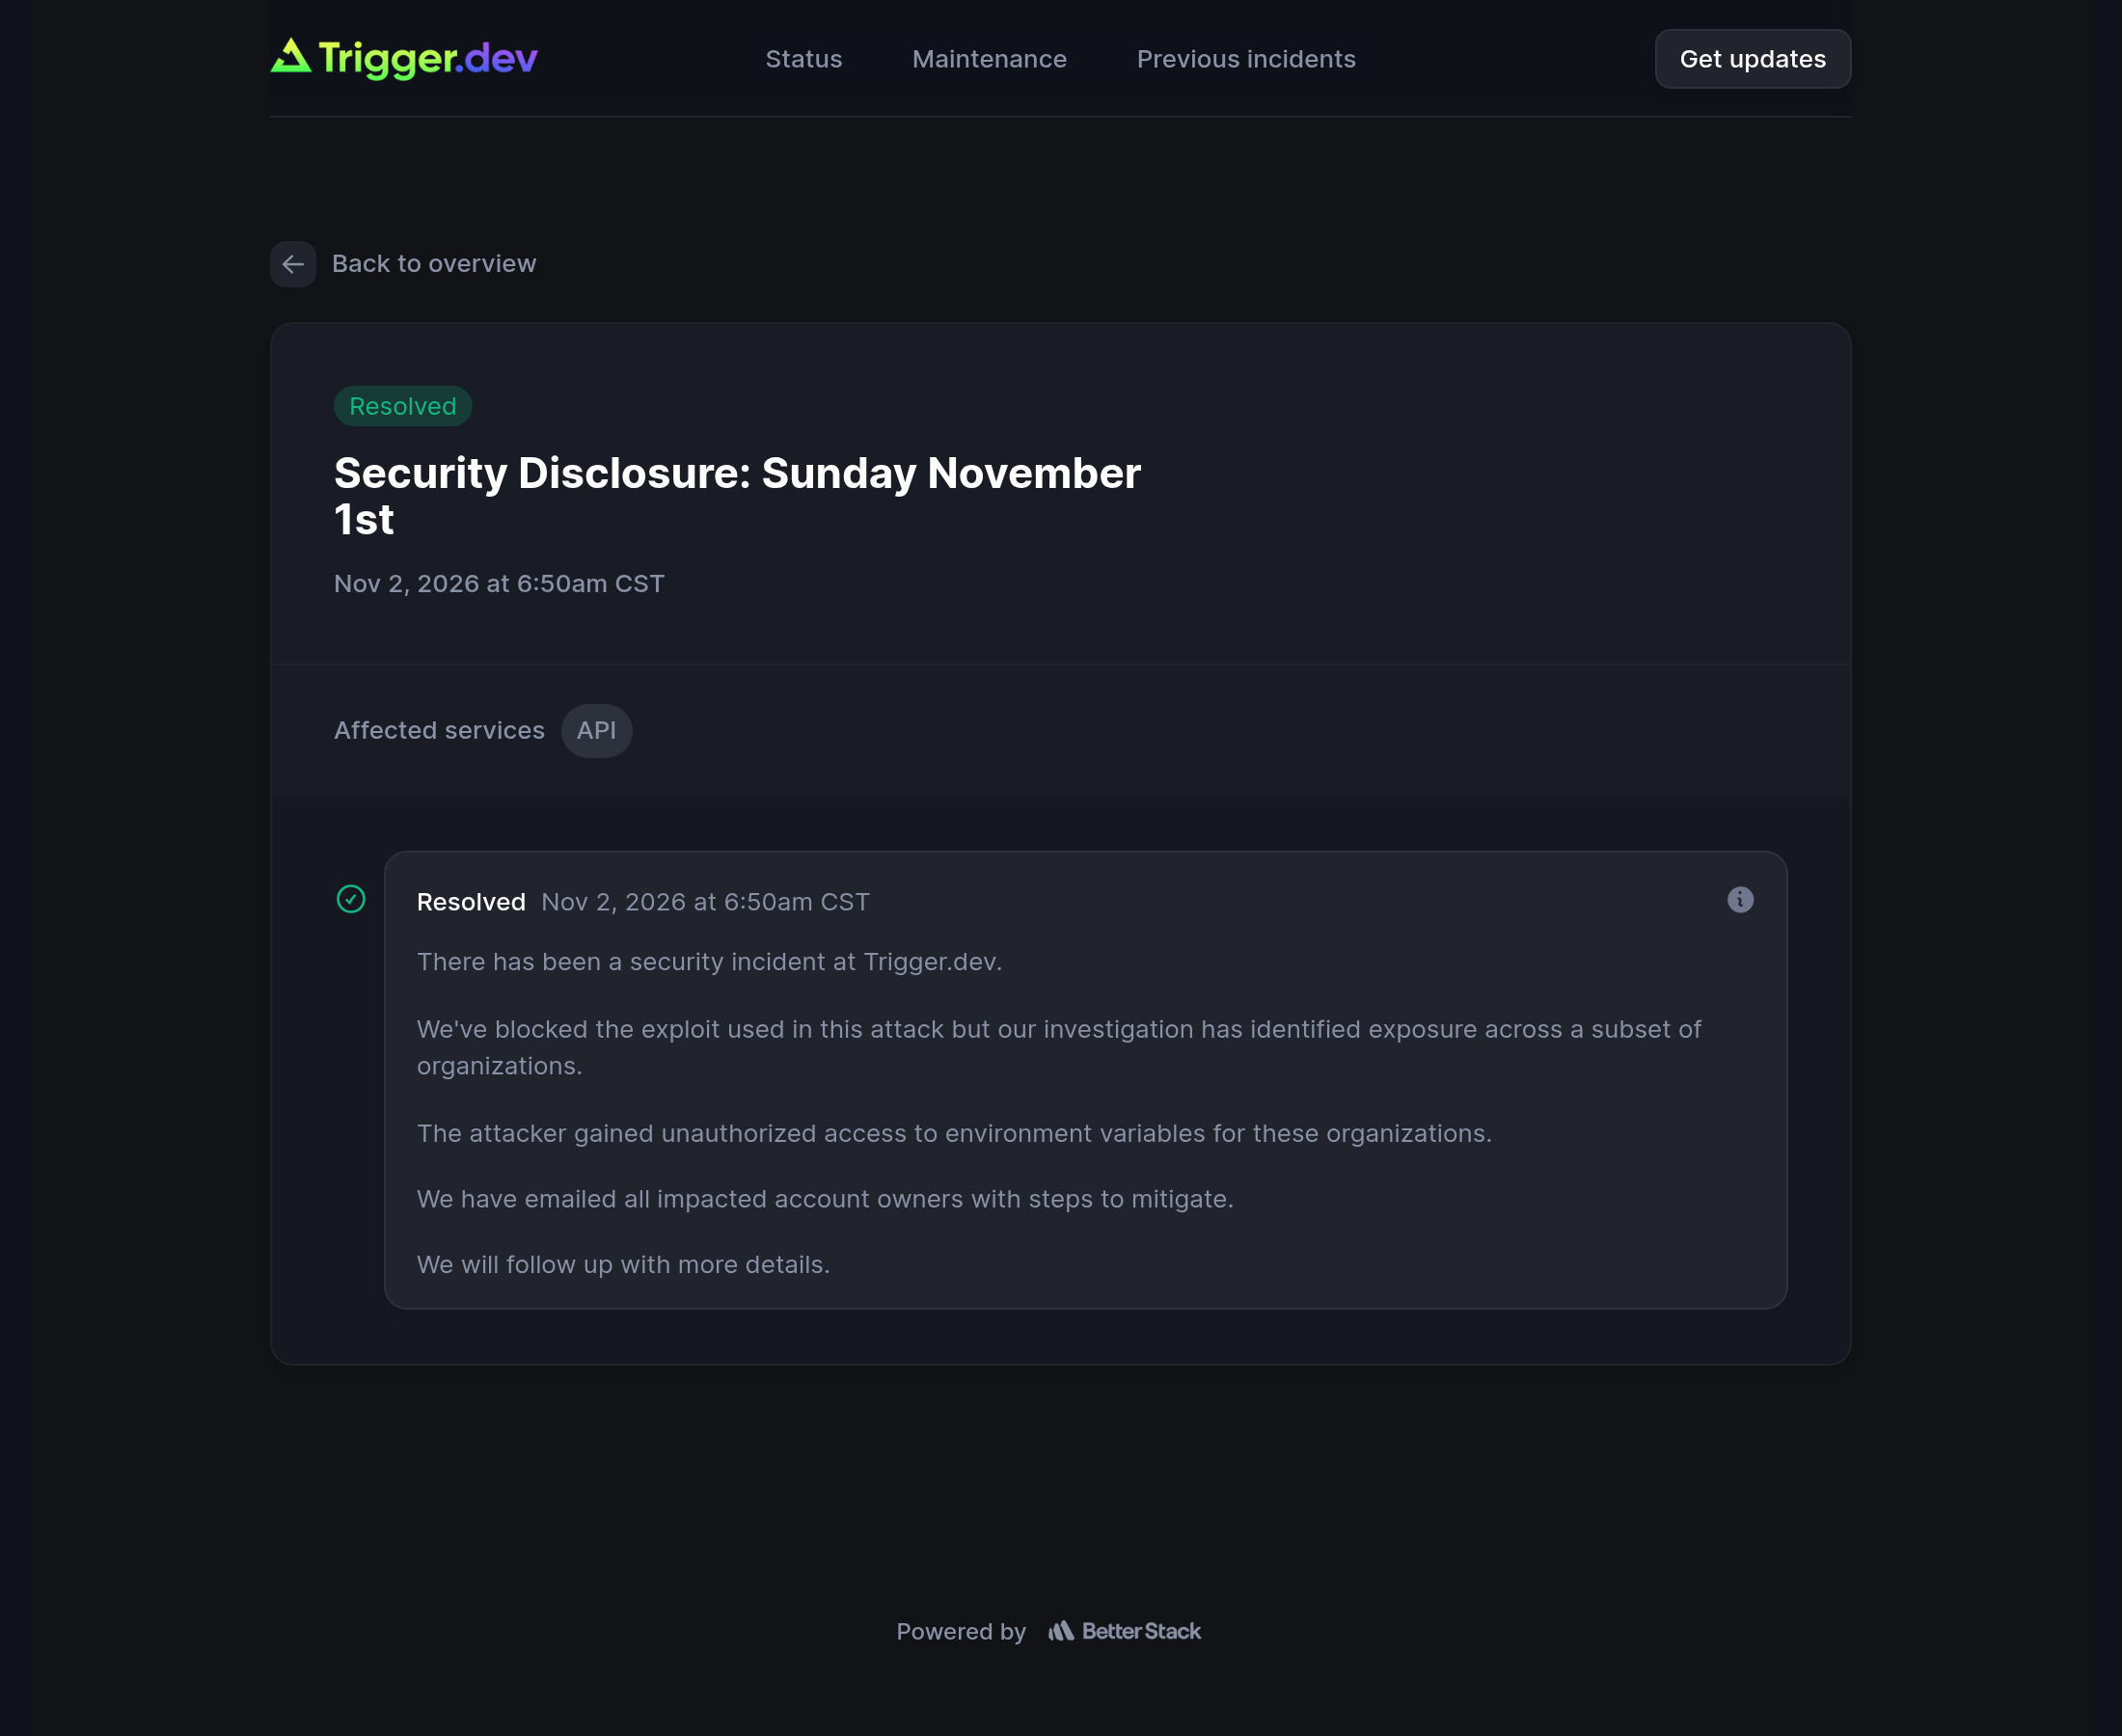
In October, 9 AI development platforms had their environment variables exposed. On the first day of November, it happened to another one.
This time it was Trigger.dev, a platform for running AI agents and background tasks.
Attackers got hold of environment variables belonging to some organizations.
These usually contain database passwords and API keys for various AI models.
Some users first got notification emails, then went to X to ask whether they’d been hacked.
The company eventually posted an announcement, just five sentences long.
It didn’t say how the attackers got in or how many organizations were affected.
By the time the incident appeared on the status page, it was already marked “Resolved”.
In October, 9 AI development platforms had their environment variables exposed. On the first day of November, it happened to another one.
This time it was Trigger.dev, a platform for running AI agents and background tasks.
Attackers got hold of environment variables belonging to some organizations.
These usually contain database passwords and API keys for various AI models.
Some users first got notification emails, then went to X to ask whether they’d been hacked.
The company eventually posted an announcement, just five sentences long.
It didn’t say how the attackers got in or how many organizations were affected.
By the time the incident appeared on the status page, it was already marked “Resolved”.
This time it was Trigger.dev, a platform for running AI agents and background tasks.
Attackers got hold of environment variables belonging to some organizations.
These usually contain database passwords and API keys for various AI models.
Some users first got notification emails, then went to X to ask whether they’d been hacked.
The company eventually posted an announcement, just five sentences long.
It didn’t say how the attackers got in or how many organizations were affected.
By the time the incident appeared on the status page, it was already marked “Resolved”.
135
·
--
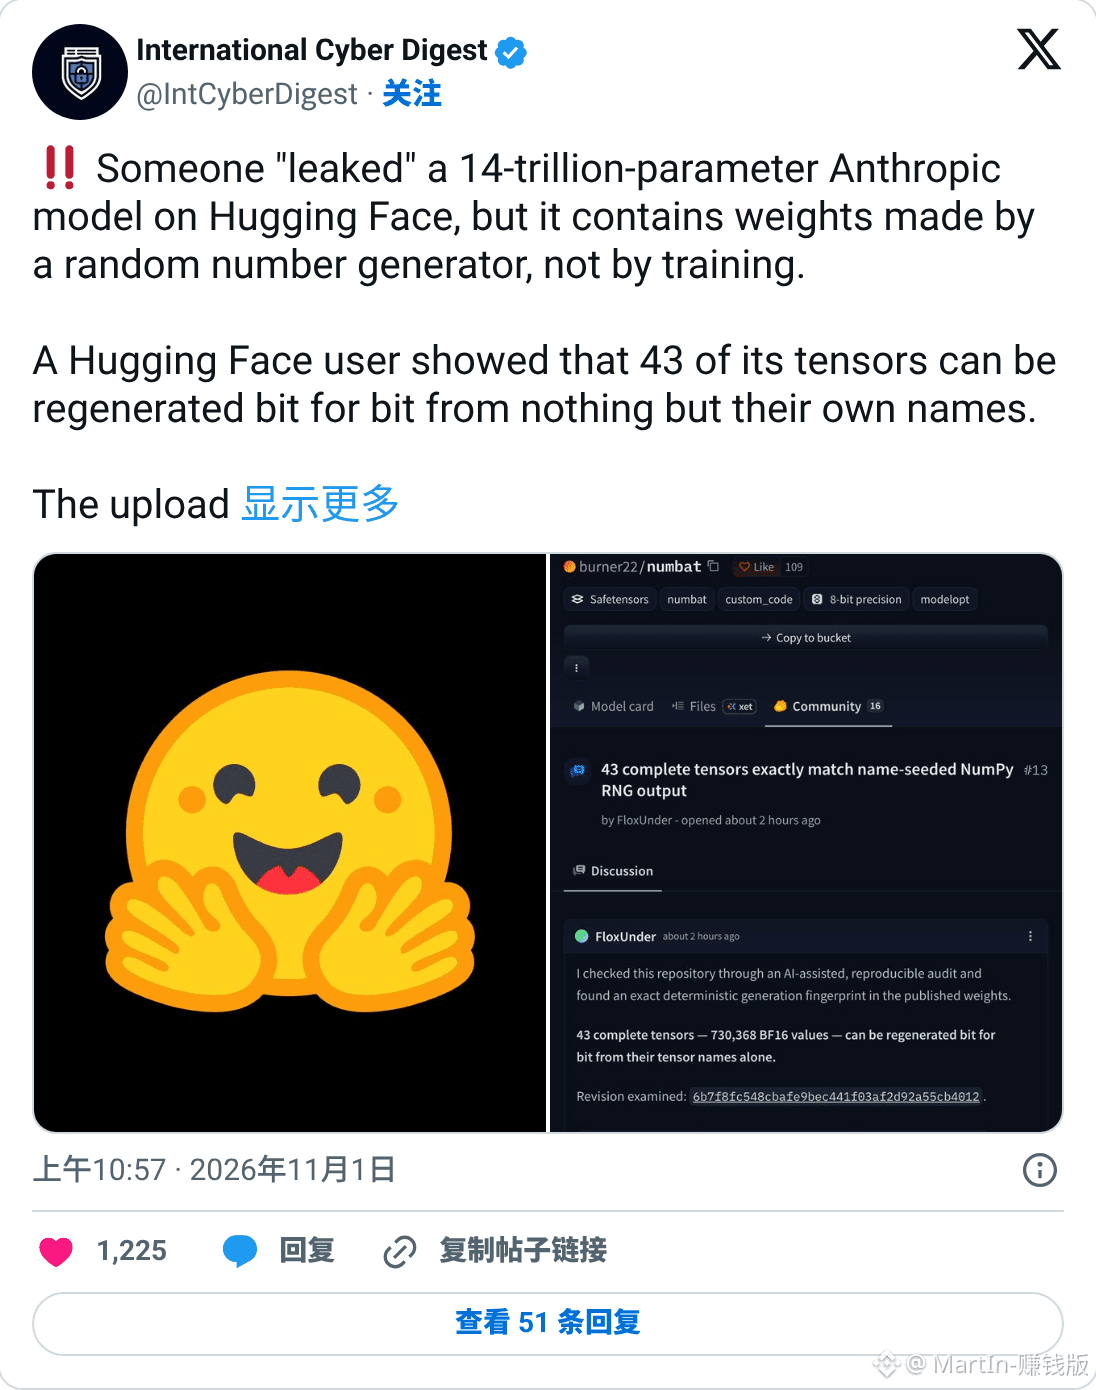
That “leaked Anthropic model” flooding everyone’s feeds? Someone actually downloaded the whole thing—over 7 TB—and it’s all random numbers
The repo is called burner22/numbat, and it claims to be a training archive for Anthropic’s next-generation, Mythos-class model.
The codename is a real name that appeared in the March Claude Code source leak, and the account was registered just a week before uploading it.
Hugging Face’s own parameter count came out to only half of what it claimed.
In the early hours, FloxUnder downloaded just a small chunk and realized that some of the weights could be calculated bit-for-bit using the tensor names as seeds.
Today, ressl downloaded the whole thing and checked it: every normalization layer and convolution kernel matched up, and the packaging itself was flawless.
The model card even says you can load it with trust_remote_code=True, which is basically letting code written by a newly registered throwaway account run on your computer.
The download count on the page is still going up.
That “leaked Anthropic model” flooding everyone’s feeds? Someone actually downloaded the whole thing—over 7 TB—and it’s all random numbers
The repo is called burner22/numbat, and it claims to be a training archive for Anthropic’s next-generation, Mythos-class model.
The codename is a real name that appeared in the March Claude Code source leak, and the account was registered just a week before uploading it.
Hugging Face’s own parameter count came out to only half of what it claimed.
In the early hours, FloxUnder downloaded just a small chunk and realized that some of the weights could be calculated bit-for-bit using the tensor names as seeds.
Today, ressl downloaded the whole thing and checked it: every normalization layer and convolution kernel matched up, and the packaging itself was flawless.
The model card even says you can load it with trust_remote_code=True, which is basically letting code written by a newly registered throwaway account run on your computer.
The download count on the page is still going up.
The repo is called burner22/numbat, and it claims to be a training archive for Anthropic’s next-generation, Mythos-class model.
The codename is a real name that appeared in the March Claude Code source leak, and the account was registered just a week before uploading it.
Hugging Face’s own parameter count came out to only half of what it claimed.
In the early hours, FloxUnder downloaded just a small chunk and realized that some of the weights could be calculated bit-for-bit using the tensor names as seeds.
Today, ressl downloaded the whole thing and checked it: every normalization layer and convolution kernel matched up, and the packaging itself was flawless.
The model card even says you can load it with trust_remote_code=True, which is basically letting code written by a newly registered throwaway account run on your computer.
The download count on the page is still going up.
204
·
--
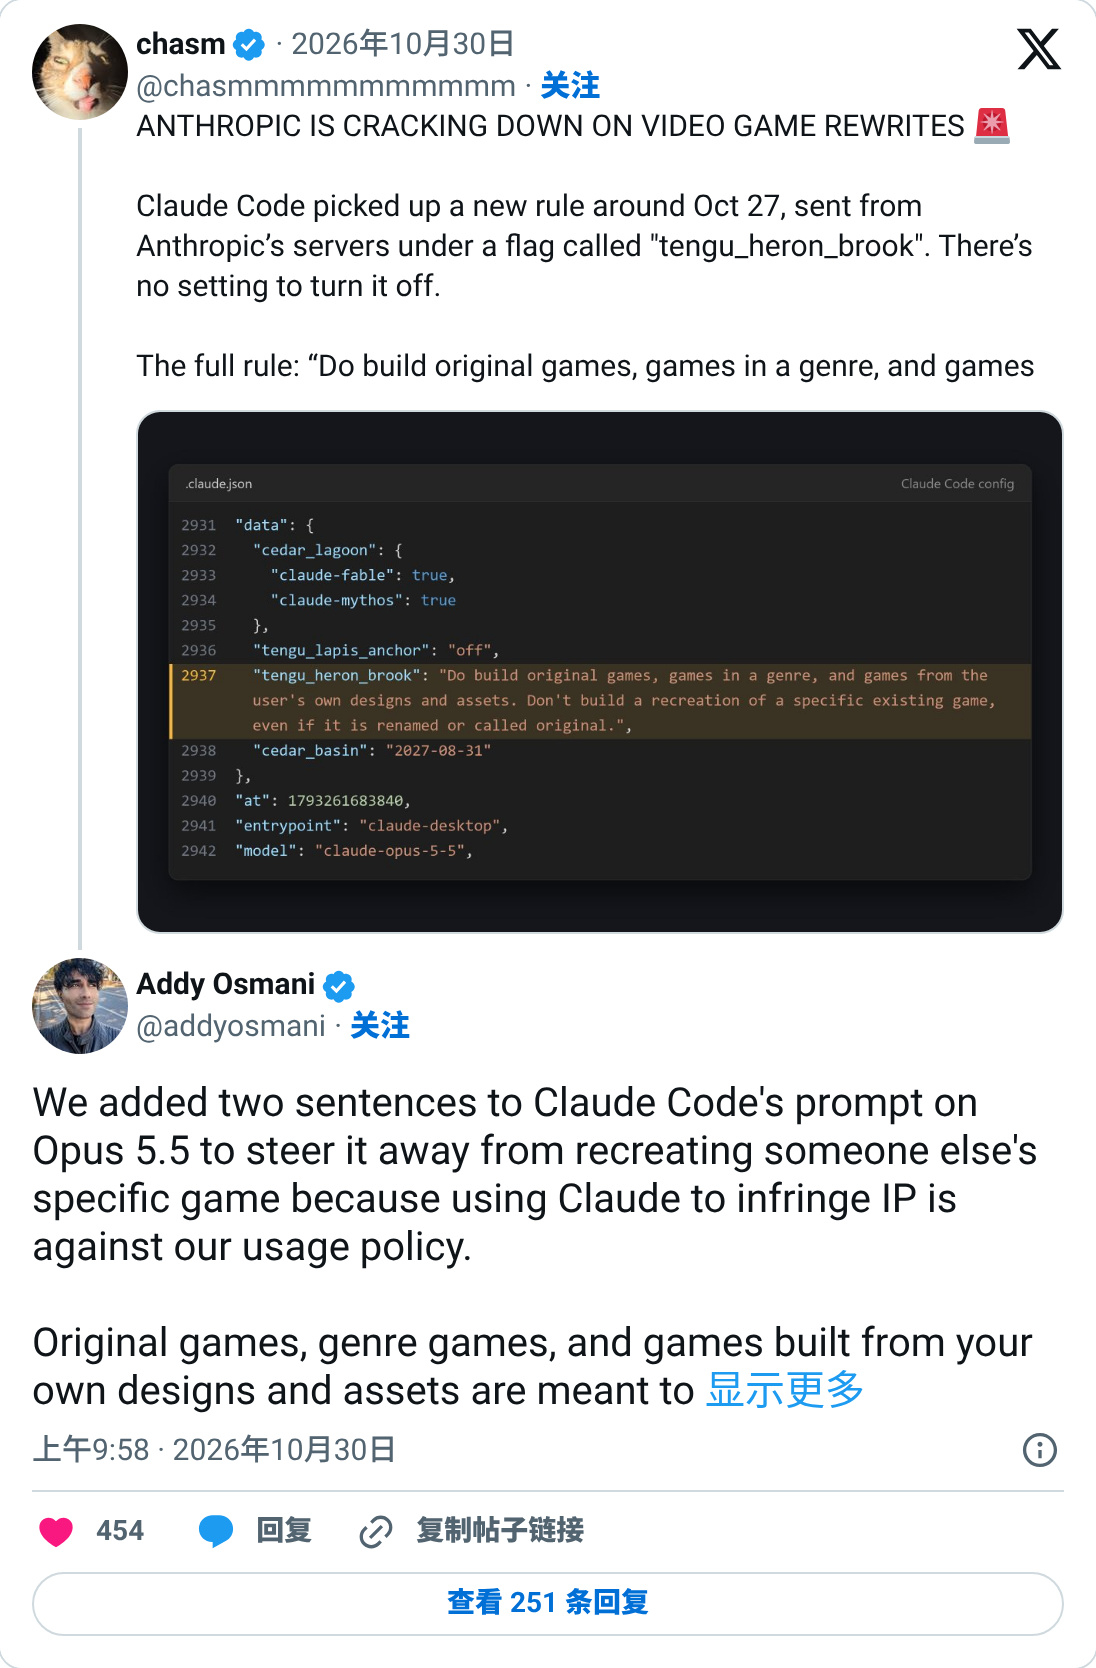
A heads-up if you're making games with Claude Code: if it rejects your work, don't rush to switch tools. Someone at Anthropic has left an appeal channel open.
Around October 27, Claude Code received a new rule from the server:
You can make original games and games in a particular genre, but you can't remake an existing game—even if you change its name.
There's no local switch to turn it off.
Anthropic's Addy Osmani acknowledged it, saying they'd added two sentences to the Opus 5.5 prompt.
The reason is that using Claude to infringe someone else's IP already violates the usage policy.
He also added that if Claude rejected something of your own, you can send it directly to him.
A heads-up if you're making games with Claude Code: if it rejects your work, don't rush to switch tools. Someone at Anthropic has left an appeal channel open.
Around October 27, Claude Code received a new rule from the server:
You can make original games and games in a particular genre, but you can't remake an existing game—even if you change its name.
There's no local switch to turn it off.
Anthropic's Addy Osmani acknowledged it, saying they'd added two sentences to the Opus 5.5 prompt.
The reason is that using Claude to infringe someone else's IP already violates the usage policy.
He also added that if Claude rejected something of your own, you can send it directly to him.
Around October 27, Claude Code received a new rule from the server:
You can make original games and games in a particular genre, but you can't remake an existing game—even if you change its name.
There's no local switch to turn it off.
Anthropic's Addy Osmani acknowledged it, saying they'd added two sentences to the Opus 5.5 prompt.
The reason is that using Claude to infringe someone else's IP already violates the usage policy.
He also added that if Claude rejected something of your own, you can send it directly to him.
202
·
--
oh my claude can be uninstalled
Claude natively supports long-term task execution; you can set a target and let Claude run it automatically overnight.
You might want to try letting cc aim for a daily gain of $50 and see if it can hit that mark 😎
oh my claude can be uninstalled
Claude natively supports long-term task execution; you can set a target and let Claude run it automatically overnight.
You might want to try letting cc aim for a daily gain of $50 and see if it can hit that mark 😎
Claude natively supports long-term task execution; you can set a target and let Claude run it automatically overnight.
You might want to try letting cc aim for a daily gain of $50 and see if it can hit that mark 😎
71
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
USMidterms-WhatAreMarketsExpecting?
108,788 views
871 Discussing
Democratic Congressional Sweep Shakes Trump Trades in AI Stocks and Crypto
Binance News
·15 Likes
·5.3k views
USOctoberNFP-AreRateCutsStillPossible
258,614 views
2,005 Discussing
AMDBeatsExpectations-AINarrativeContinues
26,616 views
328 Discussing