The attack took place through API Keys, where they found and exploited a vulnerability.
What are API Keys used for?
They are permissions and keys that allow you to operate automatically, through bots, for example.
API Keys grant permissions to buy, sell, create pools, etc.
They allow you to do almost everything, EXCEPT WITHDRAW FUNDS TO ANOTHER ACCOUNT.
If your API Key is stolen, your money cannot be stolen directly, because the thief cannot withdraw it to another wallet.
This provides security, allowing bots to operate smoothly and with confidence.
- But this is how they exploited a loophole on Lighter:
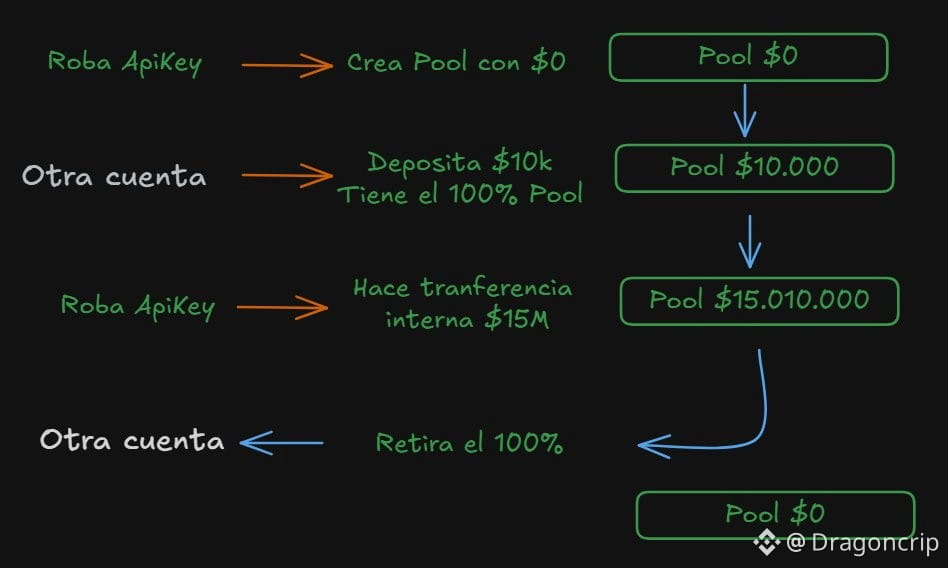
1. The attacker obtained a Market Maker’s API Key.
2. They closed all open trades, leaving the balance in USDC.
3. They created a Public Pool, but deposited nothing ($0).
4. From their own wallet, the attacker invested $10,000 USDC and bought 100% of the shares (at that point, they were the only investor).
5. They returned to the stolen account (the one that created the pool in step 3) and made an internal transfer of $15 M to the pool through the API.
*Since it was an internal transfer, they did not buy shares in the pool as they had in step 4.
6. Since the attacker held 100% of the pool’s shares in their own wallet, they withdrew all the money to their wallet.
In other words, they could not use the API to withdraw the money to the hacker’s wallet. So they used the API to create the public pool, the hacker’s wallet bought 100% of the pool, then they used the API to make an internal transfer to the pool they had created, and the hacker used their wallet to withdraw their 100% share of the pool.
The attacker used the system’s logic to steal money from a user, not from the protocol itself. However, they used protocol permissions, such as the ability to make an internal transfer to the pool.
Lighter is responsible for allowing this functionality and for exposing some of the dangers of API Keys.
What are API Keys used for?
They are permissions and keys that allow you to operate automatically, through bots, for example.
API Keys grant permissions to buy, sell, create pools, etc.
They allow you to do almost everything, EXCEPT WITHDRAW FUNDS TO ANOTHER ACCOUNT.
If your API Key is stolen, your money cannot be stolen directly, because the thief cannot withdraw it to another wallet.
This provides security, allowing bots to operate smoothly and with confidence.
- But this is how they exploited a loophole on Lighter:
1. The attacker obtained a Market Maker’s API Key.
2. They closed all open trades, leaving the balance in USDC.
3. They created a Public Pool, but deposited nothing ($0).
4. From their own wallet, the attacker invested $10,000 USDC and bought 100% of the shares (at that point, they were the only investor).
5. They returned to the stolen account (the one that created the pool in step 3) and made an internal transfer of $15 M to the pool through the API.
*Since it was an internal transfer, they did not buy shares in the pool as they had in step 4.
6. Since the attacker held 100% of the pool’s shares in their own wallet, they withdrew all the money to their wallet.
In other words, they could not use the API to withdraw the money to the hacker’s wallet. So they used the API to create the public pool, the hacker’s wallet bought 100% of the pool, then they used the API to make an internal transfer to the pool they had created, and the hacker used their wallet to withdraw their 100% share of the pool.
The attacker used the system’s logic to steal money from a user, not from the protocol itself. However, they used protocol permissions, such as the ability to make an internal transfer to the pool.
Lighter is responsible for allowing this functionality and for exposing some of the dangers of API Keys.