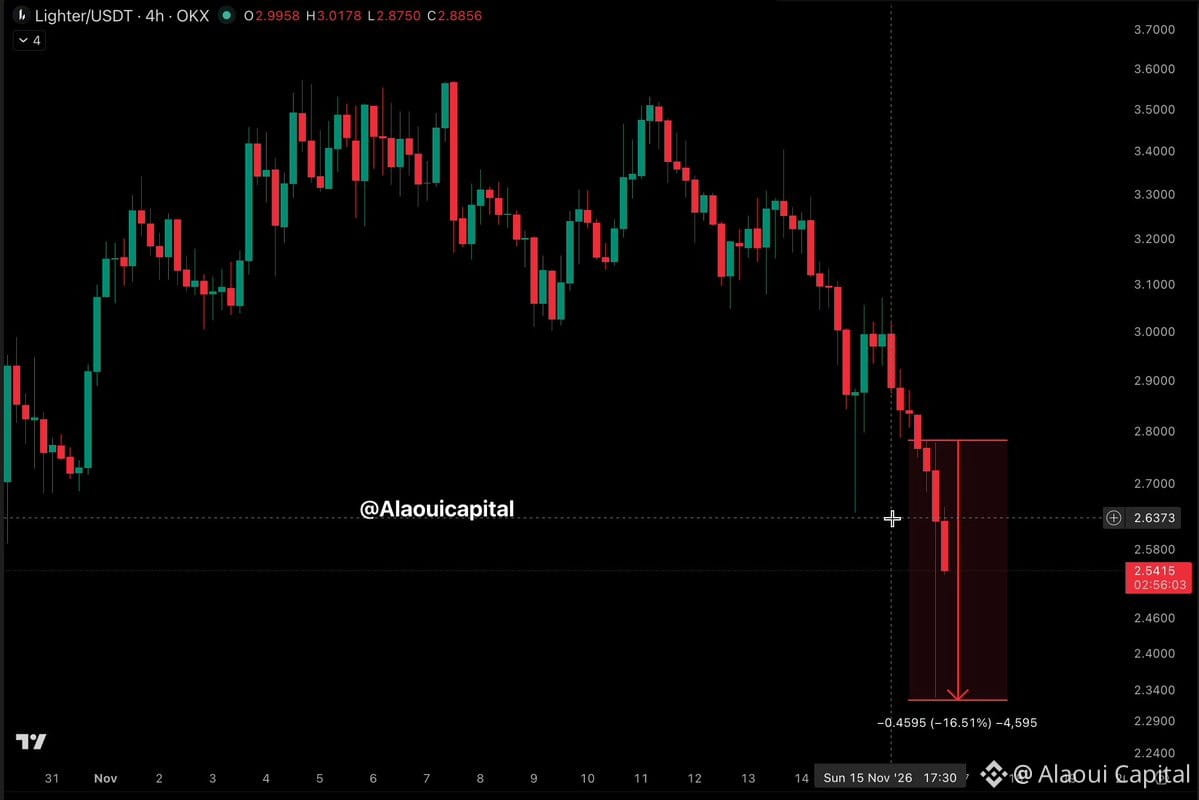

$LIT got hit where users least expected it.
$15.6M allegedly drained through compromised market-maker API keys and Lighter's Public Pools mechanism.
The scary part? The attacker didn't need a normal external withdrawal permission.
They allegedly used pools linked to the victims' own L1 addresses to move the funds.
That's a pretty expensive permissions lesson.
Now the question every user is asking:
Can I trust the permissions, pools and withdrawal infrastructure with my capital?
Recovering funds is one thing. Recovering confidence is another.
$15.6M allegedly drained through compromised market-maker API keys and Lighter's Public Pools mechanism.
The scary part? The attacker didn't need a normal external withdrawal permission.
They allegedly used pools linked to the victims' own L1 addresses to move the funds.
That's a pretty expensive permissions lesson.
Now the question every user is asking:
Can I trust the permissions, pools and withdrawal infrastructure with my capital?
Recovering funds is one thing. Recovering confidence is another.