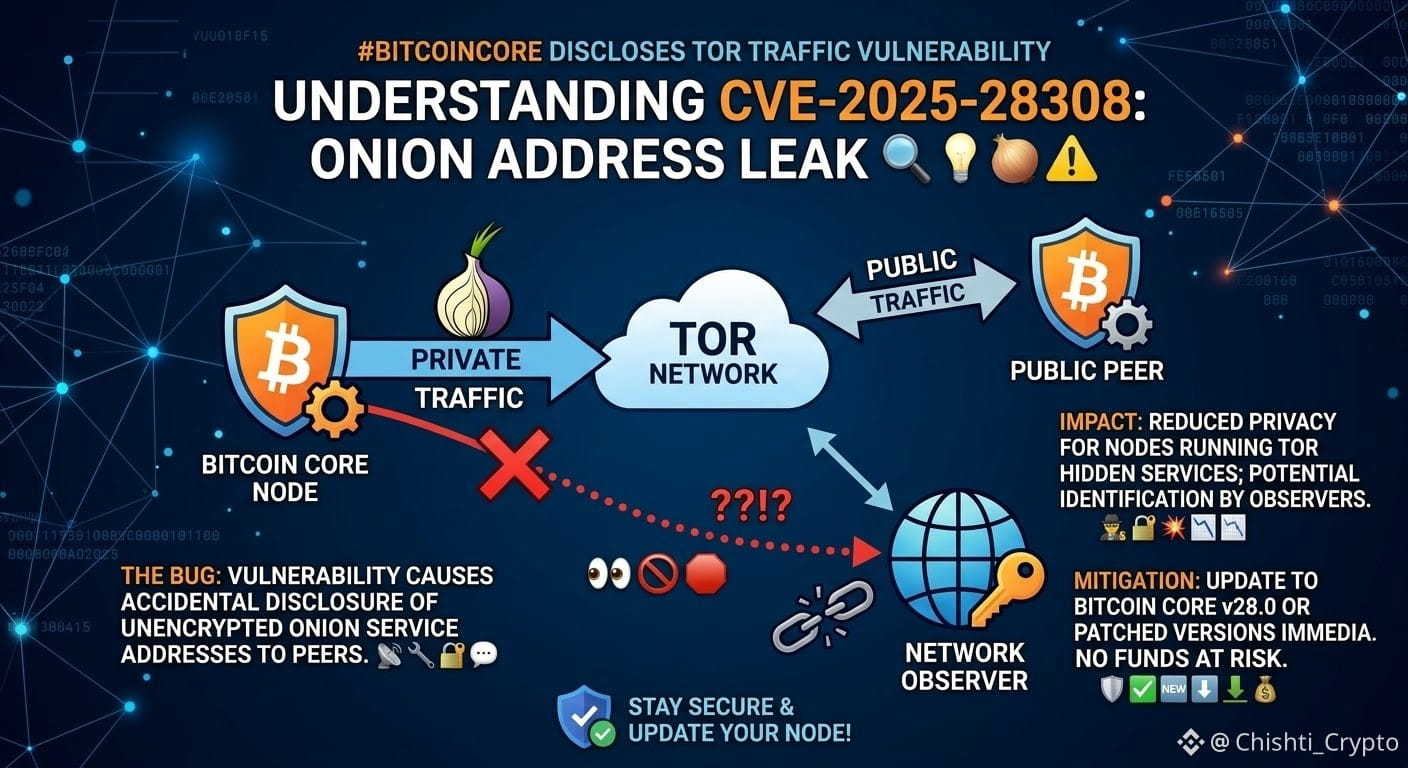
#BitcoinCoreDisclosesTorTrafficVulnerability 🚨 Bitcoin Core just disclosed a notable security flaw (CVE-2025-62860) that allowed incoming Tor traffic to inherit "trusted" permissions across thousands of reachable nodes. 🧅
When operators bundled Tor via local service providers using optional whitelist configurations, external onion connections were mistakenly treated like trusted local peers—bypassing certain spam limits and privacy protections. 🛡️
The good news? There’s no reason to panic. ✅ Developers quietly patched the bug back in October 2025 (starting in versions 28.3, 29.2, and 30.0) and waited until the 29.x series reached end-of-life before going public. No active exploits have been reported, and standard nodes without custom allowlists were never at risk.
Still, if you’re running a node on outdated software, now is the time to upgrade to a supported release! 🔄⚡
#BitcoinCoreDisclosesTorTrafficVulnerability #Bitcoin #CryptoSecurity
$BTC
$XRP
$SOL
When operators bundled Tor via local service providers using optional whitelist configurations, external onion connections were mistakenly treated like trusted local peers—bypassing certain spam limits and privacy protections. 🛡️
The good news? There’s no reason to panic. ✅ Developers quietly patched the bug back in October 2025 (starting in versions 28.3, 29.2, and 30.0) and waited until the 29.x series reached end-of-life before going public. No active exploits have been reported, and standard nodes without custom allowlists were never at risk.
Still, if you’re running a node on outdated software, now is the time to upgrade to a supported release! 🔄⚡
#BitcoinCoreDisclosesTorTrafficVulnerability #Bitcoin #CryptoSecurity
$BTC
$XRP
$SOL