Telegram new chat feature could open another door for malware. Be careful before updating.
SlowMist founder Yu Xian has warned about Telegram’s new feature that allows interactive applications to be embedded directly inside chat messages.
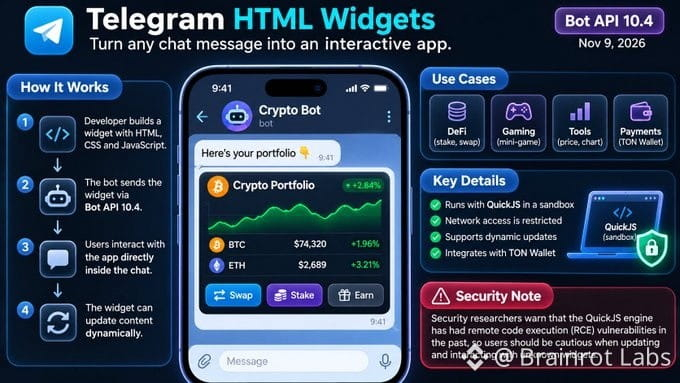
The feature, introduced in Bot API 10.4 on November 9, uses QuickJS to execute JavaScript code.
Why security researchers are concerned:
- QuickJS runs inside a sandbox designed to isolate code execution.
- Network access is restricted by Telegram.
- However, researchers have previously identified remote code execution vulnerabilities in the related engine that could potentially bypass sandbox isolation.
Sandboxing and network restrictions reduce risk, but they don't guarantee complete protection against vulnerabilities in the underlying JavaScript engine.
Telegram chats are getting more interactive. Just make sure you aren't interacting with malware disguised as a useful mini-app.
Would you trust every interactive app embedded in a Telegram message?
SlowMist founder Yu Xian has warned about Telegram’s new feature that allows interactive applications to be embedded directly inside chat messages.
The feature, introduced in Bot API 10.4 on November 9, uses QuickJS to execute JavaScript code.
Why security researchers are concerned:
- QuickJS runs inside a sandbox designed to isolate code execution.
- Network access is restricted by Telegram.
- However, researchers have previously identified remote code execution vulnerabilities in the related engine that could potentially bypass sandbox isolation.
Sandboxing and network restrictions reduce risk, but they don't guarantee complete protection against vulnerabilities in the underlying JavaScript engine.
Telegram chats are getting more interactive. Just make sure you aren't interacting with malware disguised as a useful mini-app.
Would you trust every interactive app embedded in a Telegram message?