I've seen a lot of hacks, but this one is different — it came through the official release channel itself.
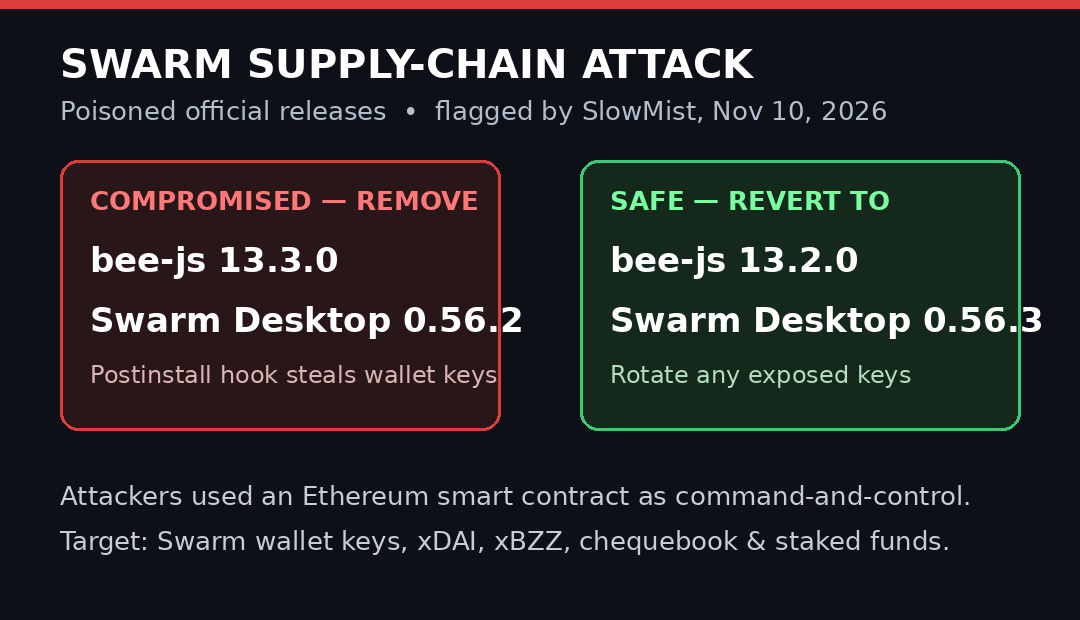
On November 9, the Swarm team's automated release process was compromised, and two poisoned versions went out through official channels: the @ethersphere/bee-js 13.3.0 npm package and Swarm Desktop 0.56.2. SlowMist flagged it on November 10. The tampered packages run a script the moment you install them — no second click needed — and the attackers even used an Ethereum smart contract as their command-and-control server. The target: Swarm wallet keys, xDAI, $BZZ, chequebook funds and staked tokens.
My take: this is the scariest class of attack in crypto right now, because there was nothing for the victim to do wrong. No phishing link, no fake site — the official package was the trap. If you installed bee-js 13.3.0 or Swarm Desktop 0.56.2, treat that machine as fully compromised: delete the package, go back to bee-js 13.2.0 or Swarm Desktop 0.56.3, and rotate any exposed keys.
The lesson I keep coming back to: 'download from the official source' isn't enough anymore. Verify the version, check the advisory, and never install a fresh release on a machine that holds real keys on day one.
Are you still running dev tools and wallets on the same machine?
On November 9, the Swarm team's automated release process was compromised, and two poisoned versions went out through official channels: the @ethersphere/bee-js 13.3.0 npm package and Swarm Desktop 0.56.2. SlowMist flagged it on November 10. The tampered packages run a script the moment you install them — no second click needed — and the attackers even used an Ethereum smart contract as their command-and-control server. The target: Swarm wallet keys, xDAI, $BZZ, chequebook funds and staked tokens.
My take: this is the scariest class of attack in crypto right now, because there was nothing for the victim to do wrong. No phishing link, no fake site — the official package was the trap. If you installed bee-js 13.3.0 or Swarm Desktop 0.56.2, treat that machine as fully compromised: delete the package, go back to bee-js 13.2.0 or Swarm Desktop 0.56.3, and rotate any exposed keys.
The lesson I keep coming back to: 'download from the official source' isn't enough anymore. Verify the version, check the advisory, and never install a fresh release on a machine that holds real keys on day one.
Are you still running dev tools and wallets on the same machine?