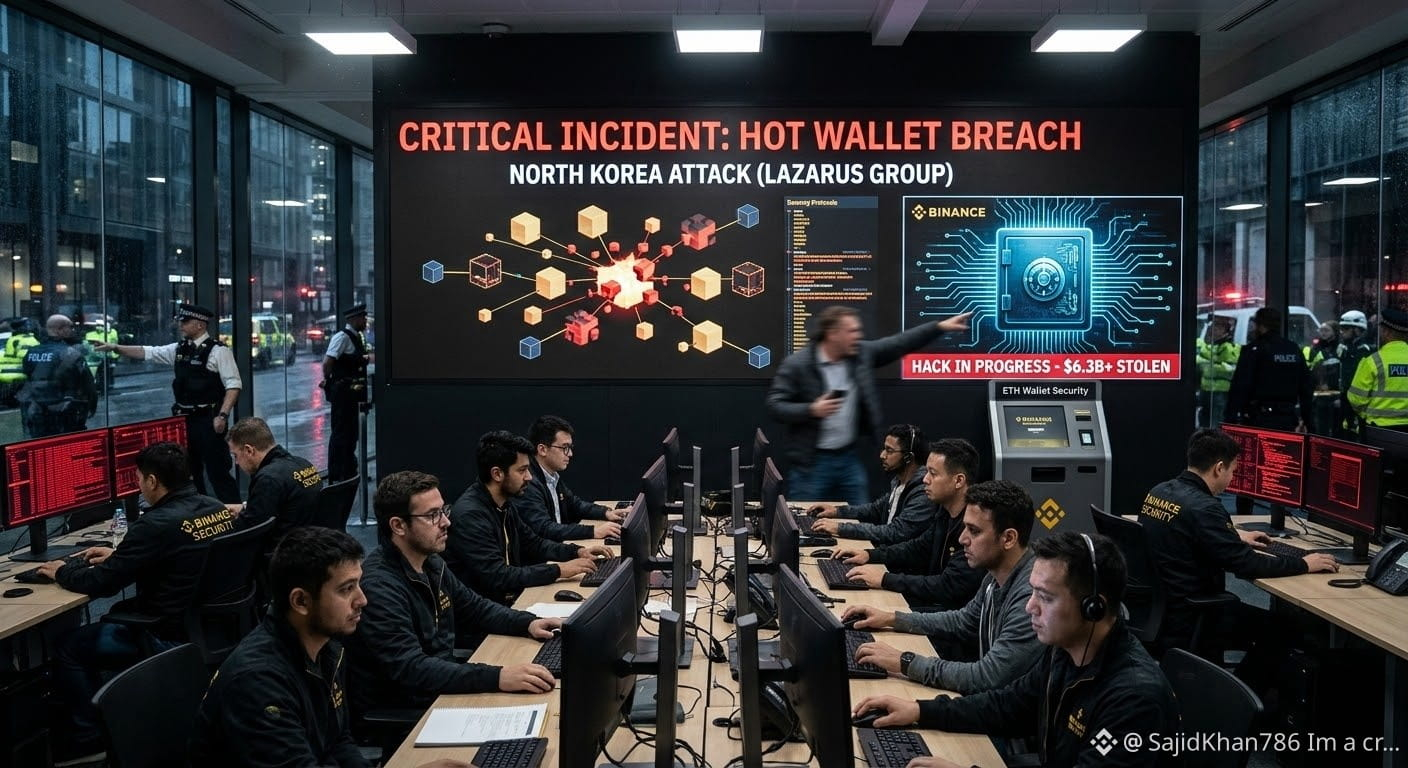
On October 29, 2026, Binance fell victim to one of the largest hacks and security breaches in history. Over $6.34 billion worth of cryptocurrency was stolen in this attack.
The primary causes and methods of this hack are as follows:
1. Social Engineering and Targeting Employees
Fake Job Interview: In September 2026, hackers targeted a Binance software engineer through a professional platform with a fake job offer. During the interview, they were asked to download a "task/assignment" file that contained dangerous malware.
Seizure of Internal Tools: Once the virus ran on the engineer's computer, the hackers gained access to Binance's internal systems and AI tools, and also took control of other engineers' systems.
2. Failure of the Hot Wallet Signing Infrastructure
Hackers gained control of Binance's Hot Wallet Signing Infrastructure (where daily transactions are authorized).
On the Ethereum network, they used the EIP-7702 technique and pre-prepared authorizations to withdraw billions of dollars in Ethereum and USDT from Binance's wallets within just a few minutes.
3. Who was the Hacker?
According to investigations by blockchain security firms (TRM Labs, Chainalysis) and the FBI, the attack was carried out by the North Korean hacking group TraderTraitor (Lazarus Group).
Current Situation and User Funds
Recovery of Funds: Through the prompt action of Binance and security firms, approximately $2.7 to $3 billion worth of crypto was immediately frozen (blocked).
User Losses: Binance promptly confirmed that all user funds were secure and fully absorbed 100% of the losses using the company's assets (SAFU / Reserve Funds), completely restoring all affected tokens by November 3, resulting in zero personal loss for users.
thank you binance #CPITestsDecemberRateOutlook
The primary causes and methods of this hack are as follows:
1. Social Engineering and Targeting Employees
Fake Job Interview: In September 2026, hackers targeted a Binance software engineer through a professional platform with a fake job offer. During the interview, they were asked to download a "task/assignment" file that contained dangerous malware.
Seizure of Internal Tools: Once the virus ran on the engineer's computer, the hackers gained access to Binance's internal systems and AI tools, and also took control of other engineers' systems.
2. Failure of the Hot Wallet Signing Infrastructure
Hackers gained control of Binance's Hot Wallet Signing Infrastructure (where daily transactions are authorized).
On the Ethereum network, they used the EIP-7702 technique and pre-prepared authorizations to withdraw billions of dollars in Ethereum and USDT from Binance's wallets within just a few minutes.
3. Who was the Hacker?
According to investigations by blockchain security firms (TRM Labs, Chainalysis) and the FBI, the attack was carried out by the North Korean hacking group TraderTraitor (Lazarus Group).
Current Situation and User Funds
Recovery of Funds: Through the prompt action of Binance and security firms, approximately $2.7 to $3 billion worth of crypto was immediately frozen (blocked).
User Losses: Binance promptly confirmed that all user funds were secure and fully absorbed 100% of the losses using the company's assets (SAFU / Reserve Funds), completely restoring all affected tokens by November 3, resulting in zero personal loss for users.
thank you binance #CPITestsDecemberRateOutlook