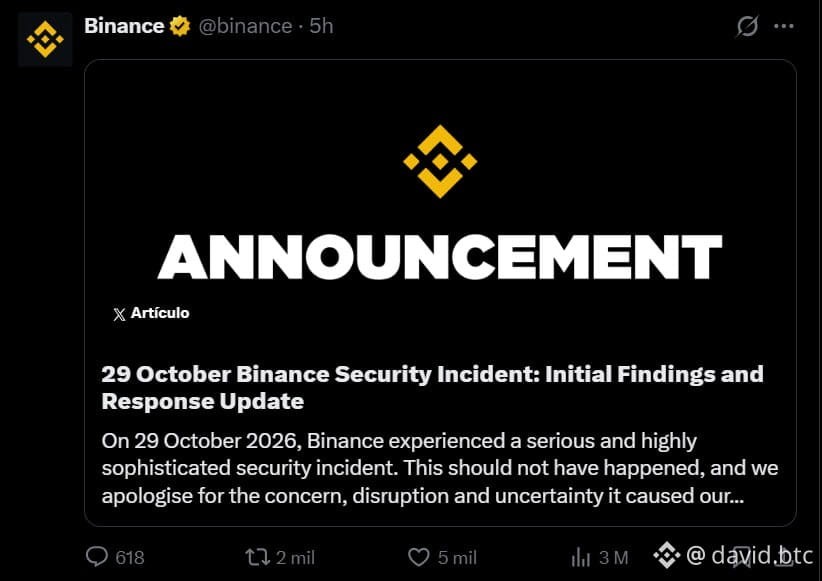
Binance just dropped the full post-mortem on how North Korean hackers pulled off the biggest crypto heist in history—$6.34B gone in 20 minutes.
Here's the kill chain:
June: Binance engineer Googles an AI coding tool. Clicks a fake ad. Downloads malware. Binance catches it, swaps his machine—but hackers already mapped the wallet infrastructure team.
September: They pivot. Target another engineer via a legit job platform. Fake recruiter. Real video interviews. Then the closer: "Here's your technical assessment, download this file."
File = zero-day malware. No AV flags it.
Once inside, they lateral move through internal tooling, compromise two more engineers, steal wallet access credentials.
October 29: They drain $6.34B in under 20 minutes.
FBI confirmed it's TraderTraitor—North Korea's elite unit. Same crew that hit Bybit for $1.5B in 2025. Fake job offers are their signature move.
Binance covered 98% of user funds from reserves. No customer losses. But the real alpha here: if Binance engineers fell for this, you're not immune.
Never download files from strangers. No matter how good the offer sounds. Social engineering is the #1 attack vector in crypto—and it's only getting sharper.
Would you have caught the red flags in that "interview"?
Here's the kill chain:
June: Binance engineer Googles an AI coding tool. Clicks a fake ad. Downloads malware. Binance catches it, swaps his machine—but hackers already mapped the wallet infrastructure team.
September: They pivot. Target another engineer via a legit job platform. Fake recruiter. Real video interviews. Then the closer: "Here's your technical assessment, download this file."
File = zero-day malware. No AV flags it.
Once inside, they lateral move through internal tooling, compromise two more engineers, steal wallet access credentials.
October 29: They drain $6.34B in under 20 minutes.
FBI confirmed it's TraderTraitor—North Korea's elite unit. Same crew that hit Bybit for $1.5B in 2025. Fake job offers are their signature move.
Binance covered 98% of user funds from reserves. No customer losses. But the real alpha here: if Binance engineers fell for this, you're not immune.
Never download files from strangers. No matter how good the offer sounds. Social engineering is the #1 attack vector in crypto—and it's only getting sharper.
Would you have caught the red flags in that "interview"?