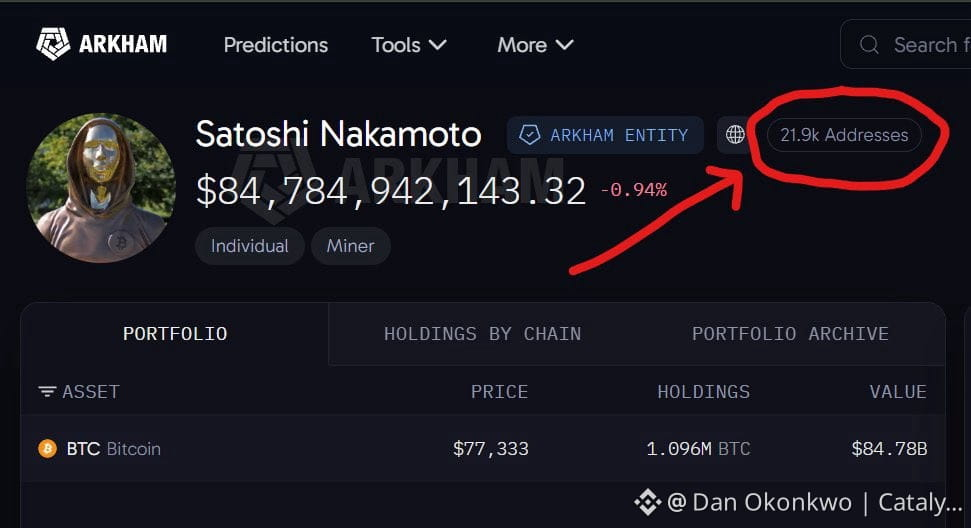
⚠️Why hackers still can't touch Satoshi's wallet?👇👇1.096 million BTC, worth $84.78 billion, untouched for 17 years.
1. No master key, just 21,900 separate locks
Most wallets today use one seed phrase that controls everything. The 2009 v0.1 client worked differently. Every time it mined 50 BTC, it generated a brand-new private key with no link to any of the others.
Even if someone cracked one key, they'd get 50 BTC. The other 21,899 would stay out of reach, with no clues to go on.
2. 256-bit randomness leaves AI nothing to learn
AI is good at finding patterns, and pure randomness doesn't have any. Even with every supercomputer on Earth brute-forcing it, guessing a single key would take tens of billions of years.
3. Offline and never moved, so there's no trail
The keys were kept in an offline wallet.dat file. They were never in the cloud and never tied to an online account anyone could hack. None of the mining addresses has ever sent a single coin. No transactions means no signatures were ever broadcast, so there's no math to work backward from.
4. The one real risk: quantum computing
Modern addresses don't reveal their public key until they send funds. Satoshi's 2009 addresses do: their public keys are written right on the blockchain where anyone can see them.
Today's computers and AI still can't break them. But a powerful enough quantum computer could, in theory, use those public keys to work out the private keys. That's the only real threat to this fortune #BTC #Satoshi #Hack #AI
1. No master key, just 21,900 separate locks
Most wallets today use one seed phrase that controls everything. The 2009 v0.1 client worked differently. Every time it mined 50 BTC, it generated a brand-new private key with no link to any of the others.
Even if someone cracked one key, they'd get 50 BTC. The other 21,899 would stay out of reach, with no clues to go on.
2. 256-bit randomness leaves AI nothing to learn
AI is good at finding patterns, and pure randomness doesn't have any. Even with every supercomputer on Earth brute-forcing it, guessing a single key would take tens of billions of years.
3. Offline and never moved, so there's no trail
The keys were kept in an offline wallet.dat file. They were never in the cloud and never tied to an online account anyone could hack. None of the mining addresses has ever sent a single coin. No transactions means no signatures were ever broadcast, so there's no math to work backward from.
4. The one real risk: quantum computing
Modern addresses don't reveal their public key until they send funds. Satoshi's 2009 addresses do: their public keys are written right on the blockchain where anyone can see them.
Today's computers and AI still can't break them. But a powerful enough quantum computer could, in theory, use those public keys to work out the private keys. That's the only real threat to this fortune #BTC #Satoshi #Hack #AI