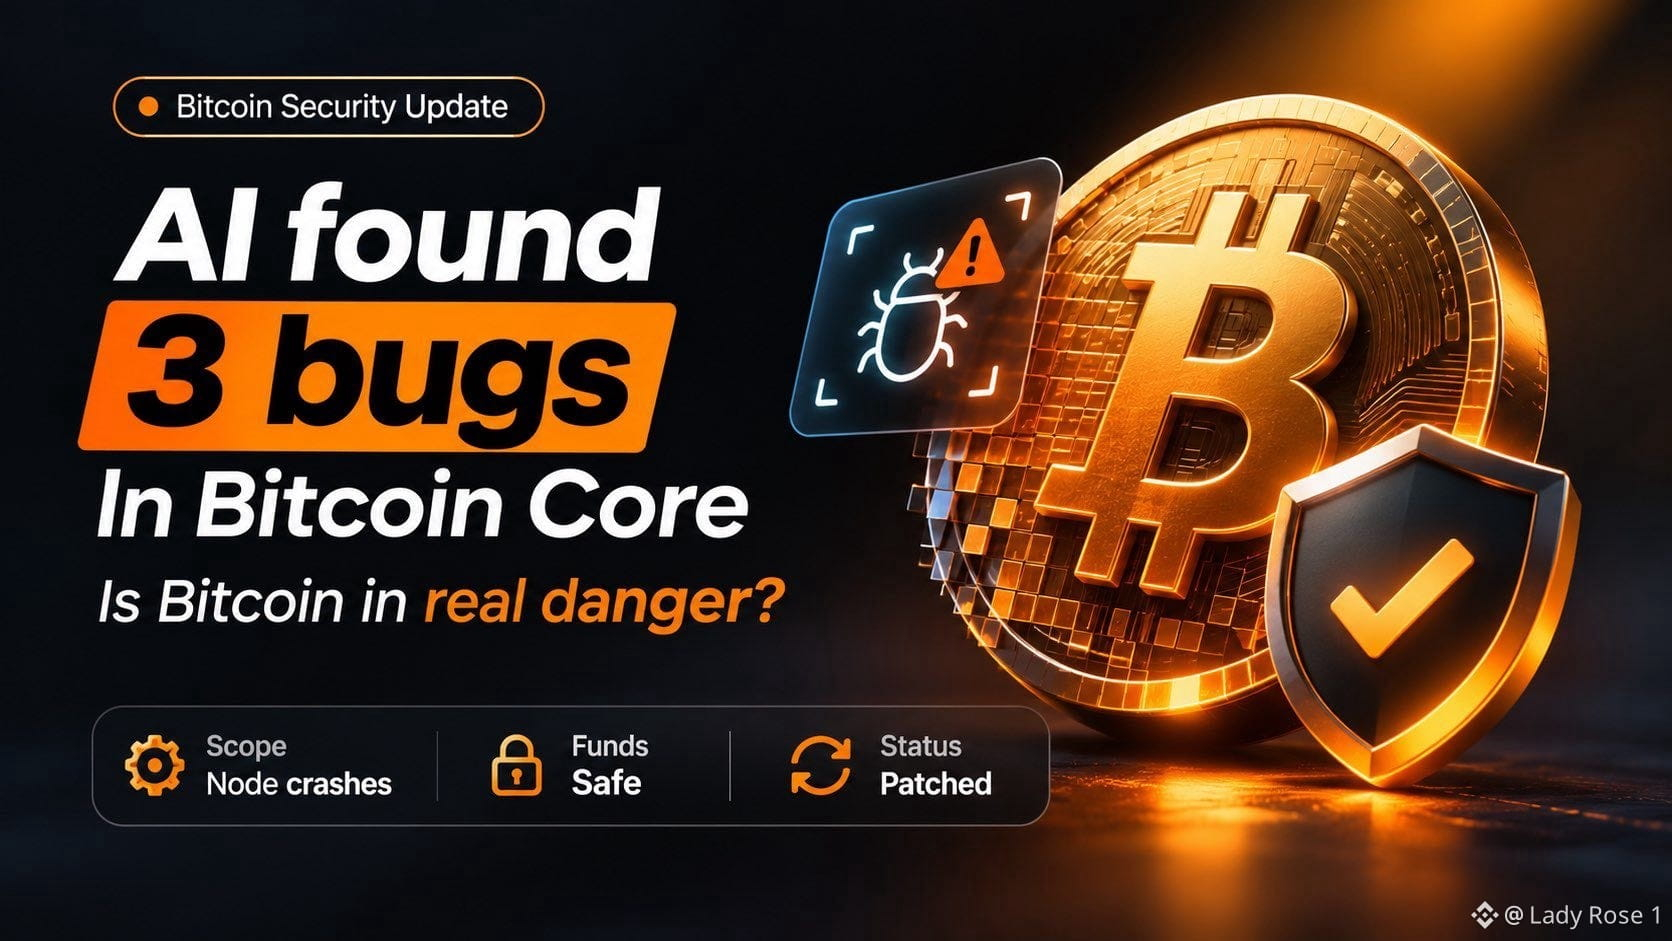
Not really. Here’s why.
Disclosed on October 28, the three vulnerabilities were identified through Project Loupe, an AI-assisted security scan led by Spiral.
Their impact was limited to individual nodes:
• One could crash Windows, macOS and BSD nodes through memory exhaustion.
• Another could slowly consume node memory through outdated peer connections.
• The third could cause node failures under extreme block and storage conditions.
The important part: these bugs cannot steal $BTC , create extra coins or compromise Bitcoin’s consensus.
No exploitation has been reported, and security patches are already available.
This is a reminder that Bitcoin’s security also depends on the people maintaining its infrastructure.
AI helped find the weaknesses. Developers validated and fixed them.
For node operators, updating is the next step.
Disclosed on October 28, the three vulnerabilities were identified through Project Loupe, an AI-assisted security scan led by Spiral.
Their impact was limited to individual nodes:
• One could crash Windows, macOS and BSD nodes through memory exhaustion.
• Another could slowly consume node memory through outdated peer connections.
• The third could cause node failures under extreme block and storage conditions.
The important part: these bugs cannot steal $BTC , create extra coins or compromise Bitcoin’s consensus.
No exploitation has been reported, and security patches are already available.
This is a reminder that Bitcoin’s security also depends on the people maintaining its infrastructure.
AI helped find the weaknesses. Developers validated and fixed them.
For node operators, updating is the next step.