

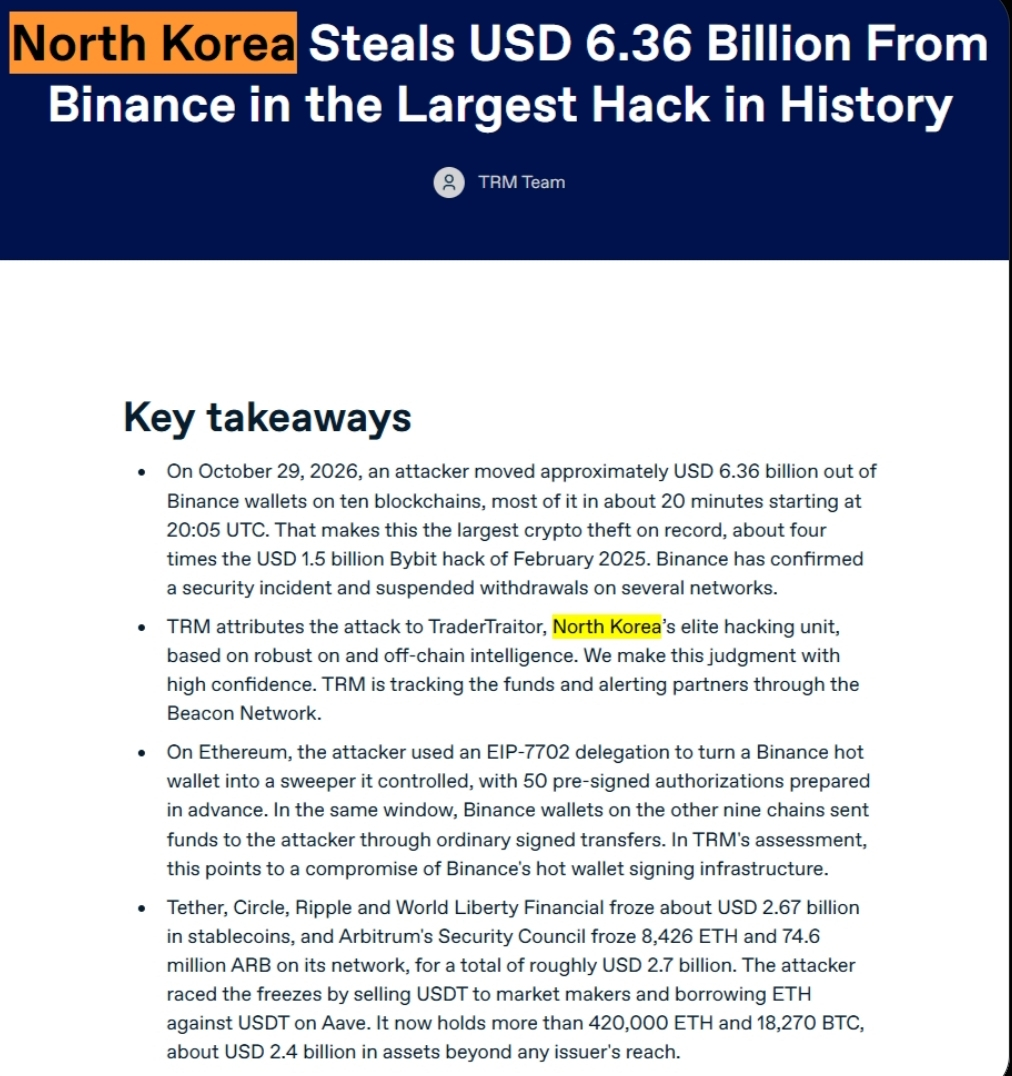
 A major cybersecurity breakthrough has officially attributed one of the largest cyber-heists in cryptocurrency history directly to North Korean state-sponsored threat actors.
According to a recent report published by blockchain intelligence firm TRM Labs, the elite North Korean cybercrime unit known as TraderTraitor has been identified as the mastermind behind the catastrophic $6.3 billion Binance exploit.$BTC $BNB
Who is TraderTraitor?
TraderTraitor (also tracked under cyber intelligence umbrellas alongside the Lazarus Group) is a sophisticated, state-backed threat actor known for targeting Web3 infrastructure, crypto exchanges, and decentralized finance (DeFi) protocols.
The group primarily relies on targeted spear-phishing campaigns, malicious trading applications, and complex social engineering tactics to gain initial network access and compromise administrative credentials.
Key Highlights of the Investigation:
Attribution: On-chain analytics and forensic tracking by TRM Labs tied the movement of stolen funds back to wallet addresses linked to TraderTraitor infrastructure.
Modus Operandi: The attackers utilized advanced obfuscation techniques, cross-chain bridges, and mixing services to launder the proceeds before intelligence firms successfully traced the flow.
Geopolitical Impact: Experts suggest funds stolen by TraderTraitor are systematically funneled into North Korea's state-sponsored weapons programs and cyber operations.
What This Means for the Crypto Ecosystem
This incident underscores the rising sophistication of nation-state actors in the Web3 domain. Security analysts strongly advise projects and centralized entities to enforce strict multi-party computation (MPC) controls, rigorous employee security awareness training, and real-time transaction monitoring to guard against state-backed exploitation.
Stay tuned as further updates and official statements from security researchers continue to unfold. #SuspectedNorthKoreaAttacksAccountForNearly89%OfCryptoHackLosses