Four data-leak disclosures landed around Oct 28, and none of them touched user funds. That's exactly why they matter. 🔐
On and around Oct 28: Coinbase said contact data for a "small subset" of users was exposed through Amplitude, a third-party analytics vendor. Coinbase says its own systems weren't breached and funds are safe. Bithumb reported unauthorized access to an internal mobile groupware system — employee data confirmed, customer data still under investigation. Daishin Securities: personal and credit info of 38,490 customers leaked from a non-face-to-face discretionary account-opening server. Mirae Asset Global Investments: outsiders viewed internal business info; the firm says investor personal data wasn't exposed.
My take: "no funds lost" doesn't close the case. Leaked emails, phone numbers and names are raw material for phishing and SIM swaps, and the attack usually shows up weeks later as a fake "support" call. The weak link here was mostly vendors and side systems, not the trading engine.
CZ's checklist is worth copying: a unique email alias per exchange, authenticator apps or hardware keys instead of SMS 2FA, withdrawal whitelisting, a carrier number lock, and regular session/API key reviews.
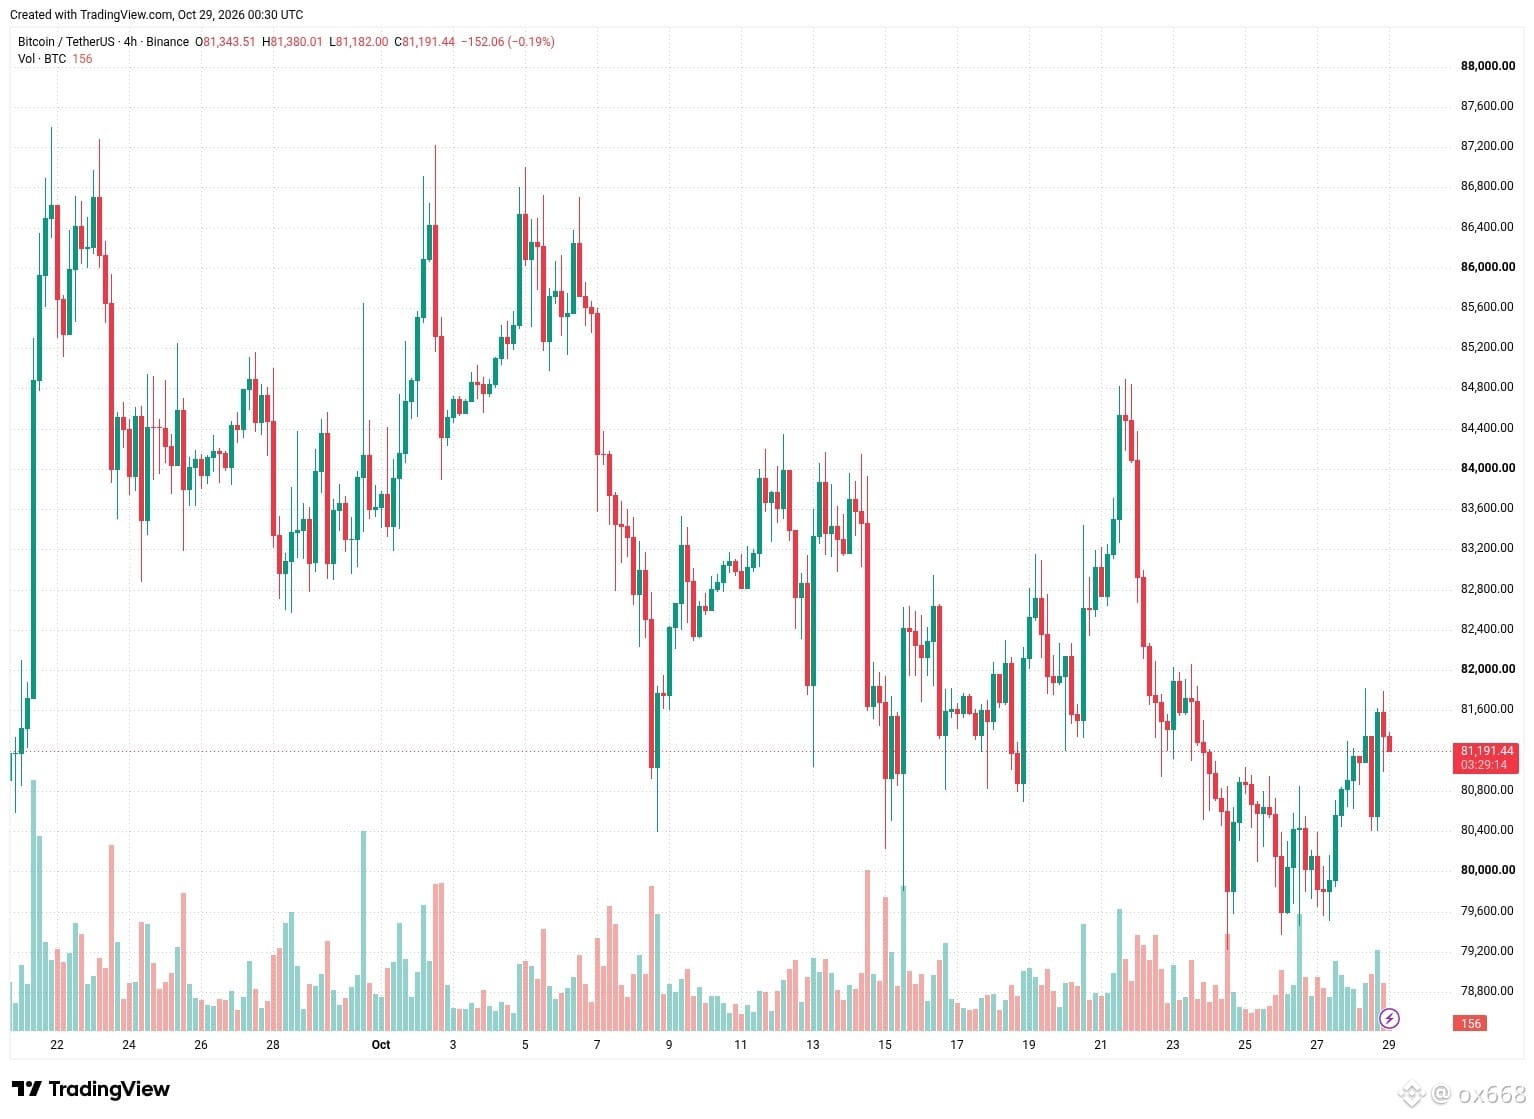
$BTC is holding near $81.2K, so the market barely reacted. Your security setup shouldn't wait for the market to care.
$BTC $BNB #CryptoSecurity #DataBreach #Coinbase #Bithumb
Not financial advice.