

EXECUTIVE SUMMARY & THREAT OVERVIEW
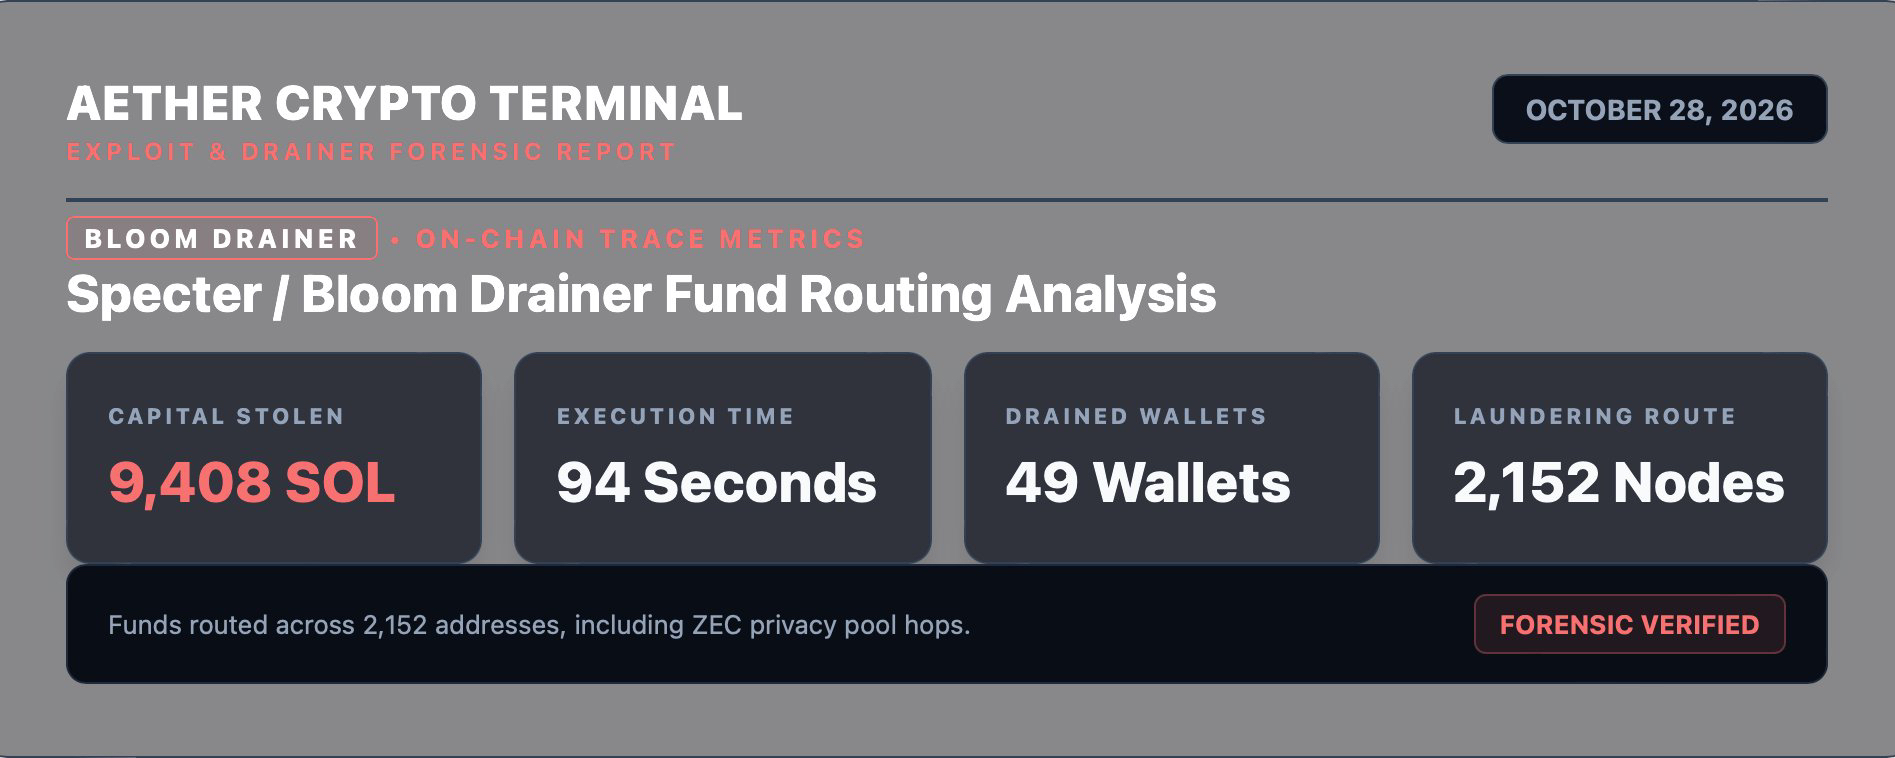
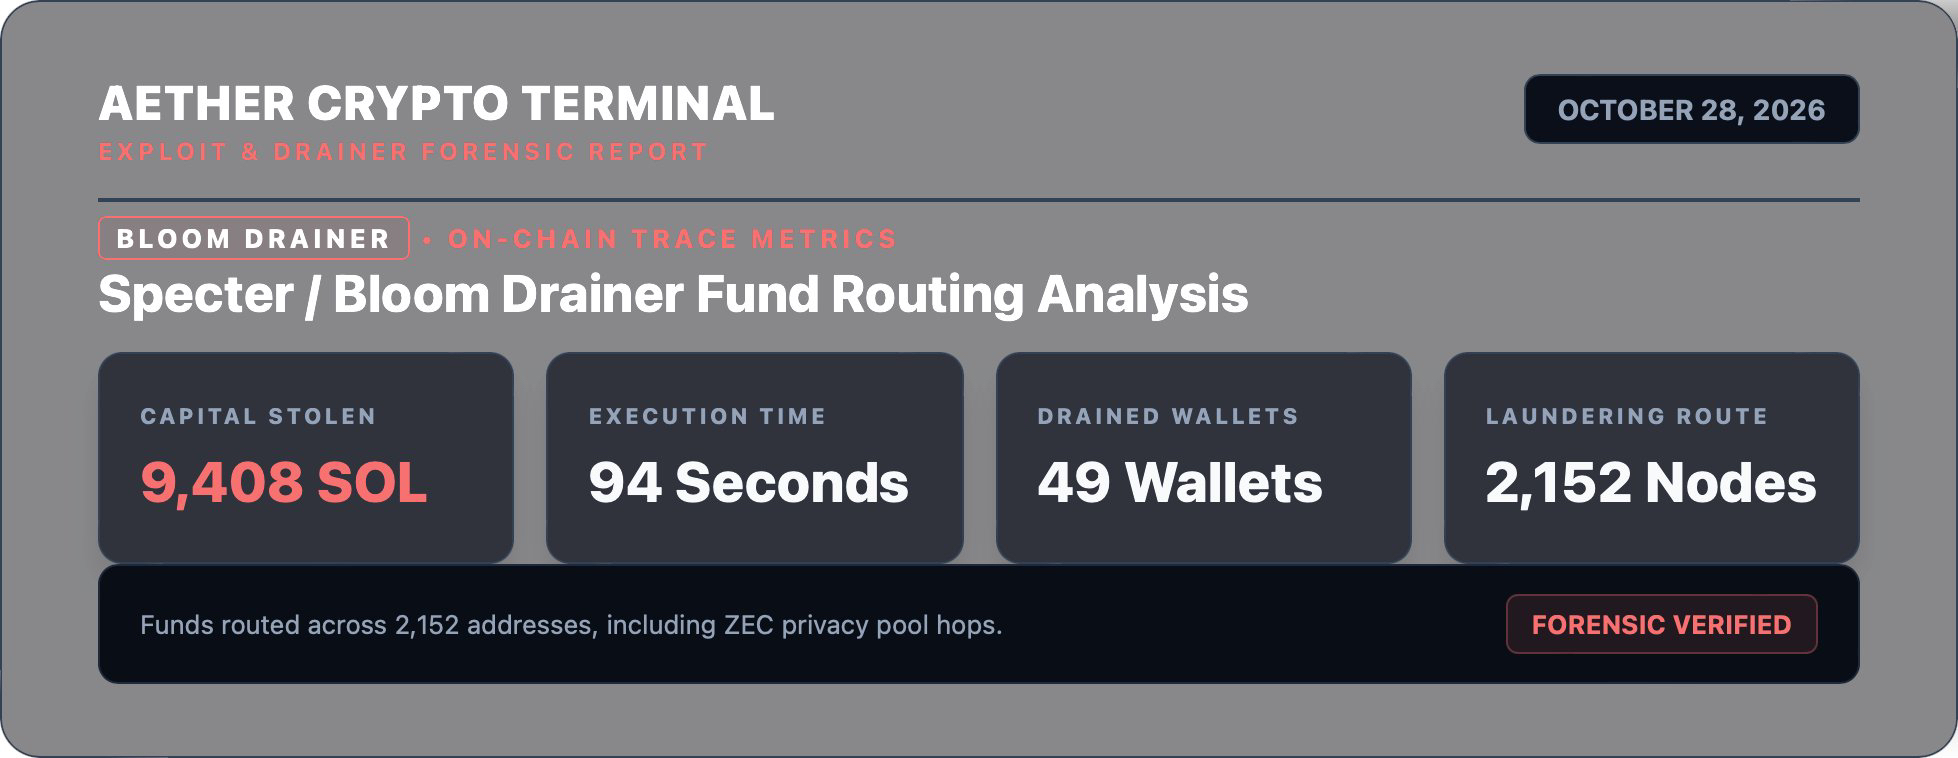
Aether On-Chain Intelligence Desk monitored an automated exploit targeting users of Bloom Trading (BloomBot), a widely adopted automated trading application across Solana ($SOL ). The attacker compromised 49 wallets assigned to 9 high-volume trading accounts, siphoning 9,408 SOL (~$1,000,000 USD). The threat actor executed an automated money-laundering script that atomized funds across 2,152 distinct addresses, cross-chain bridges, and the Zcash ($ZEC ) Sapling shielded pool
EXFILTRATED ASSET PROFILE & TARGETED CAPITAL
Forensic analysis demonstrates deliberate asset selection. The attacker exclusively targeted native SOL, leaving stablecoin holdings and SPL tokens untouched within the exact same compromised wallets.
3. ATTACK VELOCITY & CHRONOLOGICAL SWEEP
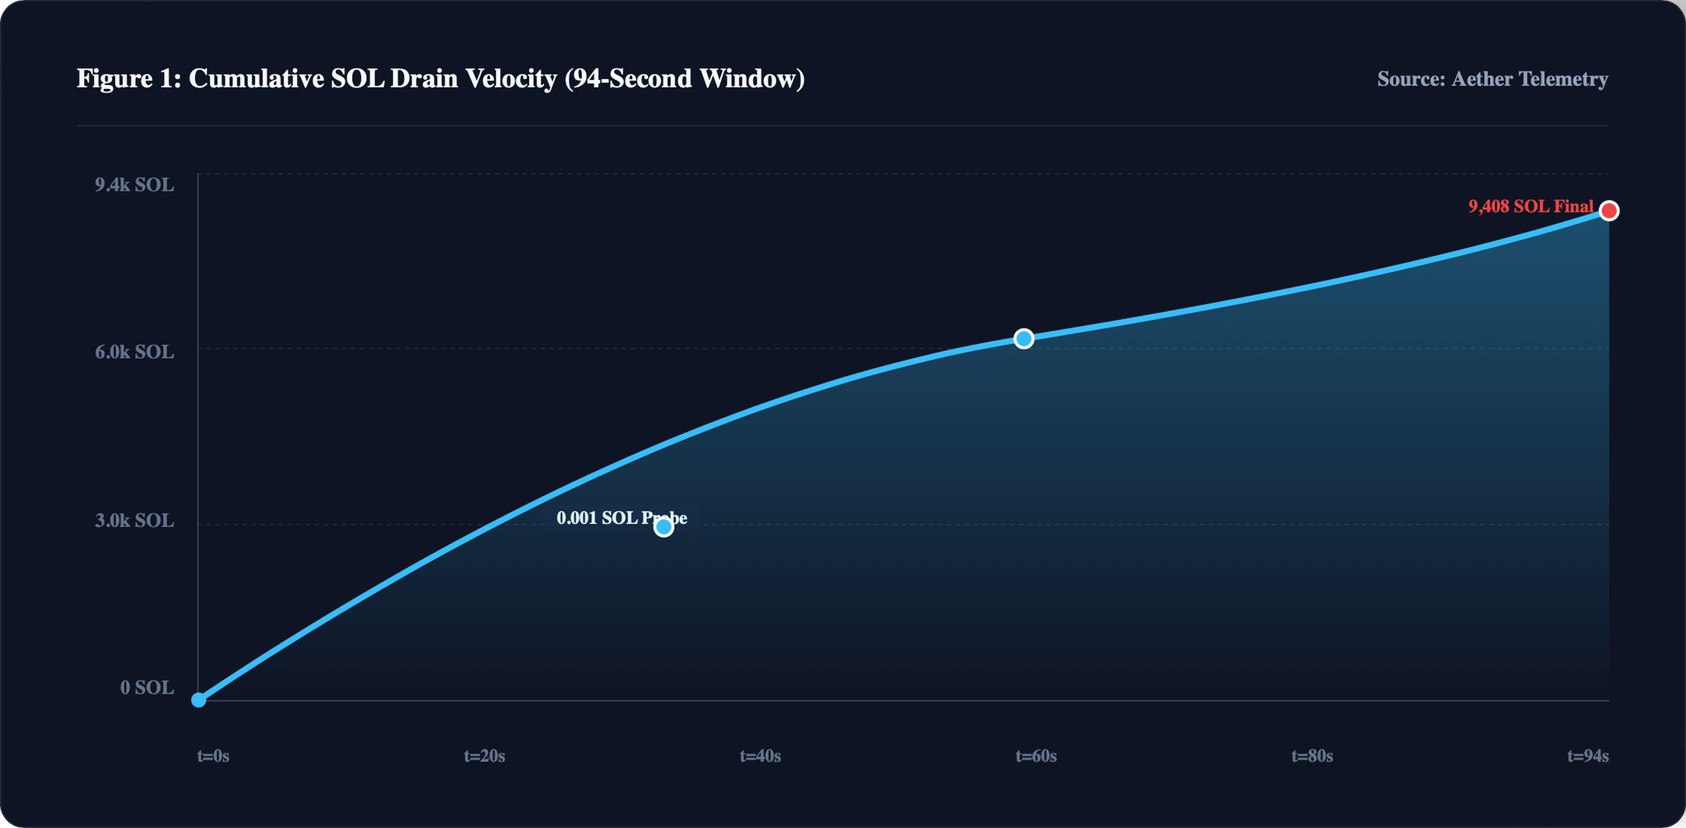
The exploit executed as a single, coordinated script sweep lasting exactly 94 seconds. Prior to initiating the main balance transfer, the script submitted a $0.001 SOL test transaction per wallet cluster to confirm signature authority. Upon confirmation, the main loop drained accounts in descending order of value to maximize capital recovery before mitigation efforts could occur.
ON-CHAIN KEY COMPROMISE INDICATORS
Target selection provided key intelligence regarding the exploit vector. Multiple drained accounts belonged to traders who had discontinued activity on Bloom months prior, including accounts dormant since early 2025. This pattern confirms that active user sessions were not hijacked; rather, historical database stores or Cloud key management vaults were exfiltrated offline.
LAUNDERING ARCHITECTURE & NODE ALLOCATION
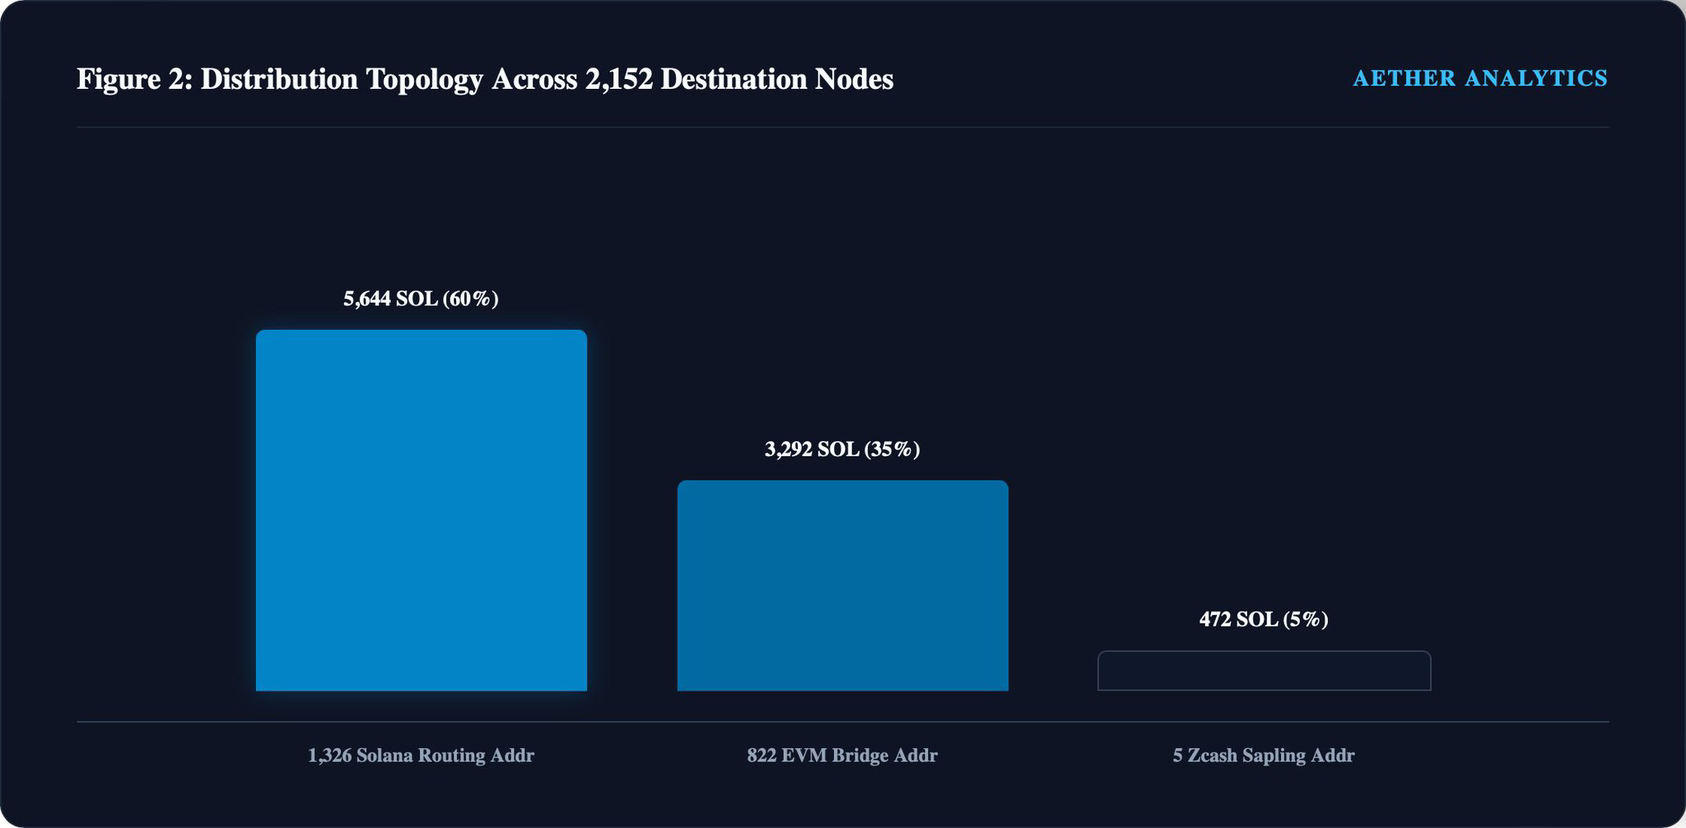
Following exfiltration into primary collection wallet 7kY8qx...p8BQ, stolen capital was divided into an automated distribution framework spanning 2,152 target nodes across three functional sectors.
SECTOR DISTRIBUTION MECHANICS
• Solana Routing Layer (1,326 Addresses): Utilized automated split-and-merge scripts to break continuous transaction tracking.
• EVM Cross-Chain Bridge Layer (822 Addresses): Converted SOL via cross-chain protocols toward #Ethereum #ARBİTRUM , and #bnb Chain destinations.
Zcash Privacy Layer (5 Addresses): Bridged capital into Zcash, depositing at least 26.099 ZEC into Sapling shielded pools.
ZCASH SAPLING ZERO-KNOWLEDGE OBFUSCATION
The most sophisticated element of the post-exploit strategy was the conversion into Zcash and insertion into the Sapling Shielded Pool.
Technical Breakdown: Sapling Pool Obfuscation
The Sapling pool leverages zk-SNARKs (Zero-Knowledge Succinct Non-Interactive Arguments of Knowledge) to construct shielded transactions. While transparent addresses (t-addresses) leave visible inputs and outputs on-chain, Sapling shielded addresses (z-addresses) encrypt transaction values, sender identities, and receiver addresses. By parking 26.099 ZEC in Sapling, the attacker severed public linkability, preventing off-chain surveillance engines from tracing subsequent withdrawal destinations without private viewing keys.
STRATEGIC SECURITY RECOMMENDATIONS FOR BOT OPERATORS
The Bloom exploit highlights structural risks in server-side custodial trading bots. Aether Desk outlines key architectural requirements for future algorithmic trading tools:
Eliminate Full Key Storage:
Transition away from storing master private keys on server databases. Implement Solana Session Keys with strict spending limits and auto-expiration timers.
Isolate Operational Capital:
Cap active trading bot wallet balances strictly to operational operational minimums. Maintain core reserves in isolated cold storage hardware.
CONCLUSION & REMEDIATION STATUS
Bloom Trading management has taken compromised backend services offline, patched internal module vulnerabilities, and pledged a 100% full reimbursement to affected traders. Aether Terminal will continue monitoring unshielded destination nodes across the EVM and Solana routing layers.
Why $EVAA pumping want to know ? Stay tunned