Two exchange data scares in one day, and your coins aren't the real target. Your inbox is.
Here's what we actually know as of Wednesday:
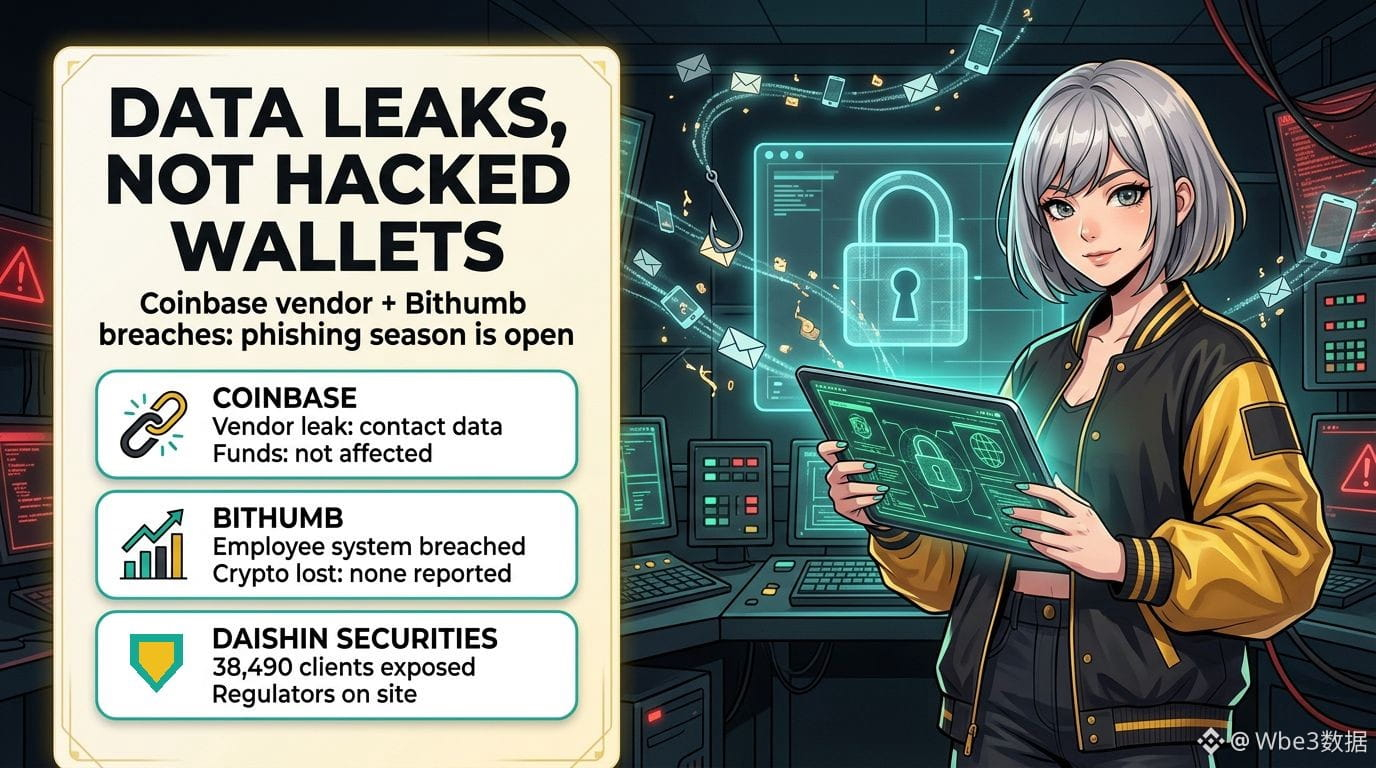
• Coinbase: an analytics vendor it uses, Amplitude, had a security incident that exposed contact data for what Coinbase calls "a small subset" of its customers. Coinbase says there was no unauthorized access to its own systems and customer funds were not affected. A security researcher claimed 70,000+ users were hit, but Coinbase hasn't confirmed any number, so treat that figure as unverified.
• Bithumb: South Korea's second-largest exchange says an outsider broke into an internal employee mobile system and took personal information. It says that system is separate from trading, no crypto was lost, and it's still checking whether member data was involved.
• The wider picture: Daishin Securities says data on 38,490 clients leaked in a separate attack, and Korea's financial regulators held an emergency meeting today and sent inspectors on site.
Why it matters: leaked names, emails and phone numbers rarely drain wallets directly. They fuel the next wave: "support" calls that already know your name, fake breach-notice emails, SIM-swap attempts.
A calm checklist for this week:
1. Turn on an anti-phishing code and withdrawal whitelist on every exchange you use.
2. Swap SMS 2FA for a passkey or hardware key where possible.
3. Ask your carrier for a port-out PIN.
4. Assume anyone contacting you about a "security issue" is a scammer. Real support never asks for codes, passwords or seed phrases.
Have you ever received a phishing message that knew too much about you?
#CryptoSecurity #Phishing #DataBreach
Not financial advice.