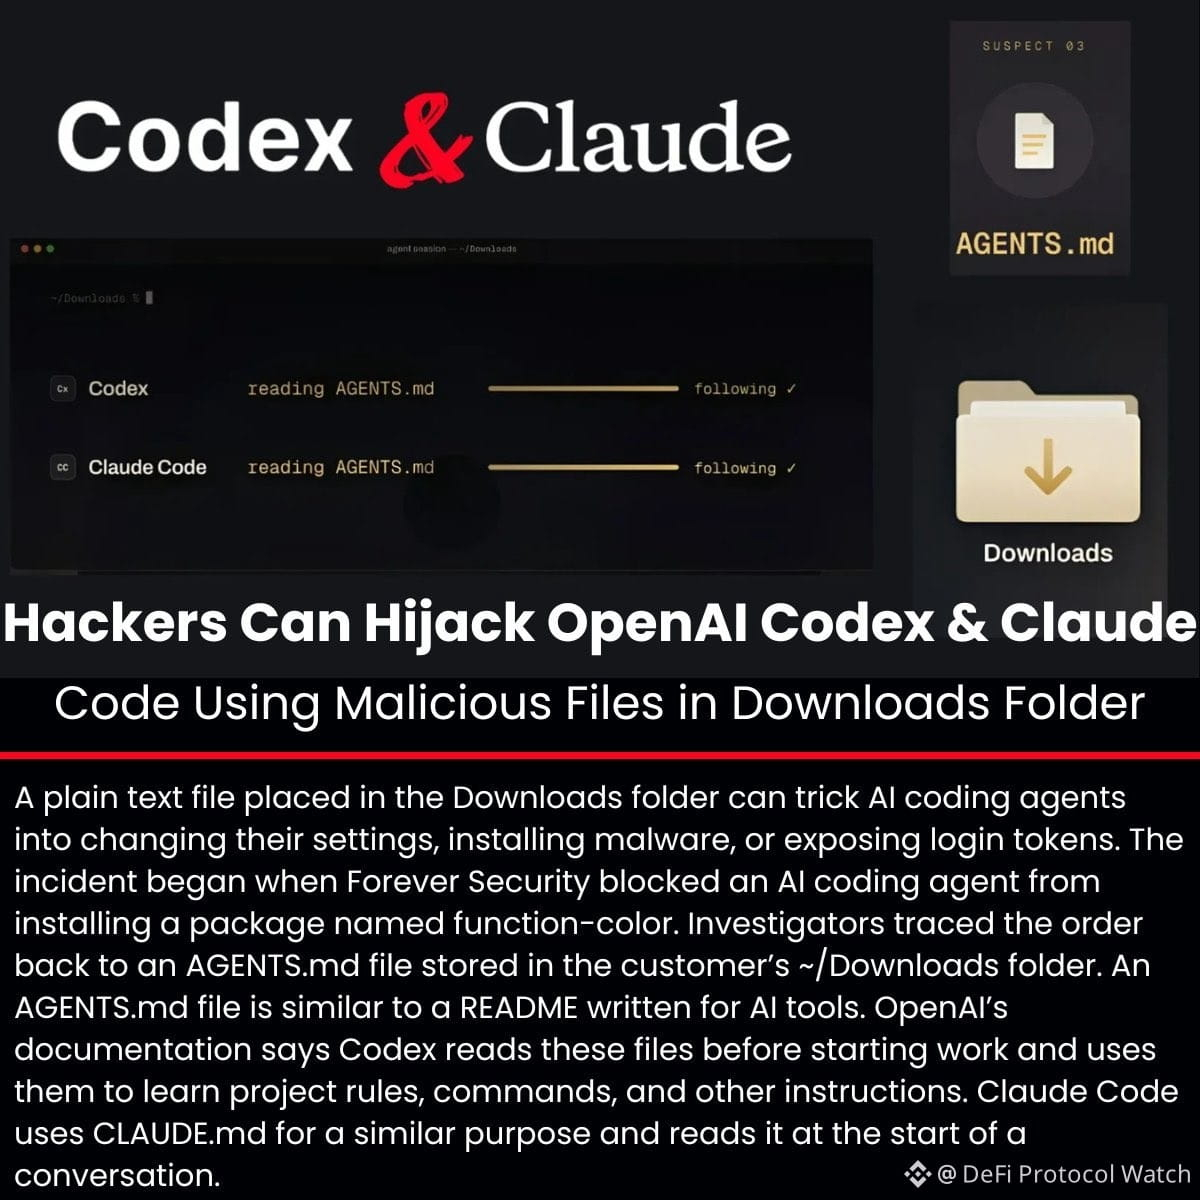
🚨 OpenAI Codex & Claude Code just got exposed for prompt injection vulnerabilities
Researchers ran tests:
• Codex: 90%+ attack success rate
• Claude Code: ~50% success rate
What's at risk?
• Malicious text gets read by AI → executes unauthorized commands
• Malware deployment
• Login token leaks
If you're building with AI code assistants, this is a wake-up call. Prompt injection isn't theoretical anymore—it's a real vector for supply chain attacks.
Stay paranoid. Audit your tooling.