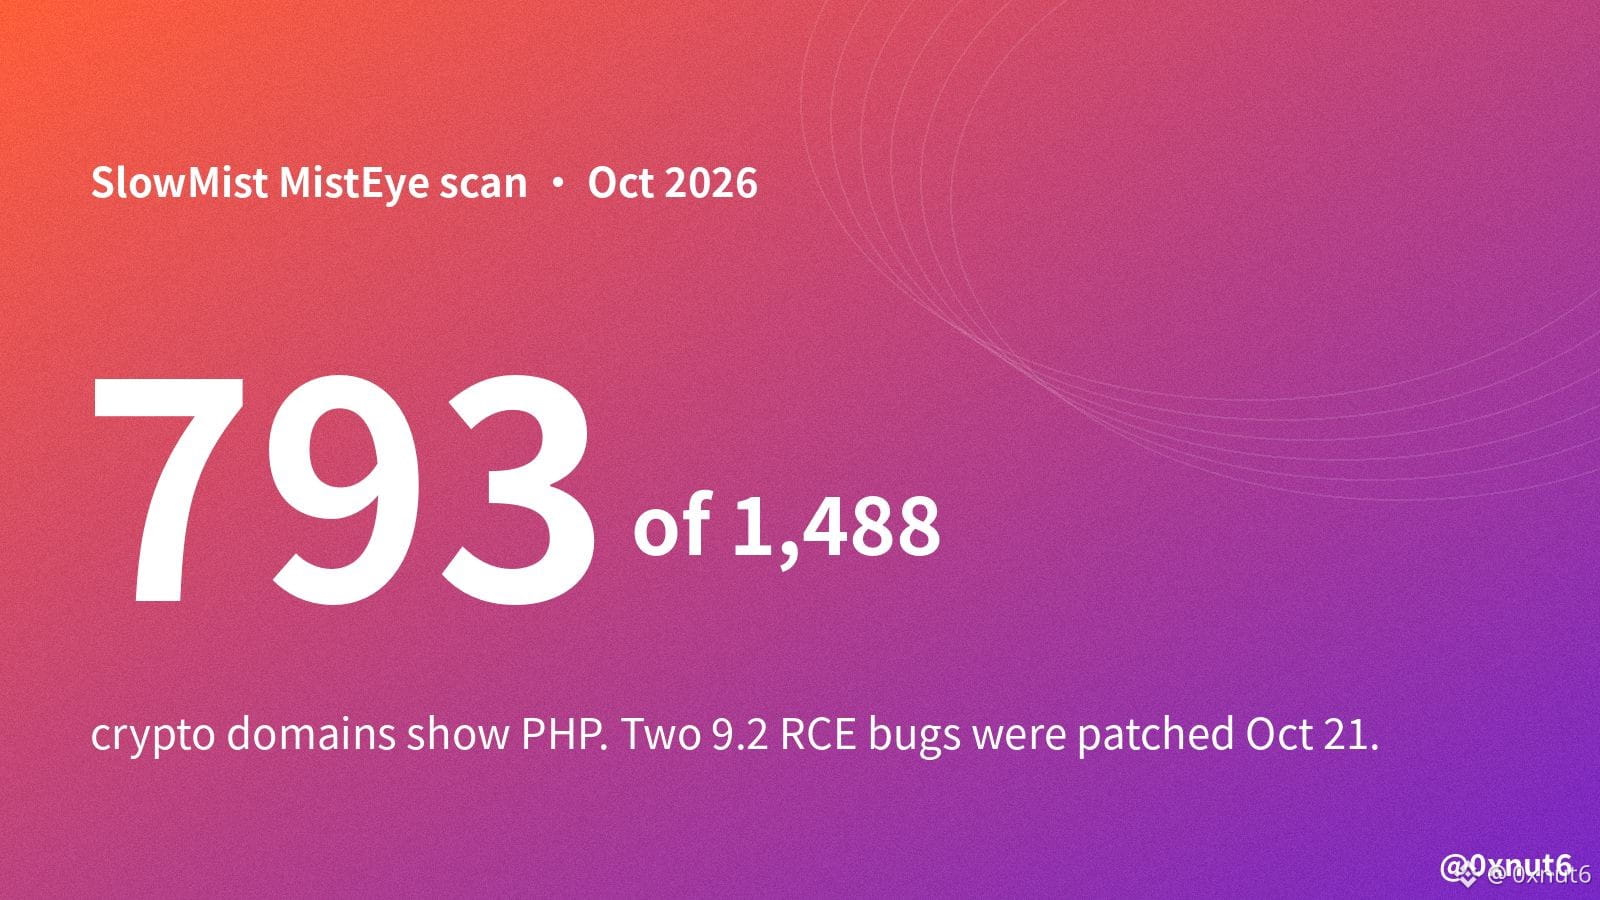
SlowMist scanned 1,488 crypto domains and found PHP on 793 of them. This week PHP patched two bugs that let a stranger run code on a web server without logging in.
Both are rated 9.2 and sit in memory management and error handling, code that nearly every request touches. On Apache with mod_php, one unauthenticated request can trigger the first bug before any app code runs. Fixes shipped Oct 21, but PHP 8.1 and older are end-of-life and get no official release, so those servers depend on a distro backport or an upgrade.
Users can get hurt even when no smart contract breaks, because an attacker who owns the web server can change what the page asks your wallet to sign. @SlowMist_Team flags swapped recipient addresses, swapped token approvals and stolen API keys that might reach a hot wallet. BadgerDAO lost about $120M to this kind of front-end tampering in December 2021, although the attacker got in through a stolen Cloudflare API key rather than PHP. Its contracts held up, while a script injected into the front end slipped extra approvals into normal deposits.
PHP on a domain doesn't mean that site is vulnerable. @PancakeSwap says it runs no PHP at all, and @binance says it had safeguards in place before the patch. PHP also disclosed a third bug on Oct 23. It only hits an unusual session setup and one config switch blocks it, so there's no emergency release, but teams still have cleanup left to do.
What I'd do this week:
- read the spender and amount on every approval, even on sites you use daily
- treat a sudden "re-approve" or "migrate" prompt as a warning sign
- revoke old unlimited approvals you don't need
Both are rated 9.2 and sit in memory management and error handling, code that nearly every request touches. On Apache with mod_php, one unauthenticated request can trigger the first bug before any app code runs. Fixes shipped Oct 21, but PHP 8.1 and older are end-of-life and get no official release, so those servers depend on a distro backport or an upgrade.
Users can get hurt even when no smart contract breaks, because an attacker who owns the web server can change what the page asks your wallet to sign. @SlowMist_Team flags swapped recipient addresses, swapped token approvals and stolen API keys that might reach a hot wallet. BadgerDAO lost about $120M to this kind of front-end tampering in December 2021, although the attacker got in through a stolen Cloudflare API key rather than PHP. Its contracts held up, while a script injected into the front end slipped extra approvals into normal deposits.
PHP on a domain doesn't mean that site is vulnerable. @PancakeSwap says it runs no PHP at all, and @binance says it had safeguards in place before the patch. PHP also disclosed a third bug on Oct 23. It only hits an unusual session setup and one config switch blocks it, so there's no emergency release, but teams still have cleanup left to do.
What I'd do this week:
- read the spender and amount on every approval, even on sites you use daily
- treat a sudden "re-approve" or "migrate" prompt as a warning sign
- revoke old unlimited approvals you don't need