🚨 $235K Stolen in 48 Hours: The Trojan Hijacking Active Sessions
A stealthy malware attack has drained over $235K across hundreds of crypto wallets in just 48 hours. 💻⚠️
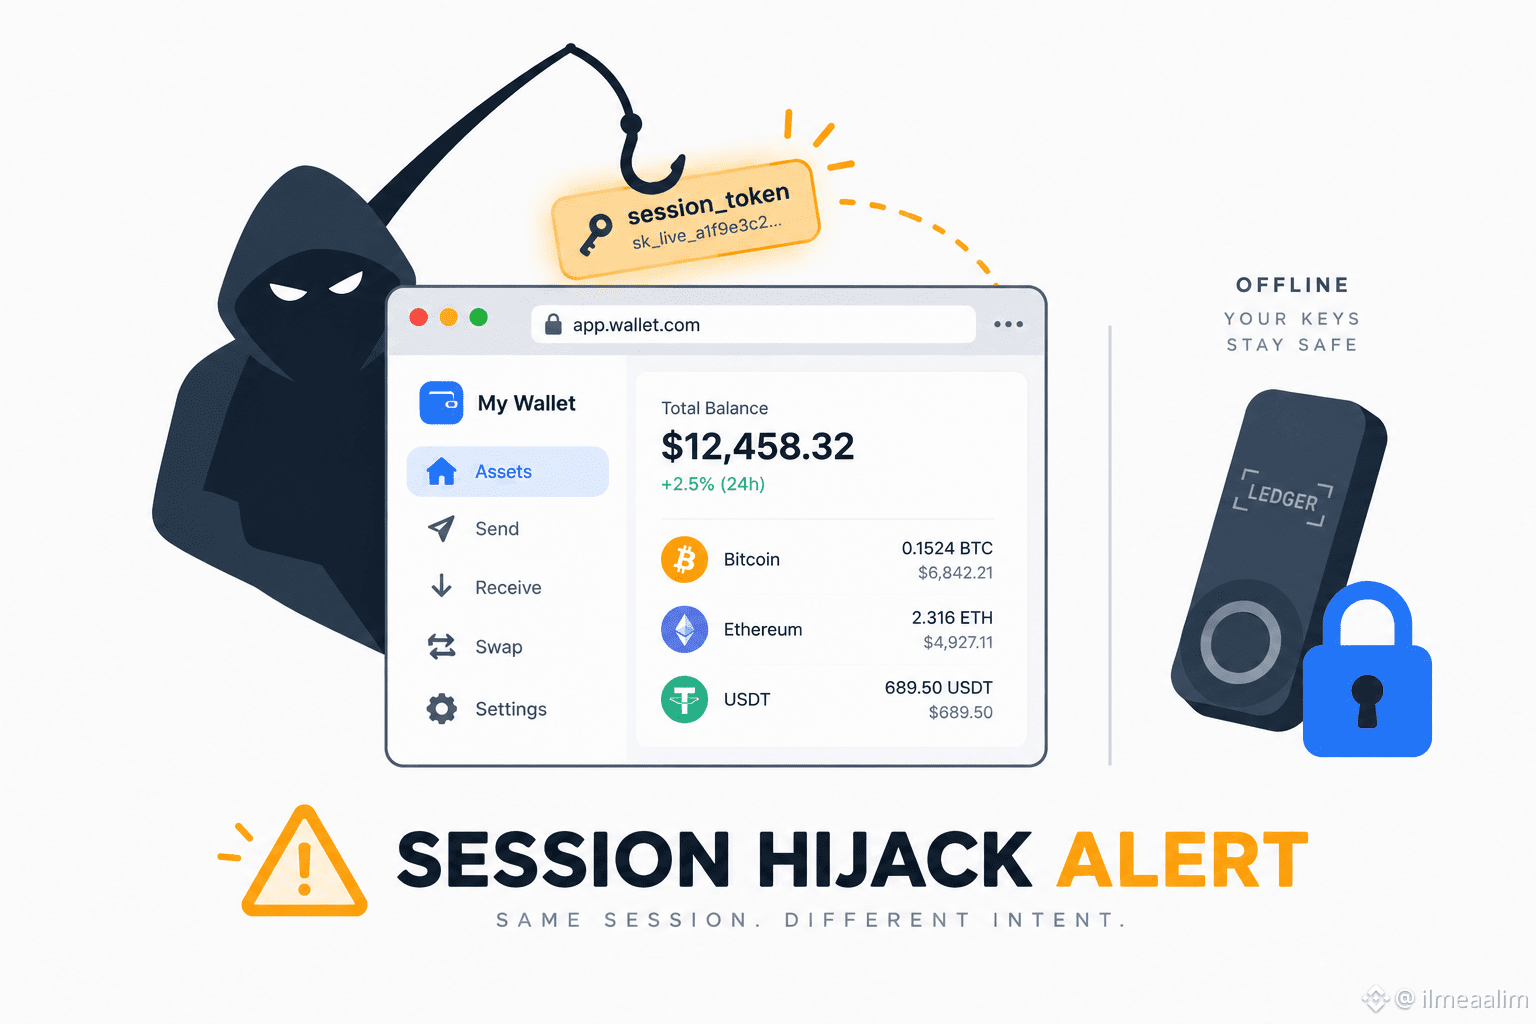
This remote access trojan targets active browser sessions on hot wallets and exchanges. Attackers do not need your private keys or seed phrase. If an exchange or web wallet tab is already logged in on an infected machine, the malware steals the live session token and signs transfers directly. 🔓
Most stolen assets were converted into $USDC and concentrated into a single attacker wallet address:
0x7028174ED69A237DE0791101b5b85D1E6Db35887 📦
Reports from Coin Bureau note the delivery vector is still unconfirmed, with malicious extensions and fake updates suspected. 🛡️
Essential defense steps:
🔹 Move large balances to offline hardware wallets.
🔸 Log out of exchange tabs immediately after use.
🔹 Use hardware keys like a YubiKey for withdrawals.
Do you log out of your wallet tabs after trading? 👇
#CryptoSecurity #CyberSecurity #USDC #Web3
A stealthy malware attack has drained over $235K across hundreds of crypto wallets in just 48 hours. 💻⚠️
This remote access trojan targets active browser sessions on hot wallets and exchanges. Attackers do not need your private keys or seed phrase. If an exchange or web wallet tab is already logged in on an infected machine, the malware steals the live session token and signs transfers directly. 🔓
Most stolen assets were converted into $USDC and concentrated into a single attacker wallet address:
0x7028174ED69A237DE0791101b5b85D1E6Db35887 📦
Reports from Coin Bureau note the delivery vector is still unconfirmed, with malicious extensions and fake updates suspected. 🛡️
Essential defense steps:
🔹 Move large balances to offline hardware wallets.
🔸 Log out of exchange tabs immediately after use.
🔹 Use hardware keys like a YubiKey for withdrawals.
Do you log out of your wallet tabs after trading? 👇
#CryptoSecurity #CyberSecurity #USDC #Web3