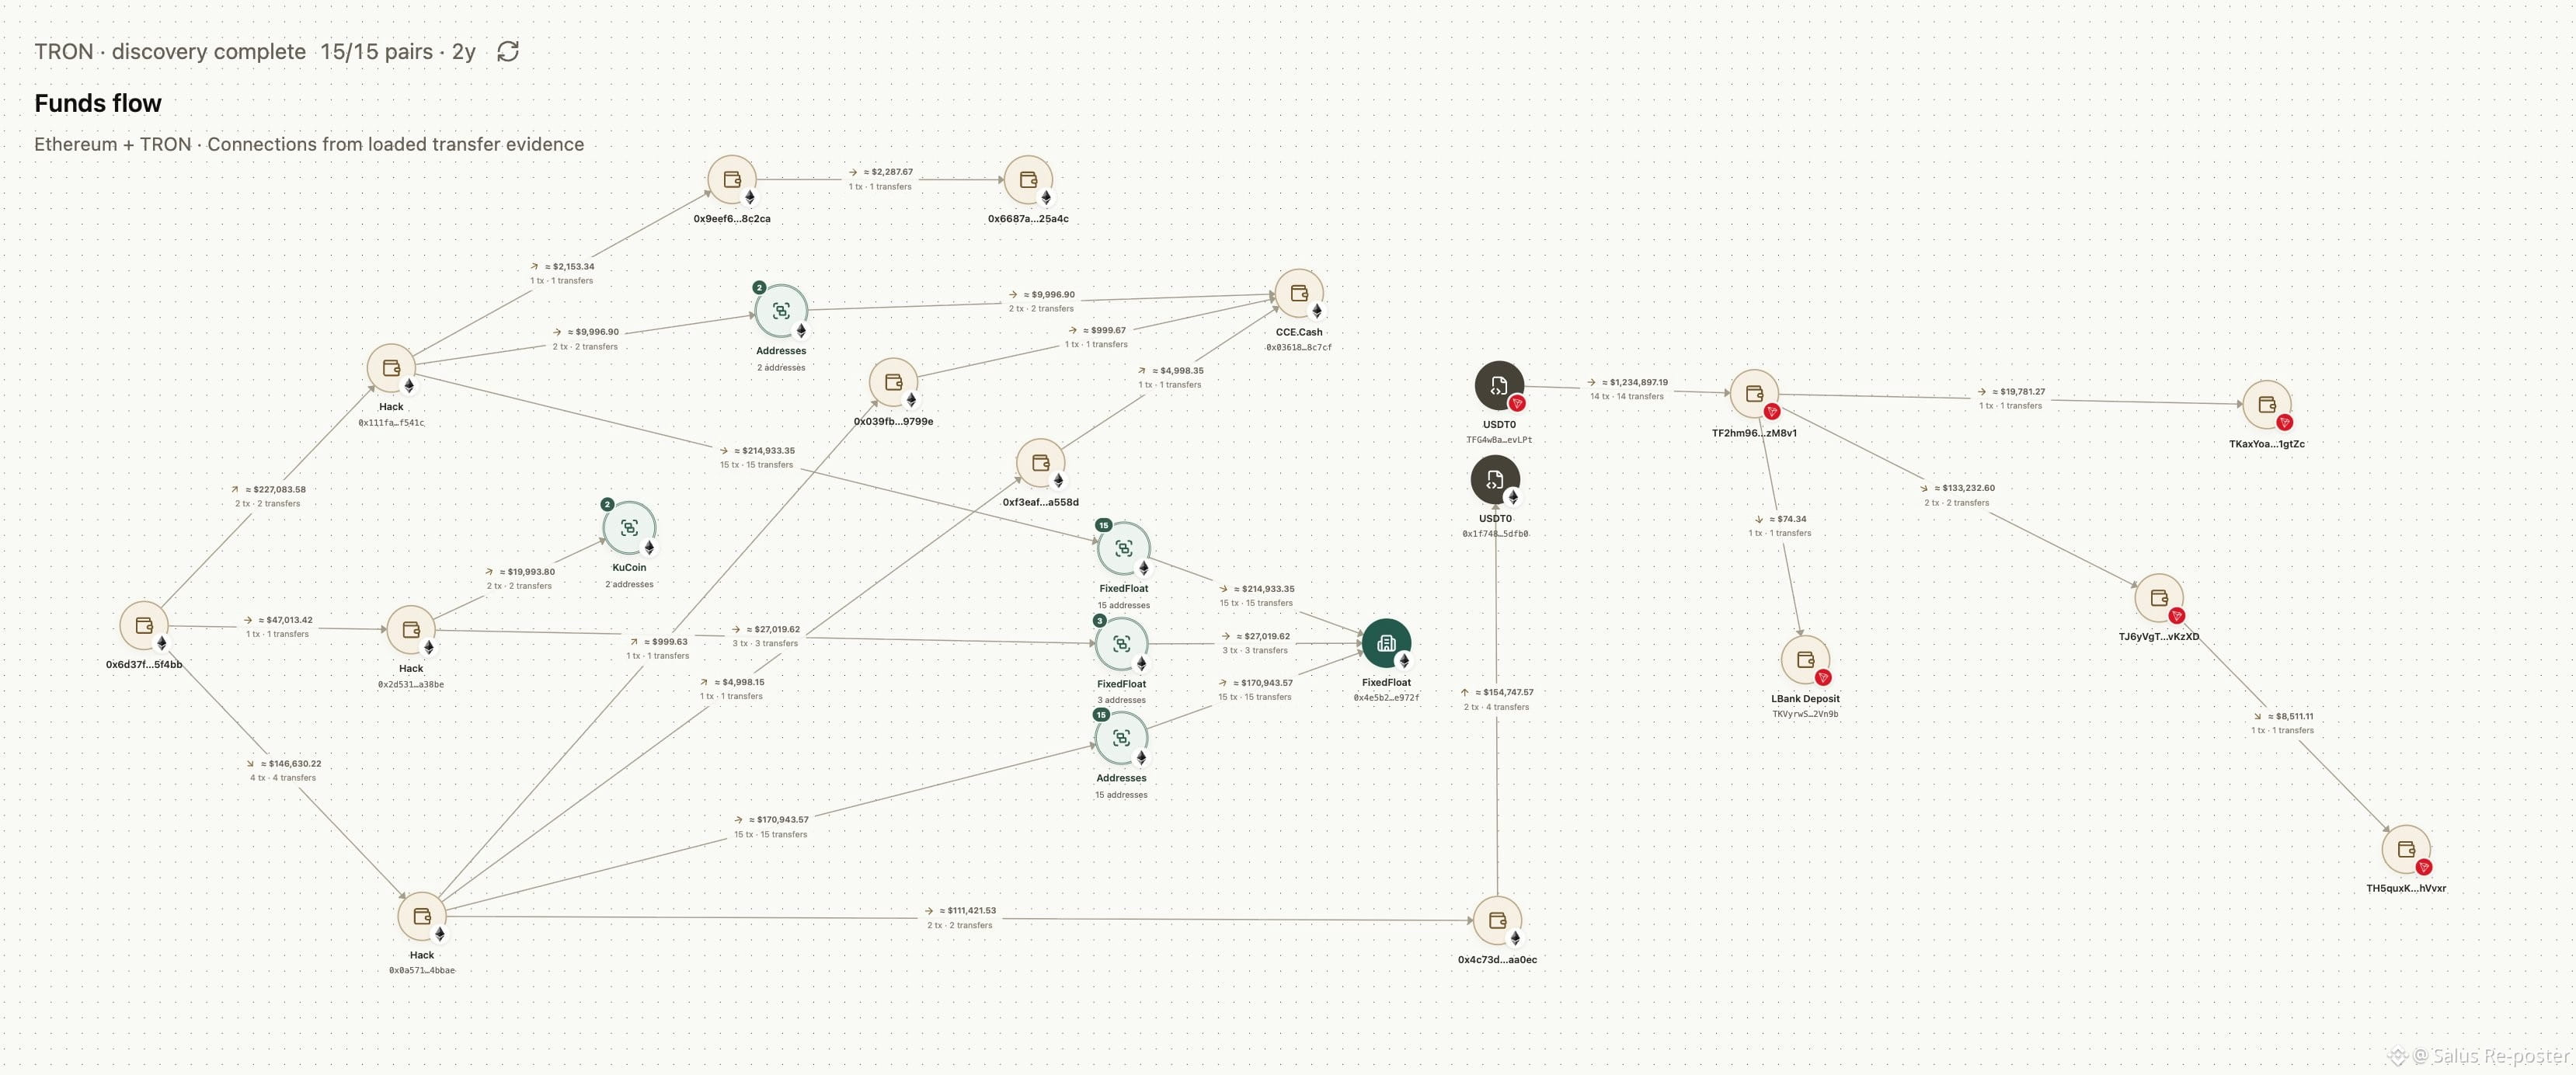
Our ongoing analysis of the FomoPeek situation reveals that the confirmed attacker wallet is 0x6d37f2C5e8F8546b648D317295565dA95975f4BB. During this event, the perpetrators managed to acquire an estimated total of approximately 579,900 USDT. Digging into the background of the group behind this breach, we discovered their previous involvement in a private-key theft case back in June. At this time, our team is still actively investigating whether they employed that exact same methodology for this latest exploit.
The unauthorized funds were subsequently moved outward through three primary channels. A substantial portion was directed via the FixedFloat route, which successfully processed a total of 401,028 USDT. To achieve this, the attackers split the capital across three intermediary wallets. Specifically, 215,000 USDT was routed through 0x111faeb95cd0786593433bcc762dc5c1debf541c, while 159,000 USDT flowed through 0x0df6ac2e2856114228756947d1b1d9ff63ea3e68. A third address, 0x2d53113c89c83c520c17b8bbcdc22aa0518a38be, handled the remaining 27,028 USDT for this specific pathway.
That same address, 0x2d53113c89c83c520c17b8bbcdc22aa0518a38be, played a role in the second major channel, which targeted KuCoin. From that wallet, a sum of 20,000 USDT was initiated in two separate 10,000 USDT transactions. These assets traveled through a pair of deposit addresses before finally being pooled together into a KuCoin hot wallet.
The third and final transfer channel involved an escrow platform. In this phase, 111,458.3085 USDT was transmitted through the wallet 0x4c73d7e8ef0e61129403e219debc597fd43aa0ec before arriving at destinations tied to the escrow service. In addition, 10,000 USDT was sent into the CCE mixing service via 0x0361897d757d13a4afad64a2e1bc561b96a8c7cf, which subsequently routed the assets to addresses also associated with that same escrow platform.
Moving forward, we are carrying out a highly comprehensive trace to track all remaining addresses associated with this incident.
The unauthorized funds were subsequently moved outward through three primary channels. A substantial portion was directed via the FixedFloat route, which successfully processed a total of 401,028 USDT. To achieve this, the attackers split the capital across three intermediary wallets. Specifically, 215,000 USDT was routed through 0x111faeb95cd0786593433bcc762dc5c1debf541c, while 159,000 USDT flowed through 0x0df6ac2e2856114228756947d1b1d9ff63ea3e68. A third address, 0x2d53113c89c83c520c17b8bbcdc22aa0518a38be, handled the remaining 27,028 USDT for this specific pathway.
That same address, 0x2d53113c89c83c520c17b8bbcdc22aa0518a38be, played a role in the second major channel, which targeted KuCoin. From that wallet, a sum of 20,000 USDT was initiated in two separate 10,000 USDT transactions. These assets traveled through a pair of deposit addresses before finally being pooled together into a KuCoin hot wallet.
The third and final transfer channel involved an escrow platform. In this phase, 111,458.3085 USDT was transmitted through the wallet 0x4c73d7e8ef0e61129403e219debc597fd43aa0ec before arriving at destinations tied to the escrow service. In addition, 10,000 USDT was sent into the CCE mixing service via 0x0361897d757d13a4afad64a2e1bc561b96a8c7cf, which subsequently routed the assets to addresses also associated with that same escrow platform.
Moving forward, we are carrying out a highly comprehensive trace to track all remaining addresses associated with this incident.