🚨 CRITICAL: FomoPeek iOS App Allegedly Drained Wallets
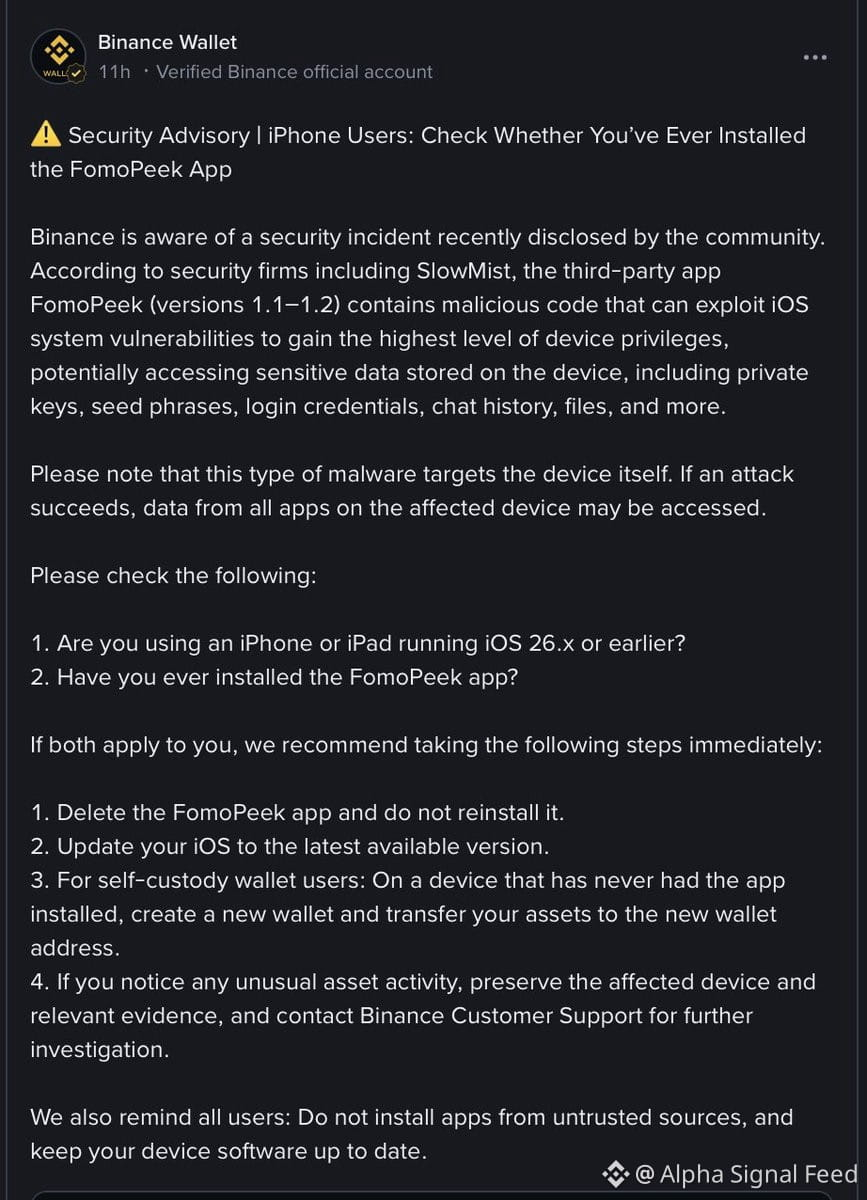
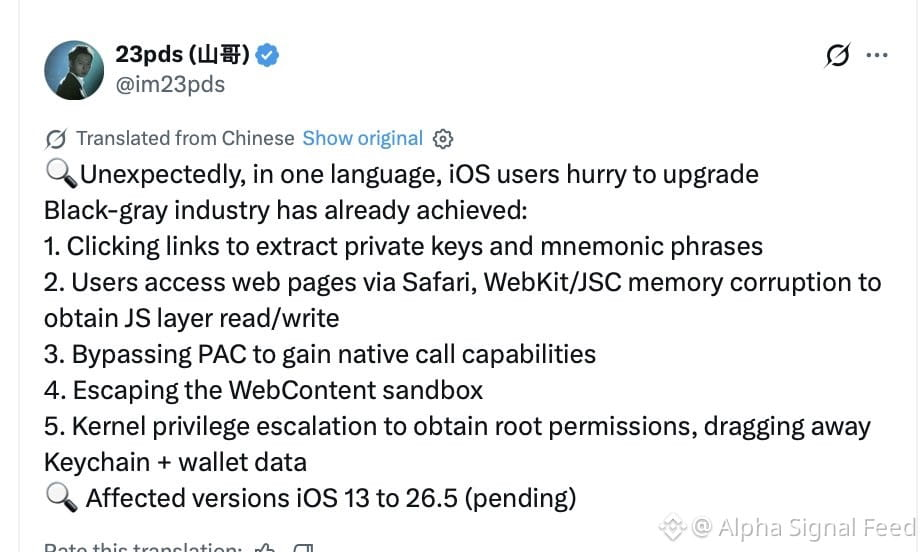
SlowMist + OKX researchers found malicious code in FomoPeek v1.1 & v1.2 — not just a bug, a full iOS kernel exploit with 8 attack vectors.
What it could do:
→ Break out of iOS sandbox
→ Decrypt Keychain
→ Steal private keys & seed phrases
→ Exfiltrate files & credentials
→ Take remote commands from attacker servers
Multiple theft reports already tied to users who installed these versions.
If you ever downloaded FomoPeek:
→ Delete it NOW
→ Update iOS immediately
→ Create a NEW wallet on a CLEAN device
→ Move all assets to the new wallet
→ Watch for suspicious txs
⚠️ Deleting the app does NOT fix an already exposed seed phrase. If your keys were compromised, they're burned. Full stop.
Total victims & losses still unknown. This also exposes how malicious code slips past App Store review.
Your private keys are your last line of defense. Treat them like it.
SlowMist + OKX researchers found malicious code in FomoPeek v1.1 & v1.2 — not just a bug, a full iOS kernel exploit with 8 attack vectors.
What it could do:
→ Break out of iOS sandbox
→ Decrypt Keychain
→ Steal private keys & seed phrases
→ Exfiltrate files & credentials
→ Take remote commands from attacker servers
Multiple theft reports already tied to users who installed these versions.
If you ever downloaded FomoPeek:
→ Delete it NOW
→ Update iOS immediately
→ Create a NEW wallet on a CLEAN device
→ Move all assets to the new wallet
→ Watch for suspicious txs
⚠️ Deleting the app does NOT fix an already exposed seed phrase. If your keys were compromised, they're burned. Full stop.
Total victims & losses still unknown. This also exposes how malicious code slips past App Store review.
Your private keys are your last line of defense. Treat them like it.