

claude opus found a bug in crypto's ~$9B privacy token that could print money out of thin air - and it's fucking scary
zcash had a hidden flaw in its code. it let you create fake zec from nothing - and it was completely invisible. nobody could even tell it happened
and it sat there for 4 years. every top cryptographer looked at zcash, and none of them caught it
then a white hat used claude opus 4.8 + a custom setup and found it in about a day - just days after the model came out. he even built a working version that minted fake coins on a test network
the scary part is because zcash is private, there's no way to 100% prove nobody already used it before the fix
now think about how many other coins have a bug like this just sitting there waiting
how it actually worked: zcash hides every transaction behind a math proof that basically says "i own this coin and i'm spending it" - without revealing anything else
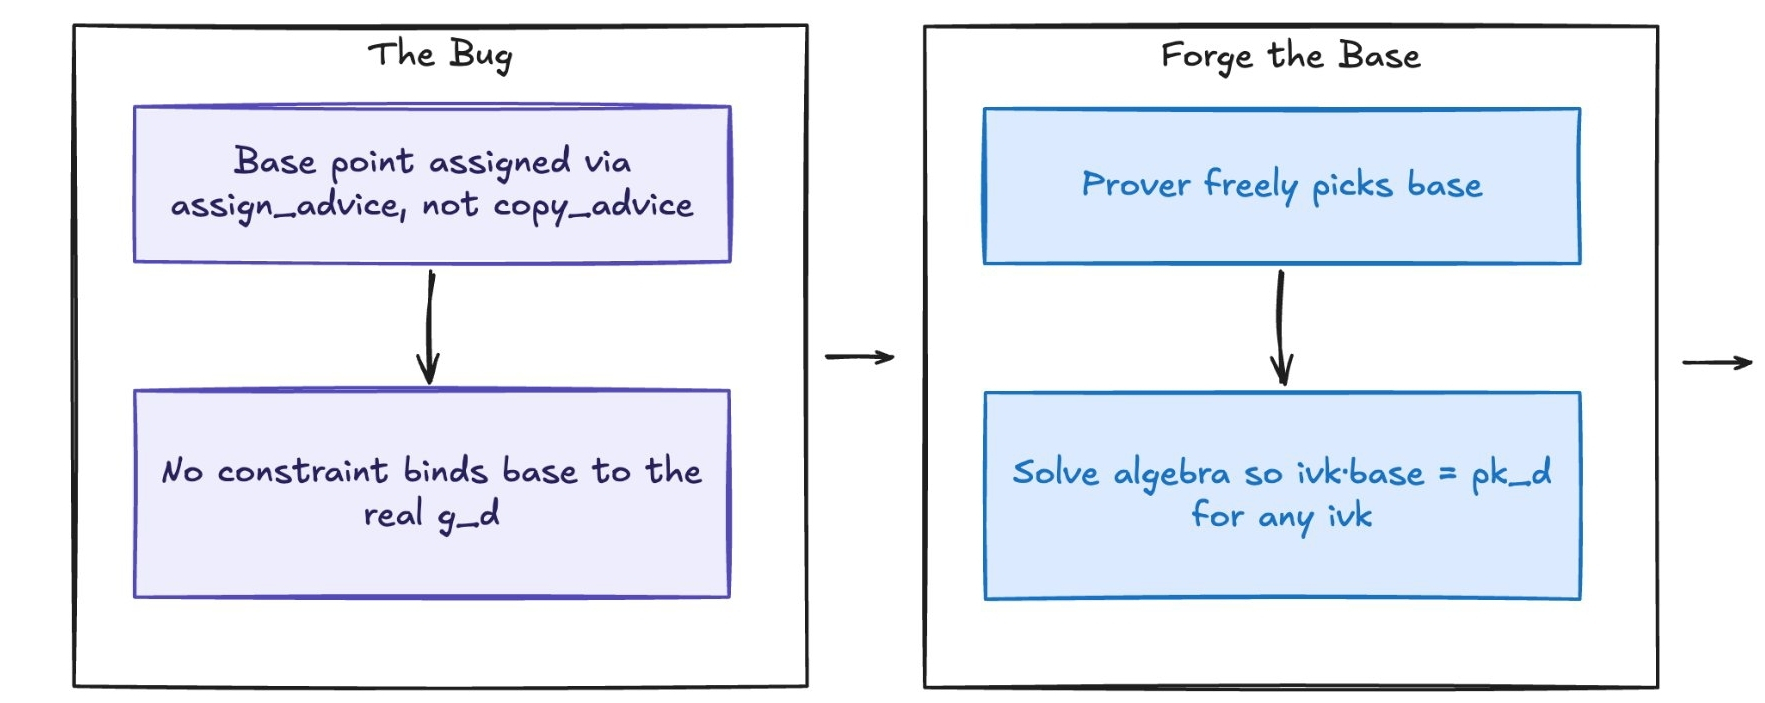
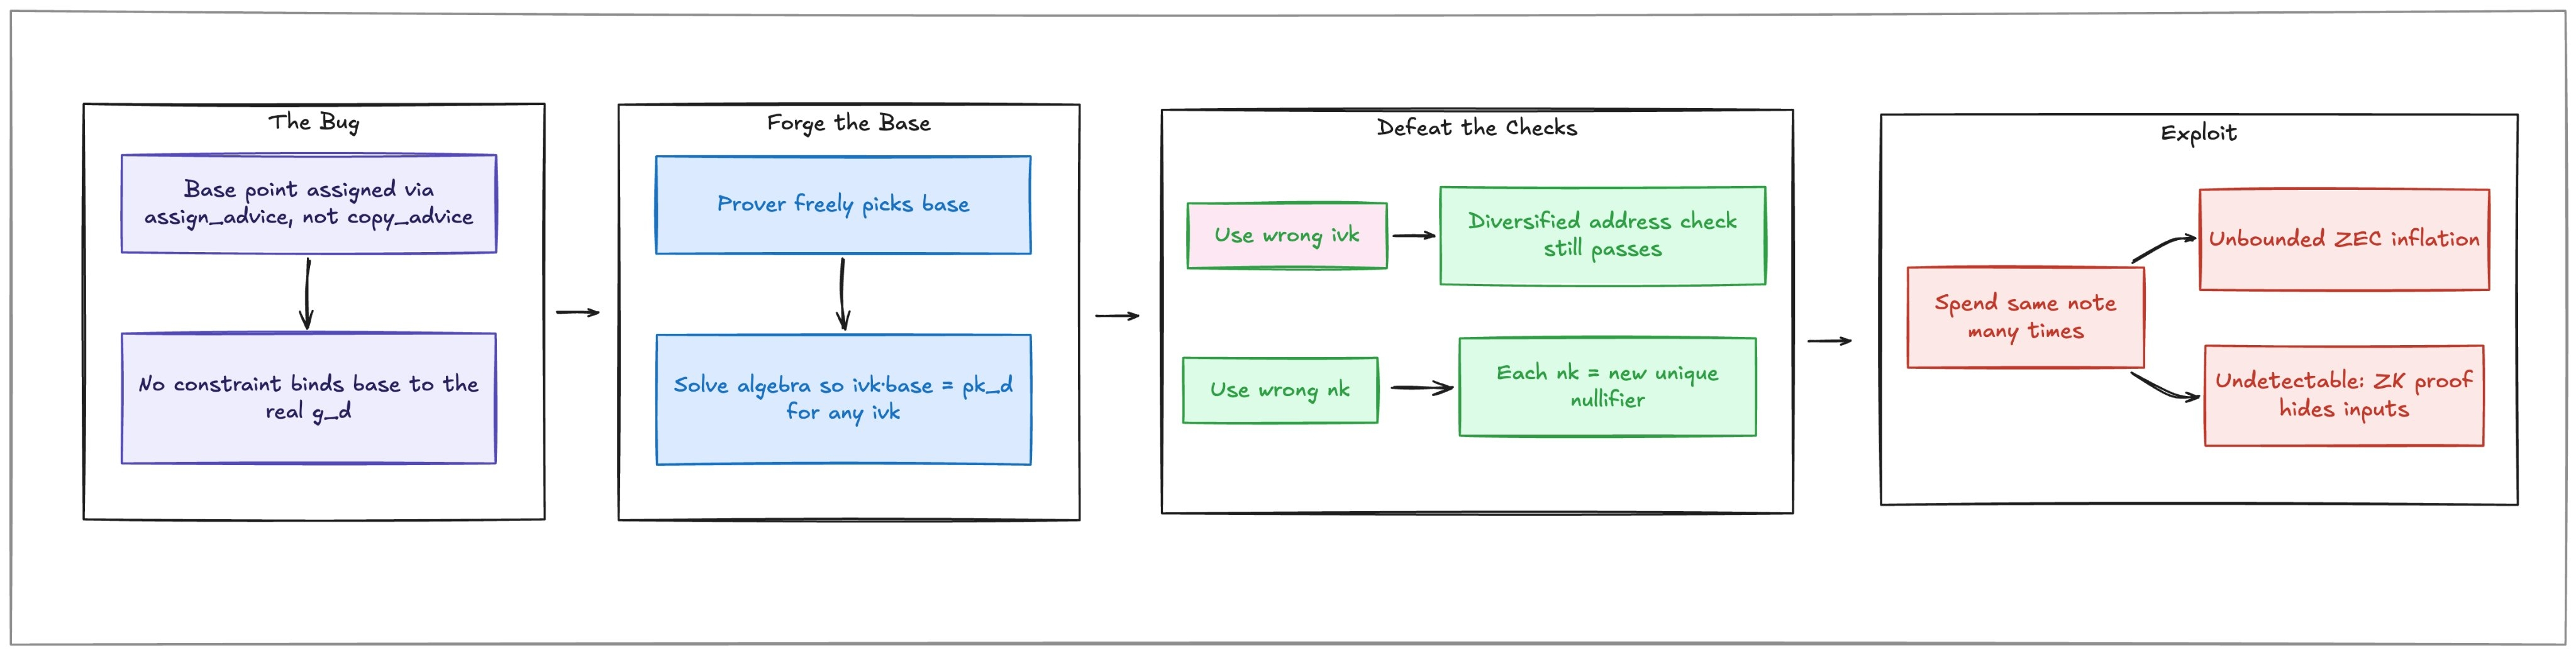
one step of that proof multiplies secret numbers on an elliptic curve to confirm your key matches the coin. the bug was that step never locked in which number you had to start with
so an attacker could quietly swap in a fake number, and the proof would still "check out" - even for a coin that was never theirs
once that check was fooled, they could spend the same coin again and again, each time stamping it with a fresh "spent" marker so the network saw a brand-new coin every time
zec conjured from nothing, fully encrypted, completely invisible. nobody watching the chain could even tell it happened
the fix was an emergency network upgrade. no evidence it was ever exploited - but no way to fully prove it wasn't