
#gnosispay
gnosispay
21,852 Aufrufe
58 Kommentare
Hot
Zuletzt

·
--
Übersetzung ansehen
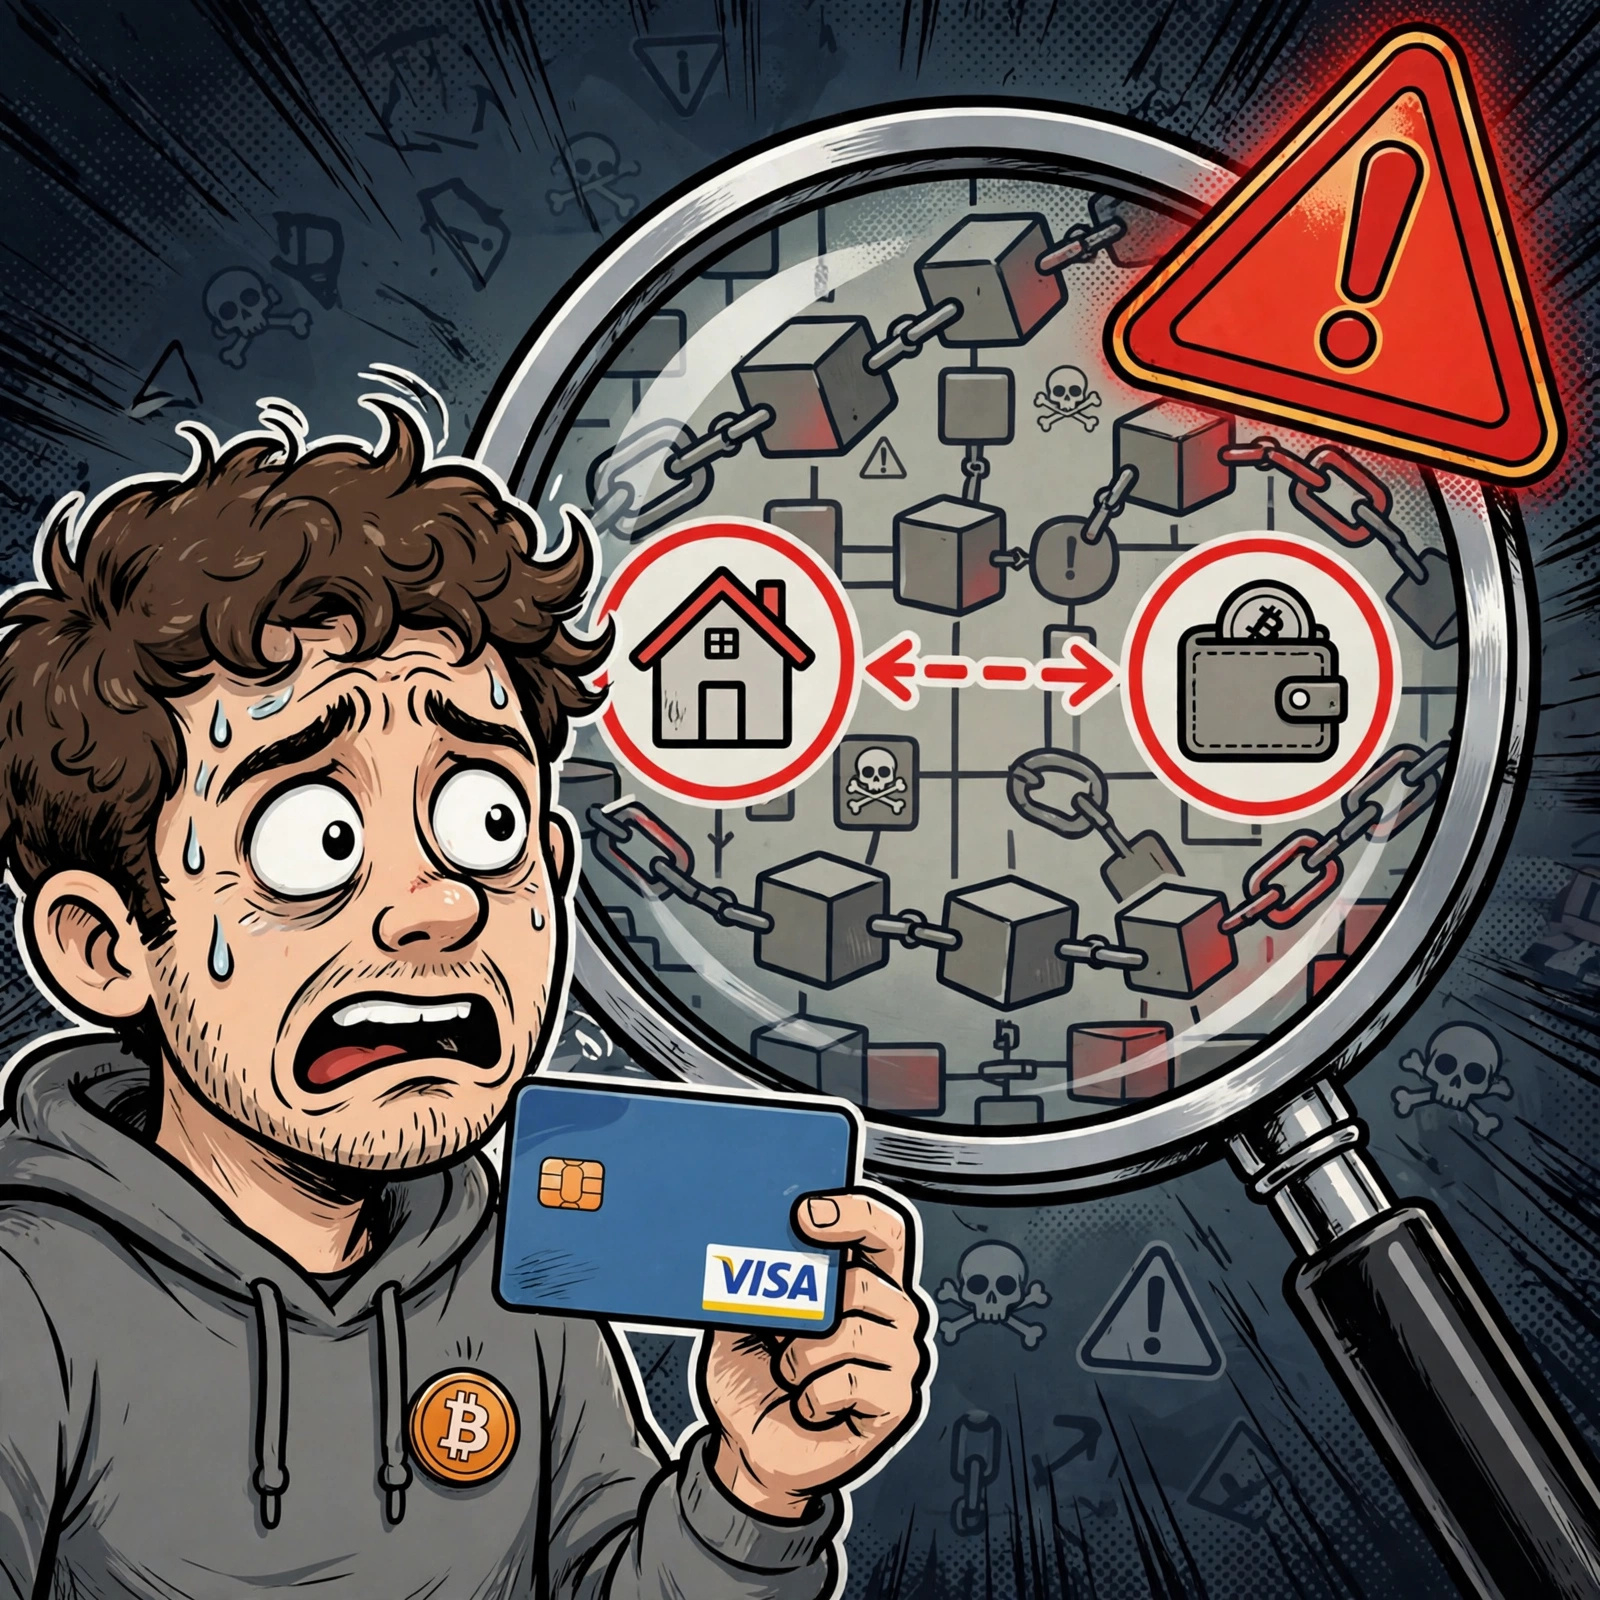
出大事了:Gnosis Pay 刚官宣数据泄露,11 月 3 日就被黑了,卡号、有效期、CVV、家庭住址全漏了,最要命的是钱包地址也被扒出来——名字、住址和链上资产直接对上号。好在资金没动,涉事卡已经注销,这块业务 12 月 20 号就关停。用过这张卡的兄弟赶紧查邮件,接下来钓鱼邮件肯定满天飞,助记词、PIN 谁要都别给。你用过加密借记卡吗?
#GnosisPay #数据泄露 #加密安全 #黑客攻击 #钱包安全
出大事了:Gnosis Pay 刚官宣数据泄露,11 月 3 日就被黑了,卡号、有效期、CVV、家庭住址全漏了,最要命的是钱包地址也被扒出来——名字、住址和链上资产直接对上号。好在资金没动,涉事卡已经注销,这块业务 12 月 20 号就关停。用过这张卡的兄弟赶紧查邮件,接下来钓鱼邮件肯定满天飞,助记词、PIN 谁要都别给。你用过加密借记卡吗?
#GnosisPay #数据泄露 #加密安全 #黑客攻击 #钱包安全
#GnosisPay #数据泄露 #加密安全 #黑客攻击 #钱包安全
10
Übersetzung ansehen
Gnosis Pay has disclosed a breach of the legacy system behind its branded consumer cards. The company says it detected unauthorised access on Nov. 3 and publicly disclosed it on Nov. 6 at 14:32 UTC. It says containment began within two hours, affected credentials were replaced and the vulnerability was addressed.
Gnosis Pay says the incident exposed certain customer information, while its white-label enterprise platform and customer funds were unaffected. Those are the company’s statements; no independent wallet-balance audit was reported. The number of affected customers, full data fields and technical cause have not been disclosed.
If you use the card, follow the account-specific notice and stay alert for personalized phishing. Open the official app directly; never share a seed phrase, private key, PIN or full card number in a message.
What matters most in a breach disclosure: clear scope, a credible timeline or independent verification?
Sources: [Gnosis Pay’s notice](https://gnosispay.com/blog/data-breach-legacy-system-gnosis-pay-branded-cards) · [DeFiPrime](https://defiprime.com/gnosis-pay-legacy-card-data-breach) · [The Defiant](https://thedefiant.io/news/security/gnosis-pay-confirms-breach-of-consumer-card-system)
Conclusion: $GNO — [Binance GNO/USDT Spot chart](https://www.binance.com/en/trade/GNO_USDT?type=spot) for the Gnosis ecosystem token; it is not a measure of this card incident. Check the chart for yourself, do your own research, and trade responsibly. #GnosisPay #GNO #CryptoSecurity #DataBreach
Gnosis Pay has disclosed a breach of the legacy system behind its branded consumer cards. The company says it detected unauthorised access on Nov. 3 and publicly disclosed it on Nov. 6 at 14:32 UTC. It says containment began within two hours, affected credentials were replaced and the vulnerability was addressed.
Gnosis Pay says the incident exposed certain customer information, while its white-label enterprise platform and customer funds were unaffected. Those are the company’s statements; no independent wallet-balance audit was reported. The number of affected customers, full data fields and technical cause have not been disclosed.
If you use the card, follow the account-specific notice and stay alert for personalized phishing. Open the official app directly; never share a seed phrase, private key, PIN or full card number in a message.
What matters most in a breach disclosure: clear scope, a credible timeline or independent verification?
Sources: [Gnosis Pay’s notice](https://gnosispay.com/blog/data-breach-legacy-system-gnosis-pay-branded-cards) · [DeFiPrime](https://defiprime.com/gnosis-pay-legacy-card-data-breach) · [The Defiant](https://thedefiant.io/news/security/gnosis-pay-confirms-breach-of-consumer-card-system)
Conclusion: $GNO — [Binance GNO/USDT Spot chart](https://www.binance.com/en/trade/GNO_USDT?type=spot) for the Gnosis ecosystem token; it is not a measure of this card incident. Check the chart for yourself, do your own research, and trade responsibly. #GnosisPay #GNO #CryptoSecurity #DataBreach
Gnosis Pay says the incident exposed certain customer information, while its white-label enterprise platform and customer funds were unaffected. Those are the company’s statements; no independent wallet-balance audit was reported. The number of affected customers, full data fields and technical cause have not been disclosed.
If you use the card, follow the account-specific notice and stay alert for personalized phishing. Open the official app directly; never share a seed phrase, private key, PIN or full card number in a message.
What matters most in a breach disclosure: clear scope, a credible timeline or independent verification?
Sources: [Gnosis Pay’s notice](https://gnosispay.com/blog/data-breach-legacy-system-gnosis-pay-branded-cards) · [DeFiPrime](https://defiprime.com/gnosis-pay-legacy-card-data-breach) · [The Defiant](https://thedefiant.io/news/security/gnosis-pay-confirms-breach-of-consumer-card-system)
Conclusion: $GNO — [Binance GNO/USDT Spot chart](https://www.binance.com/en/trade/GNO_USDT?type=spot) for the Gnosis ecosystem token; it is not a measure of this card incident. Check the chart for yourself, do your own research, and trade responsibly. #GnosisPay #GNO #CryptoSecurity #DataBreach
39

·
--
【Kartennummer, CVV, Wohnadresse und Wallet-Adresse komplett geleakt! Krypto-Karte Gnosis Pay gehackt】
Die Krypto-Visa-Debitkarte Gnosis Pay gab bekannt, dass am 3. November unbefugte Dritte auf ihr eigenes Kartensystem zugegriffen haben, das am 20. Dezember eingestellt werden soll. Dabei wurden vollständige Kartennummern, Ablaufdaten, CVVs, Namen, Wohnadressen und verknüpfte Wallet-Adressen von Kunden entwendet. Gelder blieben unangetastet. Das Unternehmen hat Online-Zahlungen nun verpflichtend mit einer 3D-Authentifizierung versehen und warnt vor Phishing-Versuchen, bei denen echte Informationen zum Betrug verwendet werden.
#GnosisPay #数据泄露 #Krypto-Karte
【Kartennummer, CVV, Wohnadresse und Wallet-Adresse komplett geleakt! Krypto-Karte Gnosis Pay gehackt】
Die Krypto-Visa-Debitkarte Gnosis Pay gab bekannt, dass am 3. November unbefugte Dritte auf ihr eigenes Kartensystem zugegriffen haben, das am 20. Dezember eingestellt werden soll. Dabei wurden vollständige Kartennummern, Ablaufdaten, CVVs, Namen, Wohnadressen und verknüpfte Wallet-Adressen von Kunden entwendet. Gelder blieben unangetastet. Das Unternehmen hat Online-Zahlungen nun verpflichtend mit einer 3D-Authentifizierung versehen und warnt vor Phishing-Versuchen, bei denen echte Informationen zum Betrug verwendet werden.
#GnosisPay #数据泄露 #Krypto-Karte
Die Krypto-Visa-Debitkarte Gnosis Pay gab bekannt, dass am 3. November unbefugte Dritte auf ihr eigenes Kartensystem zugegriffen haben, das am 20. Dezember eingestellt werden soll. Dabei wurden vollständige Kartennummern, Ablaufdaten, CVVs, Namen, Wohnadressen und verknüpfte Wallet-Adressen von Kunden entwendet. Gelder blieben unangetastet. Das Unternehmen hat Online-Zahlungen nun verpflichtend mit einer 3D-Authentifizierung versehen und warnt vor Phishing-Versuchen, bei denen echte Informationen zum Betrug verwendet werden.
#GnosisPay #数据泄露 #Krypto-Karte
29


·
--
Übersetzung ansehen
El proveedor de tarjetas cripto Gnosis Pay informó que los hackers accedieron a datos de clientes.
Según Decrypt, el ataque podría haber ocurrido a principios de este mes.
Los traders deberían estar al tanto de este incidente porque puede afectar la confianza en los servicios de pago de criptomonedas, lo que puede tener un impacto indirecto en el volumen de transacciones.
El hackeo de Gnosis Pay podría indicar que algunos proveedores de servicios de pago cripto no están lo suficientemente seguros, lo que puede afectar el comercio en línea de las criptomonedas.
¿Crees que este incidente provocará una mayor conciencia sobre la seguridad de los servicios de pago cripto entre los traders y usuarios?
#GnosisPay #HackeoCripto #SeguridadCripto #BinanceSquare
El proveedor de tarjetas cripto Gnosis Pay informó que los hackers accedieron a datos de clientes.
Según Decrypt, el ataque podría haber ocurrido a principios de este mes.
Los traders deberían estar al tanto de este incidente porque puede afectar la confianza en los servicios de pago de criptomonedas, lo que puede tener un impacto indirecto en el volumen de transacciones.
El hackeo de Gnosis Pay podría indicar que algunos proveedores de servicios de pago cripto no están lo suficientemente seguros, lo que puede afectar el comercio en línea de las criptomonedas.
¿Crees que este incidente provocará una mayor conciencia sobre la seguridad de los servicios de pago cripto entre los traders y usuarios?
#GnosisPay #HackeoCripto #SeguridadCripto #BinanceSquare
Según Decrypt, el ataque podría haber ocurrido a principios de este mes.
Los traders deberían estar al tanto de este incidente porque puede afectar la confianza en los servicios de pago de criptomonedas, lo que puede tener un impacto indirecto en el volumen de transacciones.
El hackeo de Gnosis Pay podría indicar que algunos proveedores de servicios de pago cripto no están lo suficientemente seguros, lo que puede afectar el comercio en línea de las criptomonedas.
¿Crees que este incidente provocará una mayor conciencia sobre la seguridad de los servicios de pago cripto entre los traders y usuarios?
#GnosisPay #HackeoCripto #SeguridadCripto #BinanceSquare
43
·
--
Artikel
Krypto-Kartenanbieter Gnosis Pay: Hacker hatten Zugriff auf Kundendaten🚨 Gnosis Pay bestätigt einen Angriff auf sein Kartensystem – die Gelder sind jedoch sicher!
Gnosis Pay erklärte, Hacker hätten auf Kundendaten im veralteten System hinter den Karten mit eigenem Branding zugegriffen. Die Gelder seien jedoch nicht betroffen und die Enterprise-Kartenplattform sei unberührt geblieben.
📊 Die offizielle Meldung:
• Erkennung: 3. November 2026
• Eindämmung: weniger als zwei Stunden
• Umfang: nur das Verbraucherkartensystem (B2C)
• Enterprise-Plattform: nicht betroffen
Krypto-Kartenanbieter Gnosis Pay: Hacker hatten Zugriff auf Kundendaten
🚨 Gnosis Pay bestätigt einen Angriff auf sein Kartensystem – die Gelder sind jedoch sicher!
Gnosis Pay erklärte, Hacker hätten auf Kundendaten im veralteten System hinter den Karten mit eigenem Branding zugegriffen. Die Gelder seien jedoch nicht betroffen und die Enterprise-Kartenplattform sei unberührt geblieben.
📊 Die offizielle Meldung:
• Erkennung: 3. November 2026
• Eindämmung: weniger als zwei Stunden
• Umfang: nur das Verbraucherkartensystem (B2C)
• Enterprise-Plattform: nicht betroffen
Gnosis Pay erklärte, Hacker hätten auf Kundendaten im veralteten System hinter den Karten mit eigenem Branding zugegriffen. Die Gelder seien jedoch nicht betroffen und die Enterprise-Kartenplattform sei unberührt geblieben.
📊 Die offizielle Meldung:
• Erkennung: 3. November 2026
• Eindämmung: weniger als zwei Stunden
• Umfang: nur das Verbraucherkartensystem (B2C)
• Enterprise-Plattform: nicht betroffen
1
15

·
--
Gnosis Pay hat gerade eine Mitteilung veröffentlicht: Am 3. November wurde auf das alte B2C-System für Markenkarten unbefugt zugegriffen; einige Kundendaten sind nach außen gelangt. Die White-Label-Unternehmensplattform und die Kundengelder sind nicht betroffen.
Zu den Daten, die einige Nutzer erhalten haben, gehören Name, Adresse, Kartennummer und die Adresse des verknüpften Wallets. Wenn die Adresse mit einem On-Chain-Wallet verknüpft werden kann, dürften in nächster Zeit vermehrt Phishing-Anrufe und -E-Mails mit „echten Informationen“ auftauchen. Das Unternehmen leitete innerhalb von zwei Stunden Maßnahmen ein und erzwang 3D Secure. Die Stilllegung dieses B2C-Systems war ohnehin für den 20. Dezember geplant.
Zur Erinnerung: Sie werden niemals nach deiner Seed-Phrase, deinem privaten Schlüssel oder deiner PIN fragen und dich auch nicht auffordern, zur Verifizierung Geld zu überweisen.
#GnosisPay #安全 #Phishing
Gnosis Pay hat gerade eine Mitteilung veröffentlicht: Am 3. November wurde auf das alte B2C-System für Markenkarten unbefugt zugegriffen; einige Kundendaten sind nach außen gelangt. Die White-Label-Unternehmensplattform und die Kundengelder sind nicht betroffen.
Zu den Daten, die einige Nutzer erhalten haben, gehören Name, Adresse, Kartennummer und die Adresse des verknüpften Wallets. Wenn die Adresse mit einem On-Chain-Wallet verknüpft werden kann, dürften in nächster Zeit vermehrt Phishing-Anrufe und -E-Mails mit „echten Informationen“ auftauchen. Das Unternehmen leitete innerhalb von zwei Stunden Maßnahmen ein und erzwang 3D Secure. Die Stilllegung dieses B2C-Systems war ohnehin für den 20. Dezember geplant.
Zur Erinnerung: Sie werden niemals nach deiner Seed-Phrase, deinem privaten Schlüssel oder deiner PIN fragen und dich auch nicht auffordern, zur Verifizierung Geld zu überweisen.
#GnosisPay #安全 #Phishing
Zu den Daten, die einige Nutzer erhalten haben, gehören Name, Adresse, Kartennummer und die Adresse des verknüpften Wallets. Wenn die Adresse mit einem On-Chain-Wallet verknüpft werden kann, dürften in nächster Zeit vermehrt Phishing-Anrufe und -E-Mails mit „echten Informationen“ auftauchen. Das Unternehmen leitete innerhalb von zwei Stunden Maßnahmen ein und erzwang 3D Secure. Die Stilllegung dieses B2C-Systems war ohnehin für den 20. Dezember geplant.
Zur Erinnerung: Sie werden niemals nach deiner Seed-Phrase, deinem privaten Schlüssel oder deiner PIN fragen und dich auch nicht auffordern, zur Verifizierung Geld zu überweisen.
#GnosisPay #安全 #Phishing
1

·
--
AUSGENUTZT
Gnosis Pay hat gerade eine Bombe platzen lassen und eine Software-Schwachstelle offengelegt, die bis in den Oktober 2023 zurückreicht und es ermöglichte, mit einem 1,5-Millionen-Dollar-Exploit die Karten-Safe-Infrastruktur #GnosisPay #CryptoHacks #SecurityMatters auszunutzen. Laut einem Post-Mortem wurde die Schwachstelle erst nach dem Exploit entdeckt, und zum Glück wurden alle betroffenen Nutzer vollständig erstattet. Dieser historische Hack ist eine Erinnerung daran, dass die Krypto-Landschaft ein Katz-und-Maus-Spiel ist, bei dem Sicherheit oberste Priorität hat. Die Konsequenzen sind eindeutig: Wenn Sie die Schrauben an den Sicherheitsmaßnahmen noch nicht angezogen haben, ist es jetzt an der Zeit, damit anzufangen – nicht nur für sich selbst, sondern auch für Ihre Mit-Inhaber. Werden Sie sich anpassen, bevor es zu spät ist?
AUSGENUTZT
Gnosis Pay hat gerade eine Bombe platzen lassen und eine Software-Schwachstelle offengelegt, die bis in den Oktober 2023 zurückreicht und es ermöglichte, mit einem 1,5-Millionen-Dollar-Exploit die Karten-Safe-Infrastruktur #GnosisPay #CryptoHacks #SecurityMatters auszunutzen. Laut einem Post-Mortem wurde die Schwachstelle erst nach dem Exploit entdeckt, und zum Glück wurden alle betroffenen Nutzer vollständig erstattet. Dieser historische Hack ist eine Erinnerung daran, dass die Krypto-Landschaft ein Katz-und-Maus-Spiel ist, bei dem Sicherheit oberste Priorität hat. Die Konsequenzen sind eindeutig: Wenn Sie die Schrauben an den Sicherheitsmaßnahmen noch nicht angezogen haben, ist es jetzt an der Zeit, damit anzufangen – nicht nur für sich selbst, sondern auch für Ihre Mit-Inhaber. Werden Sie sich anpassen, bevor es zu spät ist?
Gnosis Pay hat gerade eine Bombe platzen lassen und eine Software-Schwachstelle offengelegt, die bis in den Oktober 2023 zurückreicht und es ermöglichte, mit einem 1,5-Millionen-Dollar-Exploit die Karten-Safe-Infrastruktur #GnosisPay #CryptoHacks #SecurityMatters auszunutzen. Laut einem Post-Mortem wurde die Schwachstelle erst nach dem Exploit entdeckt, und zum Glück wurden alle betroffenen Nutzer vollständig erstattet. Dieser historische Hack ist eine Erinnerung daran, dass die Krypto-Landschaft ein Katz-und-Maus-Spiel ist, bei dem Sicherheit oberste Priorität hat. Die Konsequenzen sind eindeutig: Wenn Sie die Schrauben an den Sicherheitsmaßnahmen noch nicht angezogen haben, ist es jetzt an der Zeit, damit anzufangen – nicht nur für sich selbst, sondern auch für Ihre Mit-Inhaber. Werden Sie sich anpassen, bevor es zu spät ist?
122

·
--
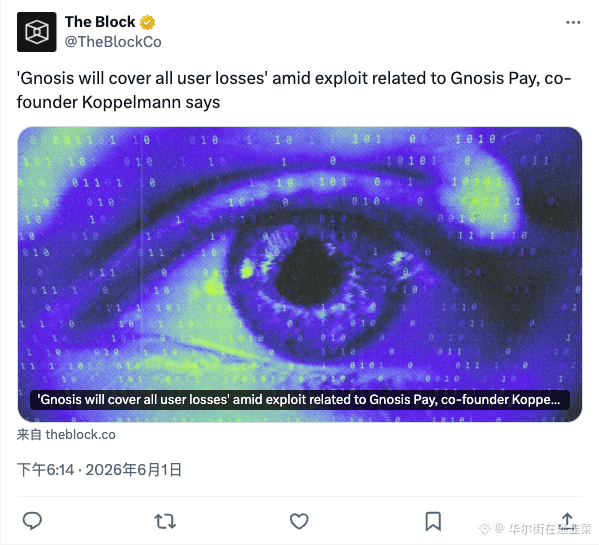
Entschädigungsabsicherung klingt zwar hart, aber wenn man die technischen Ursachen nicht ausgräbt, ist diese Runde an PR-Kosten nichts anderes als Geld, das ins Wasser geworfen wird.
Der Kern dessen, was bei dem Angriff auf Gnosis Pay passiert ist, in einem Satz: Die Signaturprüfung wurde umgangen. Nutzer konnten durch „versehentliches Betreten von Batch-Verarbeitung“ Transaktionen fälschen. Die offizielle Aussage lautet, dass alles in voller Höhe erstattet wird – die Bereitschaft ist also da.
Aber das wirklich Gefährliche ist, dass die Zahlungs-Erzählung abgewertet wurde: Selbst Account-Abstraction konnte die Sache nicht aufhalten. Die Vertrauenskosten im DeFi-Lego steigen dadurch sprunghaft. Der On-Chain-Credit-Pool wurde mit einem Loch versehen, und die Bewertungen von Wallet-Layer-Projekten in naher Zukunft werden unter Druck geraten. #GnosisPay $GNO
{spot}(GNOUSDT)
Entschädigungsabsicherung klingt zwar hart, aber wenn man die technischen Ursachen nicht ausgräbt, ist diese Runde an PR-Kosten nichts anderes als Geld, das ins Wasser geworfen wird.
Der Kern dessen, was bei dem Angriff auf Gnosis Pay passiert ist, in einem Satz: Die Signaturprüfung wurde umgangen. Nutzer konnten durch „versehentliches Betreten von Batch-Verarbeitung“ Transaktionen fälschen. Die offizielle Aussage lautet, dass alles in voller Höhe erstattet wird – die Bereitschaft ist also da.
Aber das wirklich Gefährliche ist, dass die Zahlungs-Erzählung abgewertet wurde: Selbst Account-Abstraction konnte die Sache nicht aufhalten. Die Vertrauenskosten im DeFi-Lego steigen dadurch sprunghaft. Der On-Chain-Credit-Pool wurde mit einem Loch versehen, und die Bewertungen von Wallet-Layer-Projekten in naher Zukunft werden unter Druck geraten. #GnosisPay $GNO
Der Kern dessen, was bei dem Angriff auf Gnosis Pay passiert ist, in einem Satz: Die Signaturprüfung wurde umgangen. Nutzer konnten durch „versehentliches Betreten von Batch-Verarbeitung“ Transaktionen fälschen. Die offizielle Aussage lautet, dass alles in voller Höhe erstattet wird – die Bereitschaft ist also da.
Aber das wirklich Gefährliche ist, dass die Zahlungs-Erzählung abgewertet wurde: Selbst Account-Abstraction konnte die Sache nicht aufhalten. Die Vertrauenskosten im DeFi-Lego steigen dadurch sprunghaft. Der On-Chain-Credit-Pool wurde mit einem Loch versehen, und die Bewertungen von Wallet-Layer-Projekten in naher Zukunft werden unter Druck geraten. #GnosisPay $GNO
58
·
--
"Gnosis Pay-Benutzer wurden durch einen Zodiac-Verzögerungsmodul-Bug HODL-gesperrt, und jetzt weißt du, warum sie sagen, dass Timing alles ist. Der Bug nutzte die Safe-Transaktionen der betroffenen Nutzer aus und ließ sie in einer Welt voller ERC-20-Probleme zurück. Gnosis Pay-Benutzern wird empfohlen, EURe und GNO ASAP abzuziehen, um dieses kosmische Krypto-Chaos zu vermeiden. Hat unsere Community gelernt, die Zodiac-Modul-Updates im Blick zu behalten wie die Krypto-Mondphase? Was ist dein Plan, um deine Safes abzusichern?" #GnosisPay #CryptoSecurity #ZodiacDelayModule
"Gnosis Pay-Benutzer wurden durch einen Zodiac-Verzögerungsmodul-Bug HODL-gesperrt, und jetzt weißt du, warum sie sagen, dass Timing alles ist. Der Bug nutzte die Safe-Transaktionen der betroffenen Nutzer aus und ließ sie in einer Welt voller ERC-20-Probleme zurück. Gnosis Pay-Benutzern wird empfohlen, EURe und GNO ASAP abzuziehen, um dieses kosmische Krypto-Chaos zu vermeiden. Hat unsere Community gelernt, die Zodiac-Modul-Updates im Blick zu behalten wie die Krypto-Mondphase? Was ist dein Plan, um deine Safes abzusichern?" #GnosisPay #CryptoSecurity #ZodiacDelayModule
69
·
--
Die Ausnutzung des Verzögerungsmoduls von Gnosis Pay weckt Bedenken, aber das Team verspricht sofortige Rückerstattungen. Die aktuelle Situation erfordert Vorsicht. Die Maßnahmen zeigen das Engagement für Sicherheit. #CryptoNews #BinanceSquare #GnosisPay
Die Ausnutzung des Verzögerungsmoduls von Gnosis Pay weckt Bedenken, aber das Team verspricht sofortige Rückerstattungen. Die aktuelle Situation erfordert Vorsicht. Die Maßnahmen zeigen das Engagement für Sicherheit. #CryptoNews #BinanceSquare #GnosisPay
84
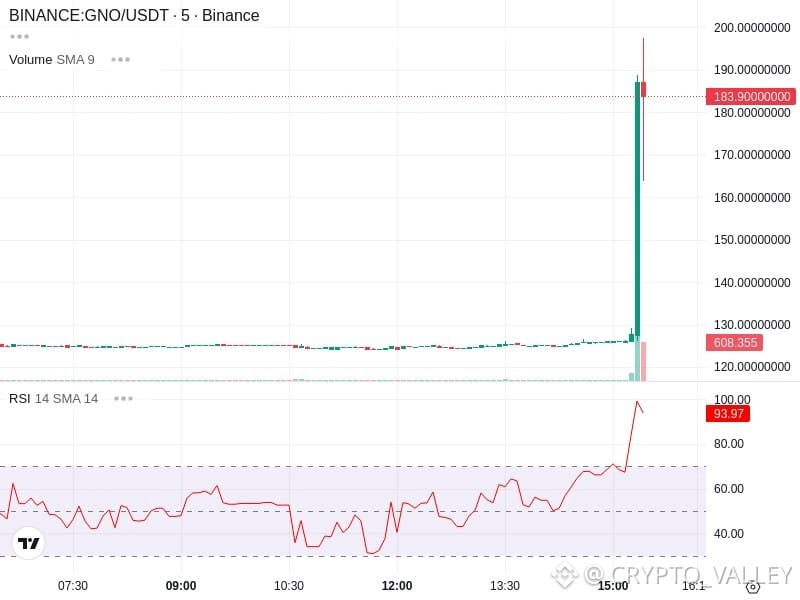
GNO/USDT [Binance]$GNO $GNO $GNO
Große Verkäufe aktiv 🔴
Es wurden 84,72 GNO verkauft
💰Preis: 180,18 USDT (-8,54%)
🚨Ordervolumen: 15.411 USDT (5,08%)
⏳Dauer: 22 Sekunden
📊24-Stunden-Handelsvolumen: 303,5 USDT
#GNO #GnosisPay #EthereumFoundationSellsETHtoBitmineAgain #BankofEnglandMayPauseDigitalPound #TrumpSaysIranConflictHasEnded
GNO/USDT [Binance]$GNO $GNO $GNO
Große Verkäufe aktiv 🔴
Es wurden 84,72 GNO verkauft
💰Preis: 180,18 USDT (-8,54%)
🚨Ordervolumen: 15.411 USDT (5,08%)
⏳Dauer: 22 Sekunden
📊24-Stunden-Handelsvolumen: 303,5 USDT
#GNO #GnosisPay #EthereumFoundationSellsETHtoBitmineAgain #BankofEnglandMayPauseDigitalPound #TrumpSaysIranConflictHasEnded
Große Verkäufe aktiv 🔴
Es wurden 84,72 GNO verkauft
💰Preis: 180,18 USDT (-8,54%)
🚨Ordervolumen: 15.411 USDT (5,08%)
⏳Dauer: 22 Sekunden
📊24-Stunden-Handelsvolumen: 303,5 USDT
#GNO #GnosisPay #EthereumFoundationSellsETHtoBitmineAgain #BankofEnglandMayPauseDigitalPound #TrumpSaysIranConflictHasEnded
96
·
--
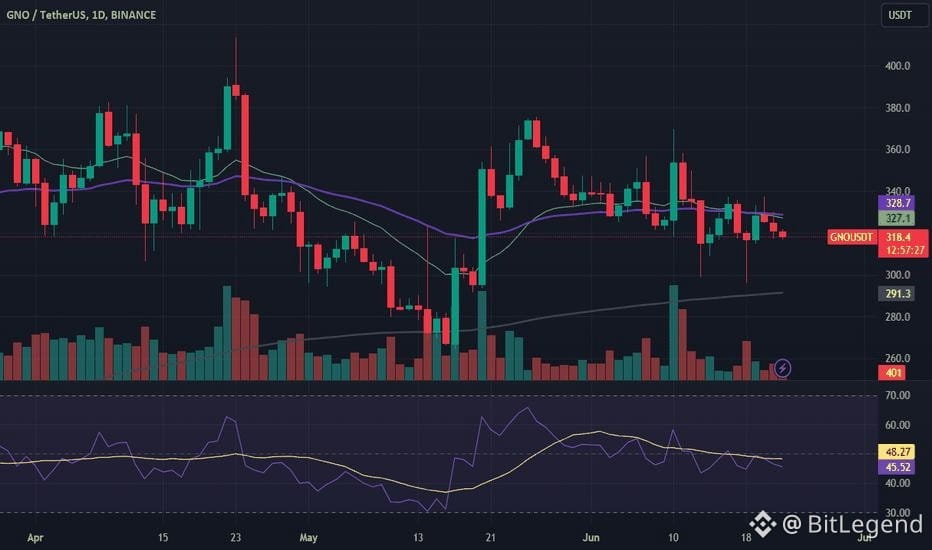
$GNO (Gnosis)
Aktueller Preis: etwa 113–114 $. Der jüngste Handel zeigte eine Zunahme der Aktivität, mit einem 24-Stunden-Volumen von rund 19,6 Mio. $ auf CoinGecko.
📈 Technische Einschätzung: GNO hat in letzter Zeit einen starken kurzfristigen Anstieg erlebt, aber die aktuellen Marktkommentare deuten darauf hin, dass die Bewegung teilweise durch Liquiditätseffekte getrieben ist, statt durch einen bedeutenden neuen Katalysator.
Bullische Faktoren:
• Steigende Handelsaktivität und neues Marktinteresse.
• Entwicklungen im Gnosis-Ökosystem, einschließlich Fortschritten in Richtung Layer 2, könnten die mittelfristige Stimmung stützen.
• Gnosis Pay bietet weiterhin echten praktischen Nutzen; für die Kartenausgaben im Juli 2026 wird ein Betrag von etwa 8,4 Mio. $ berichtet.
Ausblick: 🟢 Vorsichtig bullisch, aber GNO bleibt volatil. Ein anhaltender Ausbruch mit starkem Volumen würde die bullische These untermauern, während ein Fehlschlag, die zuletzt unterstützende Zone zu halten, einen Rücksetzer auslösen könnte.
Risiko: Hohe Volatilität und kursgetriebene Ausschläge durch Liquidität bedeuten, dass Trader ein angemessenes Risikomanagement nutzen sollten. Dies ist eine Marktanalyse, keine Finanzberatung.
#GNO #GnosisPay #USStorageStocksExtendLosses #ChinaToDropOlderWindowsFromStateAgencies #UnitreeRockets629%OnShanghaiDebut
{spot}(GNOUSDT)
$GNO (Gnosis)
Aktueller Preis: etwa 113–114 $. Der jüngste Handel zeigte eine Zunahme der Aktivität, mit einem 24-Stunden-Volumen von rund 19,6 Mio. $ auf CoinGecko.
📈 Technische Einschätzung: GNO hat in letzter Zeit einen starken kurzfristigen Anstieg erlebt, aber die aktuellen Marktkommentare deuten darauf hin, dass die Bewegung teilweise durch Liquiditätseffekte getrieben ist, statt durch einen bedeutenden neuen Katalysator.
Bullische Faktoren:
• Steigende Handelsaktivität und neues Marktinteresse.
• Entwicklungen im Gnosis-Ökosystem, einschließlich Fortschritten in Richtung Layer 2, könnten die mittelfristige Stimmung stützen.
• Gnosis Pay bietet weiterhin echten praktischen Nutzen; für die Kartenausgaben im Juli 2026 wird ein Betrag von etwa 8,4 Mio. $ berichtet.
Ausblick: 🟢 Vorsichtig bullisch, aber GNO bleibt volatil. Ein anhaltender Ausbruch mit starkem Volumen würde die bullische These untermauern, während ein Fehlschlag, die zuletzt unterstützende Zone zu halten, einen Rücksetzer auslösen könnte.
Risiko: Hohe Volatilität und kursgetriebene Ausschläge durch Liquidität bedeuten, dass Trader ein angemessenes Risikomanagement nutzen sollten. Dies ist eine Marktanalyse, keine Finanzberatung.
#GNO #GnosisPay #USStorageStocksExtendLosses #ChinaToDropOlderWindowsFromStateAgencies #UnitreeRockets629%OnShanghaiDebut
Aktueller Preis: etwa 113–114 $. Der jüngste Handel zeigte eine Zunahme der Aktivität, mit einem 24-Stunden-Volumen von rund 19,6 Mio. $ auf CoinGecko.
📈 Technische Einschätzung: GNO hat in letzter Zeit einen starken kurzfristigen Anstieg erlebt, aber die aktuellen Marktkommentare deuten darauf hin, dass die Bewegung teilweise durch Liquiditätseffekte getrieben ist, statt durch einen bedeutenden neuen Katalysator.
Bullische Faktoren:
• Steigende Handelsaktivität und neues Marktinteresse.
• Entwicklungen im Gnosis-Ökosystem, einschließlich Fortschritten in Richtung Layer 2, könnten die mittelfristige Stimmung stützen.
• Gnosis Pay bietet weiterhin echten praktischen Nutzen; für die Kartenausgaben im Juli 2026 wird ein Betrag von etwa 8,4 Mio. $ berichtet.
Ausblick: 🟢 Vorsichtig bullisch, aber GNO bleibt volatil. Ein anhaltender Ausbruch mit starkem Volumen würde die bullische These untermauern, während ein Fehlschlag, die zuletzt unterstützende Zone zu halten, einen Rücksetzer auslösen könnte.
Risiko: Hohe Volatilität und kursgetriebene Ausschläge durch Liquidität bedeuten, dass Trader ein angemessenes Risikomanagement nutzen sollten. Dies ist eine Marktanalyse, keine Finanzberatung.
#GNO #GnosisPay #USStorageStocksExtendLosses #ChinaToDropOlderWindowsFromStateAgencies #UnitreeRockets629%OnShanghaiDebut
61

·
--
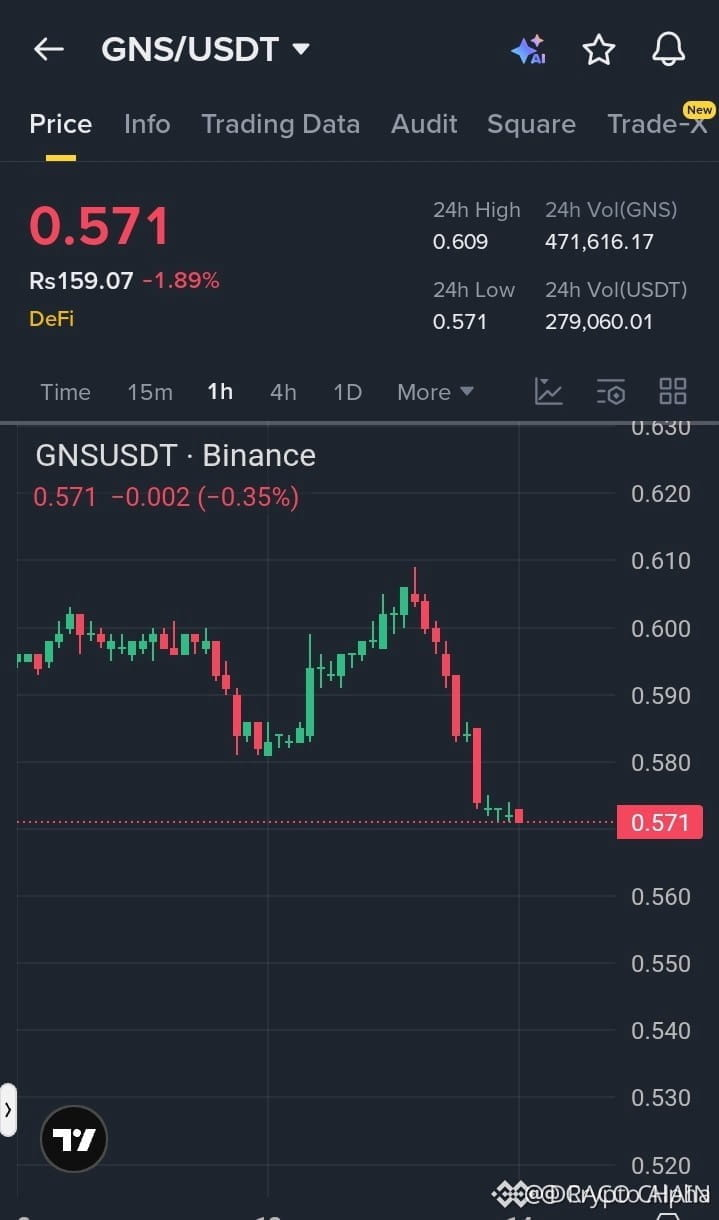
$GNS FACES STEEPER DECLINE 🔻
Entry: 0.570-0.573 🔥
Target: 0.565, 0.558, 0.550 🚀
Stop Loss: 0.582 ⚠️
Mehrfache Ablehnungen an der aktuellen Widerstandsstufe und schwacher Kaufdruck zeigen, dass die Verkäufer das Sagen haben. Bärischer Momentum konsolidiert, mit Liquidität, die sich im Bereich 0.570‑0.573 gruppiert. Ein Bruch der nächsten Unterstützung könnte den Abwärtstrend auf der erstklassigen Börse beschleunigen, wo das institutionelle Interesse zurückhaltend zu sein scheint.
Dies ist keine Finanzberatung. Manage dein Risiko.
#Crypto #Trading #Altcoins #GnosisPay #BearMarket 🚀
{spot}(GNSUSDT)
$GNS FACES STEEPER DECLINE 🔻
Entry: 0.570-0.573 🔥
Target: 0.565, 0.558, 0.550 🚀
Stop Loss: 0.582 ⚠️
Mehrfache Ablehnungen an der aktuellen Widerstandsstufe und schwacher Kaufdruck zeigen, dass die Verkäufer das Sagen haben. Bärischer Momentum konsolidiert, mit Liquidität, die sich im Bereich 0.570‑0.573 gruppiert. Ein Bruch der nächsten Unterstützung könnte den Abwärtstrend auf der erstklassigen Börse beschleunigen, wo das institutionelle Interesse zurückhaltend zu sein scheint.
Dies ist keine Finanzberatung. Manage dein Risiko.
#Crypto #Trading #Altcoins #GnosisPay #BearMarket 🚀
Entry: 0.570-0.573 🔥
Target: 0.565, 0.558, 0.550 🚀
Stop Loss: 0.582 ⚠️
Mehrfache Ablehnungen an der aktuellen Widerstandsstufe und schwacher Kaufdruck zeigen, dass die Verkäufer das Sagen haben. Bärischer Momentum konsolidiert, mit Liquidität, die sich im Bereich 0.570‑0.573 gruppiert. Ein Bruch der nächsten Unterstützung könnte den Abwärtstrend auf der erstklassigen Börse beschleunigen, wo das institutionelle Interesse zurückhaltend zu sein scheint.
Dies ist keine Finanzberatung. Manage dein Risiko.
#Crypto #Trading #Altcoins #GnosisPay #BearMarket 🚀
1
107
·
--
GNO/USDT Trading-Signal: Gnosis-Token zielt auf einen wichtigen Trendwechsel nach dem Halten der wesentlichen UnterstützungGnosis (GNO) sticht weiterhin als erstklassige Infrastruktur und dezentrales Vorhersagemarkt-Ökosystem hervor. Bei stetigem Marktinteresse ist GNO um +0,73% gestiegen und wird solide bei $118,22 gehandelt.
$GNO
+------------------------------------------------------------+
| GNO/USDT |
| Widerstand: $125,00 -----------> Ziel 2: $148,00 |
| Aktueller Preis: $118,22 --------> Ziel 1: $134,00 |
| Unterstützung: $115,00 --------------> Stop Loss: $110,00 |
+------------------------------------------------------------+
Marktdynamik & Fundamentaldaten
GNO/USDT Trading-Signal: Gnosis-Token zielt auf einen wichtigen Trendwechsel nach dem Halten der wesentlichen Unterstützung
Gnosis (GNO) sticht weiterhin als erstklassige Infrastruktur und dezentrales Vorhersagemarkt-Ökosystem hervor. Bei stetigem Marktinteresse ist GNO um +0,73% gestiegen und wird solide bei $118,22 gehandelt.
$GNO
+------------------------------------------------------------+
| GNO/USDT |
| Widerstand: $125,00 -----------> Ziel 2: $148,00 |
| Aktueller Preis: $118,22 --------> Ziel 1: $134,00 |
| Unterstützung: $115,00 --------------> Stop Loss: $110,00 |
+------------------------------------------------------------+
Marktdynamik & Fundamentaldaten
$GNO
+------------------------------------------------------------+
| GNO/USDT |
| Widerstand: $125,00 -----------> Ziel 2: $148,00 |
| Aktueller Preis: $118,22 --------> Ziel 1: $134,00 |
| Unterstützung: $115,00 --------------> Stop Loss: $110,00 |
+------------------------------------------------------------+
Marktdynamik & Fundamentaldaten
1
65
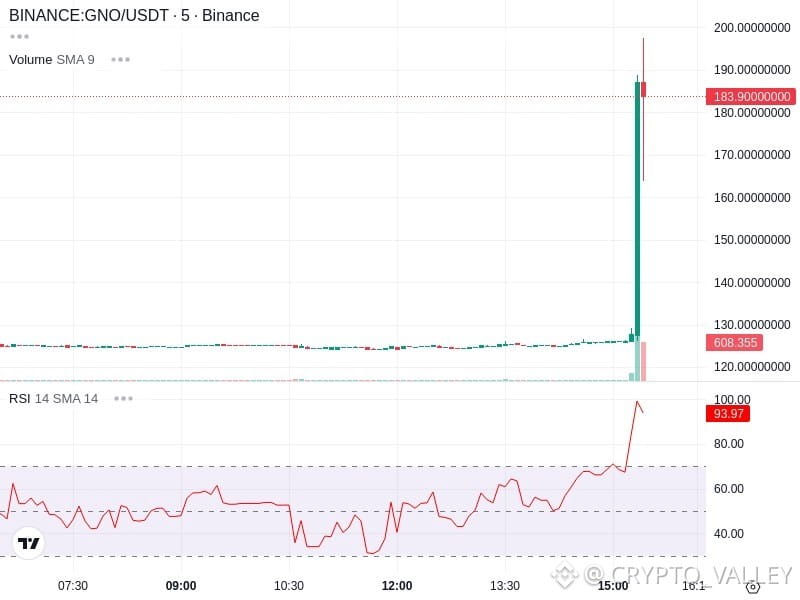
Kauf $GNO $GNO $GNO wird heute 200 Dollar erreichen ..
.#EthereumFoundationSellsETHtoBitmineAgain #GNO #GnosisPay #BuyTheDip #long
Kauf $GNO $GNO $GNO wird heute 200 Dollar erreichen ..
.#EthereumFoundationSellsETHtoBitmineAgain #GNO #GnosisPay #BuyTheDip #long
.#EthereumFoundationSellsETHtoBitmineAgain #GNO #GnosisPay #BuyTheDip #long
88

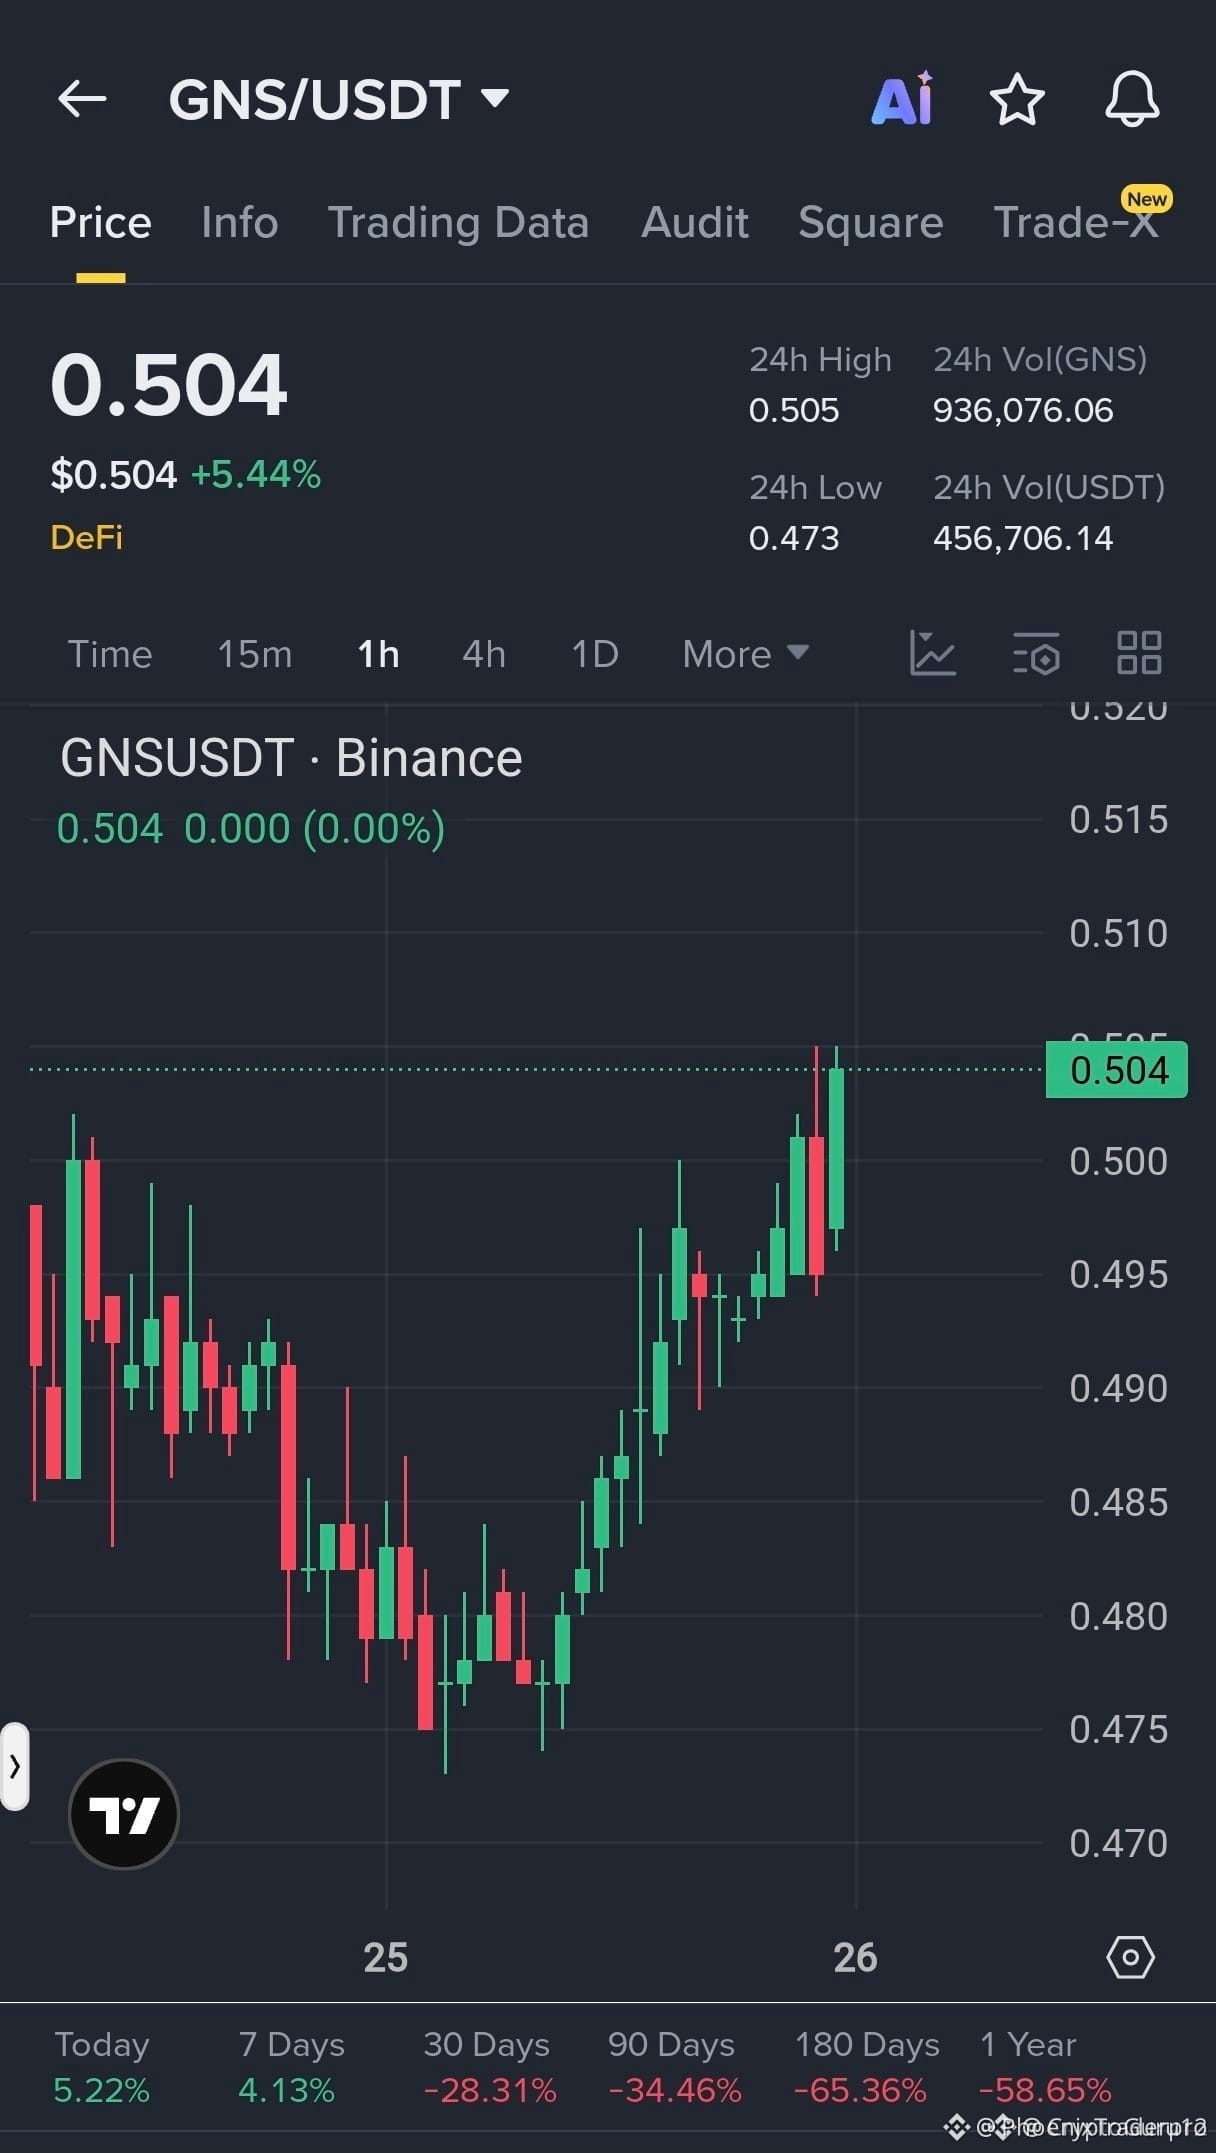
$GNS BULLISH TREPPENSTEIGUNG WIRD LAUT 🔥
$0.500 - $0.505 🚥
$0.515 / $0.530 / $0.550 / $0.575 🚀
$0.490 🛑
Käufer absorbieren Rücksetzer schnell. Höhere Hochs, steigende Dynamik, bullische Struktur bleibt intakt. Das ist die Art von Setup, die Wale beobachten, wenn der Fortsetzungsdruck nahe dem Widerstand aufzubauen beginnt. Wenn die Struktur hält, bleibt $GNS im Ausbruchmodus.
Keine Finanzberatung. Manage dein Risiko.
#GnosisPay #CryptoTrading #Altcoins #BinanceSquare #CryptoSignals
⚡
{spot}(GNSUSDT)
$GNS BULLISH TREPPENSTEIGUNG WIRD LAUT 🔥
$0.500 - $0.505 🚥
$0.515 / $0.530 / $0.550 / $0.575 🚀
$0.490 🛑
Käufer absorbieren Rücksetzer schnell. Höhere Hochs, steigende Dynamik, bullische Struktur bleibt intakt. Das ist die Art von Setup, die Wale beobachten, wenn der Fortsetzungsdruck nahe dem Widerstand aufzubauen beginnt. Wenn die Struktur hält, bleibt $GNS im Ausbruchmodus.
Keine Finanzberatung. Manage dein Risiko.
#GnosisPay #CryptoTrading #Altcoins #BinanceSquare #CryptoSignals
⚡
$0.500 - $0.505 🚥
$0.515 / $0.530 / $0.550 / $0.575 🚀
$0.490 🛑
Käufer absorbieren Rücksetzer schnell. Höhere Hochs, steigende Dynamik, bullische Struktur bleibt intakt. Das ist die Art von Setup, die Wale beobachten, wenn der Fortsetzungsdruck nahe dem Widerstand aufzubauen beginnt. Wenn die Struktur hält, bleibt $GNS im Ausbruchmodus.
Keine Finanzberatung. Manage dein Risiko.
#GnosisPay #CryptoTrading #Altcoins #BinanceSquare #CryptoSignals
⚡
64

·
--
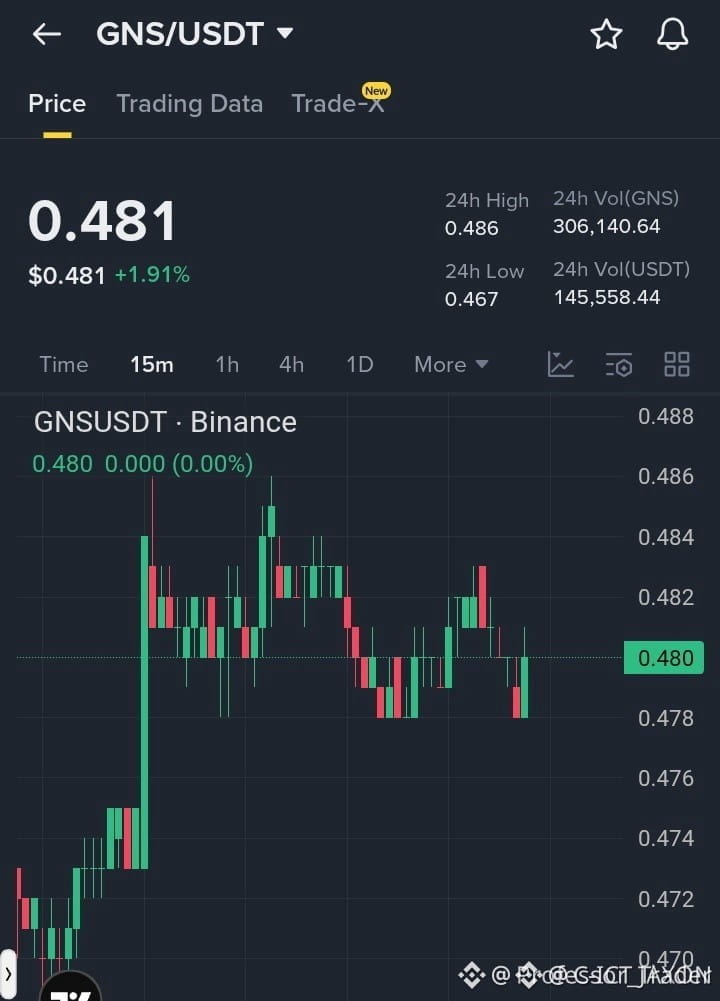
$GNO LONG SETUP TESTS EIN ENGES LIQUIDITÄTSFENSTER ⚡
Einstieg: 0.4780-0.4800 🎯
Ziel: 0.4840 / 0.4880 / 0.4940 ✅
Stop Loss: 0.4720 🛡️
Das Setup wird durch eine enge Einstiegzone und eine nahe Invalidation definiert, was die Ausführungsdisziplin wichtig macht. Wenn der Preis in den Gewinnbereich geht, kann das Verschieben des Stops auf den Einstieg die Abwärtsrisiken verringern, insbesondere wenn Leverage im Spiel ist. Trader sollten die Liquidität um das erste Ziel im Auge behalten, da Teilgewinne den kurzfristigen Momentum beeinflussen könnten.
Keine Finanzberatung. Manage dein Risiko.
#CryptoTrading #Altcoins #BinanceSquar #GnosisPay
🧭
{spot}(GNSUSDT)
$GNO LONG SETUP TESTS EIN ENGES LIQUIDITÄTSFENSTER ⚡
Einstieg: 0.4780-0.4800 🎯
Ziel: 0.4840 / 0.4880 / 0.4940 ✅
Stop Loss: 0.4720 🛡️
Das Setup wird durch eine enge Einstiegzone und eine nahe Invalidation definiert, was die Ausführungsdisziplin wichtig macht. Wenn der Preis in den Gewinnbereich geht, kann das Verschieben des Stops auf den Einstieg die Abwärtsrisiken verringern, insbesondere wenn Leverage im Spiel ist. Trader sollten die Liquidität um das erste Ziel im Auge behalten, da Teilgewinne den kurzfristigen Momentum beeinflussen könnten.
Keine Finanzberatung. Manage dein Risiko.
#CryptoTrading #Altcoins #BinanceSquar #GnosisPay
🧭
Einstieg: 0.4780-0.4800 🎯
Ziel: 0.4840 / 0.4880 / 0.4940 ✅
Stop Loss: 0.4720 🛡️
Das Setup wird durch eine enge Einstiegzone und eine nahe Invalidation definiert, was die Ausführungsdisziplin wichtig macht. Wenn der Preis in den Gewinnbereich geht, kann das Verschieben des Stops auf den Einstieg die Abwärtsrisiken verringern, insbesondere wenn Leverage im Spiel ist. Trader sollten die Liquidität um das erste Ziel im Auge behalten, da Teilgewinne den kurzfristigen Momentum beeinflussen könnten.
Keine Finanzberatung. Manage dein Risiko.
#CryptoTrading #Altcoins #BinanceSquar #GnosisPay
🧭
15
Anmelden und weiter Inhalte entdecken
Krypto-Nutzer weltweit auf Binance Square kennenlernen
⚡️ Bleib in Sachen Krypto stets am Puls.
💬 Die weltgrößte Kryptobörse vertraut darauf.
👍 Erhalte verlässliche Einblicke von verifizierten Creators.
E-Mail-Adresse/Telefonnummer
Trendthemen
1
#BitcoinRebounds$75KAsChipsLead
3,981 Aufrufe
94 Kommentare
2
#JobsReportRaisesHikeOdds
73,956 Aufrufe
824 Kommentare
3
#US Data Center Rules May Constrain AI Expansion
8,711 Aufrufe
91 Kommentare
4
#$2TWipedOutHedgeFundsFaceLiquidation
10,683 Aufrufe
95 Kommentare
5
#WillAnthropicListOnTime
8,250 Aufrufe
217 Kommentare
6
#USNovemberMichiganExpectationsIndexPrelimAt50.9
16,260 Aufrufe
323 Kommentare
7
#OilPlungesBelow$100
17,446 Aufrufe
37 Kommentare
8
#TradFiForBeginners
10,052 Aufrufe
205 Kommentare
9
#USMidtermsCouldShakeUpUS-IranTies
34,392 Aufrufe
491 Kommentare
10
#RussianCentralBankNamesBTCETHUSDTForNonQualifiedInvestors
656 Aufrufe
11 Kommentare