

#softwaresecurity
softwaresecurity
1,489 baxış
Müzakirə edir: 3
Populyar
Sonuncu
·
--
Məqalə
Tərcüməyə bax
Download verification: bytes and identityA matching download hash can still lead you to the wrong software.
A checksum answers: "Does this file match this reference value?" It doesn't answer: "Who gave me that reference?"
If an attacker replaces both an installer and the hash beside it, they can match perfectly. A parcel arriving with its own handwritten receipt isn't independent verification.
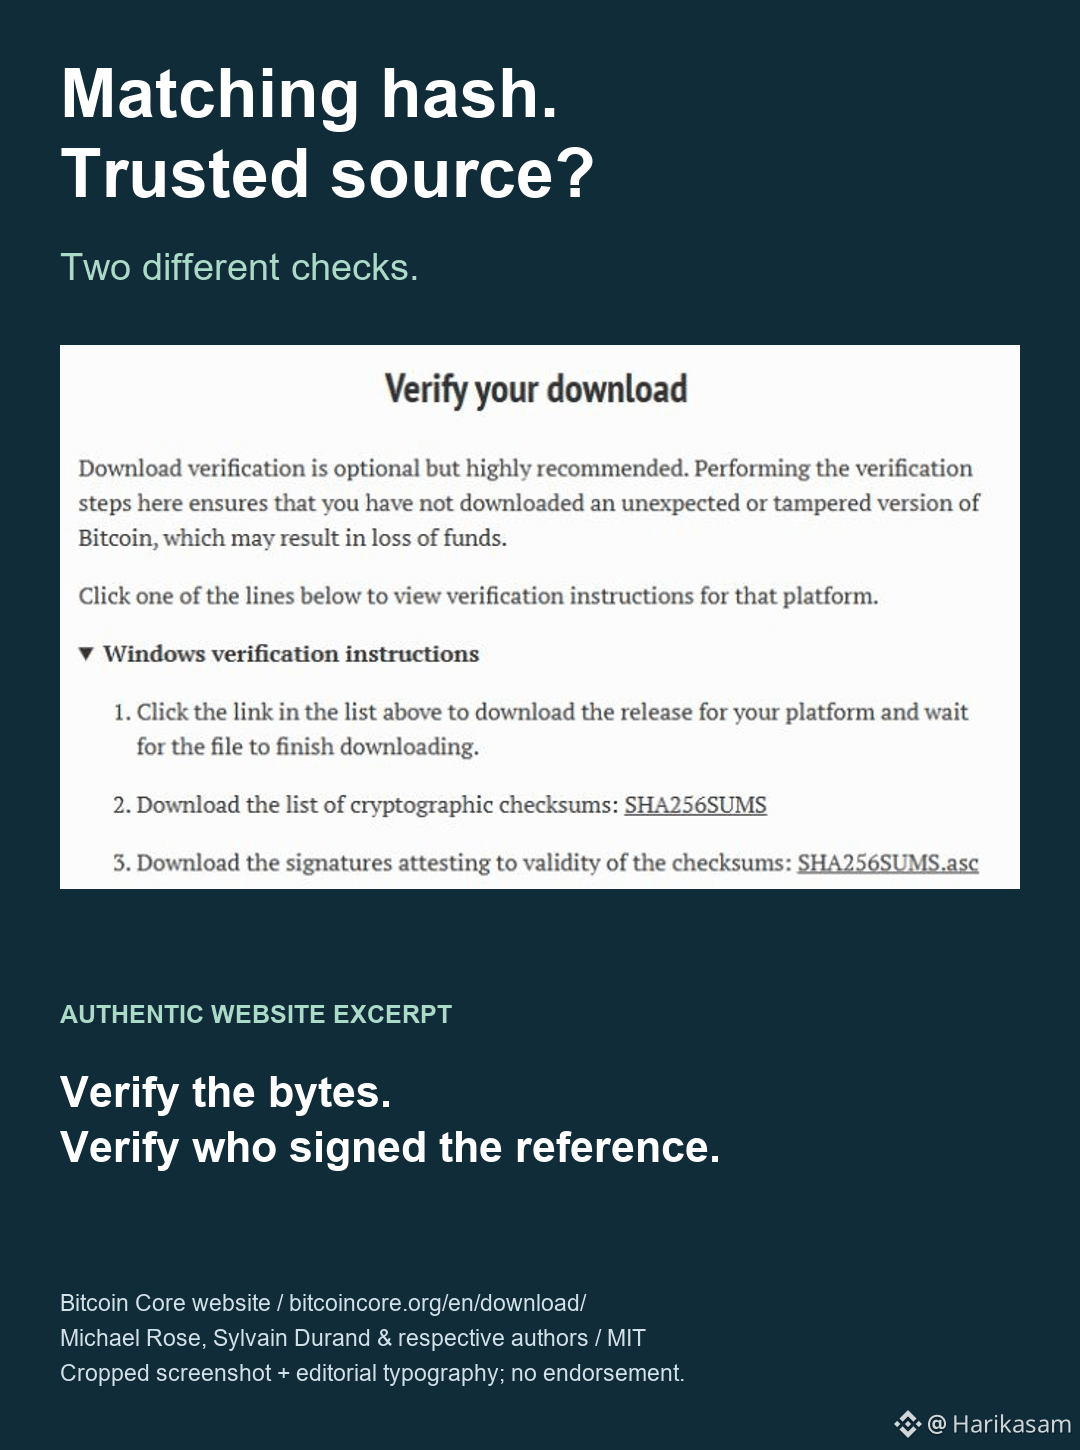
Bitcoin Core's download instructions separate file checksums from signatures on the checksum list. That distinction is useful beyond Bitcoin.
- Start from the project's official download page, reached through a trusted bookmark or independently checked address.
- Obtain the release, its checksum list, and the signature file using the project's instructions. For Bitcoin Core, those files are SHA256SUMS and SHA256SUMS.asc.
- Establish which signing keys you trust. Check their fingerprints against an independently trusted reference; importing a key from the same suspicious page doesn't establish its identity.
- Verify the signature on the checksum list. Then compute your downloaded file's SHA-256 hash and compare every character with the appropriate entry.
Don't treat a signature warning as decorative terminal confetti. Understand whether the problem is an unknown key, a fingerprint mismatch, or a failed signature before running anything.
A valid signature links a file's reference hash to a signing key. It doesn't prove the program is bug-free or that the key was never compromised.
The useful habit: verify both the bytes and the identity behind the reference. "The hash matches" is one check, not the whole security review.
$BTC
#SoftwareSecurity #BitcoinCore
Download verification: bytes and identity
A matching download hash can still lead you to the wrong software.
A checksum answers: "Does this file match this reference value?" It doesn't answer: "Who gave me that reference?"
If an attacker replaces both an installer and the hash beside it, they can match perfectly. A parcel arriving with its own handwritten receipt isn't independent verification.
Bitcoin Core's download instructions separate file checksums from signatures on the checksum list. That distinction is useful beyond Bitcoin.
- Start from the project's official download page, reached through a trusted bookmark or independently checked address.
- Obtain the release, its checksum list, and the signature file using the project's instructions. For Bitcoin Core, those files are SHA256SUMS and SHA256SUMS.asc.
- Establish which signing keys you trust. Check their fingerprints against an independently trusted reference; importing a key from the same suspicious page doesn't establish its identity.
- Verify the signature on the checksum list. Then compute your downloaded file's SHA-256 hash and compare every character with the appropriate entry.
Don't treat a signature warning as decorative terminal confetti. Understand whether the problem is an unknown key, a fingerprint mismatch, or a failed signature before running anything.
A valid signature links a file's reference hash to a signing key. It doesn't prove the program is bug-free or that the key was never compromised.
The useful habit: verify both the bytes and the identity behind the reference. "The hash matches" is one check, not the whole security review.
$BTC
#SoftwareSecurity #BitcoinCore
75

Məqalə
Notepad++ Yeniləmə Serverləri Çin Hakerləri Tərəfindən 6 Ay Ələ Keçirildi – Kripto Koderlər Riskdə?Notepad++ infrastruktur pozulmasının hücumçulara zərərli serverlərə yeniləmələri yönləndirməyə imkan verdiyini təsdiqləyir, bu da 2025-ci ilin iyun ayından dekabr ayına qədər seçici istifadəçiləri təsir edib.
Notepad++-un arxasında duran inkişaf etdirici, dünyanın ən populyar mətn redaktorlarından biri, proqram təminatının yeniləmə infrastrukturasını pozan mürəkkəb altı aylıq kiberhücum haqqında məlumat verib. Təhlükəsizlik mütəxəssisləri pozulmanı seçici olaraq istifadəçiləri zərərli serverlərə yönləndirən Çin dövləti tərəfindən dəstəklənən təhdid qrupuna aid ediblər.
The_Cyber_News-ə görə X-də, hakerlər Notepad++ yeniləmə serverlərini ələ keçirərək istifadəçiləri zərərli infrastruktura yönləndirdilər. Pozulma, köhnə versiyaların yeniləmə paketlərini 8.8.9 versiyasının buraxılmasından əvvəl necə təsdiqlədiyi ilə bağlı zəifliklərdən istifadə etdi.
Notepad++ Yeniləmə Serverləri Çin Hakerləri Tərəfindən 6 Ay Ələ Keçirildi – Kripto Koderlər Riskdə?
Notepad++ infrastruktur pozulmasının hücumçulara zərərli serverlərə yeniləmələri yönləndirməyə imkan verdiyini təsdiqləyir, bu da 2025-ci ilin iyun ayından dekabr ayına qədər seçici istifadəçiləri təsir edib.
Notepad++-un arxasında duran inkişaf etdirici, dünyanın ən populyar mətn redaktorlarından biri, proqram təminatının yeniləmə infrastrukturasını pozan mürəkkəb altı aylıq kiberhücum haqqında məlumat verib. Təhlükəsizlik mütəxəssisləri pozulmanı seçici olaraq istifadəçiləri zərərli serverlərə yönləndirən Çin dövləti tərəfindən dəstəklənən təhdid qrupuna aid ediblər.
The_Cyber_News-ə görə X-də, hakerlər Notepad++ yeniləmə serverlərini ələ keçirərək istifadəçiləri zərərli infrastruktura yönləndirdilər. Pozulma, köhnə versiyaların yeniləmə paketlərini 8.8.9 versiyasının buraxılmasından əvvəl necə təsdiqlədiyi ilə bağlı zəifliklərdən istifadə etdi.
7
4.4k
Daha çox kontent araşdırmaq üçün daxil olun
Binance Square-də qlobal kriptovalyuta istifadəçilərinə qoşulun
⚡️ Kriptovalyuta haqqında ən son və faydalı məlumatları əldə edin.
💬 Dünyanın ən böyük kriptovalyuta birjası tərəfindən etibar edilir.
👍 Doğrulanmış yaradıcılardan gələn real məlumatları kəşf edin.
E-poçt/Telefon nömrəsi
Trenddə olan mövzular
1
#EarningsSeason
6.6M baxış
Müzakirə edir: 33,056
2
#USMidtermElections
83,914 baxış
Müzakirə edir: 1,092
3
#StrategySTRCReaches$99.95ForFirstTimeIn165Days
605 baxış
Müzakirə edir: 31
4
#BinanceWillListPredictPREDICT
10,943 baxış
Müzakirə edir: 340
5
#SwitzerlandFirstSpotBitcoinETFExpectedToTradeInNovember
753 baxış
Müzakirə edir: 48
6
#StrategyReports$21BQ3OperatingProfit
597 baxış
Müzakirə edir: 29
7
#Strategy三季度营业利润210亿美元
13,141 baxış
Müzakirə edir: 47
8
#TwoAddressesHoldingAbout1.28BUSDTFrozen
3,908 baxış
Müzakirə edir: 157
9
#FirstDigitalBlacklistsAttackerAddressHoldingAbout3.4MFDUSD
231 baxış
Müzakirə edir: 13
10
#BitcoinDropsBelow$80K
60,229 baxış
Müzakirə edir: 160