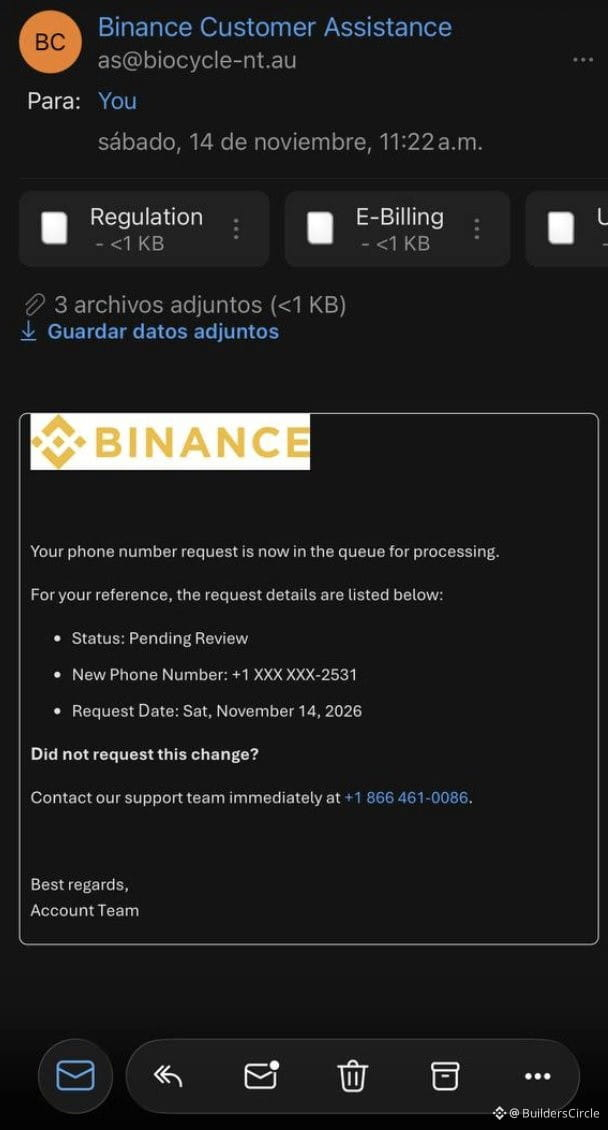
New phishing attack vector targeting $BNB exchange users combines email spoofing + vishing (voice phishing).
Attack flow:
1. Fake email claims unauthorized phone number change on user account
2. Creates urgency to call attacker-controlled number
3. Social engineering to extract 2FA codes or credentials
Technical defense layers:
- Verify sender domain via SPF/DKIM records before trusting
- Never use contact info from suspicious emails (always use official app/website)
- Don't open attachments (potential malware delivery)
- Enable platform's anti-phishing code feature (adds unique identifier to legit emails)
- Check account activity only through authenticated sessions
This is classic pretexting combined with urgency manipulation. The phone number change claim is designed to bypass email-only verification skepticism by pushing victims to voice channels where social engineering is more effective.
Attack flow:
1. Fake email claims unauthorized phone number change on user account
2. Creates urgency to call attacker-controlled number
3. Social engineering to extract 2FA codes or credentials
Technical defense layers:
- Verify sender domain via SPF/DKIM records before trusting
- Never use contact info from suspicious emails (always use official app/website)
- Don't open attachments (potential malware delivery)
- Enable platform's anti-phishing code feature (adds unique identifier to legit emails)
- Check account activity only through authenticated sessions
This is classic pretexting combined with urgency manipulation. The phone number change claim is designed to bypass email-only verification skepticism by pushing victims to voice channels where social engineering is more effective.