🚨 CRITICAL SUPPLY CHAIN ATTACK 🚨
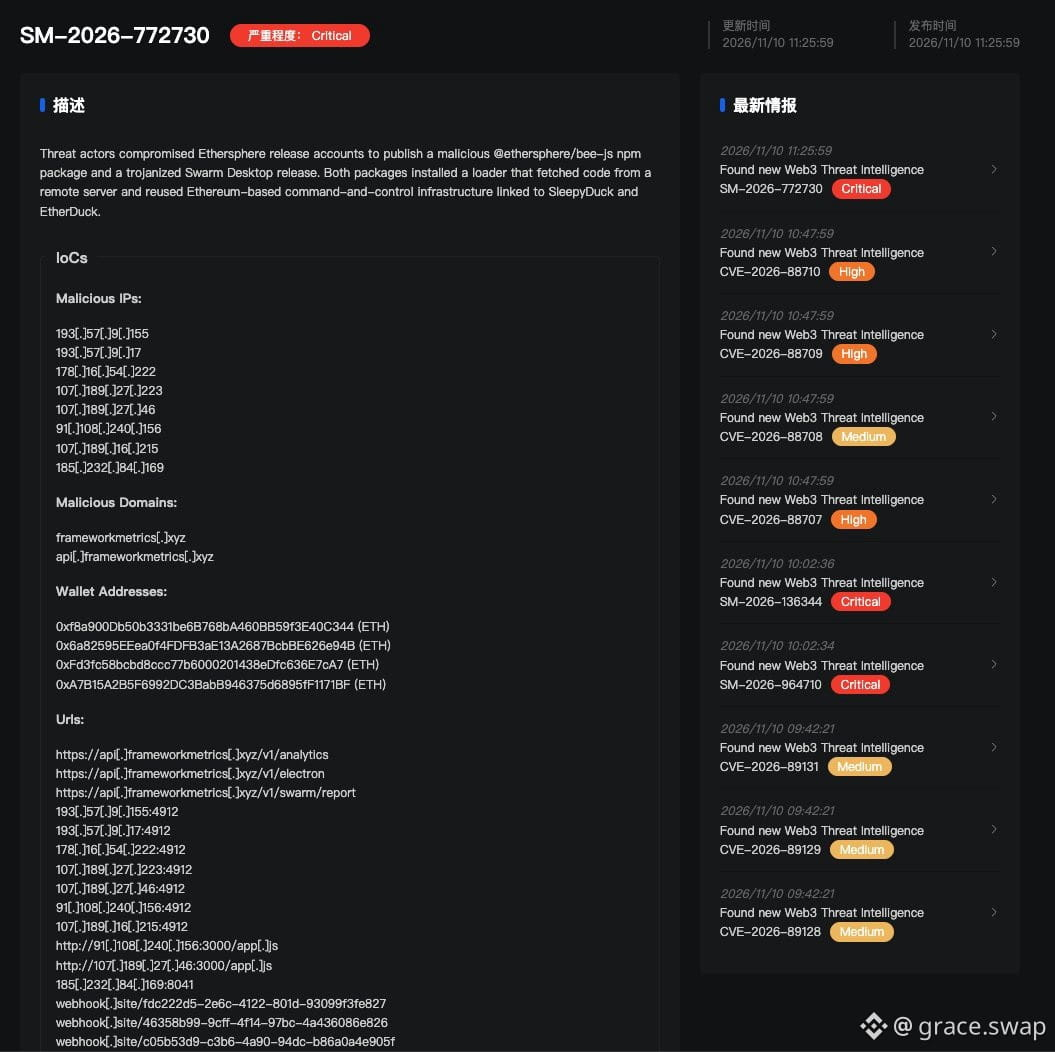
Ethersphere's npm package @ethersphere/bee-js v13.3.0 + Swarm Desktop v0.56.2 got REKT by attackers who hijacked legit GitHub accounts and release pipelines. All platforms hit: Windows, macOS, Linux.
How it works:
• Malicious code pulls remote JS from api[.]frameworkmetrics[.]xyz
• Uses Ethereum smart contract 0xf8a900Db50b3331be6B768bA460BB59f3E40C344 as decentralized C2 config store
• Same contract tied to SleepyDuck/EtherDuck malware from poisoned Open VSX extensions
What's at risk:
• Wallet credentials stolen
• Private keys drained
• Persistent backdoors planted
• Unauthorized remote access
IMM ACTION REQUIRED:
✅ Remove @ethersphere/bee-js v13.3.0 NOW
✅ Pin to v13.2.0 (safe version)
✅ Upgrade Swarm Desktop to v0.56.3 (clean release)
✅ Audit affected systems
✅ Rotate ALL potentially exposed credentials
✅ Monitor connections to malicious infrastructure
Check your dependencies at SlowMist's free scanner before it's too late. This is why we can't have nice things in Web3.
Stay paranoid. 🛡️
Ethersphere's npm package @ethersphere/bee-js v13.3.0 + Swarm Desktop v0.56.2 got REKT by attackers who hijacked legit GitHub accounts and release pipelines. All platforms hit: Windows, macOS, Linux.
How it works:
• Malicious code pulls remote JS from api[.]frameworkmetrics[.]xyz
• Uses Ethereum smart contract 0xf8a900Db50b3331be6B768bA460BB59f3E40C344 as decentralized C2 config store
• Same contract tied to SleepyDuck/EtherDuck malware from poisoned Open VSX extensions
What's at risk:
• Wallet credentials stolen
• Private keys drained
• Persistent backdoors planted
• Unauthorized remote access
IMM ACTION REQUIRED:
✅ Remove @ethersphere/bee-js v13.3.0 NOW
✅ Pin to v13.2.0 (safe version)
✅ Upgrade Swarm Desktop to v0.56.3 (clean release)
✅ Audit affected systems
✅ Rotate ALL potentially exposed credentials
✅ Monitor connections to malicious infrastructure
Check your dependencies at SlowMist's free scanner before it's too late. This is why we can't have nice things in Web3.
Stay paranoid. 🛡️