$6M Keplr Wallet Exploit via Web3Auth - Here's the Real Story
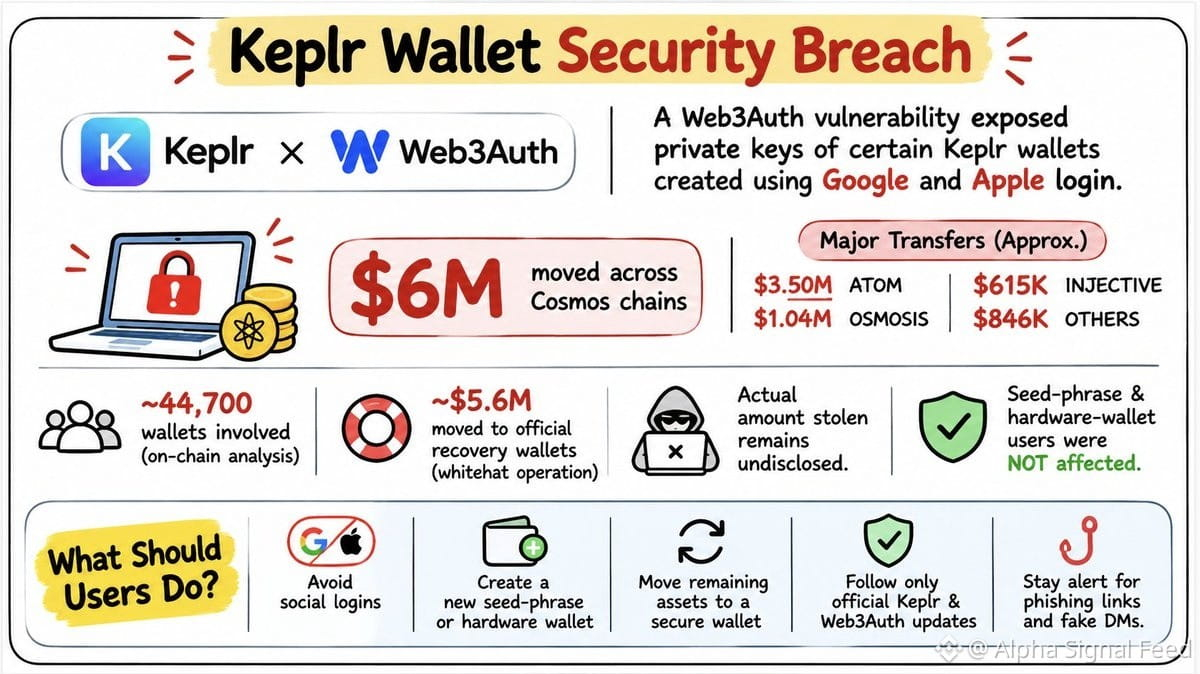
Web3Auth vulnerability exposed private keys for Keplr wallets using Google/Apple social logins. Thousands of wallets compromised, but most funds were whitehat rescued before attackers could drain them.
The Breakdown:
Nov 6, 2026 - Web3Auth infra breach hits Keplr social-login wallets. Google and Apple login accounts got exposed. Seed phrase and hardware wallet users were safe.
$6M moved across Cosmos chains:
$ATOM - $3.5M
$OSMO - $1.04M
$INJ - $615K
$AKT - $422K
$TIA - $238K
Noble - $108K
$DYDX - $62K
$BBN - $16K
Critical: Most of this was emergency whitehat recovery, NOT hacker profit. ~$5.6M secured in official recovery wallets. Actual attacker haul? Still unknown.
44,700 wallets flagged in datasets. Real damage likely way smaller than headlines suggest.
What This Really Means:
Your "decentralized" wallet isn't decentralized if your auth layer runs through Web3Auth or any third-party provider. One exploit in their system = your keys exposed.
Social logins are convenient until they're not. This is why hardware wallets and self-custody seed phrases exist.
If You Used Google/Apple Login on Keplr:
Stop using that wallet immediately
Generate new seed phrase wallet or use hardware
Move liquid assets out following official Keplr instructions
Check staked positions separately
Ignore all DMs offering "recovery help"
Only trust @keplrwallet and @Web3Auth official channels.
Bottom Line:
Convenience has a cost. Outsourced auth = outsourced risk. The attacker got in because the login provider failed, not because Cosmos chains are broken.
Most funds were saved, but the lesson is clear: Control your keys or someone else will.
Web3Auth vulnerability exposed private keys for Keplr wallets using Google/Apple social logins. Thousands of wallets compromised, but most funds were whitehat rescued before attackers could drain them.
The Breakdown:
Nov 6, 2026 - Web3Auth infra breach hits Keplr social-login wallets. Google and Apple login accounts got exposed. Seed phrase and hardware wallet users were safe.
$6M moved across Cosmos chains:
$ATOM - $3.5M
$OSMO - $1.04M
$INJ - $615K
$AKT - $422K
$TIA - $238K
Noble - $108K
$DYDX - $62K
$BBN - $16K
Critical: Most of this was emergency whitehat recovery, NOT hacker profit. ~$5.6M secured in official recovery wallets. Actual attacker haul? Still unknown.
44,700 wallets flagged in datasets. Real damage likely way smaller than headlines suggest.
What This Really Means:
Your "decentralized" wallet isn't decentralized if your auth layer runs through Web3Auth or any third-party provider. One exploit in their system = your keys exposed.
Social logins are convenient until they're not. This is why hardware wallets and self-custody seed phrases exist.
If You Used Google/Apple Login on Keplr:
Stop using that wallet immediately
Generate new seed phrase wallet or use hardware
Move liquid assets out following official Keplr instructions
Check staked positions separately
Ignore all DMs offering "recovery help"
Only trust @keplrwallet and @Web3Auth official channels.
Bottom Line:
Convenience has a cost. Outsourced auth = outsourced risk. The attacker got in because the login provider failed, not because Cosmos chains are broken.
Most funds were saved, but the lesson is clear: Control your keys or someone else will.